CVE-2023-38831-KQL
 pascalasch/cve-2023-38831-kql
KQL Hunting for WinRAR CVE-2023-38831
incident-responseinformation-gatheringioc-management+3
4
pascalasch/cve-2023-38831-kqlKQL Hunting for WinRAR CVE-2023-38831
 rv4l3r3/log4v-vuln-check
This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 jipegit/osxauditor
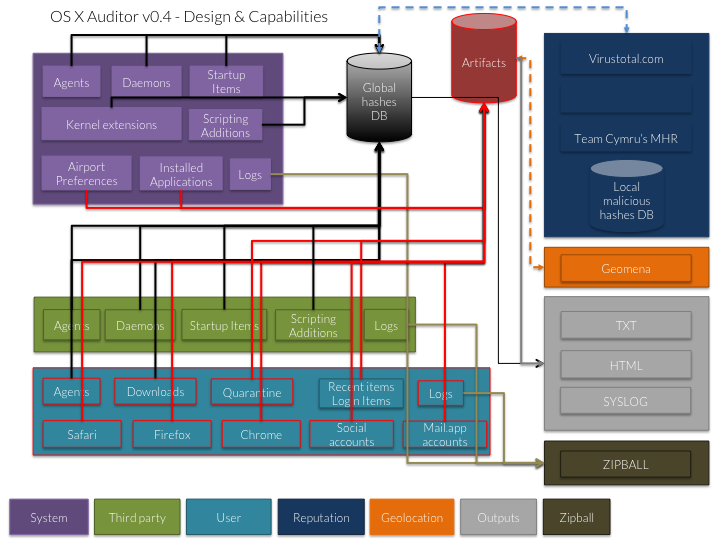
OS X Auditor is a free Mac OS X computer forensics tool
 ericzimmerman/kapefiles
This repository serves as a place for community created Targets and Modules for use with KAPE.
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
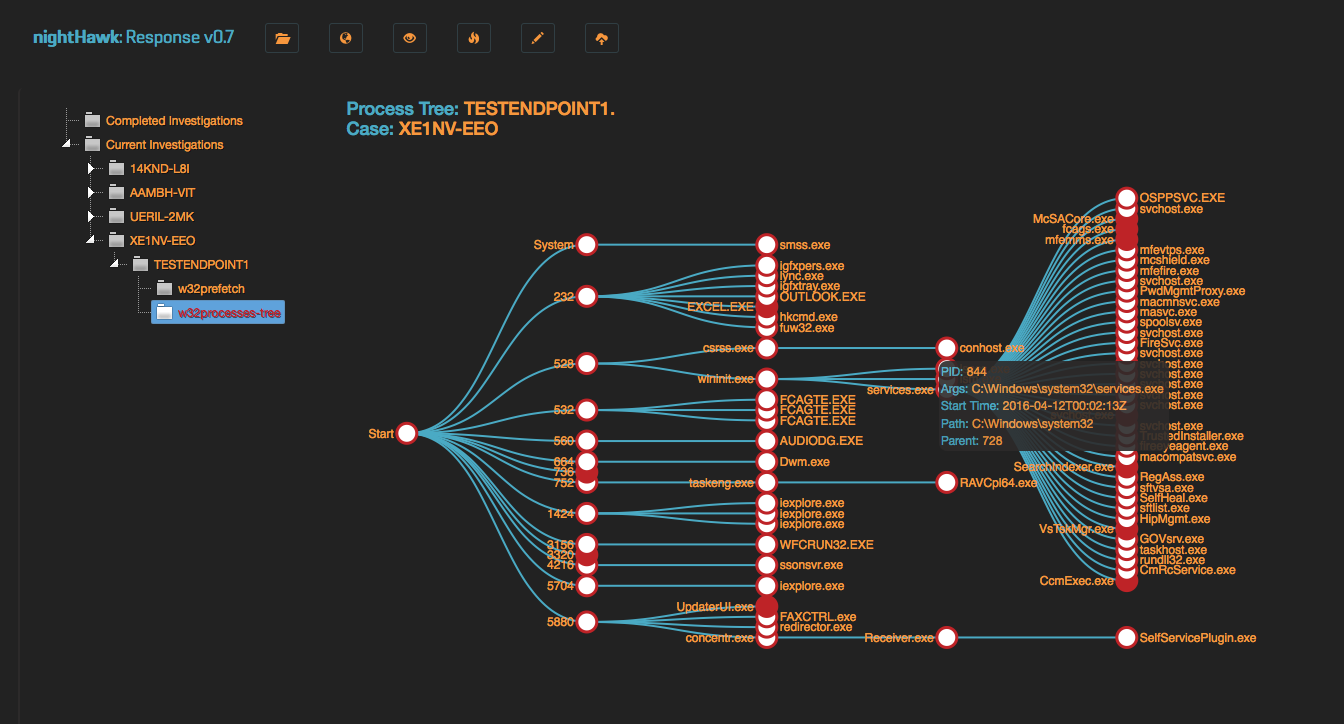 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
 kvasirsecurity/kvasir
Kvasir: Penetration Test Data Management
 dfir-dd/dfir-toolkit
CLI tools for forensic investigation of Windows artifacts