

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
702 results
arkime preview

arkime

GitHubarkime/arkime

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

defensive-toolsdigital-forensicsforensics+7
7.4k1 day ago
ntopng preview

ntopng

GitHubntop/ntopng

Web-based Traffic and Cybersecurity Network Traffic Monitoring
anomaly-detectiondns-analysisintrusion-detection+6
8.1k7h 2m ago
professional-services preview

professional-services

GitHubgooglecloudplatform/professional-services

Collection of Google Cloud solution examples and operational utilities for audit log monitoring, DLP de-identification, encryption key management,…

anomaly-detectionchaos-engineeringcloud-security+5
3.1k3 days ago
ossec-hids preview

ossec-hids

GitHubossec/ossec-hids

OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
defensive-toolsintrusion-detectionlog-analysis
5.0k21h 30m ago
AiSOC preview

AiSOC

GitHubbeenuar/aisoc

Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
ai-securityanomaly-detectiondefensive-tools+5
1.8k11h 39m ago
DetectionLab preview

DetectionLab

GitHubclong/detectionlab

Automate the creation of a lab environment complete with security tooling and logging best practices
configuration-auditingdefensive-toolsdigital-forensics+5
5.0k3 years ago
awesome-threat-detection preview

awesome-threat-detection

GitHub0x4d31/awesome-threat-detection

Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…

curated-resourceseducationincident-response+7
4.8k10 months ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k8 days ago
detection-rules preview

detection-rules

GitHubelastic/detection-rules

Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…

anomaly-detectioncurated-resourcesdefensive-tools+3
2.7k22h 9m ago
securityonion preview

securityonion

GitHubsecurity-onion-solutions/securityonion

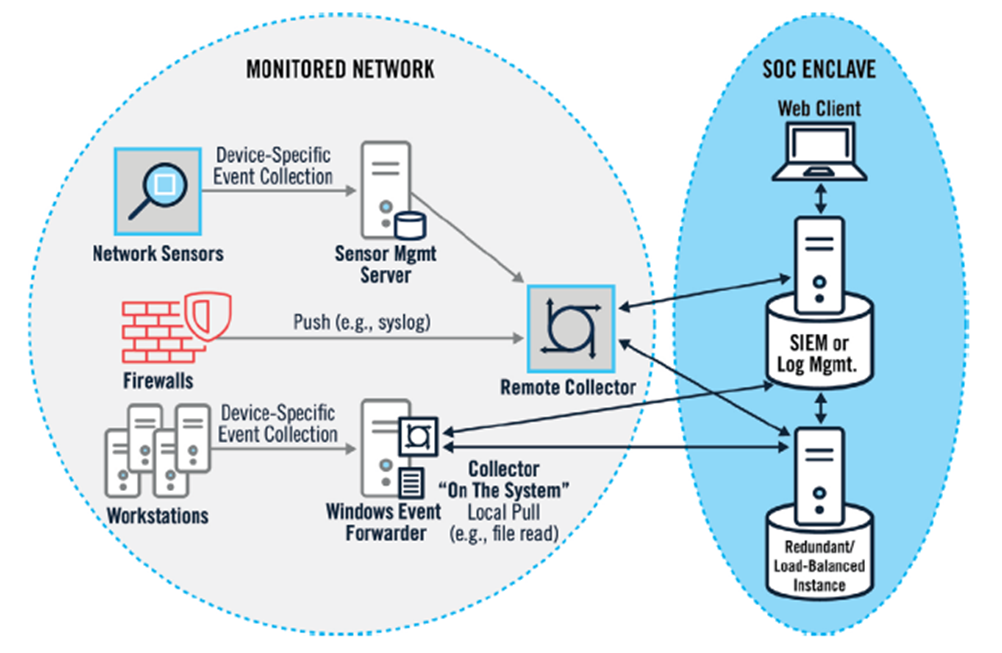
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
anomaly-detectionanti-botdefensive-tools+9
5.0k1 day ago
awesome-soc preview

awesome-soc

GitHubcyb3rxp/awesome-soc

A curated knowledge base to build, run and mature a SOC (including CSIRT).

ai-securitycurated-resourcesdefensive-tools+7
1.8k1 day ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
digital-forensicsforensicsincident-response+2
3.3k5 days ago
web preview

web

GitHubpi-hole/web

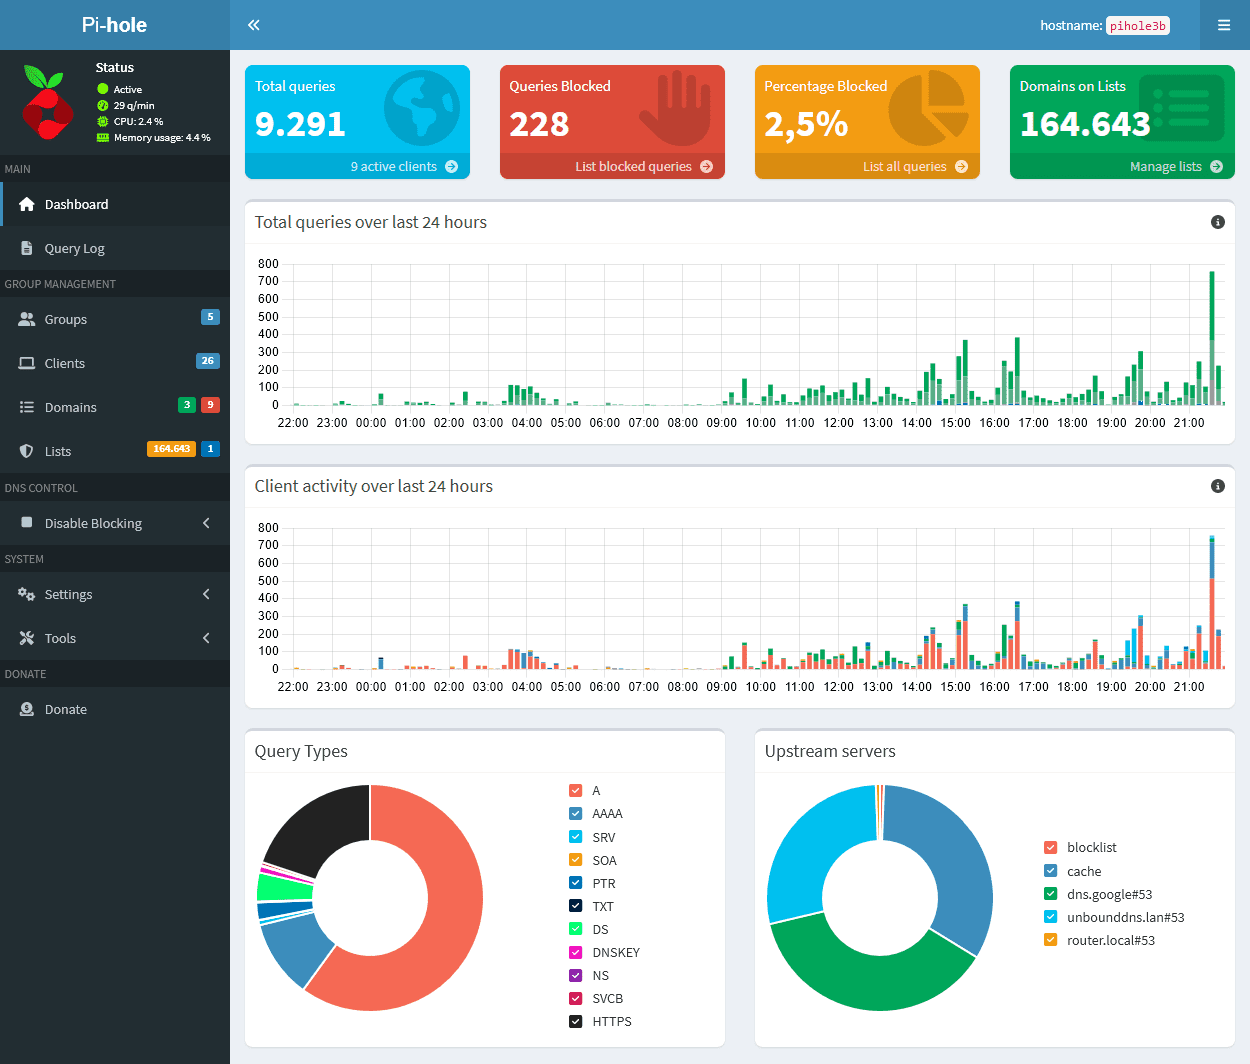
Pi-hole Dashboard for stats and more

dns-analysislog-analysisnetwork-security+1
2.5k17 days ago
chainsaw preview

chainsaw

GitHubwithsecureopensource/chainsaw

Rapidly Search and Hunt through Windows Forensic Artefacts
defensive-toolsdigital-forensicsforensics+4
3.7k20 days ago
opencanary preview

opencanary

GitHubthinkst/opencanary

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
defensive-toolsincident-responseintrusion-detection+3
3.1k6 days ago
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

digital-forensicsdns-analysisforensics+9
2.5k5 days ago
plaso preview

plaso

GitHublog2timeline/plaso

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
data-recoverydigital-forensicsdisk-forensics+5
2.2k1 day ago
RedELK preview

RedELK

GitHuboutflanknl/redelk

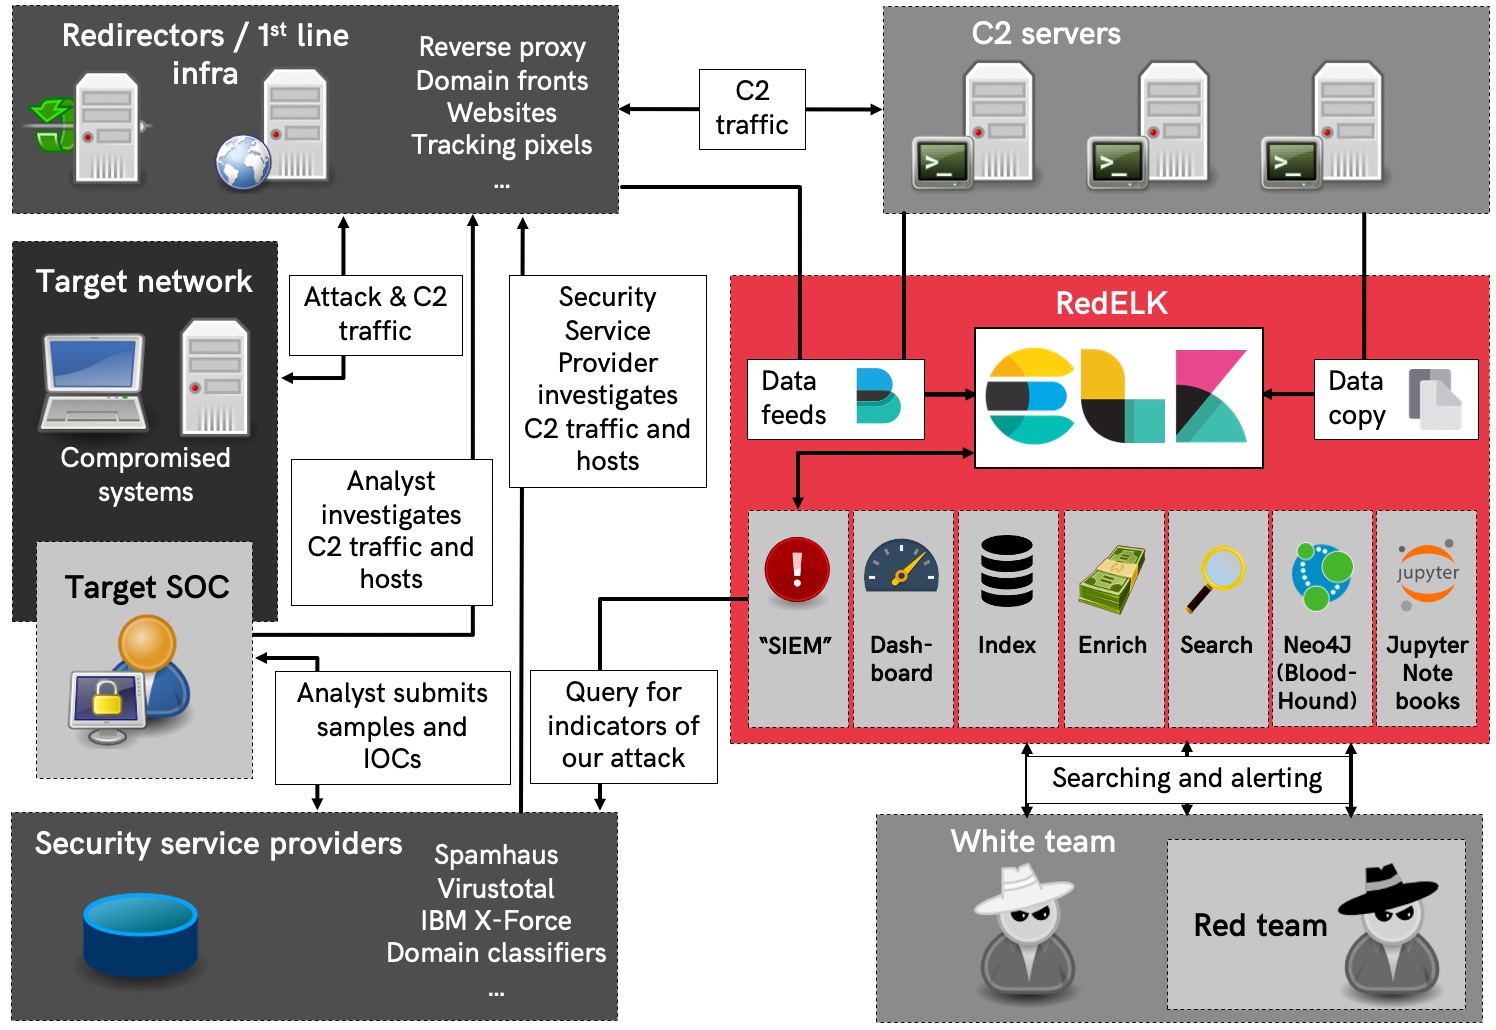
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.

defensive-toolsincident-responseinformation-gathering+4
2.7k1 day ago
Previous123…39Next