
seccubus
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
defensive-toolslog-analysisnetwork-mapping+5
seccubus/seccubusEasy automated vulnerability scanning, reporting and analysis
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 orgito1015/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes vulnerability analysis, detection rules…
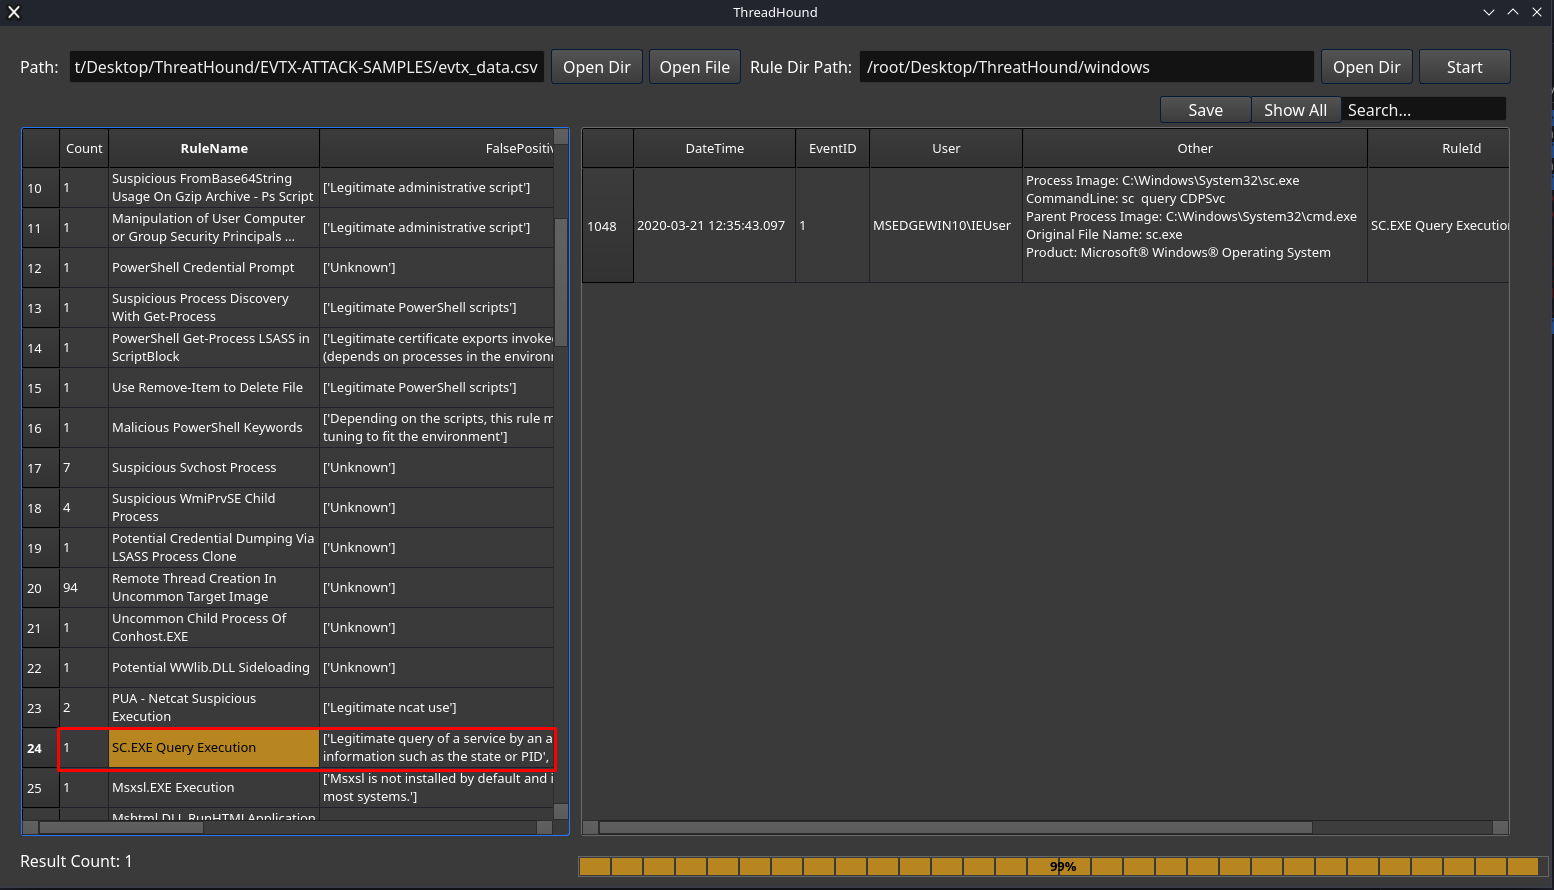 mazx0p/threathound
Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
 al0ne/cloud-audit
Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 osbornepro/btps-secpack
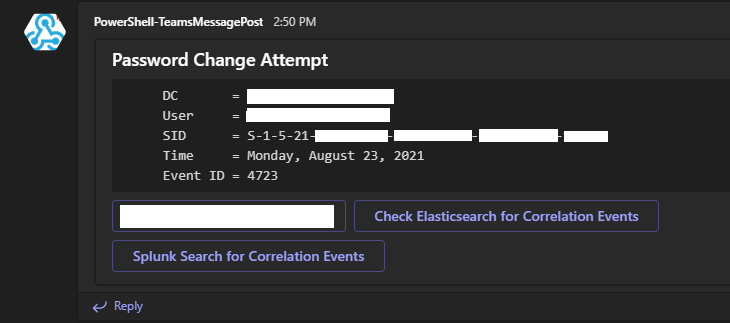
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 lethal-forensics/macos-collector
macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 yossisassi/zerologon-exploitation-check
quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…
 onsec-fr/cve-2019-19781-forensic
Automated forensic script hunting for cve-2019-19781