mimikatz-detector-condrv

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…

The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…

Automate stopping bad bots from accessing your server

Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…

Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…

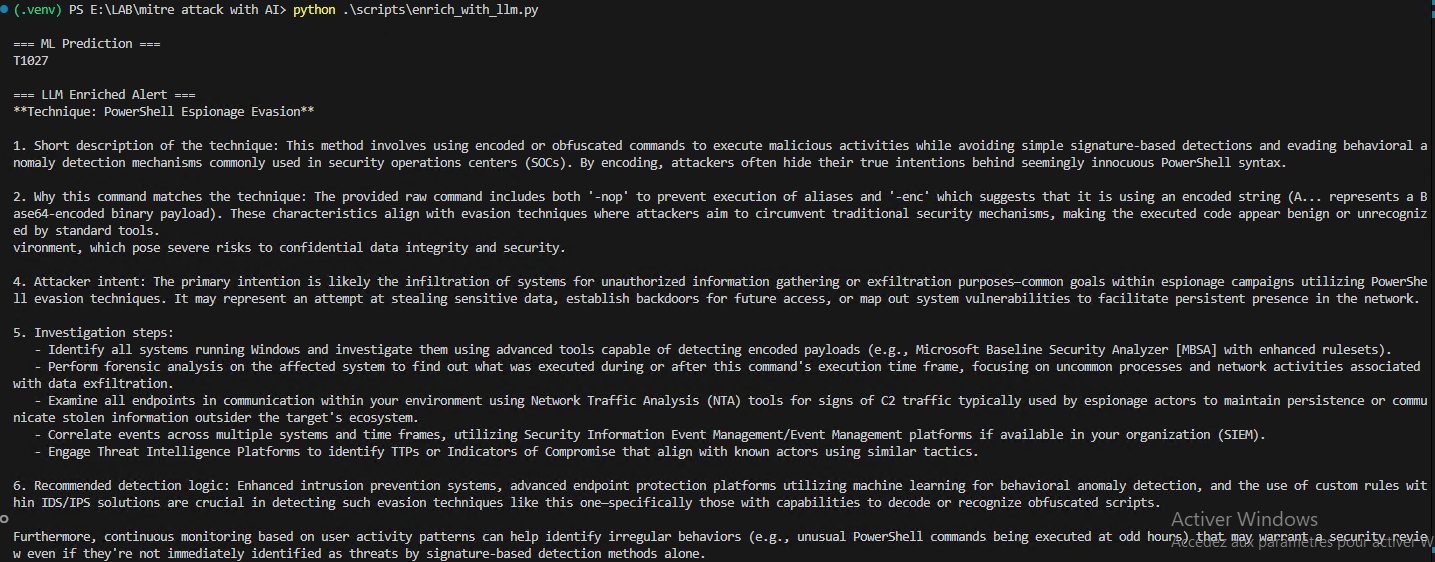
This repository demonstrates a machine learning pipeline for detecting MITRE ATT&CK techniques from logs and enriching the output using a local LLM.

Collects multi-source security logs from reproducible Docker attack scenarios, builds attack chains, and provides the SecLog-Bench-216 benchmark for…

Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…

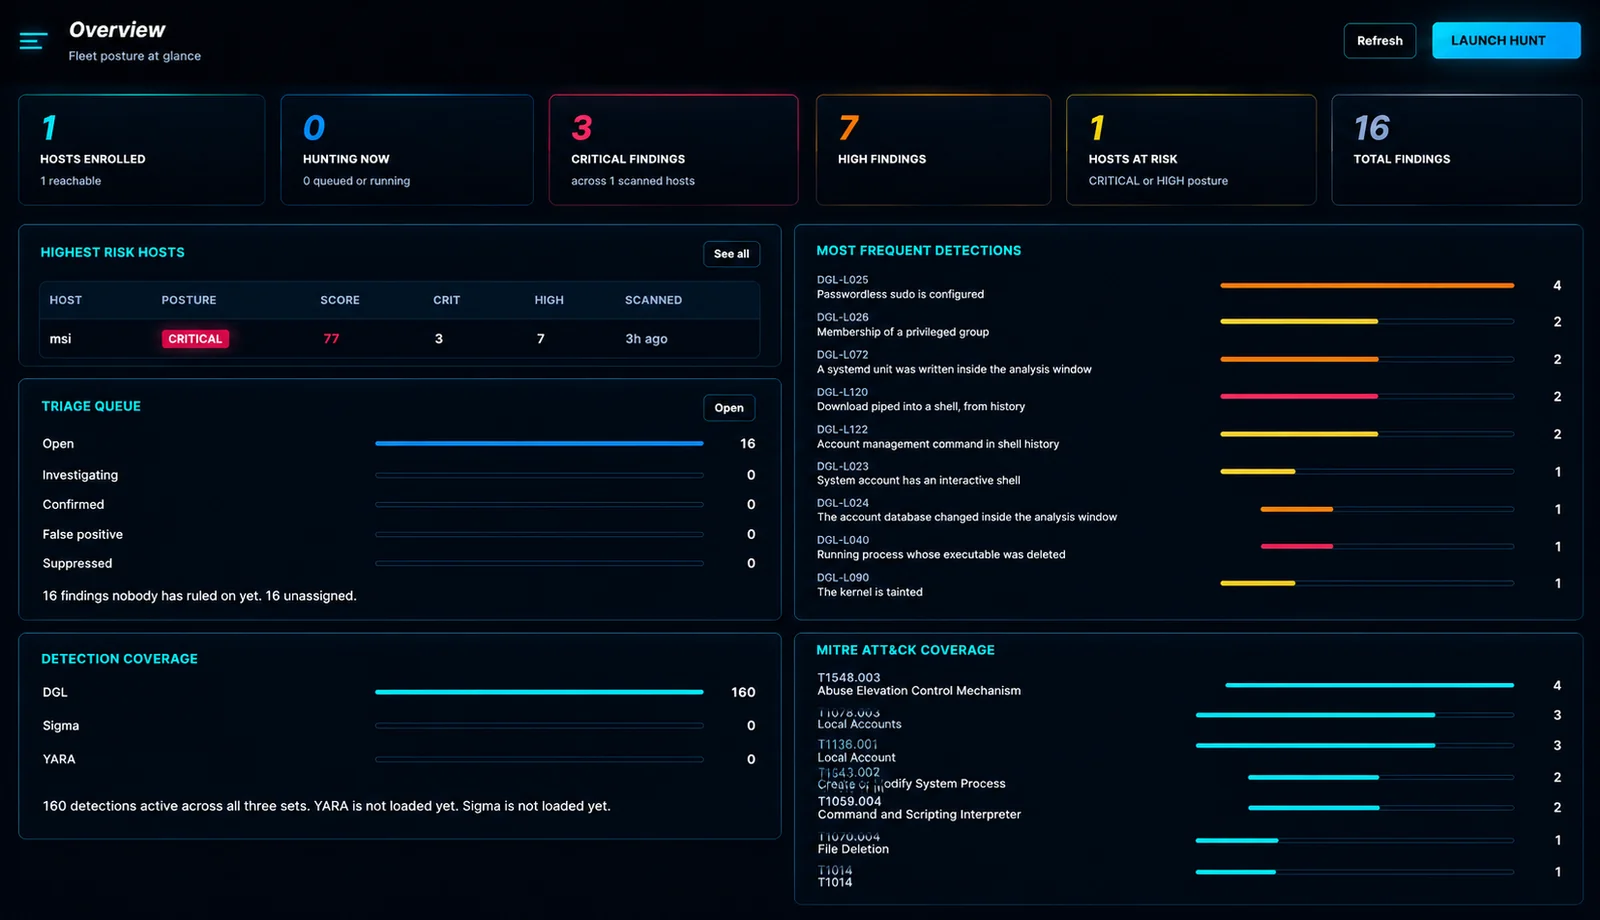
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…

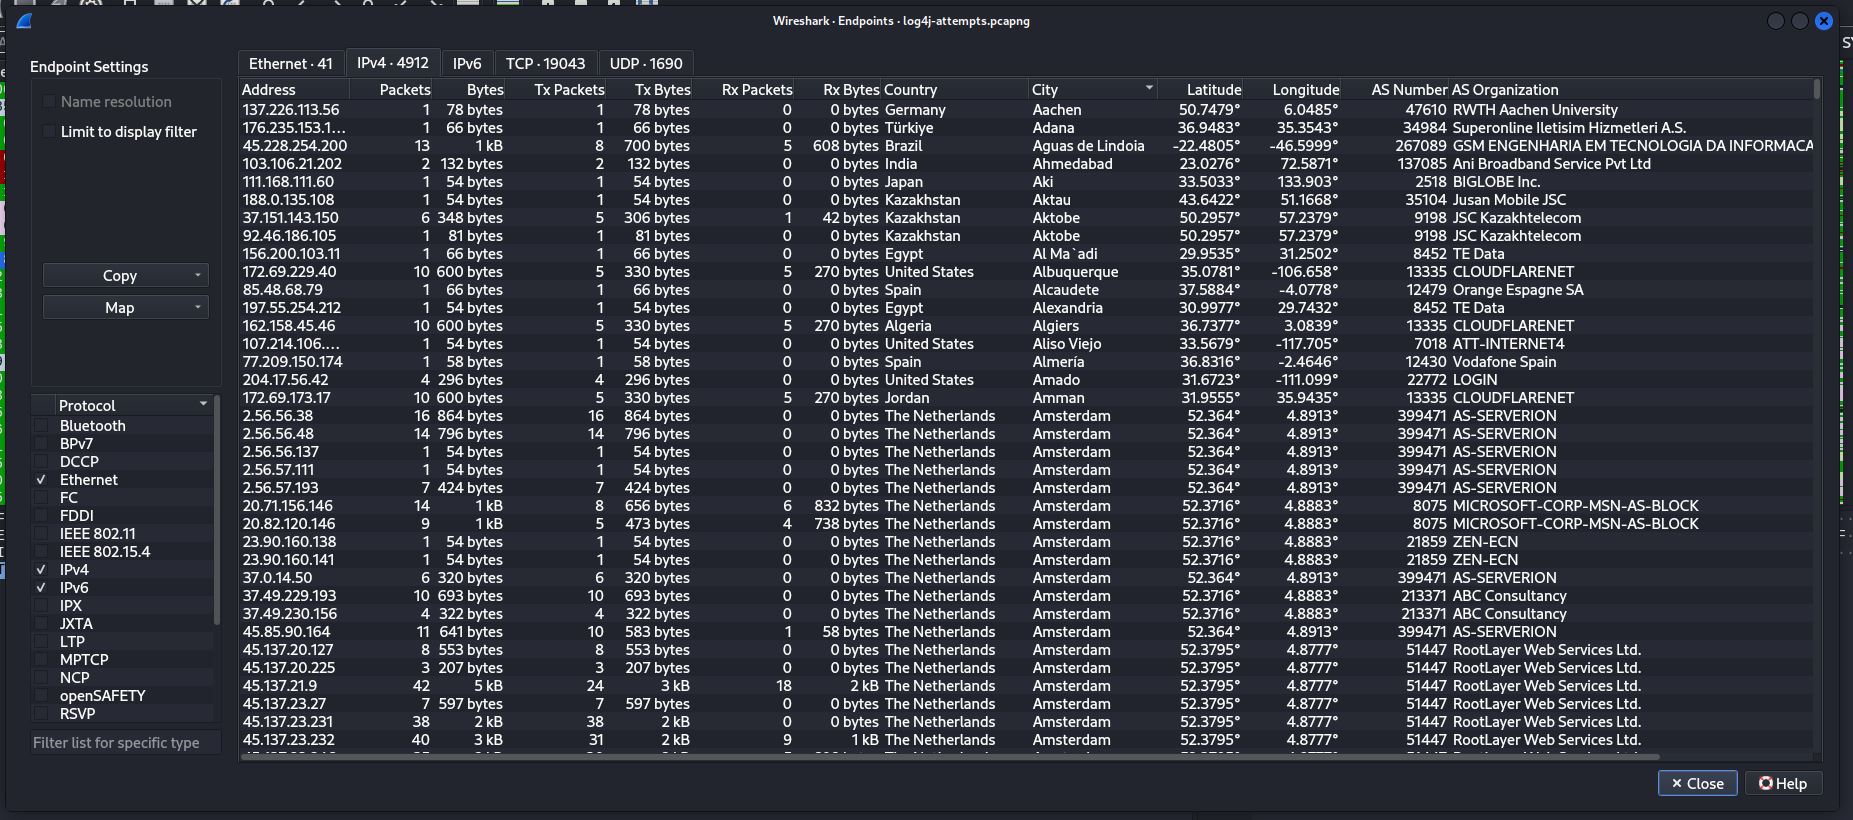
Downloaded a packet capture (.pcapng) file from malware-traffic-analysis.net which was an example of an attempted attack against a webserver using…

Extract useful information from PANOS support file for CVE-2024-3400

iOS Airborne vulnerabilities log artifact extractor from LogArchive CVE-2025-24252

Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…

Audit Guide for the Citrix ADC Vulnerability CVE-2019-19871. Collected from multiple sources and threat assessments. Will be updated as new methods…

Deception-engineering tools pulled from a production platform that takes live attacker traffic, supply-chain canary tokens, honeypot logs → MITRE…

Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…

Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…

Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…