
Zeek-CVE-Enrichment
 corelight/zeek-cve-enrichment
Zeek script and Python utility to enrich network security monitoring logs with CVE identifiers for improved threat intelligence and vulnerability…
incident-responseioc-managementlog-analysis+3
1
corelight/zeek-cve-enrichmentZeek script and Python utility to enrich network security monitoring logs with CVE identifiers for improved threat intelligence and vulnerability…
 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
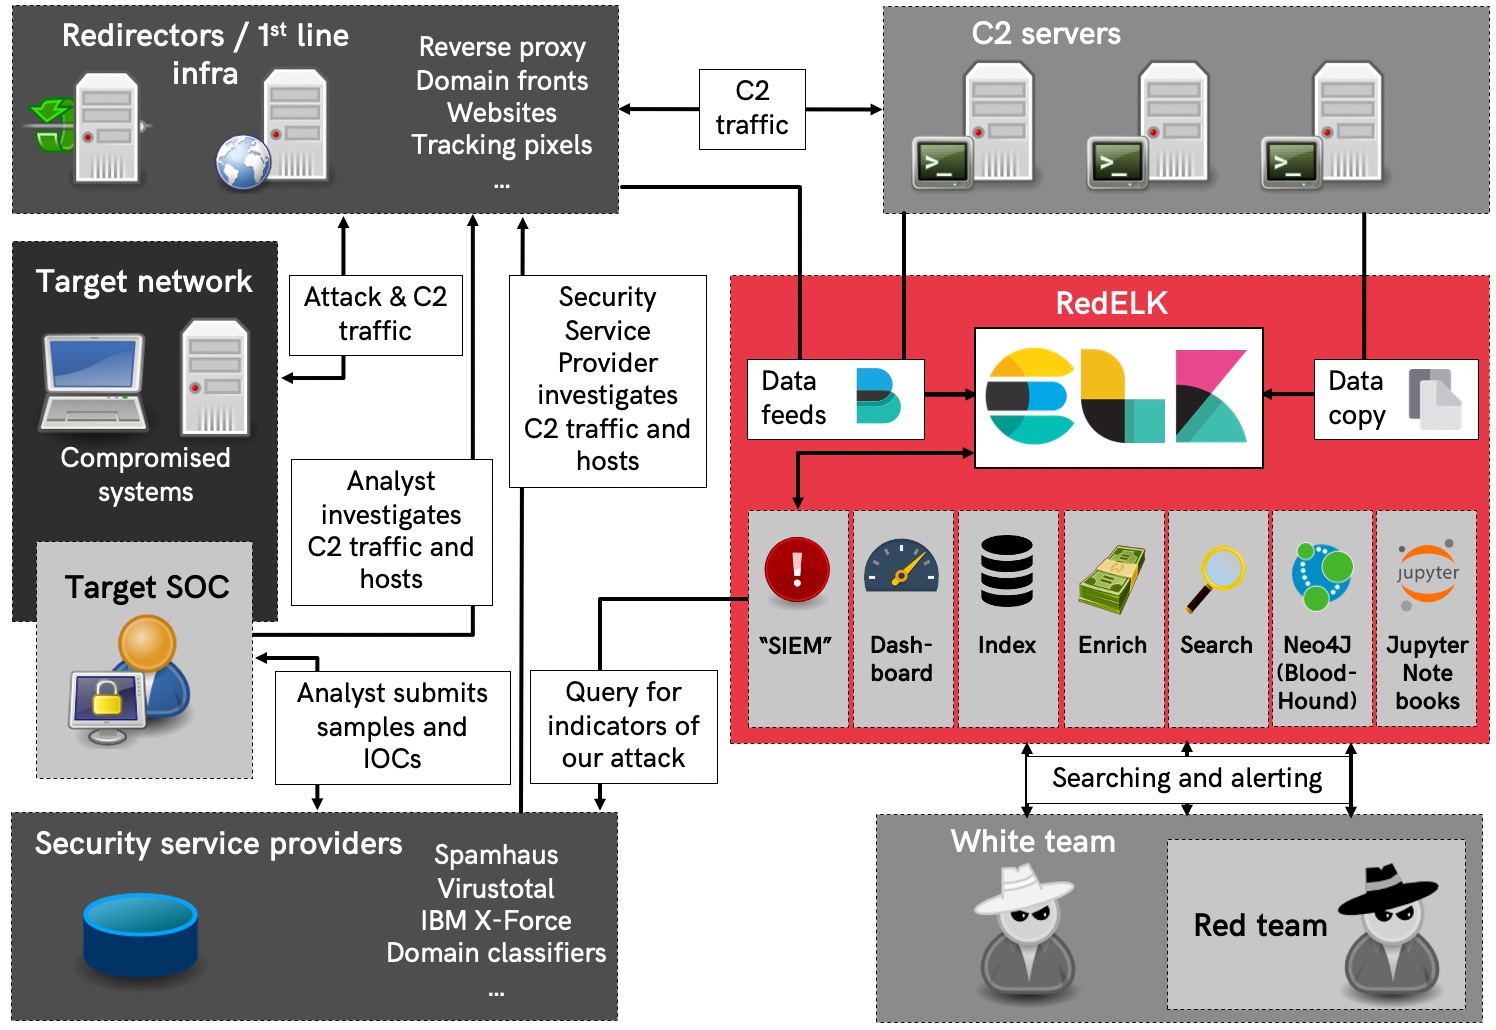 outflanknl/redelk
Red Team's SIEM - tool for Red Teams used for tracking and alarming about Blue Team activities as well as better usability in long term operations.
 dshield-isc/dshield
Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 zephrfish/cve-2025-53770-scanner
ToolShell scanner - CVE-2025-53770 and detection information
 yossisassi/zerologon-exploitation-check
quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…
 k11h-de/bbot-ui
a terminal UI to browse bbot reports
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 randomrobbiebf/cve-2023-47529
Cloud Templates & Patterns collection <= 1.2.2 - Sensitive Information Exposure via Log File
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 rv4l3r3/log4v-vuln-check
This script is used to perform a fast check if your server is possibly affected by CVE-2021-44228 (the log4j vulnerability).