

SnafflerParser
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
data-exfiltrationinformation-gatheringlog-analysis+5
150
zh54321/snafflerparserParses Snaffler output file and generate beautified outputs.
 t4d/phishingkithunter
Find phishing kits which use your brand/organization's files and image.
 abdulrhmanalfaifi/fennec
Artifact collection tool for *nix systems
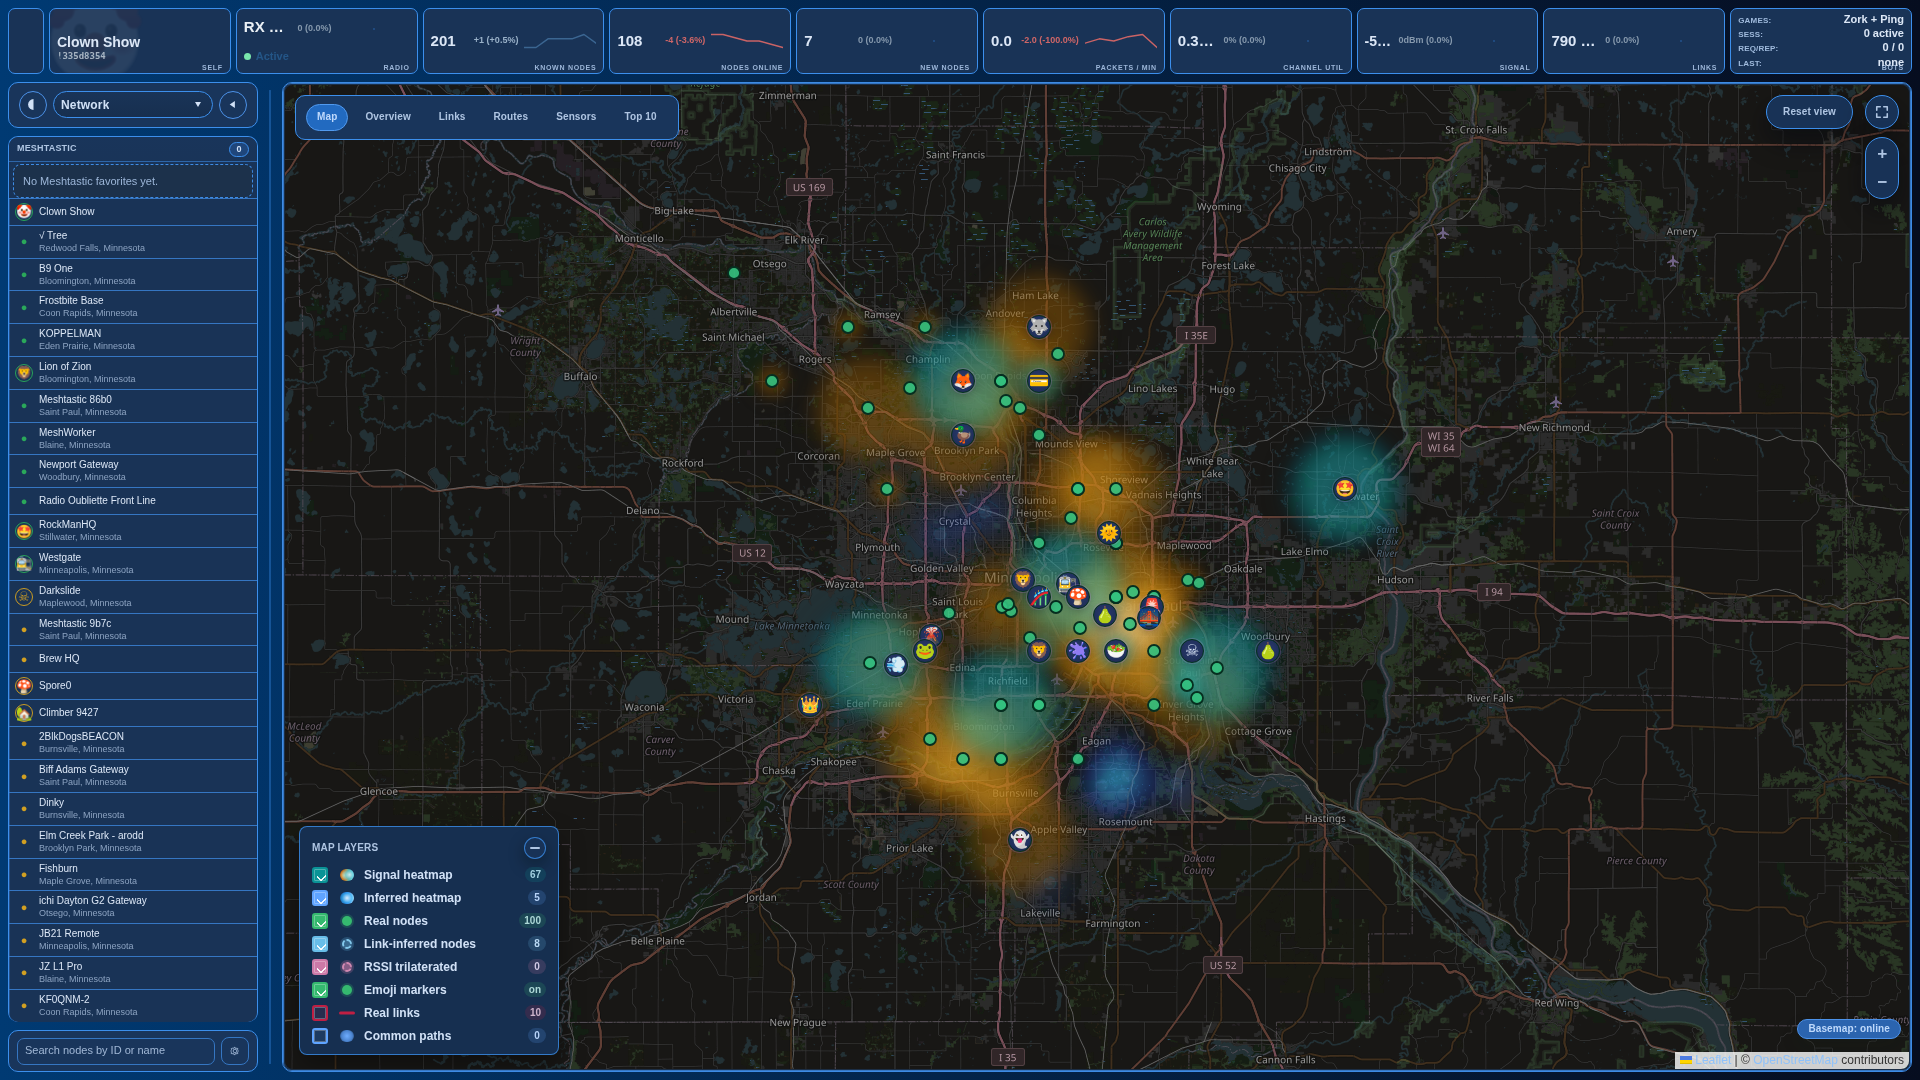 jaronmcd/meshyface
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 ctrlaltint3l/intelligence
Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 jangeisbauer/gundog
gundog - guided hunting in Microsoft Defender
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
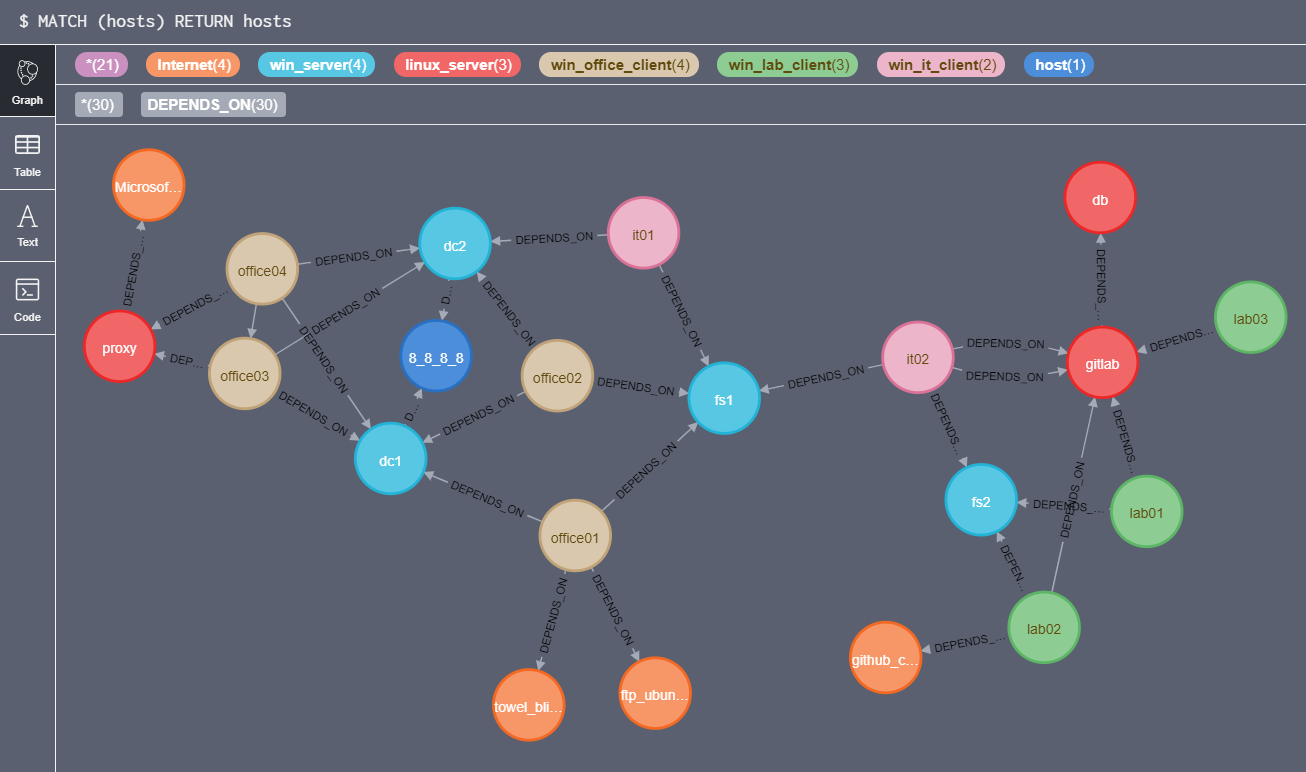 trinitor/netstat2neo4j
create cypher create statements for neo4j out of netstat files from multiple machines
 rootly-ai-labs/rootly-graphify-importer
Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
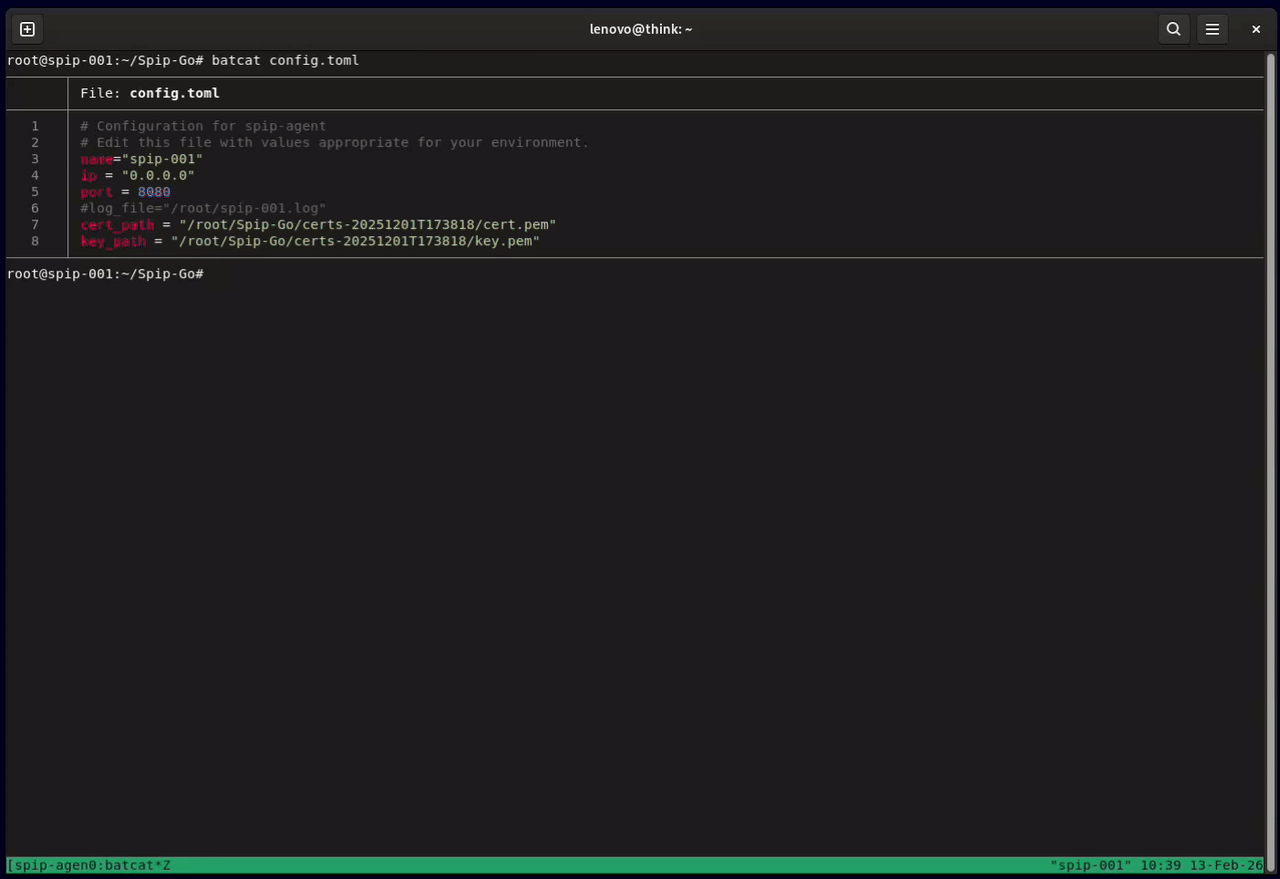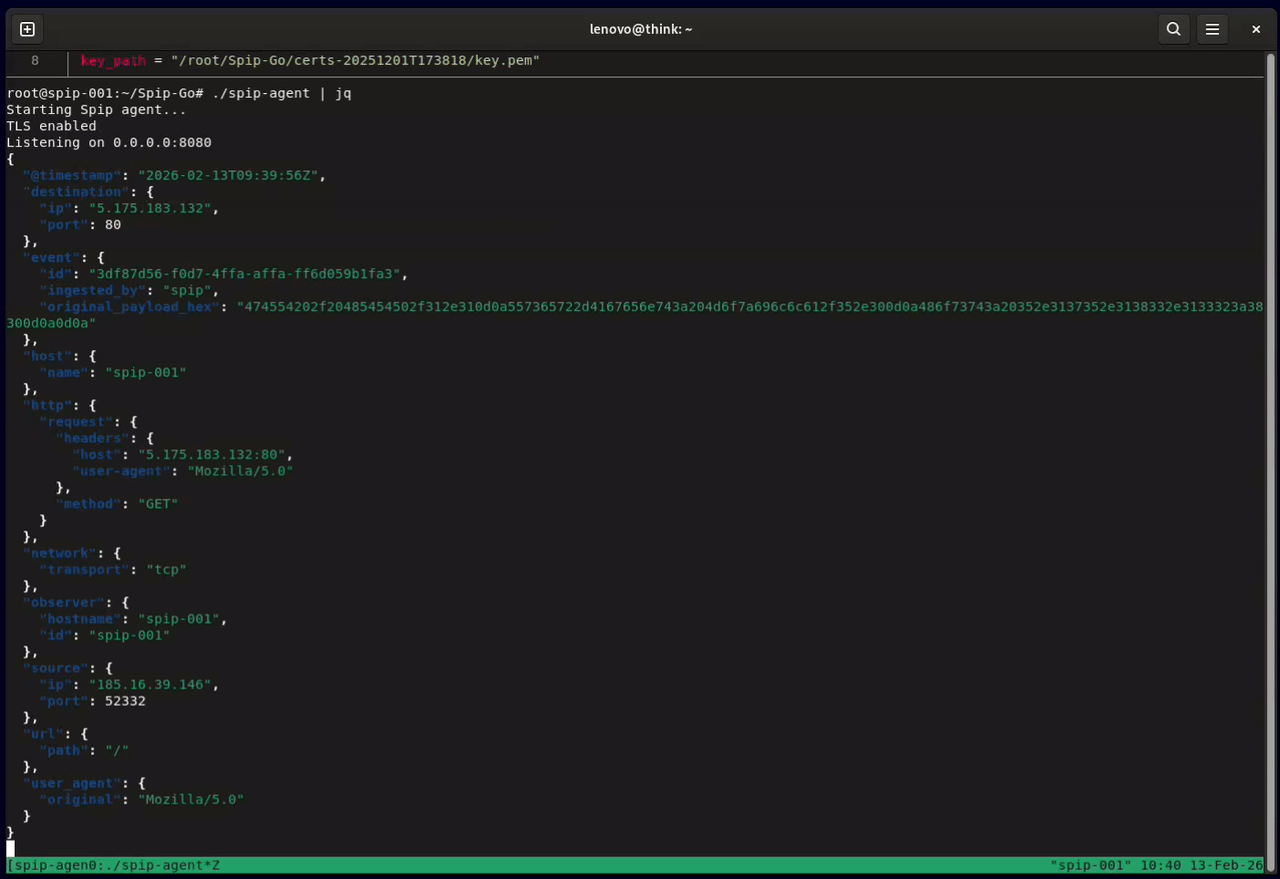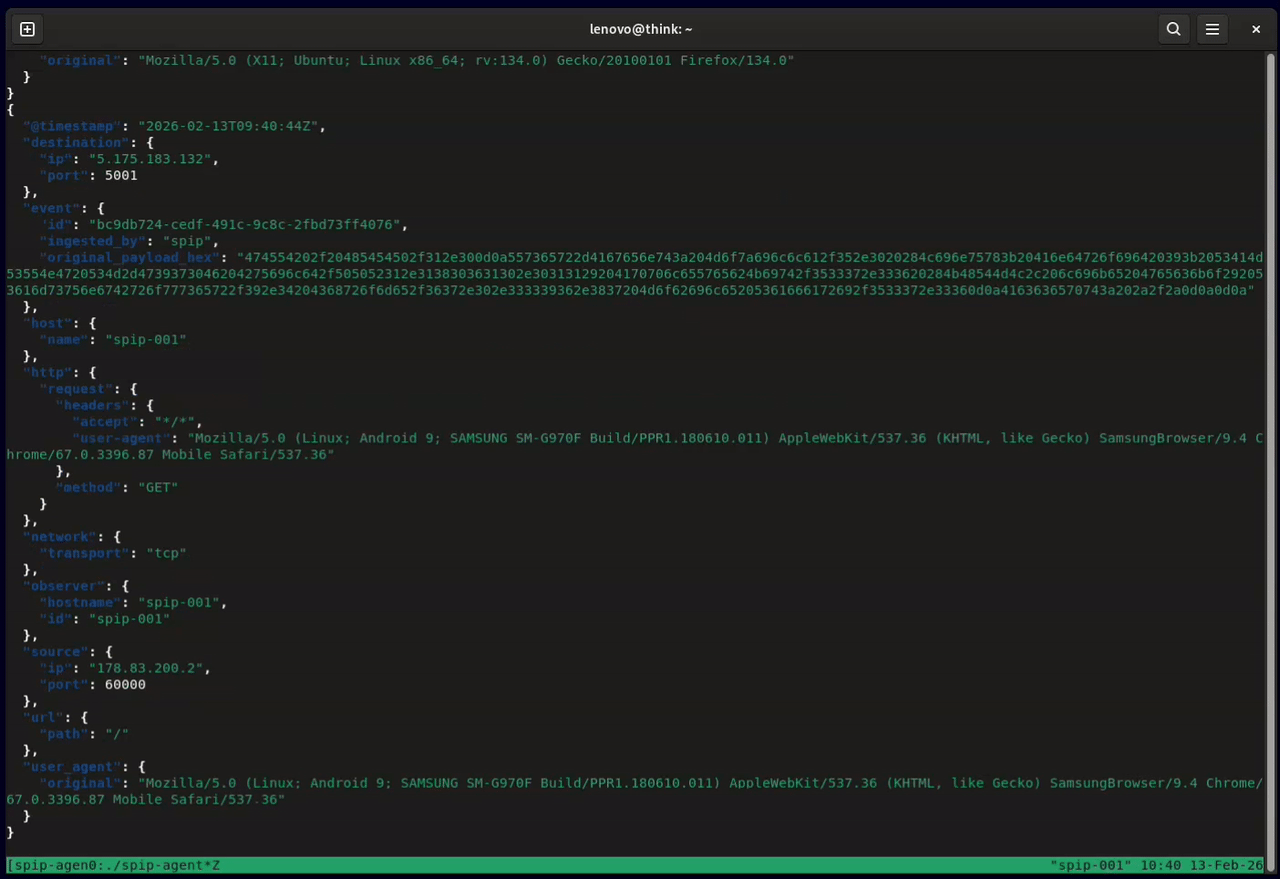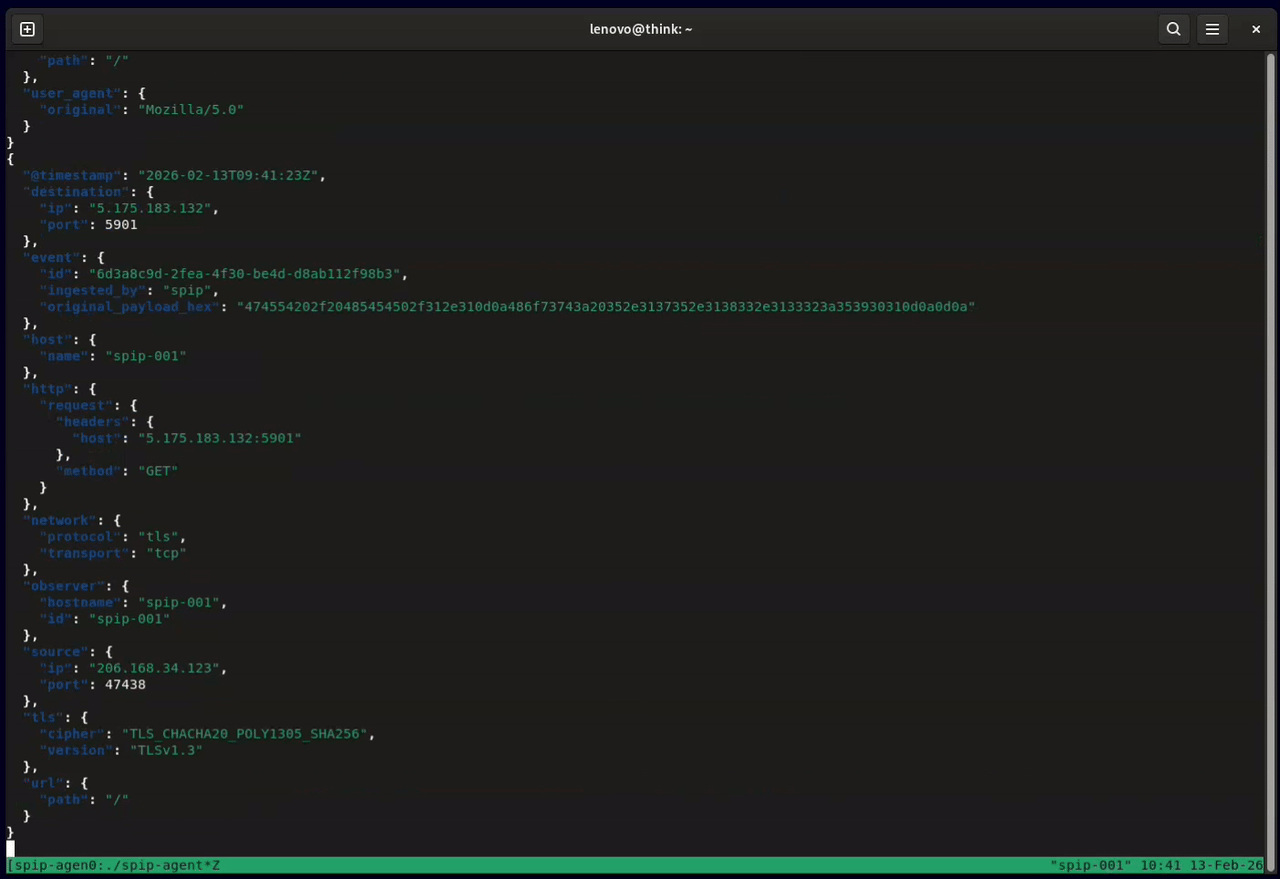 honeylabshq/spip-go
Spip network sensor written in Go
 corelight/top-dns
Top DNS Measurement for Bro
 yossisassi/zerologon-exploitation-check
quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…
 k11h-de/bbot-ui
a terminal UI to browse bbot reports