ZeroLogon-Exploitation-Check

quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…

quick'n'dirty automated checks for potential exploitation of CVE-2020-1472 (aka ZeroLogon), using leading artifects in determining an actual…

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…


A modern and elegant dashboard for network traffic visualization and analysis.

A curated list of awesome Security Hardening techniques for Windows.

A Python package and CLI for parsing aggregate and forensic DMARC reports

A script that helps you understand why your E-Mail ended up in Spam

Passive DNS Capture and Monitoring Toolkit

Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.

Database Driven DNS Server with a Web UI

PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…

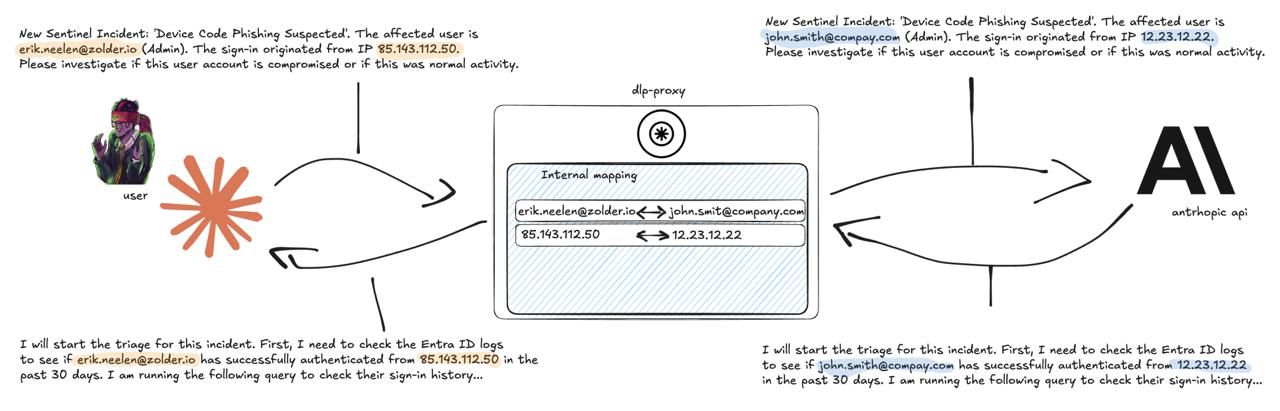
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…

Post-Exploitation EVTX Analyzer for BloodHound Mapping

PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Check for events that indicate non compatible devices -> CVE-2020-1472

Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…