
sleep_python_bridge
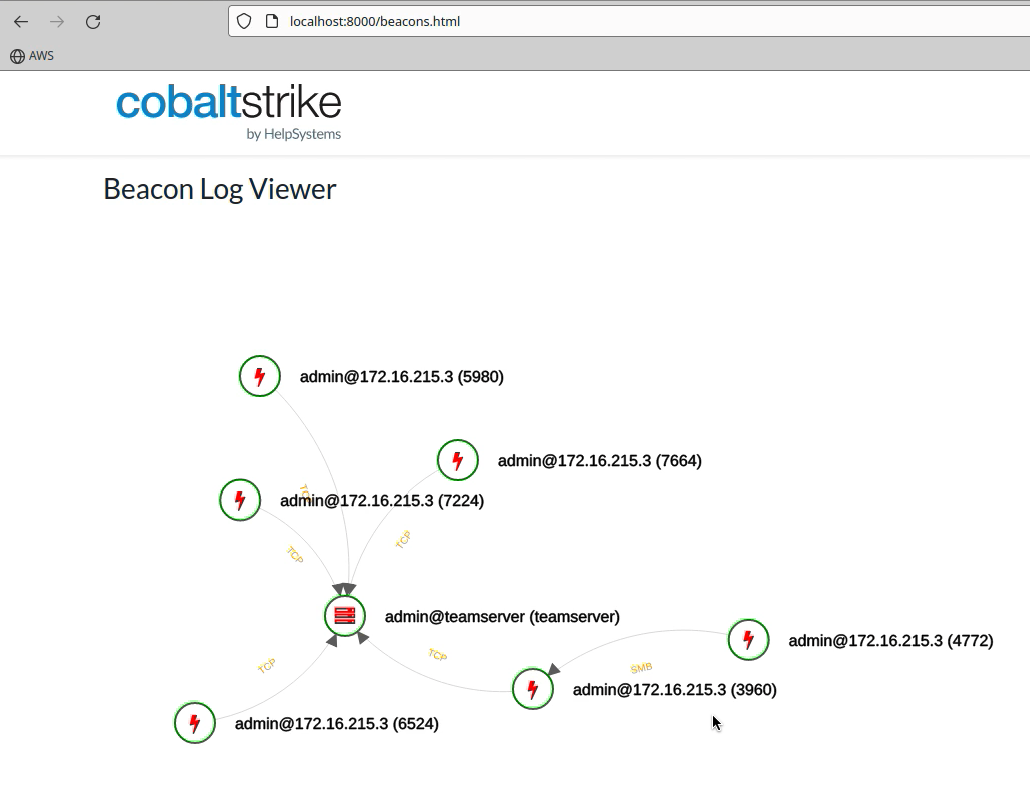
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

A python package for use in generating fake data for SOC and security automation.

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…

Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…

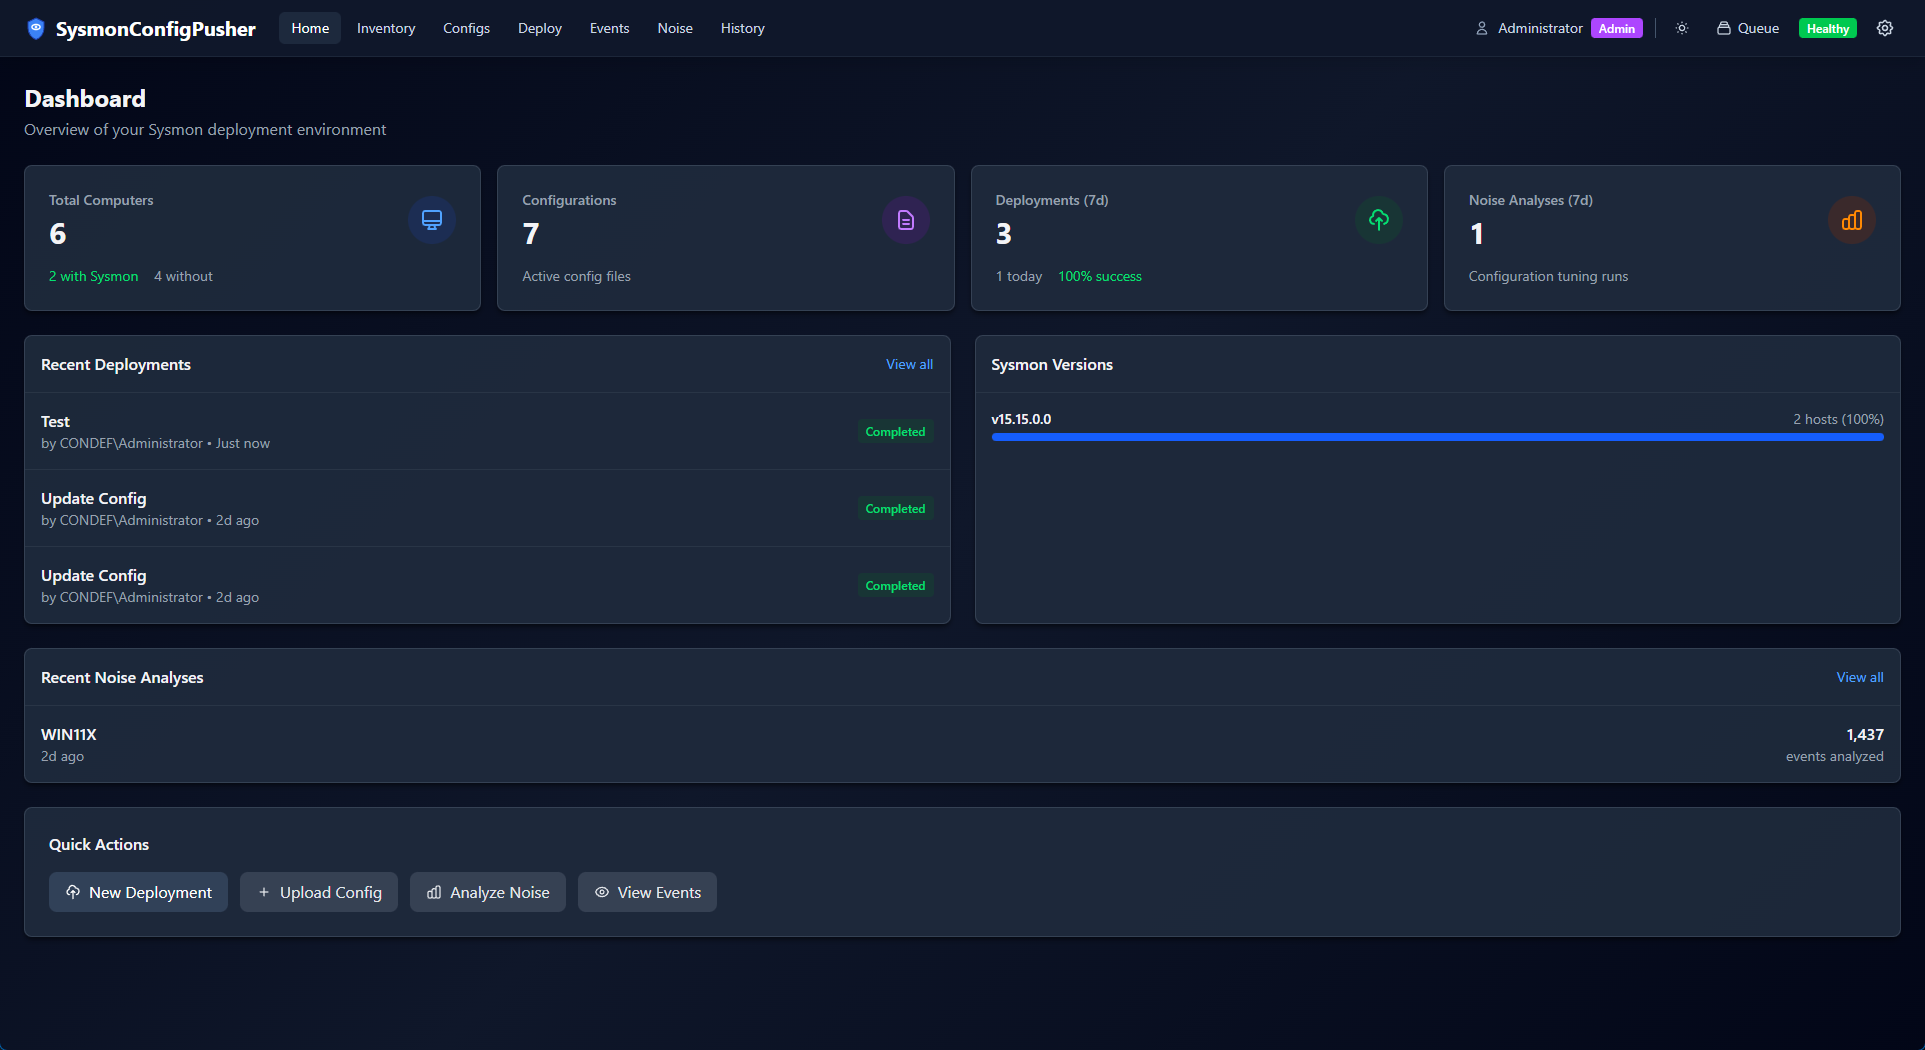
Web-based tool for managing and deploying Sysmon configurations across Windows endpoints via agentless (WMI/SMB) or agent-based methods, with remote…

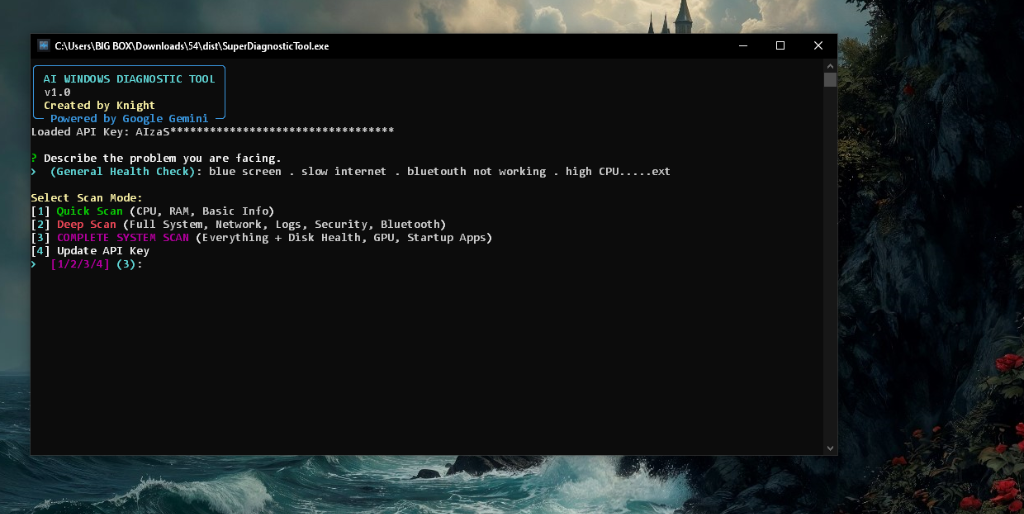
AI-powered Windows diagnostic & auto-repair tool using Google Gemini. Detect crashes, optimize performance, scan for malware, and generate PowerShell…

ESF modular ingestion tool for development and research.

Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…

Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…

Chronicle parser for CORELIGHT and related information.

This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…

Corelight Dashboards and Parsers for Sentinel One Singularity

CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…

Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…

Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…

Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.

Provides BigFix Fixlets and analyses to detect Log4j vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105) across Windows and Linux…