
Nimbus Vestige
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
cloud-securitydigital-forensicseducation+6
2
dobybaxter127/nimbus-vestigeA forensic reconstruction engine for cloud and identity incident response.
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
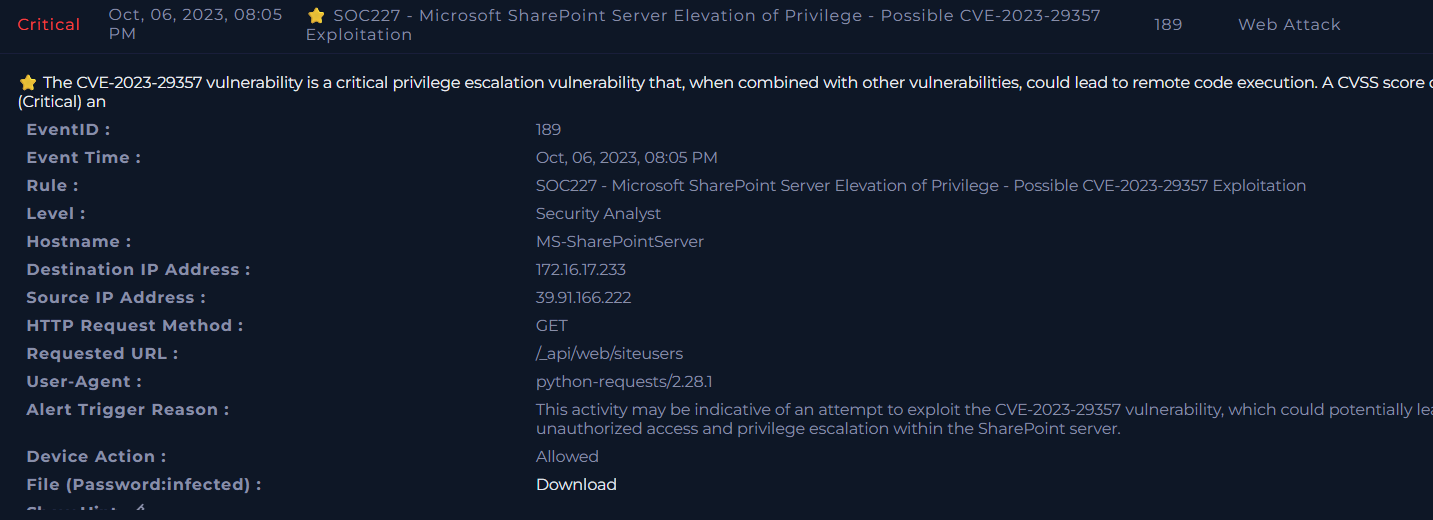 zedocun/sharepoint-cve-2023-29375-incident-response
End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29357) using SIEM logs,…
 velessecurity/cve-2021-1675-printnightmare-analysis
Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 fabianch20/soc335---cve-2024-49138-exploitation-detected
SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…
 glebusalt/cybersecurity_portfolio
Практические кейсы по информационной безопасности: развёртывание SIEM Wazuh и эксплуатация CVE-2021-41773
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 borsch-appreciator/soc235---atlassian-confluence-broken-access-control-0-day-cve-2023-22515
SOC analyst walkthrough triaging a Confluence CVE-2023-22515 broken access control exploitation attempt, covering log analysis, MITRE ATT&CK mapping,…
 chandanshastri/log4j_vulnerability_demo
A simple program to demonstrate how Log4j vulnerability can be exploited ( CVE-2021-44228 )
 chpratik/cve-2026-54121
Improper authorization in Active Directory Certificate Services (AD CS) allows an authorized attacker to elevate privileges over a network.
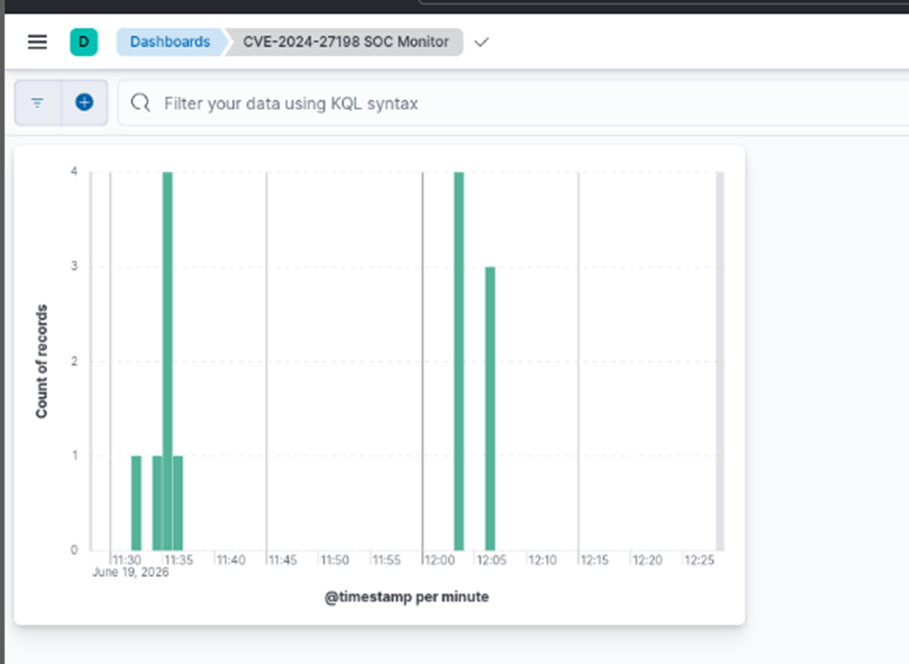 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
 iqx6889/cve-2026-52813-gogs-rce
CVE-2026-52813 (Gogs Path Traversal → Git Hooks RCE) defensive writeup: root-cause & patch analysis, Sigma/SIEM detection rules, IOCs, non-intrusive…