Adversarial-Detection-Engineering-Framework

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…

You didn't think I'd go and leave the blue team out, right?

Detect Tactics, Techniques & Combat Threats

AI runtime inventory: discover shadow AI, trace LLM calls

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.


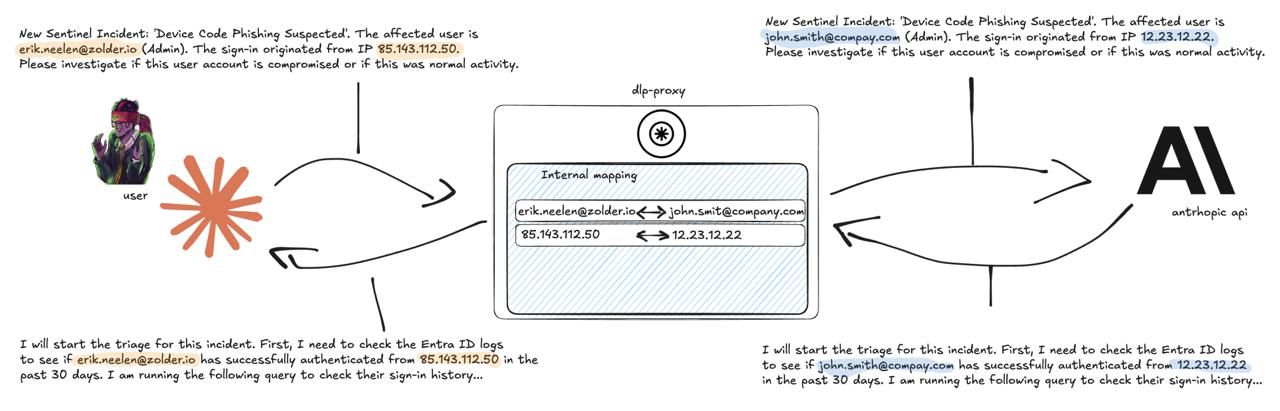
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…

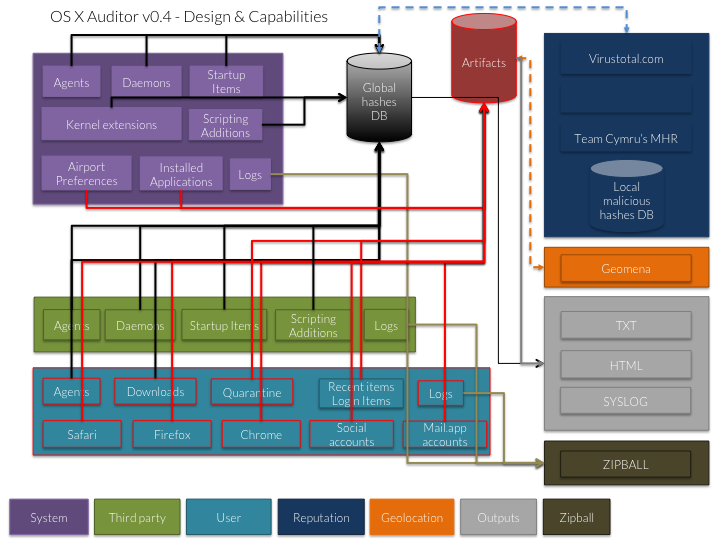
OS X Auditor is a free Mac OS X computer forensics tool