windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

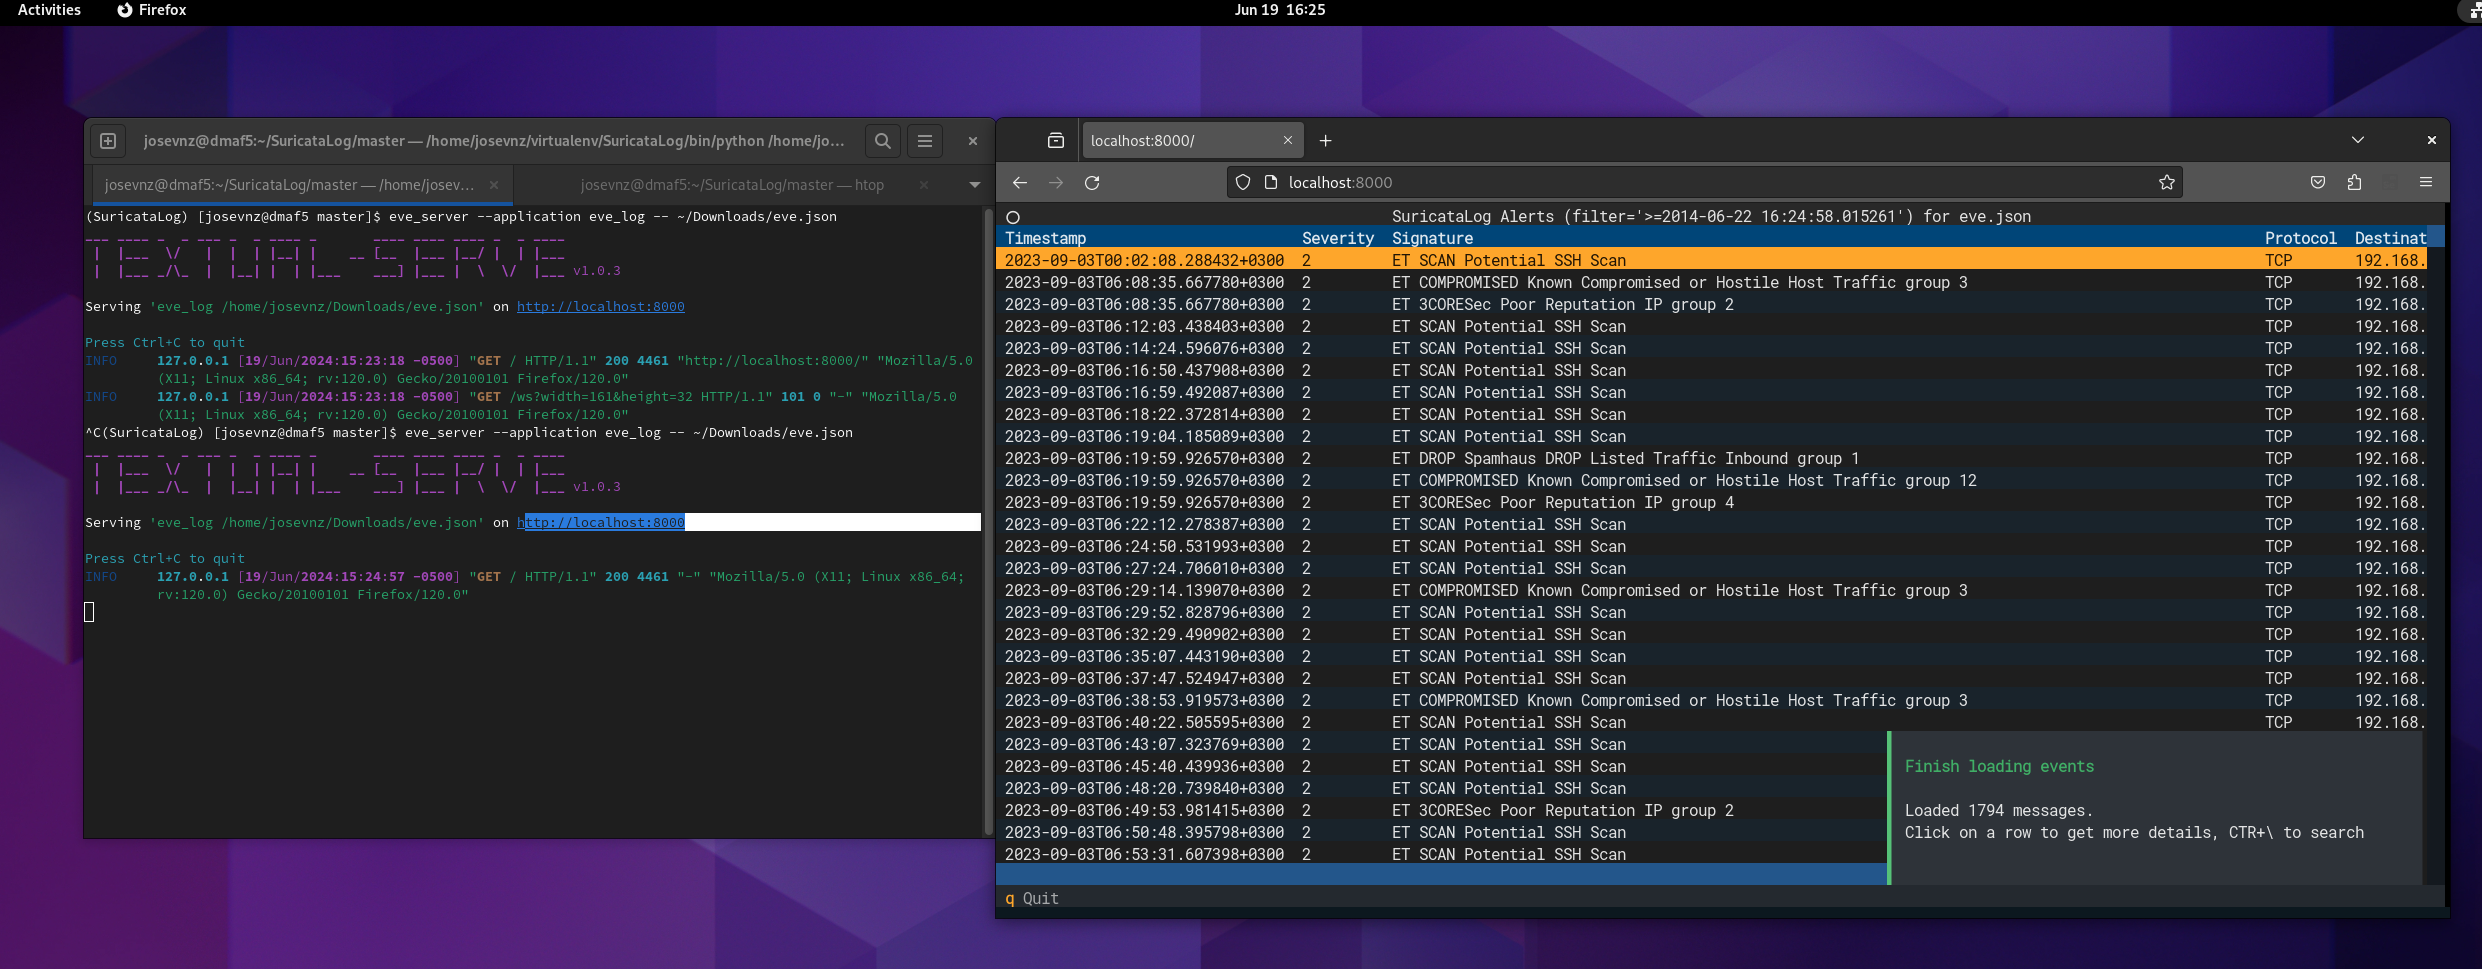
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…

An open-source, single-script CVE scanner for RMM-managed fleets. Pure PowerShell 7 — joins your RMM software inventory against NVD, CISA KEV, EPSS…

This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…

Chronicle parser for CORELIGHT and related information.

Hands-on analysis of common APT attack techniques, focused on how they show up in logs and how defenders can realistically detect them.

IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.

A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…

A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…

Powershell Based tool for gathering information related to O365 intrusions and potential Breaches

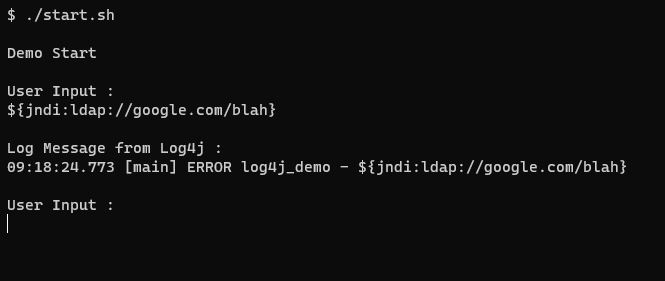
A simple program to demonstrate how Log4j vulnerability can be exploited ( CVE-2021-44228 )