logdata-anomaly-miner

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…

A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.

Cyber Threat Defense World Modeling

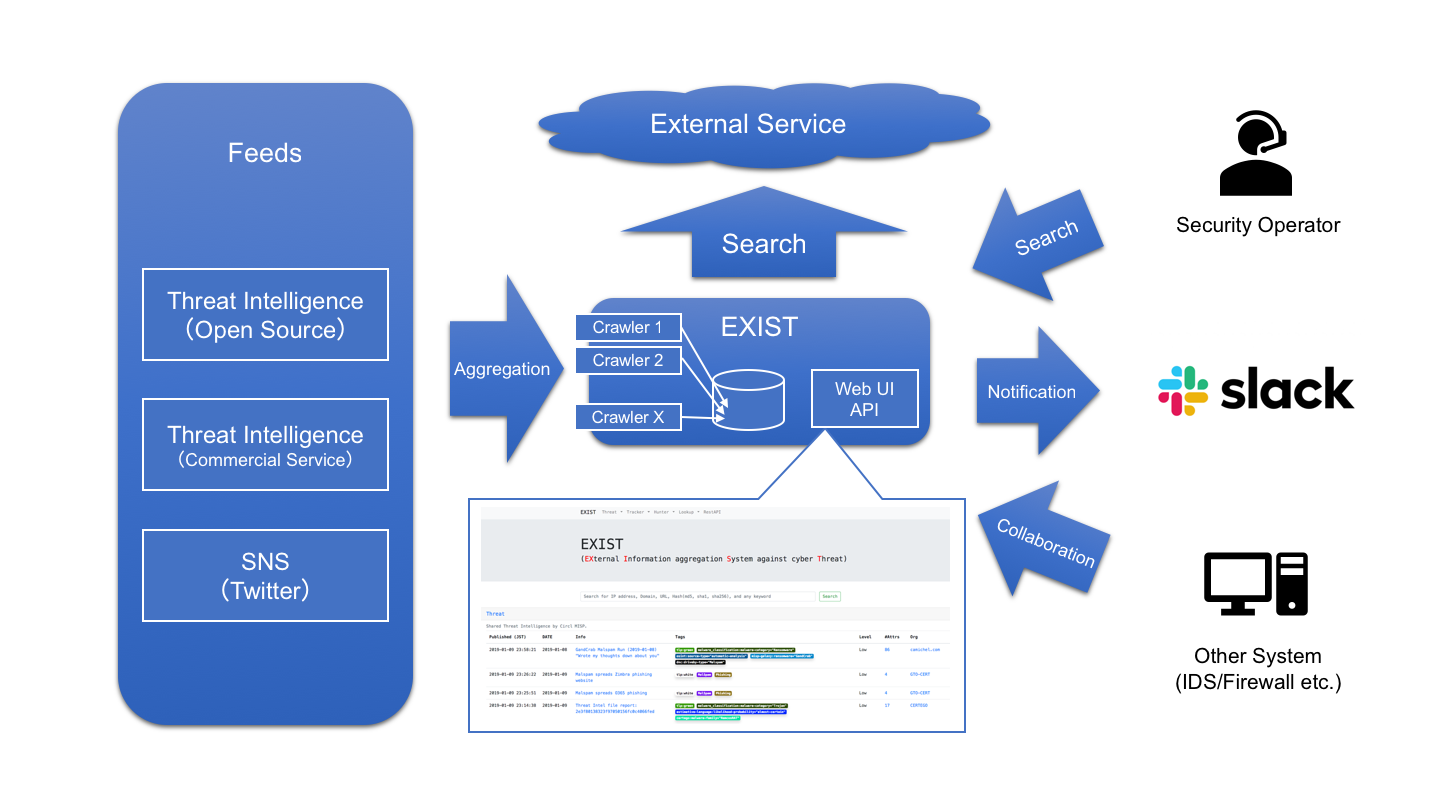
EXIST is a web application for aggregating and analyzing cyber threat intelligence.

MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs

USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…


A machine learning toolkit for log parsing [ICSE'19, DSN'16]

This project is a SIEM with SIRP and Threat Intel, all in one.

A machine learning toolkit for log-based anomaly detection [ISSRE'16]

Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.

The Intelligent Process Lifecycle of Active Cyber Defenders

A list of cyber-chef recipes and curated links

An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.