
preflight
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
code-analysisconfiguration-auditingdevsecops+8
62
preflightsh/preflightGo-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
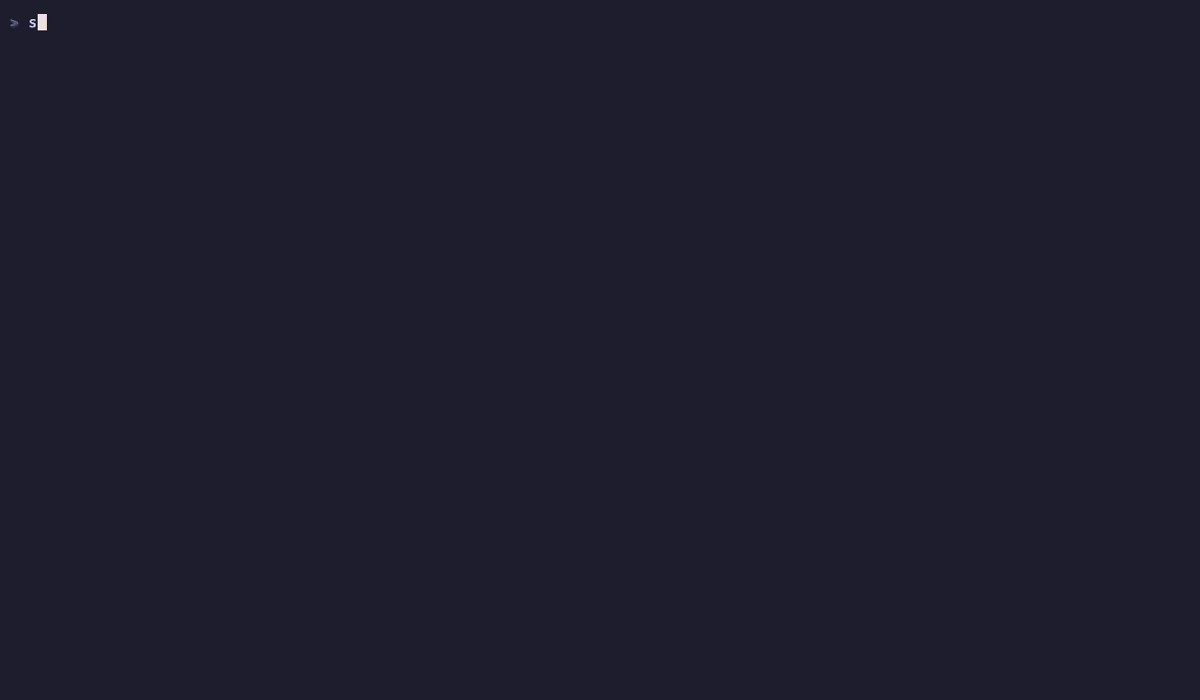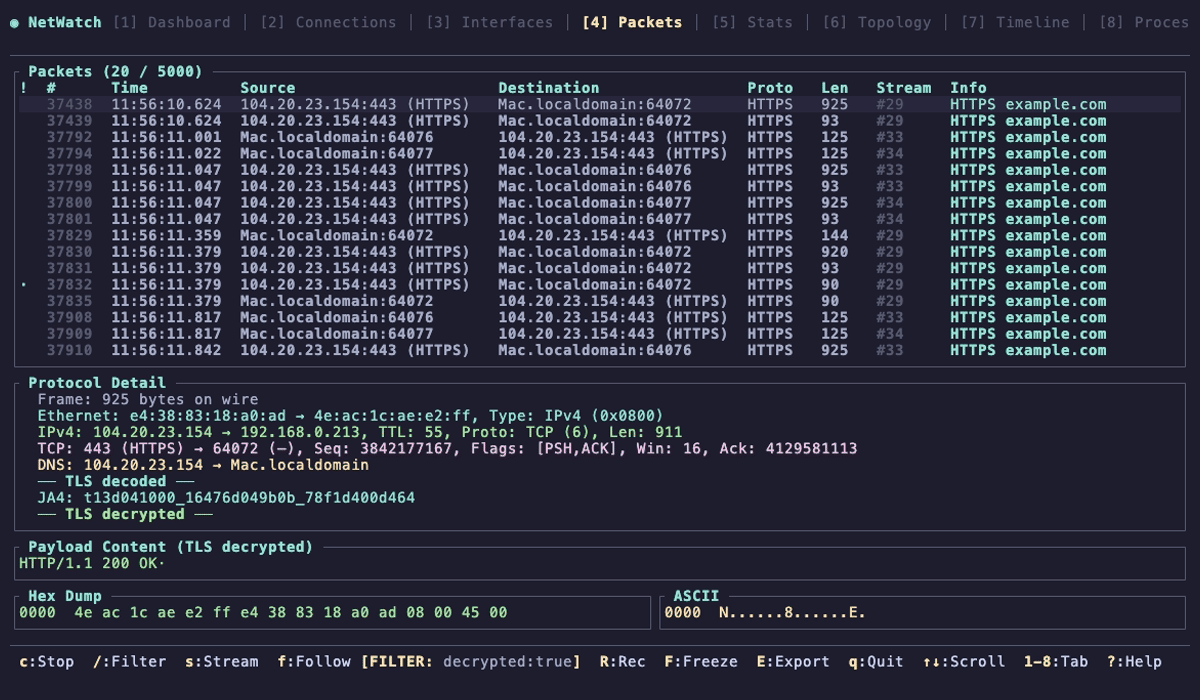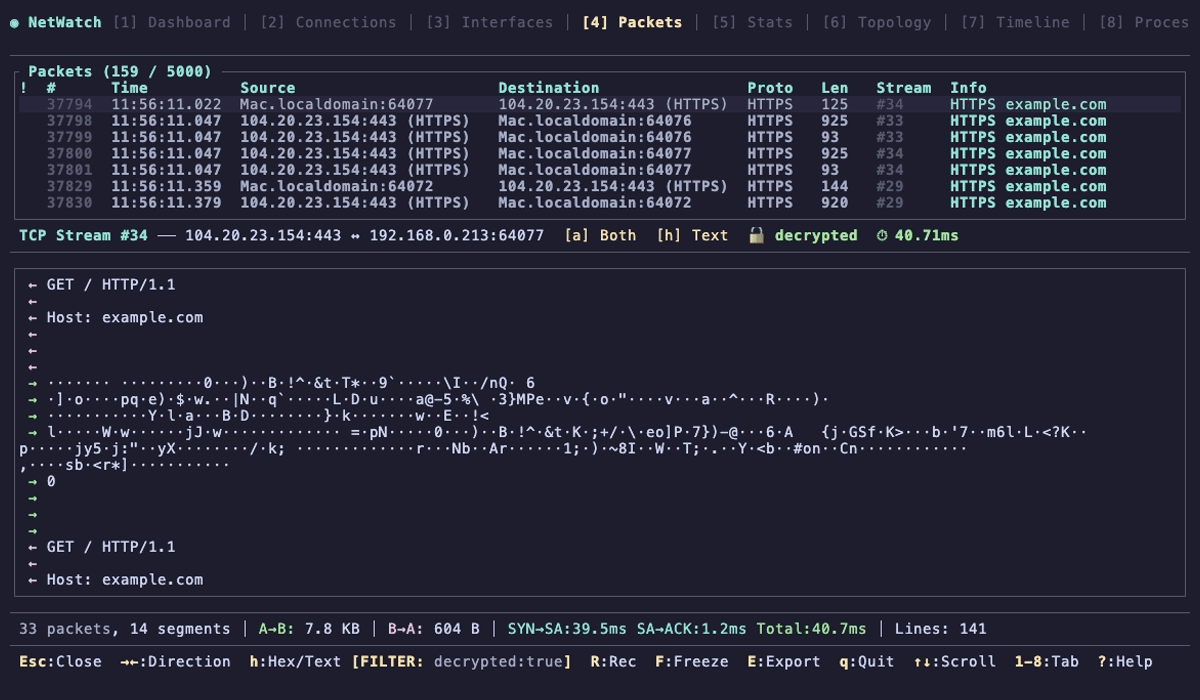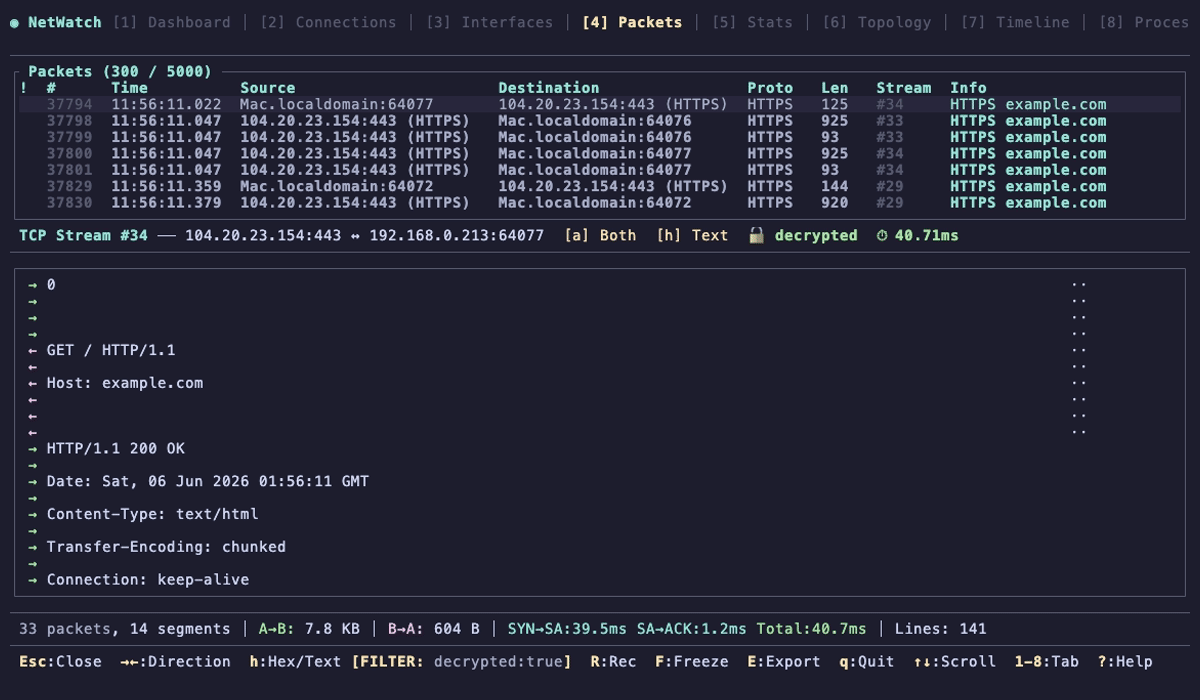 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 joshuagodwin7929/purple-team-automation
Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.
 purp1ew0lf/blue-team-notes
You didn't think I'd go and leave the blue team out, right?
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
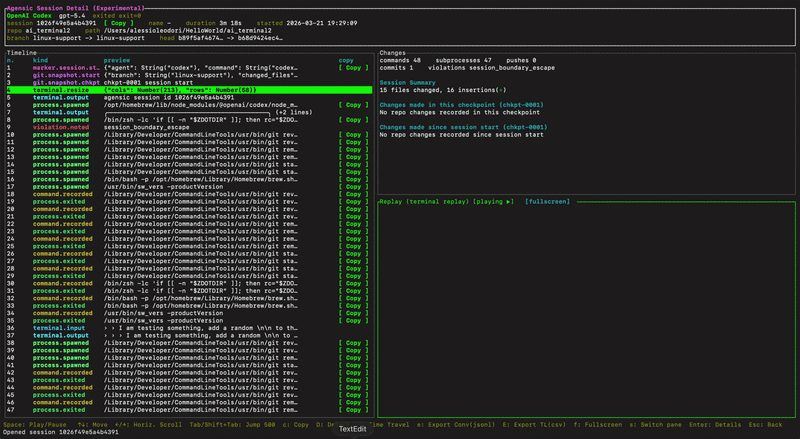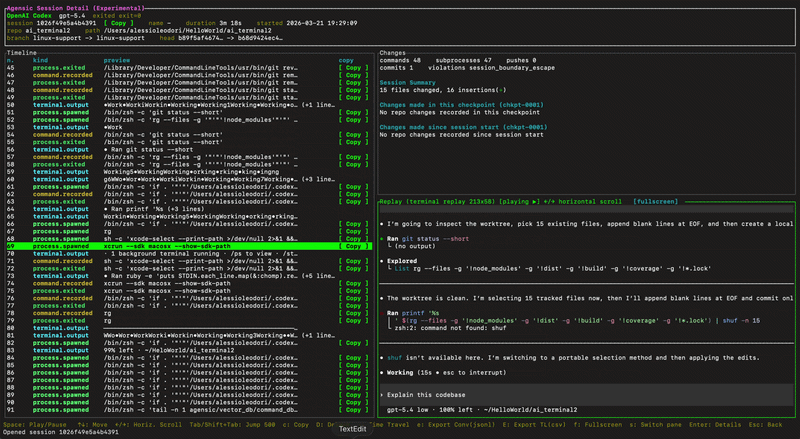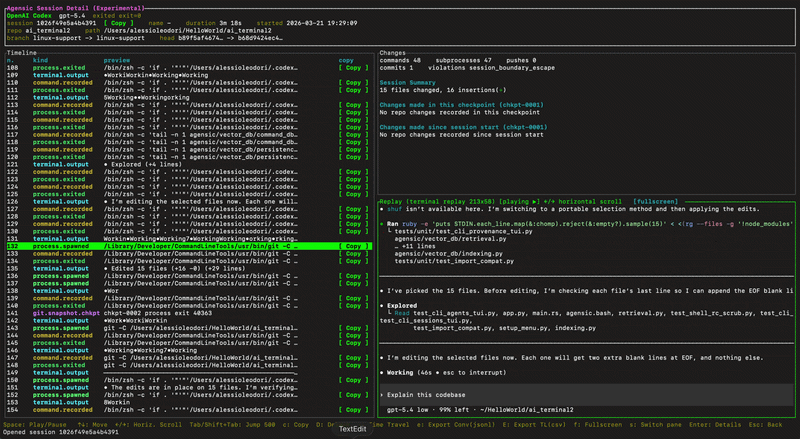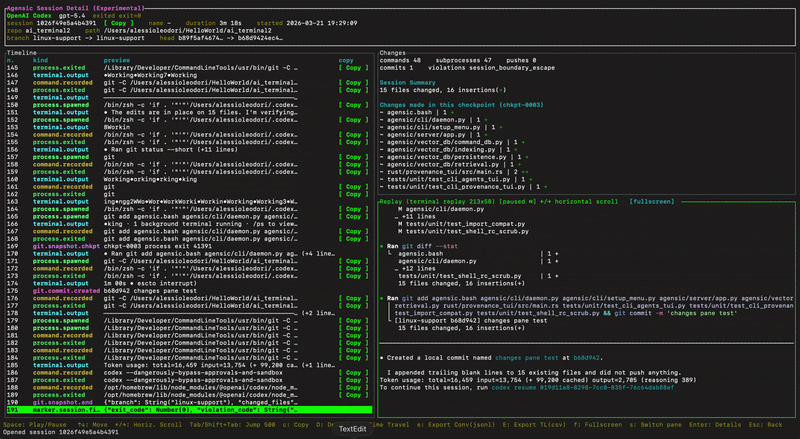 alex188dot/agensic
Cryptographic terminal forensics and session replay for AI agents. Tracks, signs, and audits every command with provenance labels, replayable…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
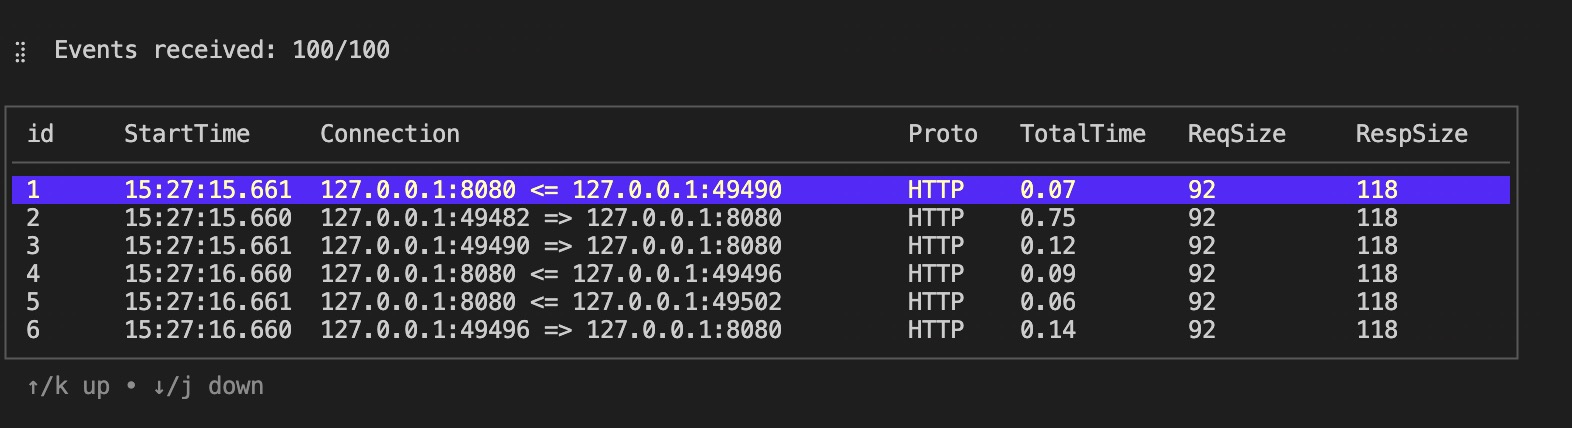 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
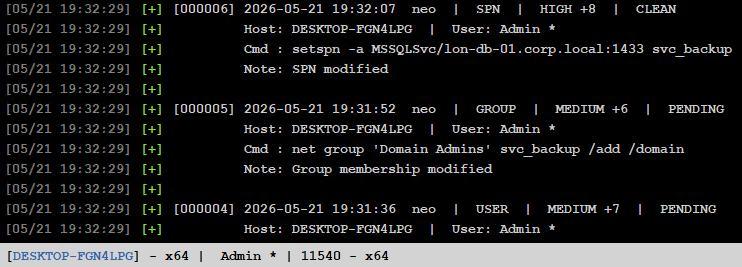 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
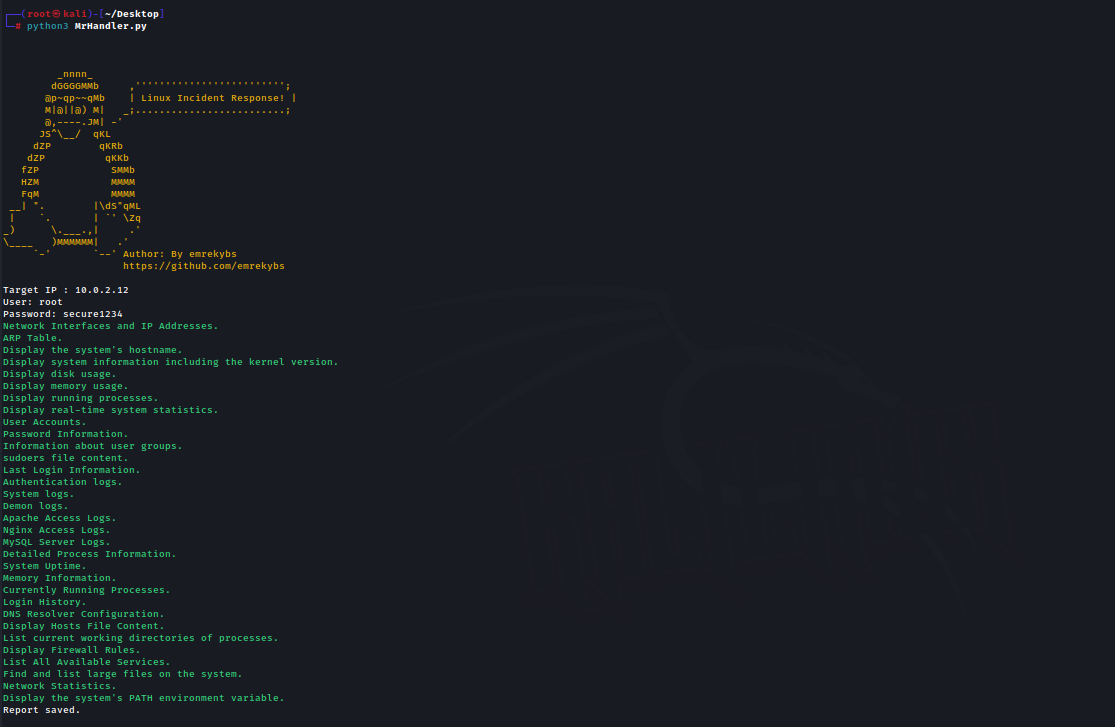 emrekybs/mrhandler
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 ayush-parab/sentinel-gpt
Automated threat hunting pipeline that ingests Azure logs, uses LLM reasoning to detect suspicious activity, assess risk, and generate remediation…
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation