log-horizon
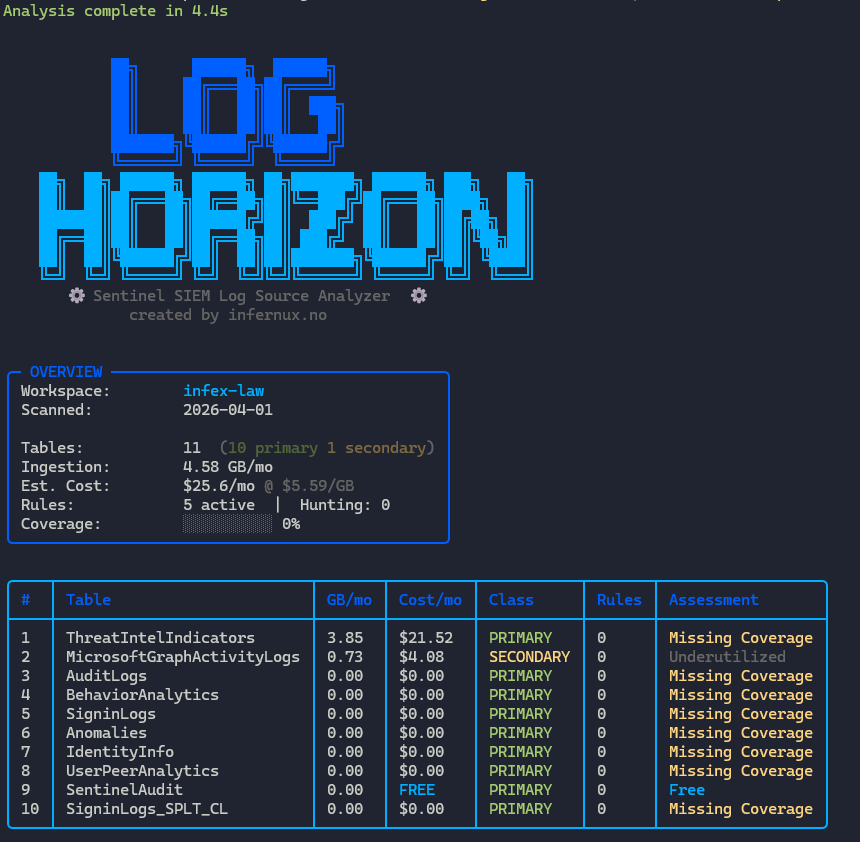
 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
2917 days ago
lnfernux/log-horizonMicrosoft Sentinel SIEM Log Source Analyzer
 corelight/extendintel
This package extends the Intel package to log more fields
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
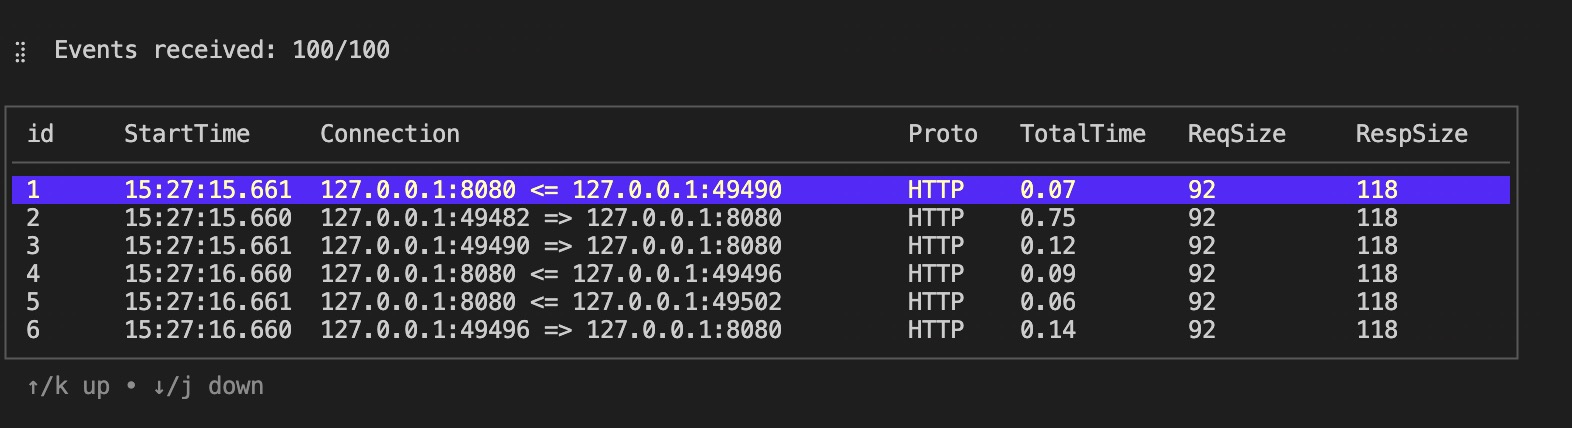 hengyoush/kyanos
Kyanos is a networking analysis tool using eBPF. It can visualize the time packets spend in the kernel, capture requests/responses, makes…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
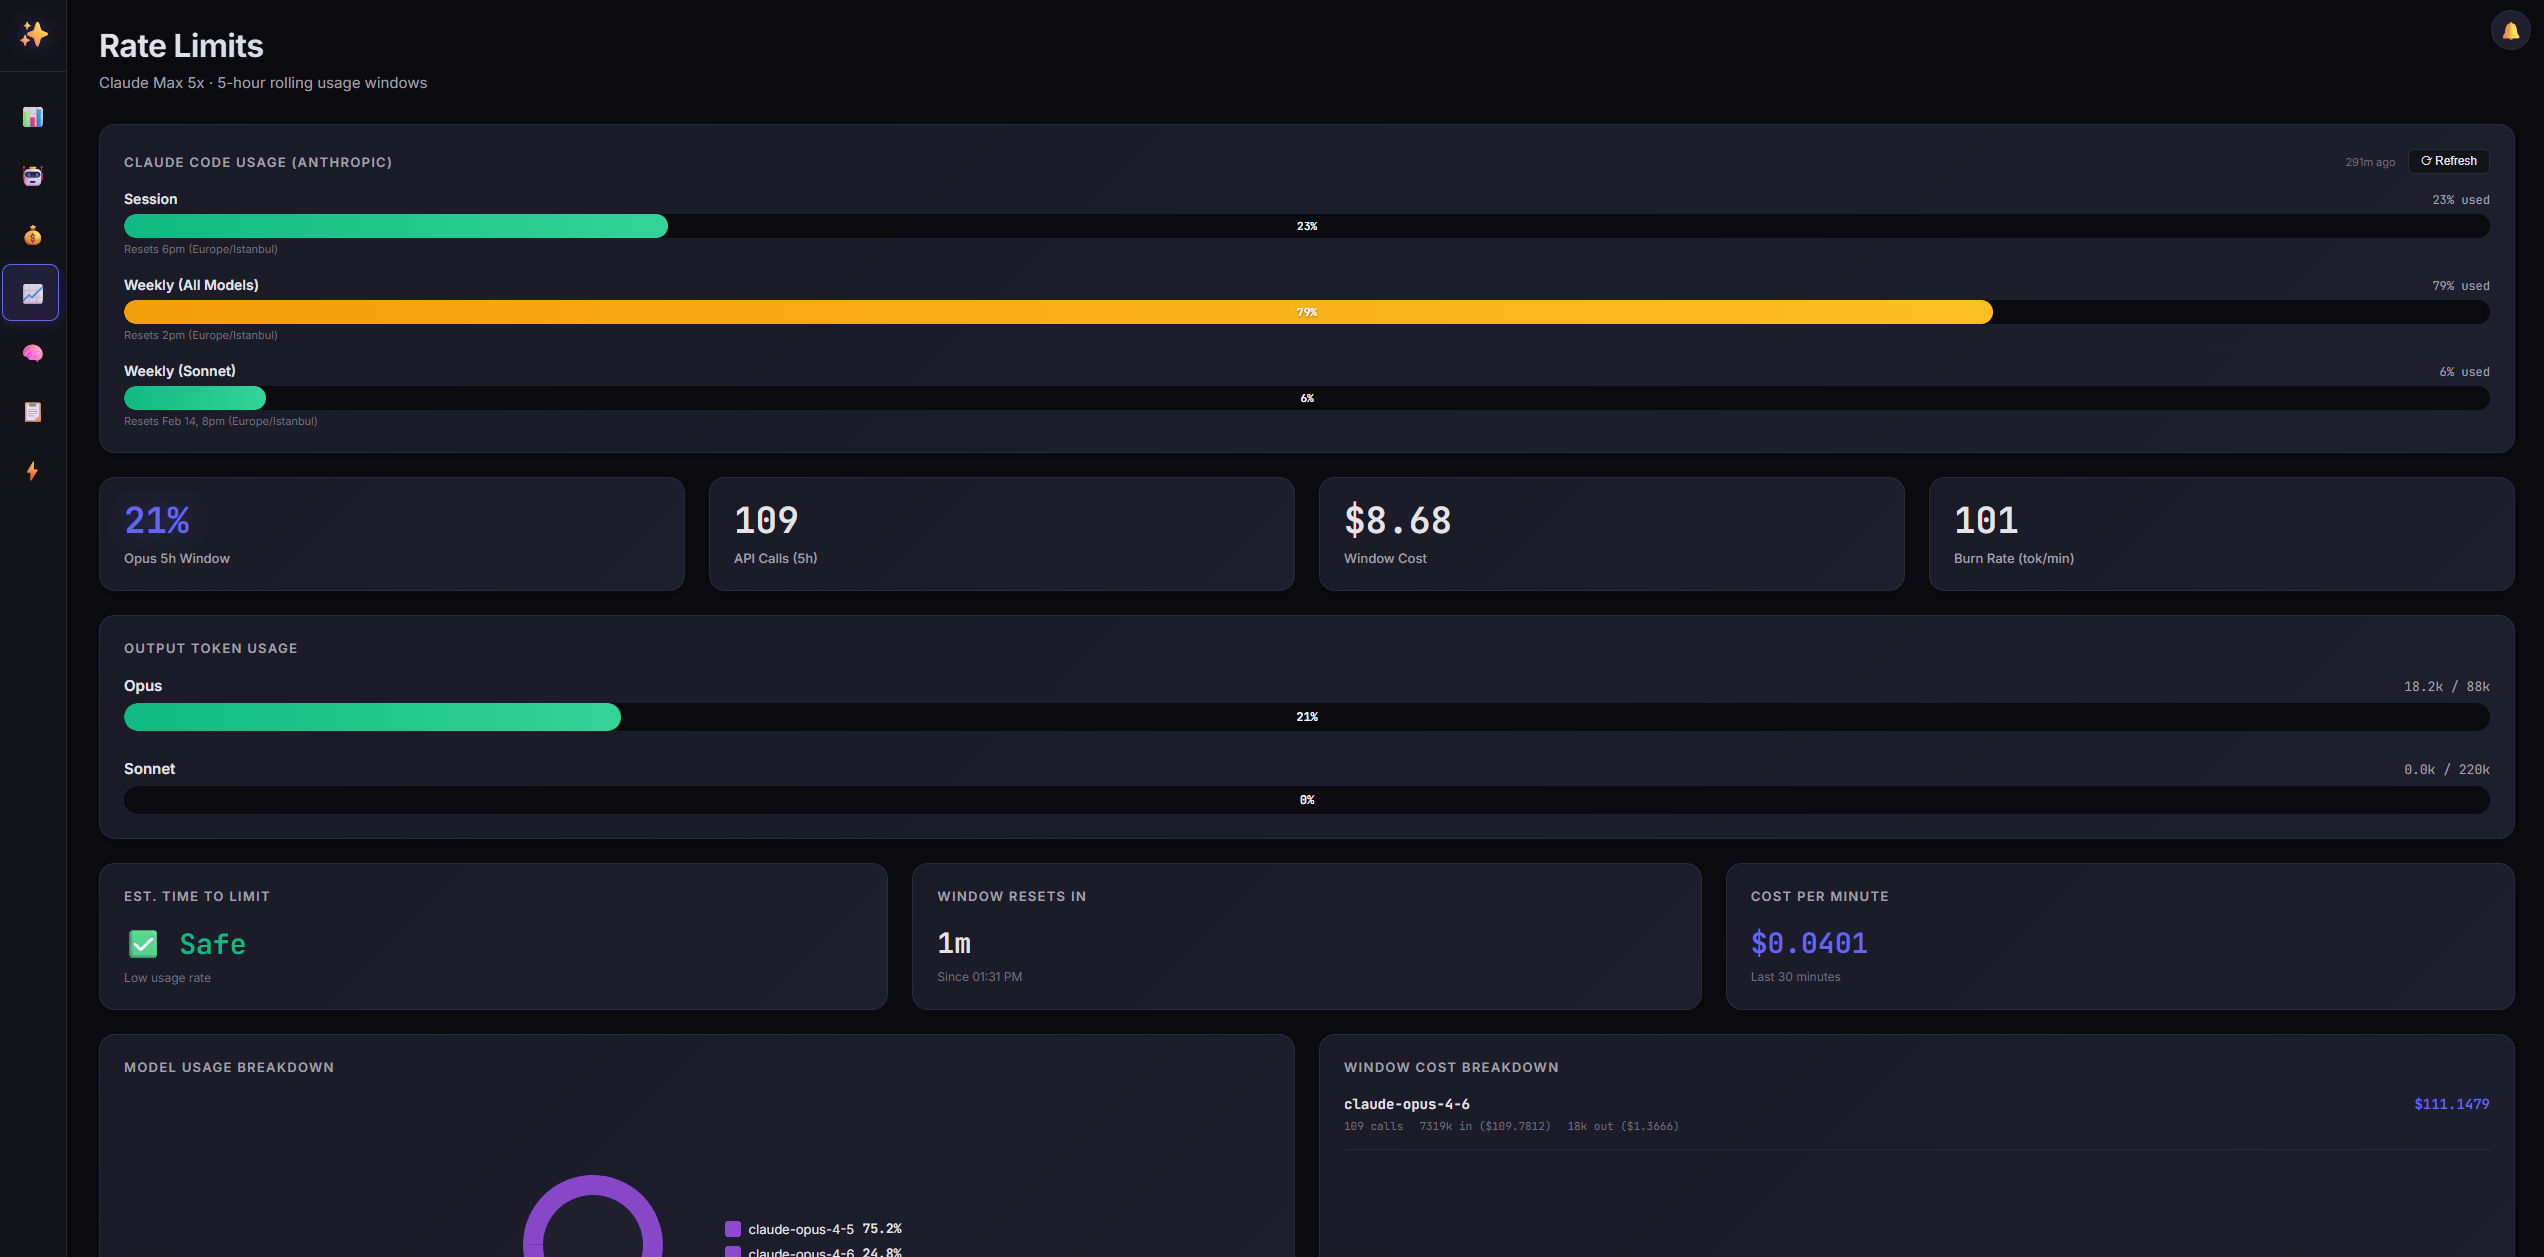 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
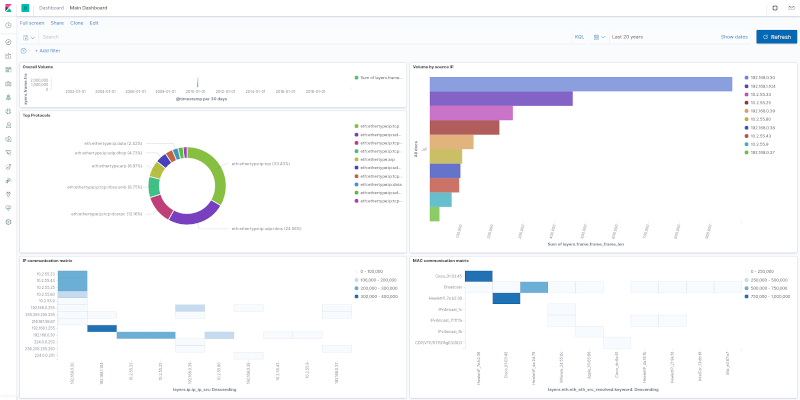 h21lab/tsharkvm
tshark + ELK analytics virtual machine
 swimlane/soc-faker
A python package for use in generating fake data for SOC and security automation.
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
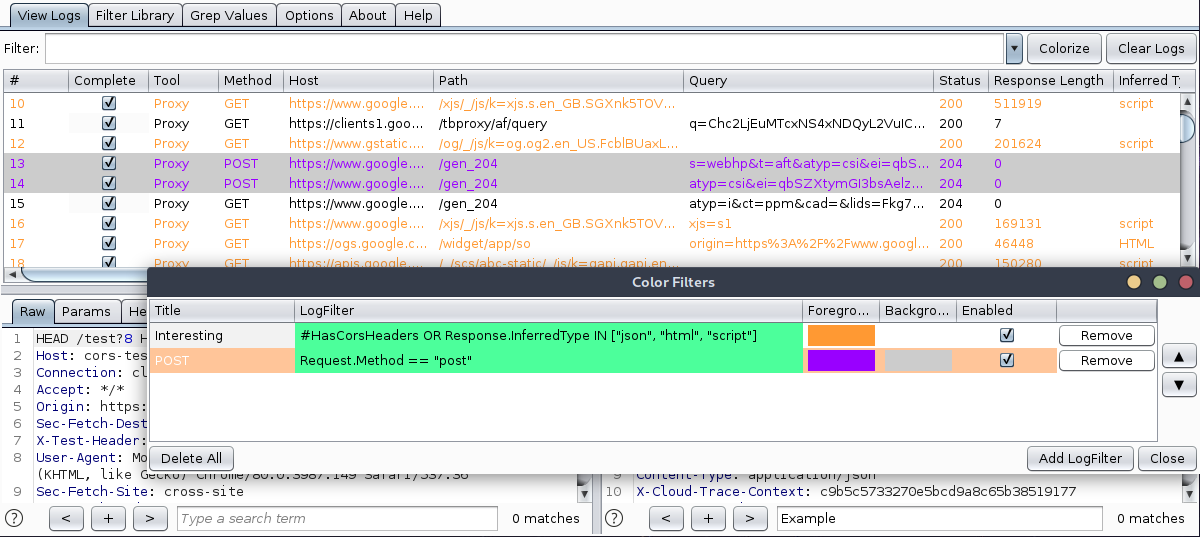 nccgroup/loggerplusplus
Advanced Burp Suite Logging Extension
 maliceio/malice
VirusTotal Wanna Be - Now with 100% more Hipster
 threathunters-io/qlog
ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…
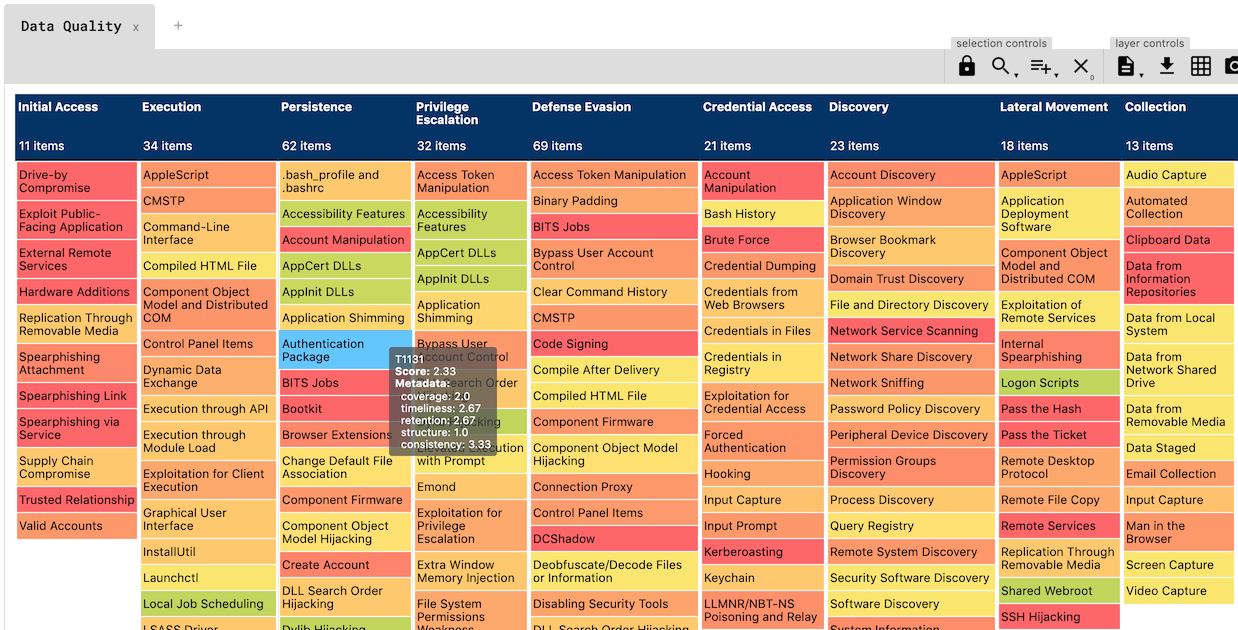 hxnoyd/ossem-power-up
A tool to assess data quality, built on top of the awesome OSSEM.