
pastokrapacefleciks
 nu11secur1ty/pastokrapacefleciks
Analyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
digital-forensicsforensicslog-analysis+2
nu11secur1ty/pastokrapacefleciksAnalyzes .pcapng files to generate HTML reports for network traffic inspection and forensic review.
 cyb3r-monk/rita-j
Implementation of RITA (Real Intelligence Threat Analytics) in Jupyter Notebook with improved scoring algorithm.
 scriptjunkie/fwallower
Analyze Windows Firewall outbound blocks and selectively allow traffic
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…
 nccgroup/mimikatz-detector-condrv
The Console Monitor Driver is a KMDF kernel-mode filter driver that captures certain Fast I/O operations (input and output) that is sent to or from…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
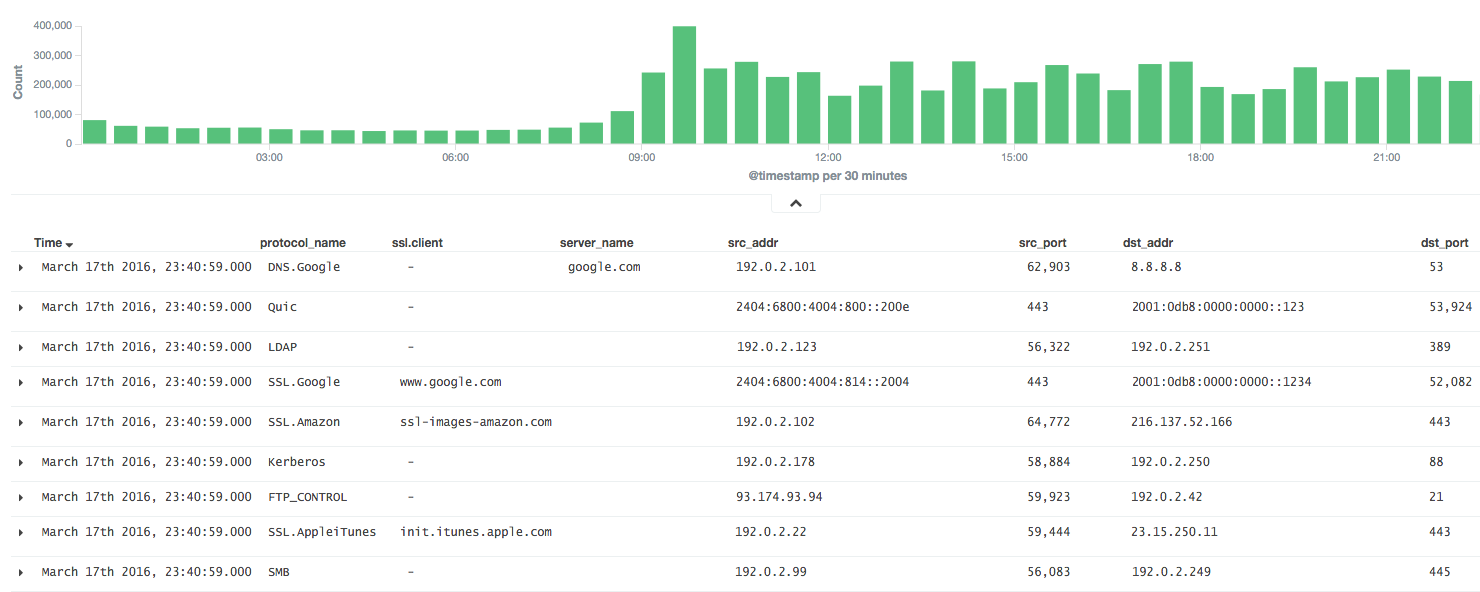 knqyf263/ndff
A flow-based network monitor with Deep Packet Inspection
 corelight/corelightforsplunk
Splunk app for integrating and analyzing Corelight network detection data, enabling real-time threat hunting and incident response.
 corelight/raspi-corelight
Corelight@Home script
 corelight/zeek-community-id
Zeek support for Community ID flow hashing.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 corelight/corelightforsentinelone
Corelight Dashboards and Parsers for Sentinel One Singularity
 corelight/zeek-spicy-openvpn
A Zeek OpenVPN protocol analyzer, based on Spicy.
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…