

jataayu
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
ai-securityauthentication-authorizationdata-exfiltration+6
gmh5225/jataayuLLM-backed AI agent security — inbound injection detection + outbound privacy protection
 fabianch20/soc335---cve-2024-49138-exploitation-detected
SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 withsecureopensource/chainsaw
Rapidly Search and Hunt through Windows Forensic Artefacts
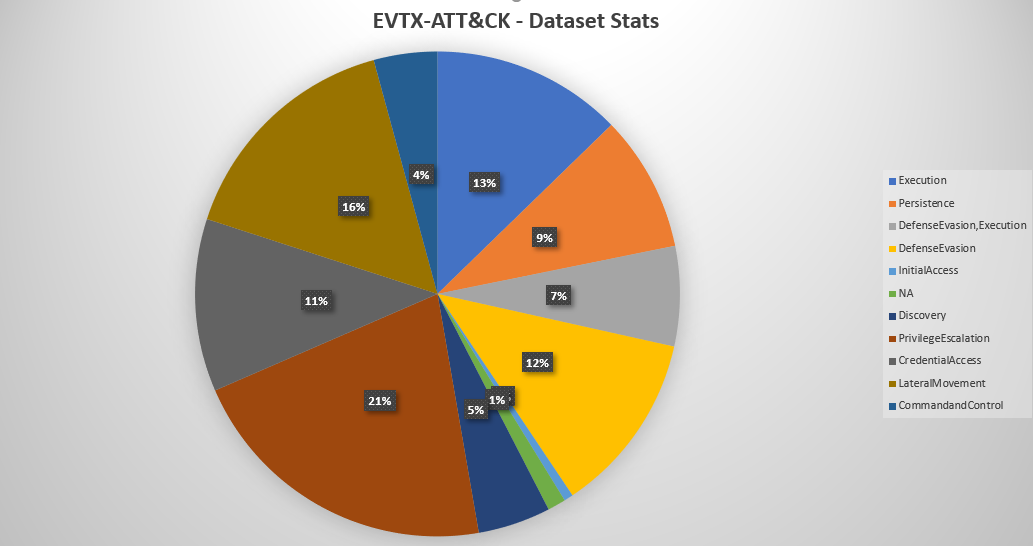 sbousseaden/evtx-attack-samples
Curated collection of Windows EVTX attack samples mapped to MITRE ATT&CK techniques, designed for testing detection scripts, DFIR training, and…
 withsecurelabs/remotepspy
Live monitoring tool for remote PowerShell sessions using ETW to capture and decode WinRM/PSRP protocol, providing command execution traces and…
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
 virologi-info/papercut-toolkit
#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained
 siberanka/rdp-guard
Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…
 letlaka/redsun-bluehammer-undefend-detection-pack
Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.
 bilal3755/detecting_blue_hammer_vuln
Threat hunting query for bluehammer CVE windows CVE-2026-33825
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…