
fengarde
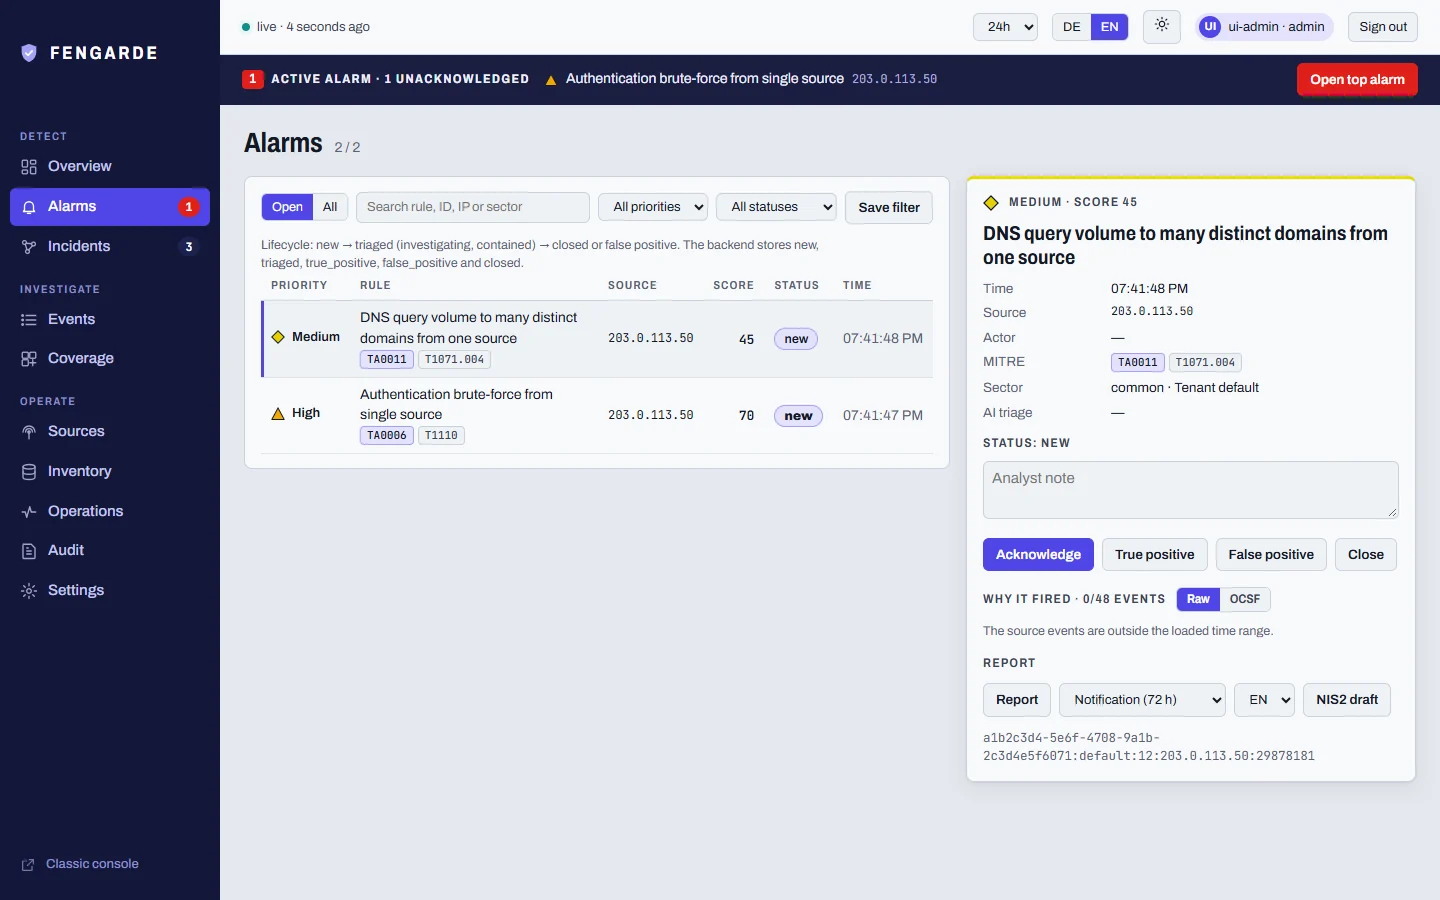
 supermhel/fengarde
Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
ai-securitydefensive-toolsincident-response+4
15
supermhel/fengardeOpen-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
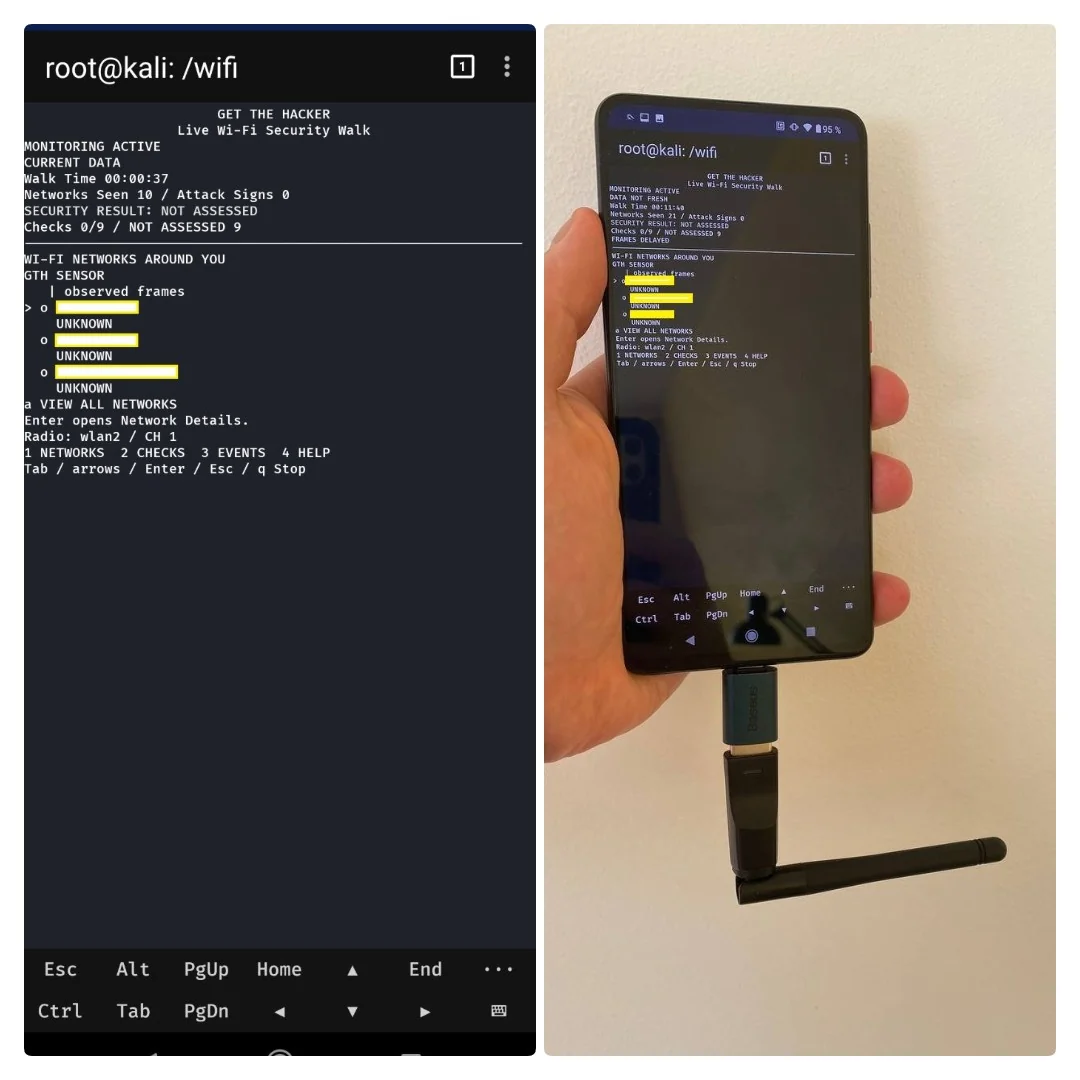 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.

 yashubitra/mobile-intrusion-detection-system
Unsupervised deep autoencoder that flags anomalous mobile traffic: 25,000+ HTTP/HTTPS flows intercepted from a live iOS device with mitmproxy,…
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
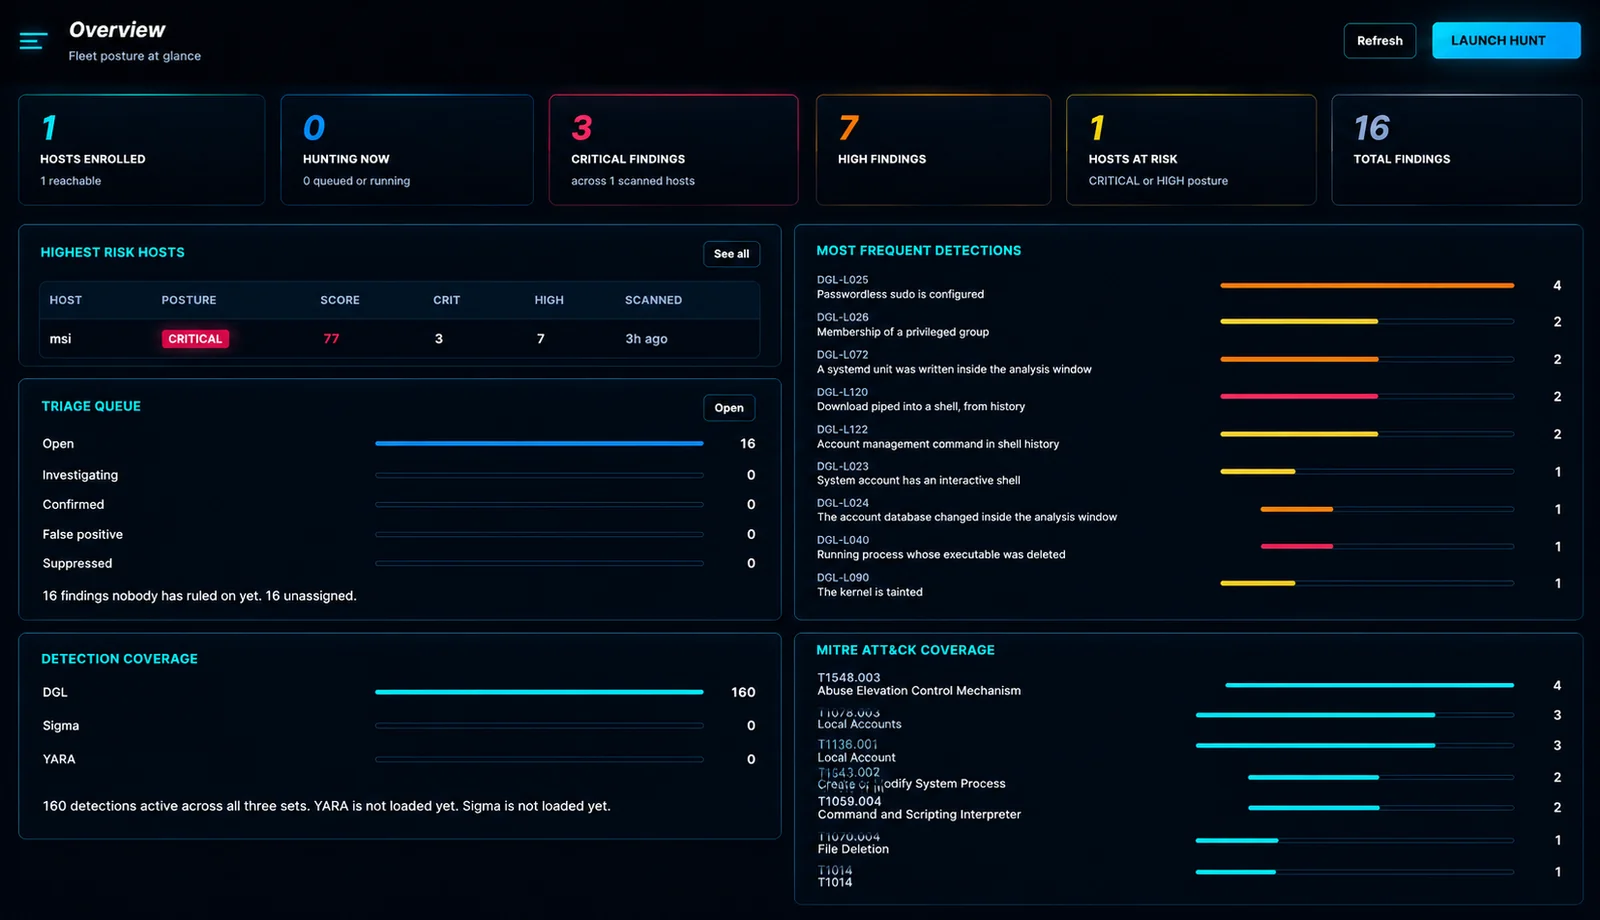 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 d3vhex/sentora
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
 unfold-security/cve-2026-41940-detection
Detection signatures for CVE-2026-41940 and shemas for cPanel logs
 srozb/reditrap
Minimal Redis honeypot detecting RediShell (CVE-2025-49844) exploits.
 letlaka/redsun-bluehammer-undefend-detection-pack
Microsoft Defender XDR KQL detections for RedSun, BlueHammer, UnDefend, and CVE-2026-33825-related Defender abuse behaviors.
 garethmsheldon/cve-2026-22557-unifi-detection
Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…