

c2detect
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
command-and-controldefensive-toolsfingerprint-spoofing+8
44
cognis-digital/c2detectC2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
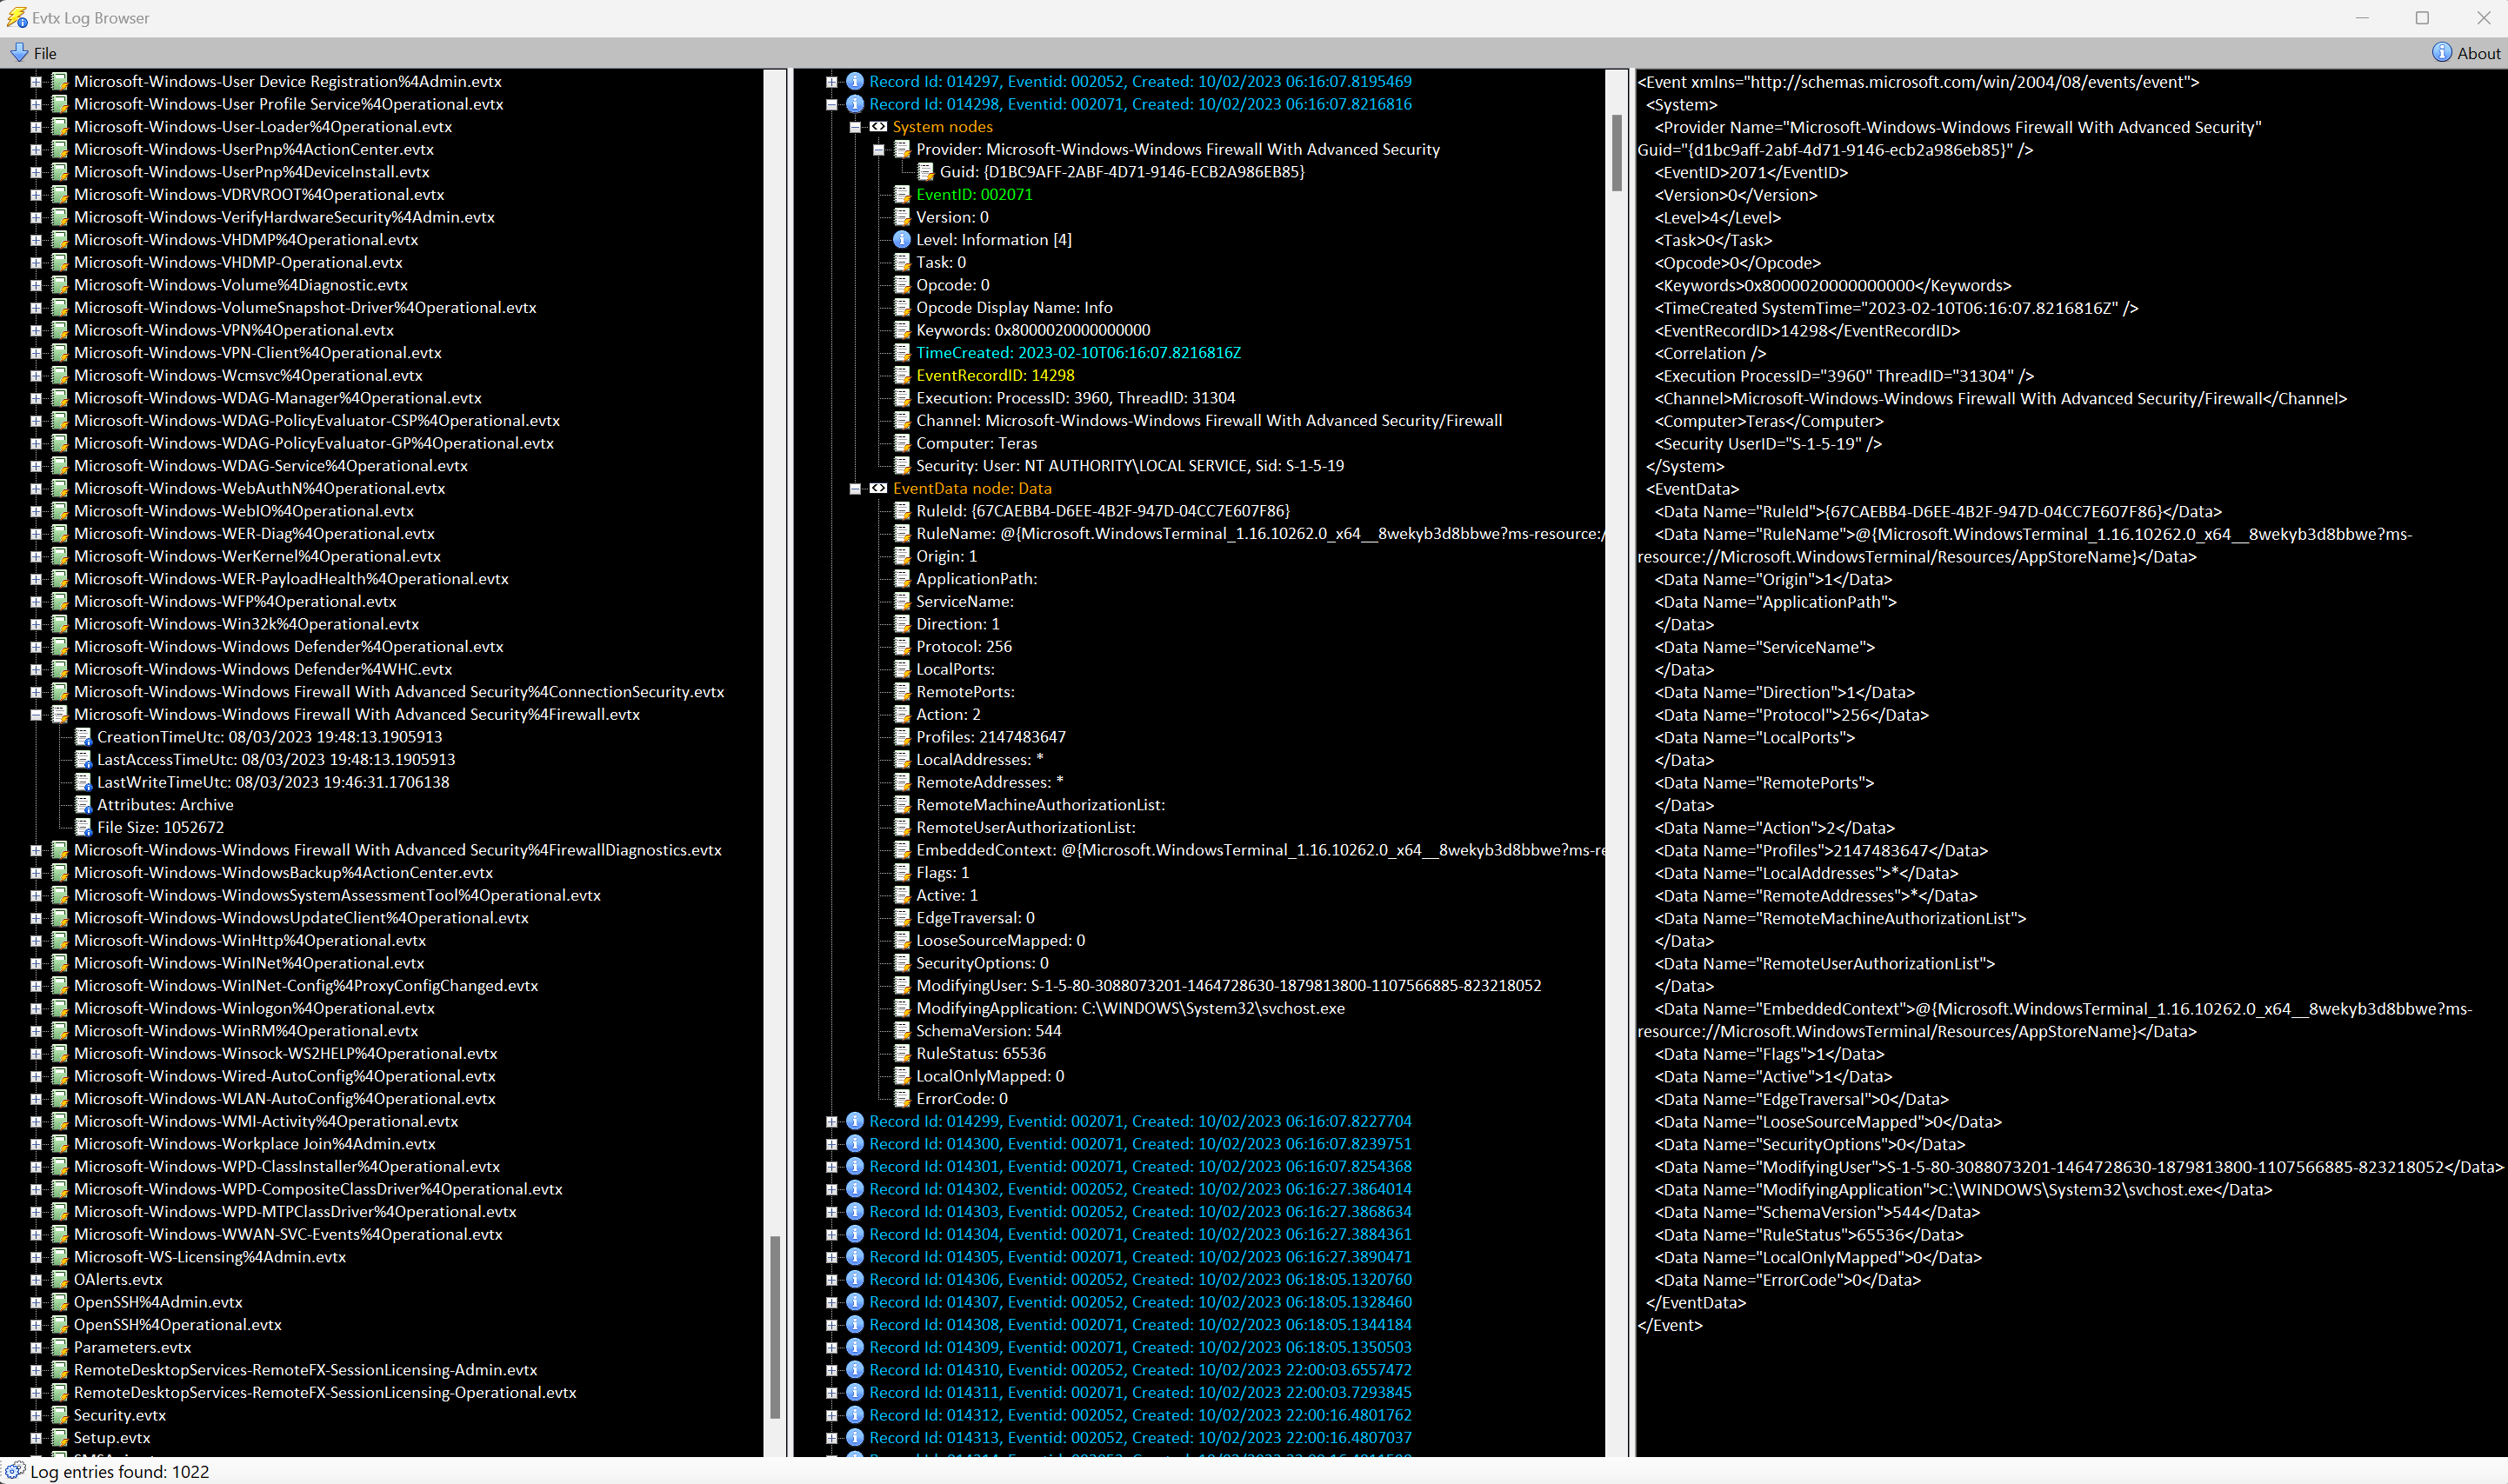 kacos2000/evtx_log_browser
Evtx Log (xml) Browser
 linux-audit/audit-kernel
GitHub mirror of the Linux Kernel's audit repository
 adversarial-detection-engineering/adversarial-detection-engineering-framework
A framework and taxonomy for identifying, classifying, and reasoning about detection logic bugs in SIEM, EDR, and XDR rules, with concrete examples…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 tirrenotechnologies/tirreno
Open-source security framework for real-time event tracking, threat detection, and risk scoring. Monitors user behavior, detects fraud, bot attacks,…