

plaso
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
data-recoverydigital-forensicsdisk-forensics+5
2.2k
log2timeline/plasoDigital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 mandiant/macos-unifiedlogs
A cross platform parser for Apple UnifiedLogs!
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
 jschicht/logfileparser
Parser for $LogFile on NTFS
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 jonny-jhnson/ldapmon
Proof-of-concept telemetry collector for Windows LDAP client activity via ETW, logging structured events to Event Viewer with a Sentinel parser for…
 nccgroup/burp-reflux
Burp proxy text log converter to CSV and SQLLite
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
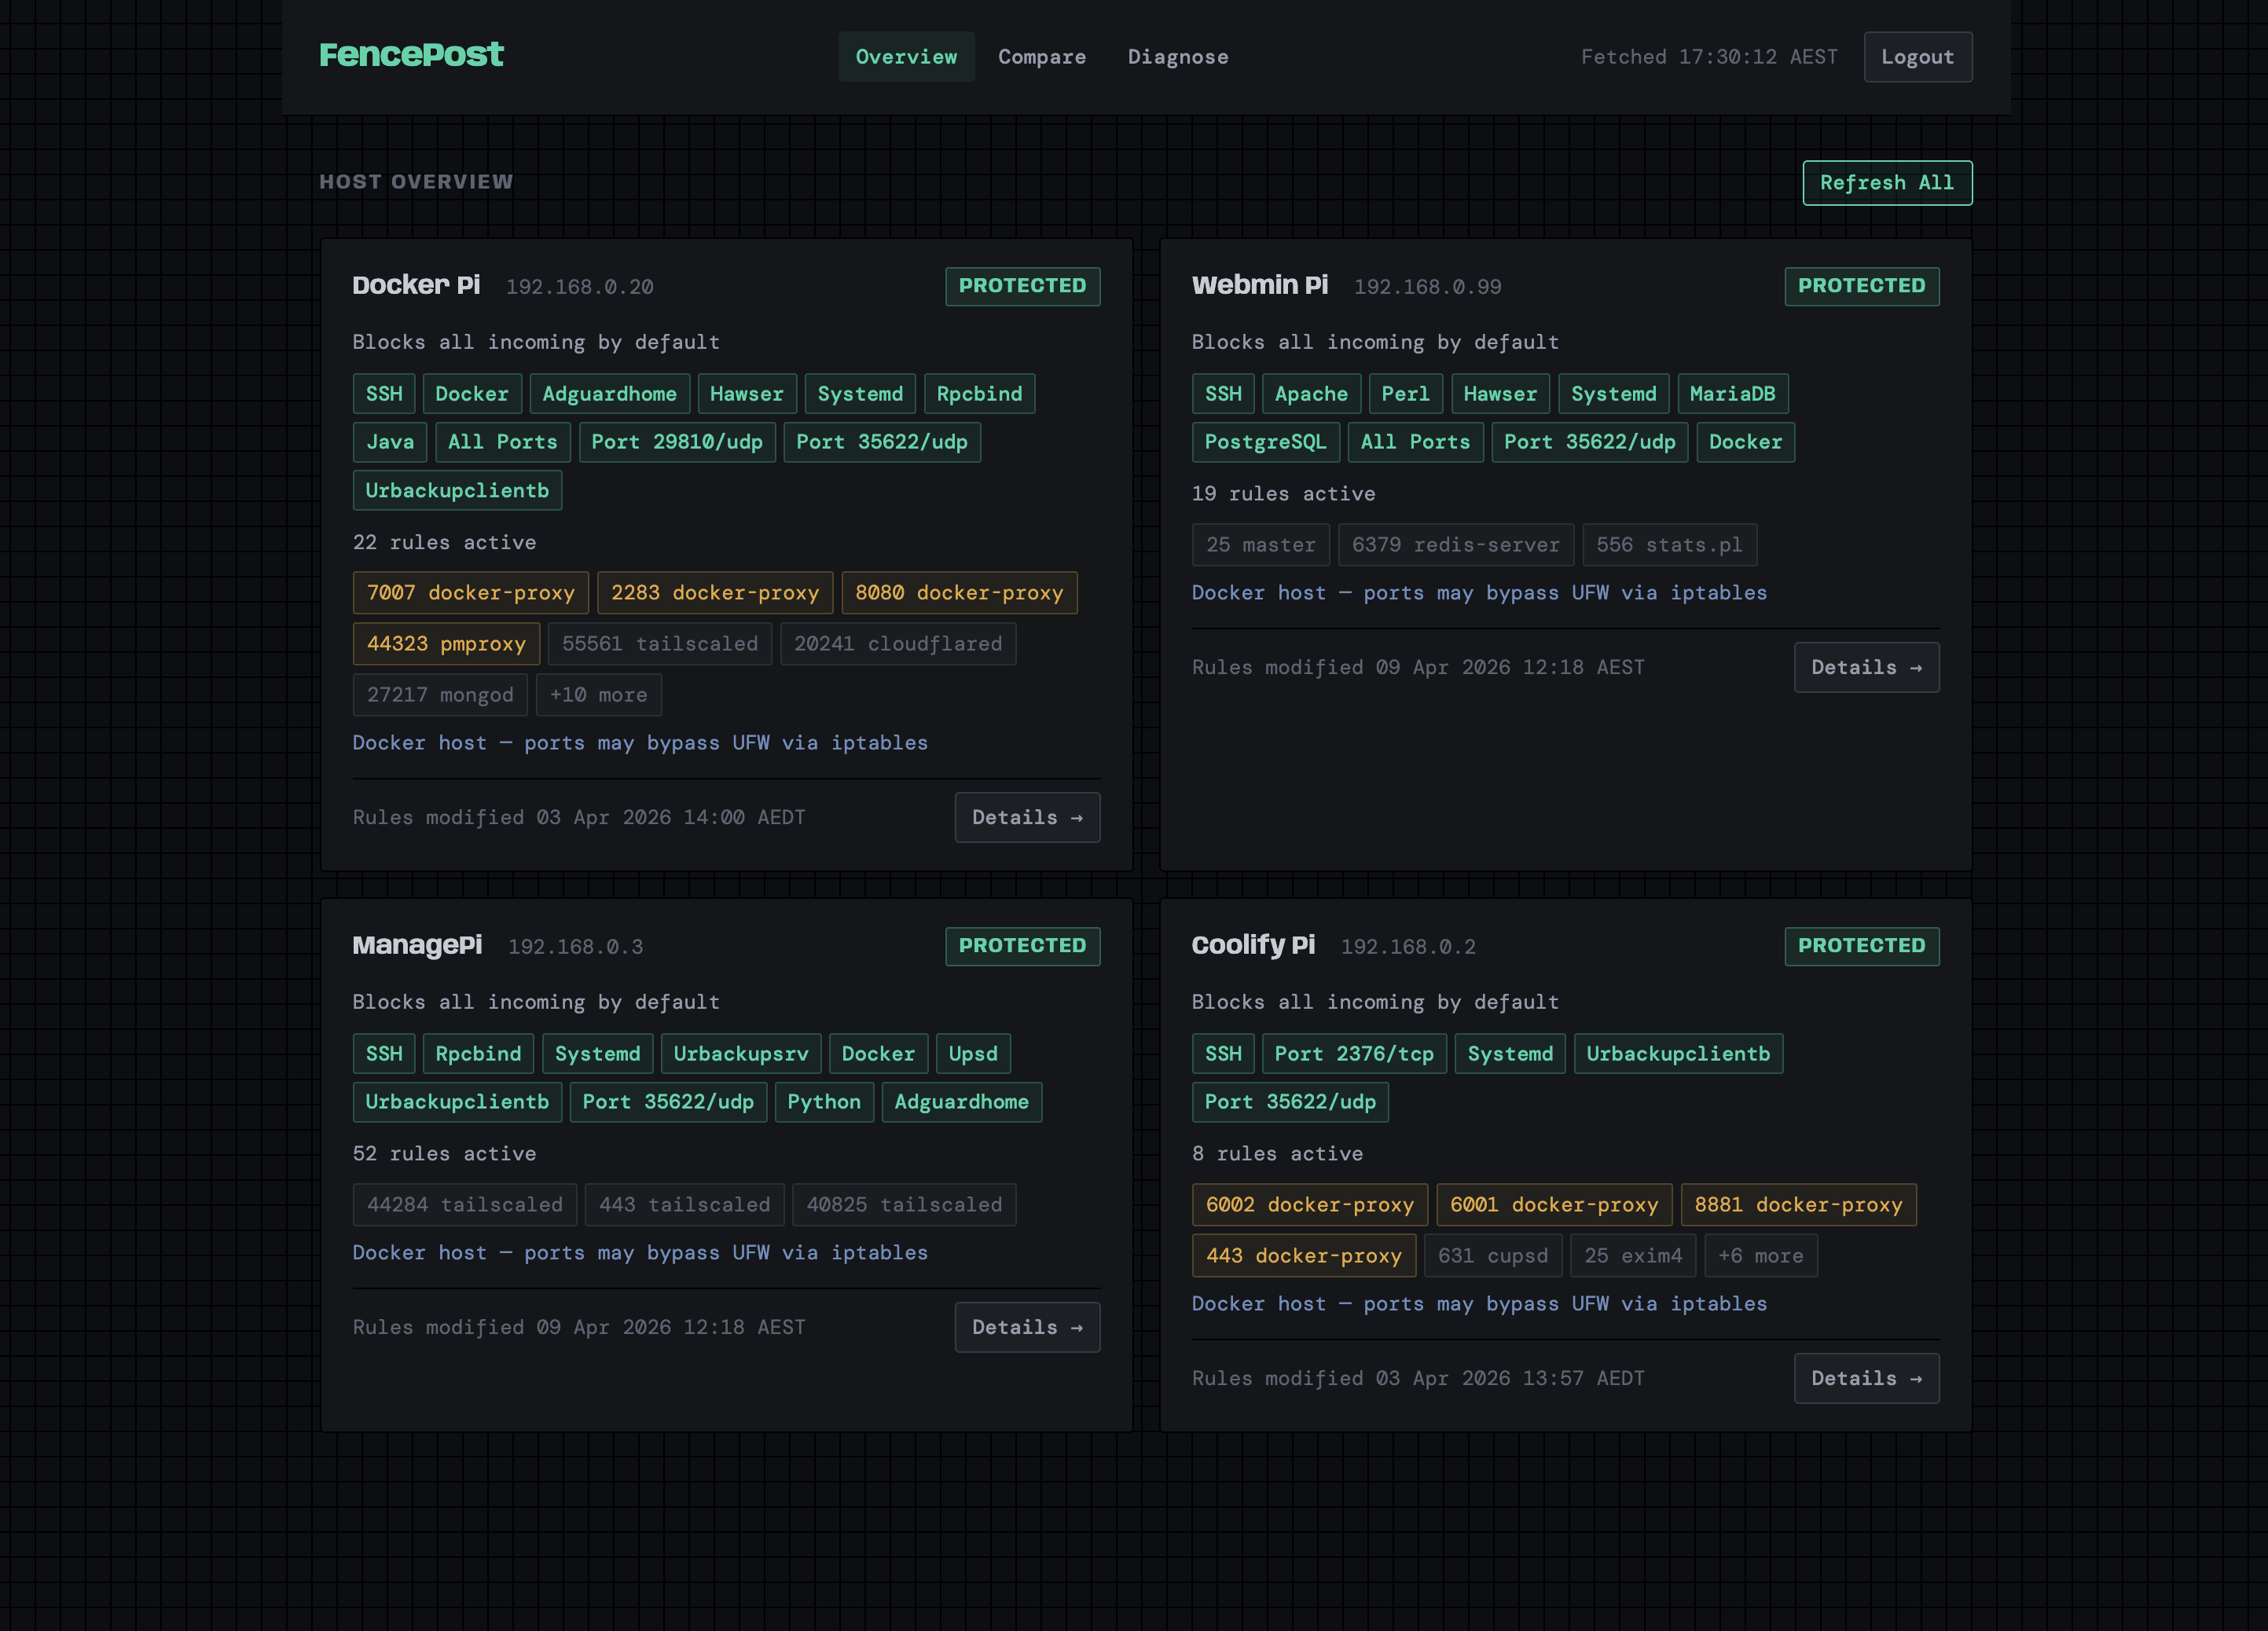 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 lightless-labs/third-thoughts
Research toolkit for analyzing AI agent behavioral patterns through multi-disciplinary corpus analysis. Parses session logs, runs 23 analytical…
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.