
DShield-SIEM
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
defensive-toolsincident-responseintrusion-detection+4
50
bruneaug/dshield-siemDShield Sensor Log Collection with ELK
 olafhartong/sysmon-parser
Automatically generated Sysmon parser for Azure Sentinel
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
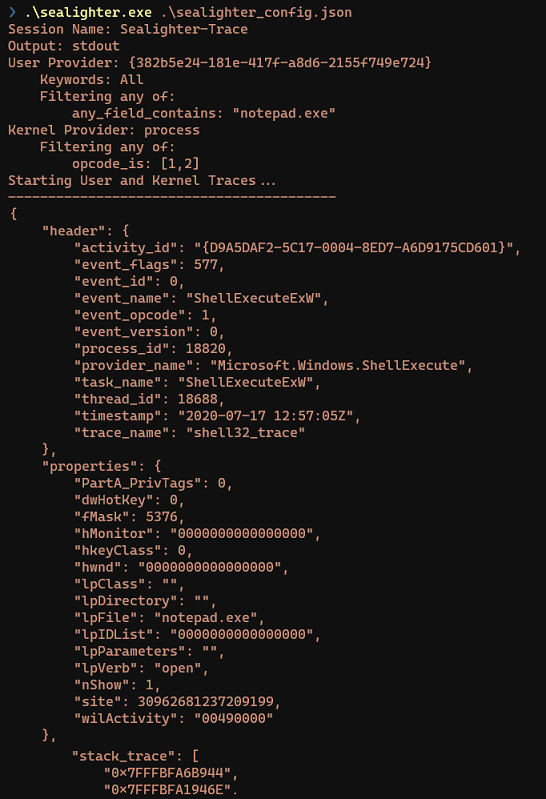 pathtofile/sealighter
ETW and WPP tracing tool for security research. Subscribes to multiple providers, auto-parses events to JSON, and supports advanced filtering,…
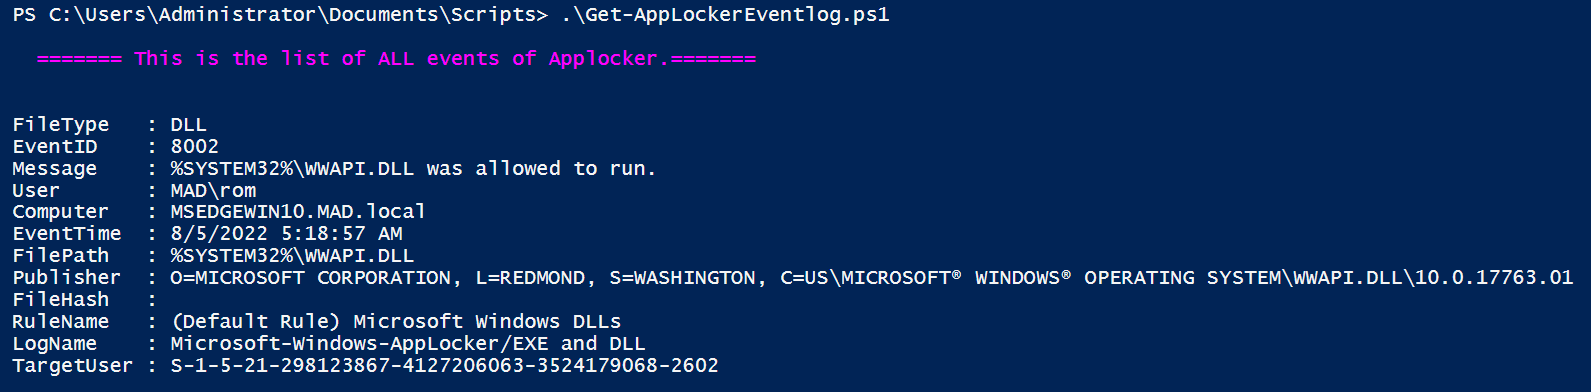 romaissaadjailia/get-applockereventlog
This is a repo for fetching Applocker event log by parsing the win-event log
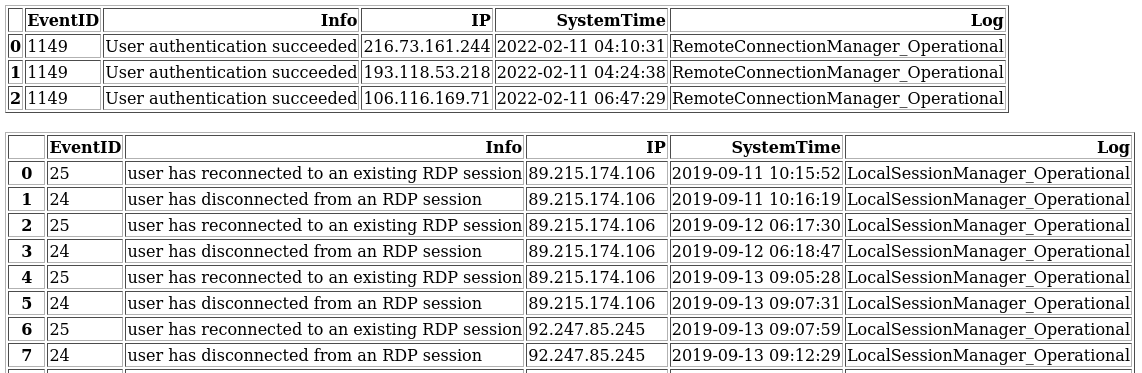 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
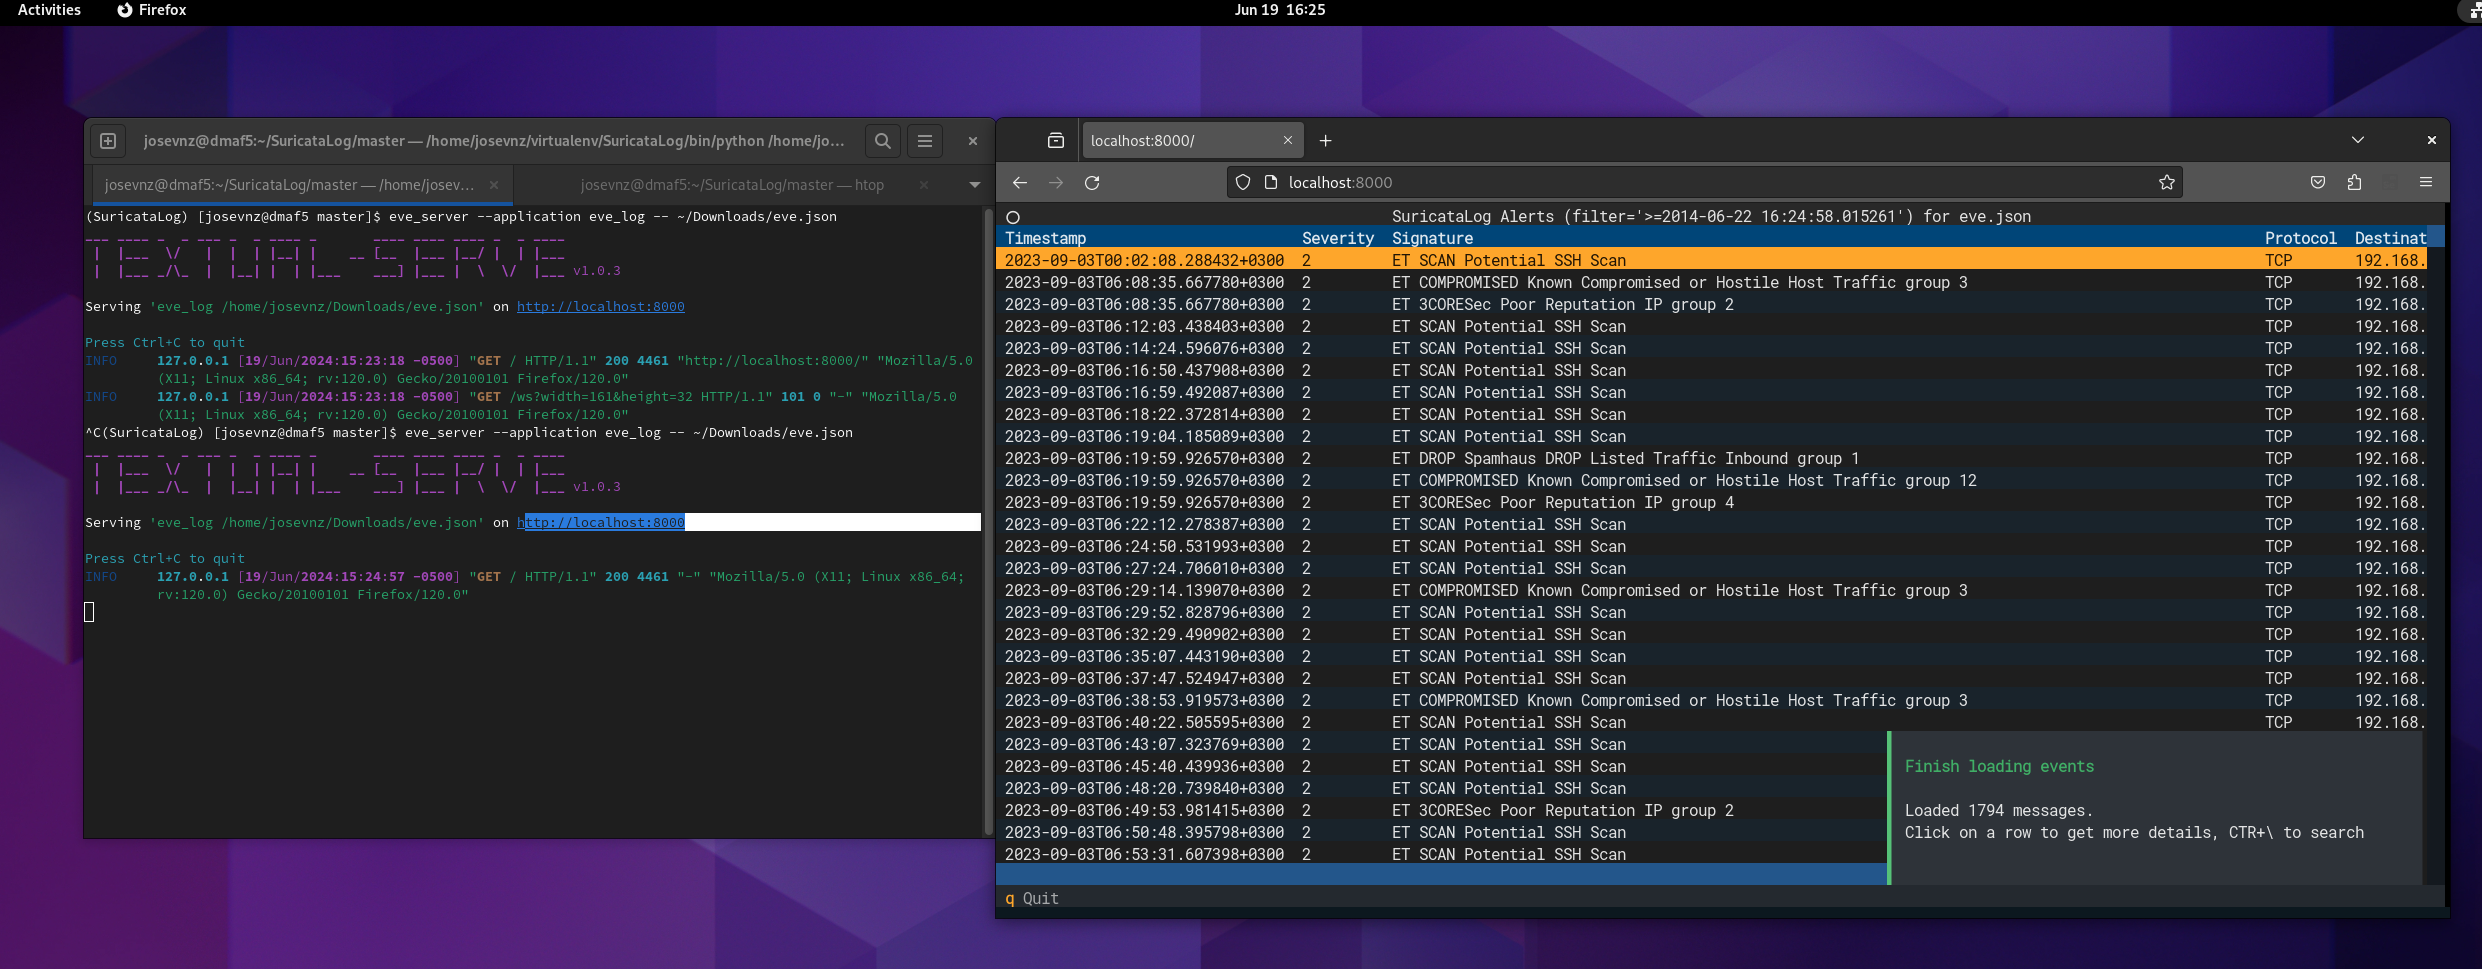 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…