
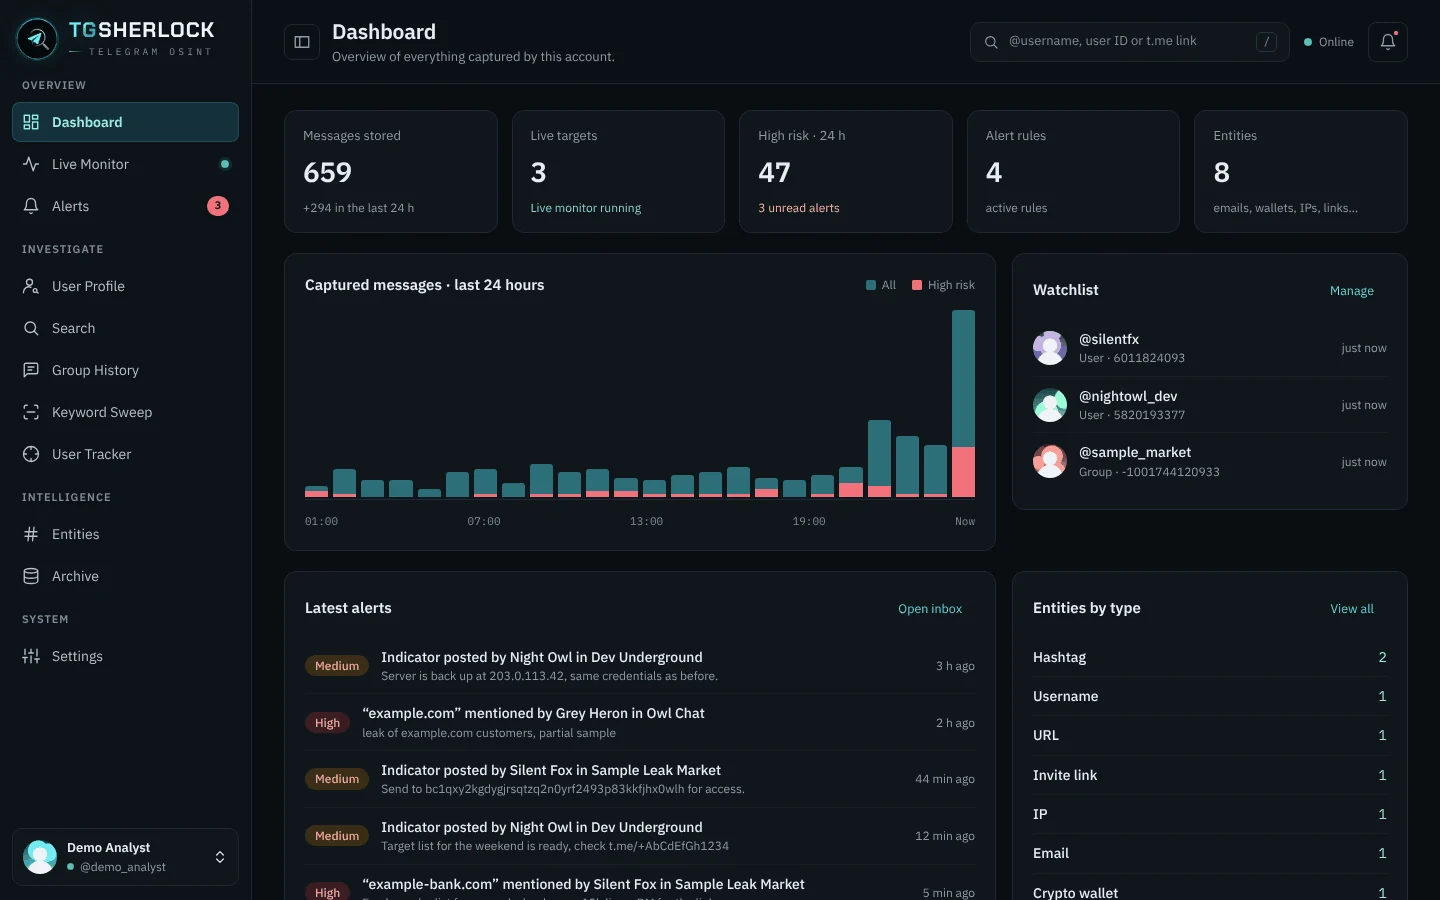
tgsherlock
 emrekybs/tgsherlock
Telegram OSINT tool for user, group and message investigation
data-exfiltrationinformation-gatheringlog-analysis+6
emrekybs/tgsherlockTelegram OSINT tool for user, group and message investigation
 wagga40/logstotal
Self-hosted multi-engine Sigma detection for event logs
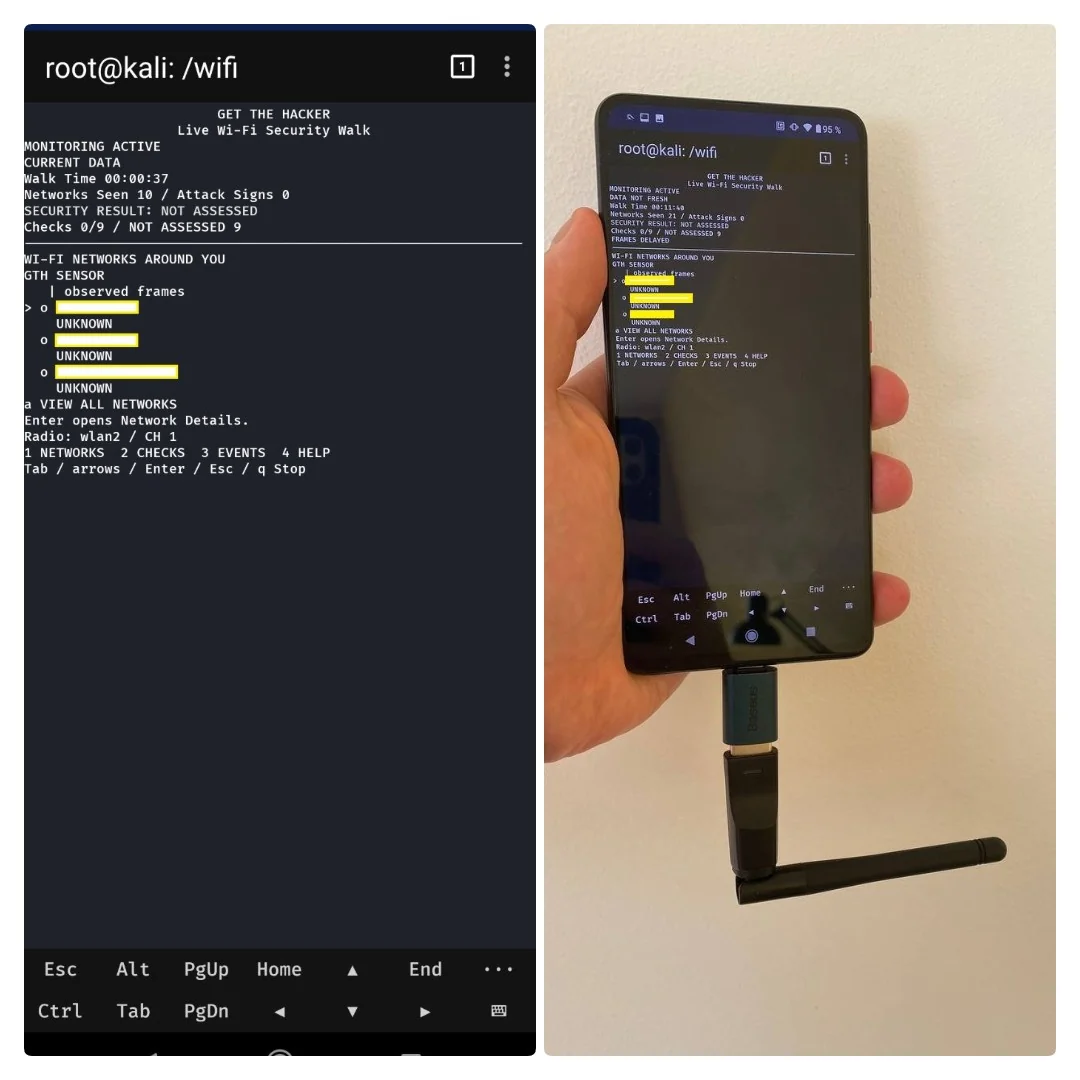 buybitart/get-the-hacker
Hunt WiFi threats silently. Catch the hackers.
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 msuhanov/easy_triage
Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 olafhartong/sysmon-modular
A repository of sysmon configuration modules
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
 linux-audit/audit-kernel
GitHub mirror of the Linux Kernel's audit repository
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 municipalparkingservices/cve-2021-44228-scanner
Single-binary scanner for CVE-2021-44228 (Log4Shell) that detects vulnerable log4j versions in JAR/WAR/EAR files and applies mitigation patches by…
 guillaumepetit84/cve-2020-35488
Proof-of-concept exploit for CVE-2020-35488, a denial-of-service vulnerability in NXLOG Community Edition via crafted syslog payloads causing…
 verveindustrialprotection/cve-2021-44228-log4j
Provides BigFix Fixlets and analyses to detect Log4j vulnerabilities (CVE-2021-44228, CVE-2021-45046, CVE-2021-45105) across Windows and Linux…
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally