

jev-ids
 jev-sec/jev-ids
Blazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
anomaly-detectiondefensive-toolsintrusion-detection+5
3014h 3m ago
jev-sec/jev-idsBlazing-Fast Token-Efficient Intrusion Detection System (IDS) based on TypeSafe's Jev.
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..
 signalapp/key-transparency-auditor
Continuously fetches and cryptographically verifies key transparency log updates, maintains a condensed prefix and log tree view, and returns signed…
 nccgroup/windowsmempagedelta
A Microsoft Windows service to provide telemetry on Windows executable memory page changes to facilitate threat detection
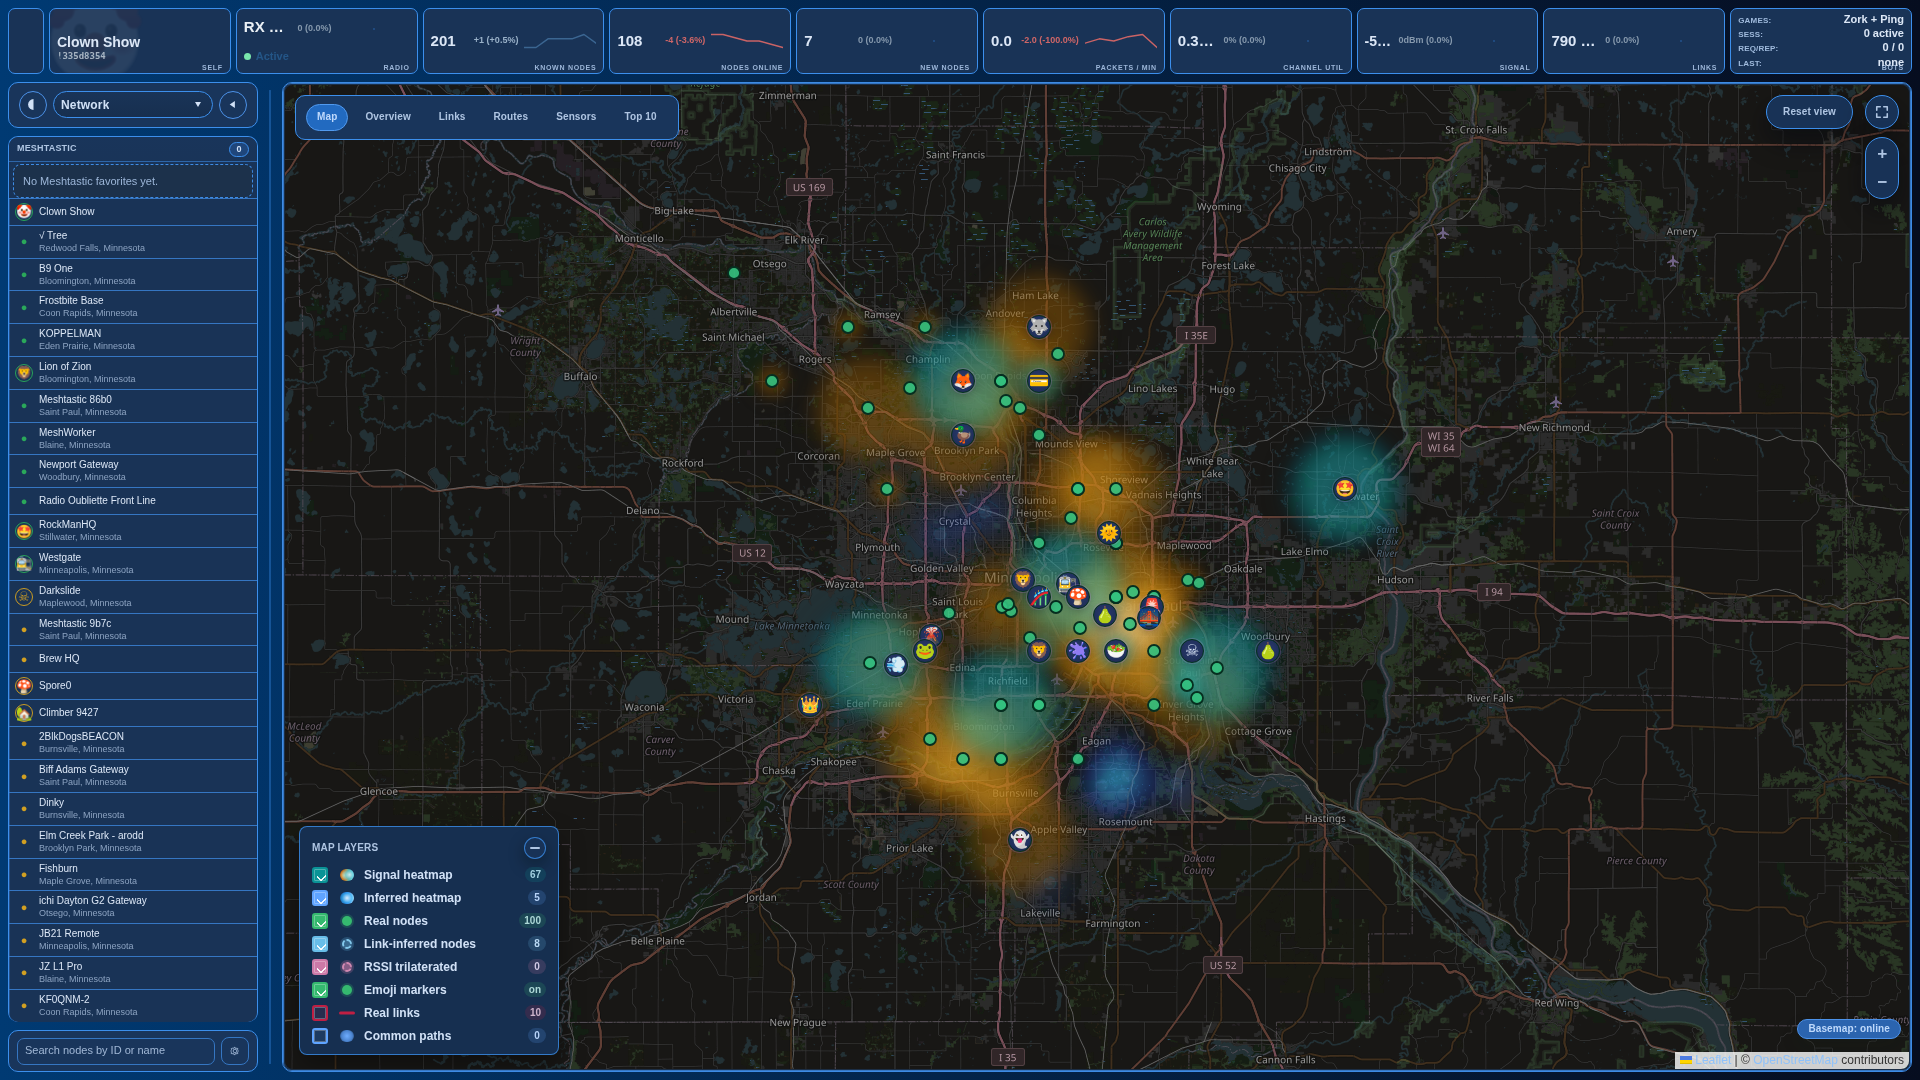 jaronmcd/meshyface
Single-page web dashboard for Meshtastic mesh networks with live network mapping, packet analysis, chat, sensor telemetry, and topology…
 wdahlenburg/cve-2022-38725
Proof of Concept for CVE-2022-38725 against syslog-ng
 lucadibello/network-attack-detection
Advanced detection of port scanning, DoS and malware attacks using Machine Learning techniques
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 zedocun/pan-os-cve-2024-3400-command-injection-investigation
Investigation of a PAN-OS CVE-2024-3400 command injection attempt, analyzing payload delivery, internal processing, and execution validation based on…
 rootly-ai-labs/rootly-graphify-importer
Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 digitalruby/ipban
Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…