DFIRHub
 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
curated-resourcesdigital-forensicsforensics+4
10
lascc/dfirhubSearch Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 withsecurelabs/macostriagecollectionscript
Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…
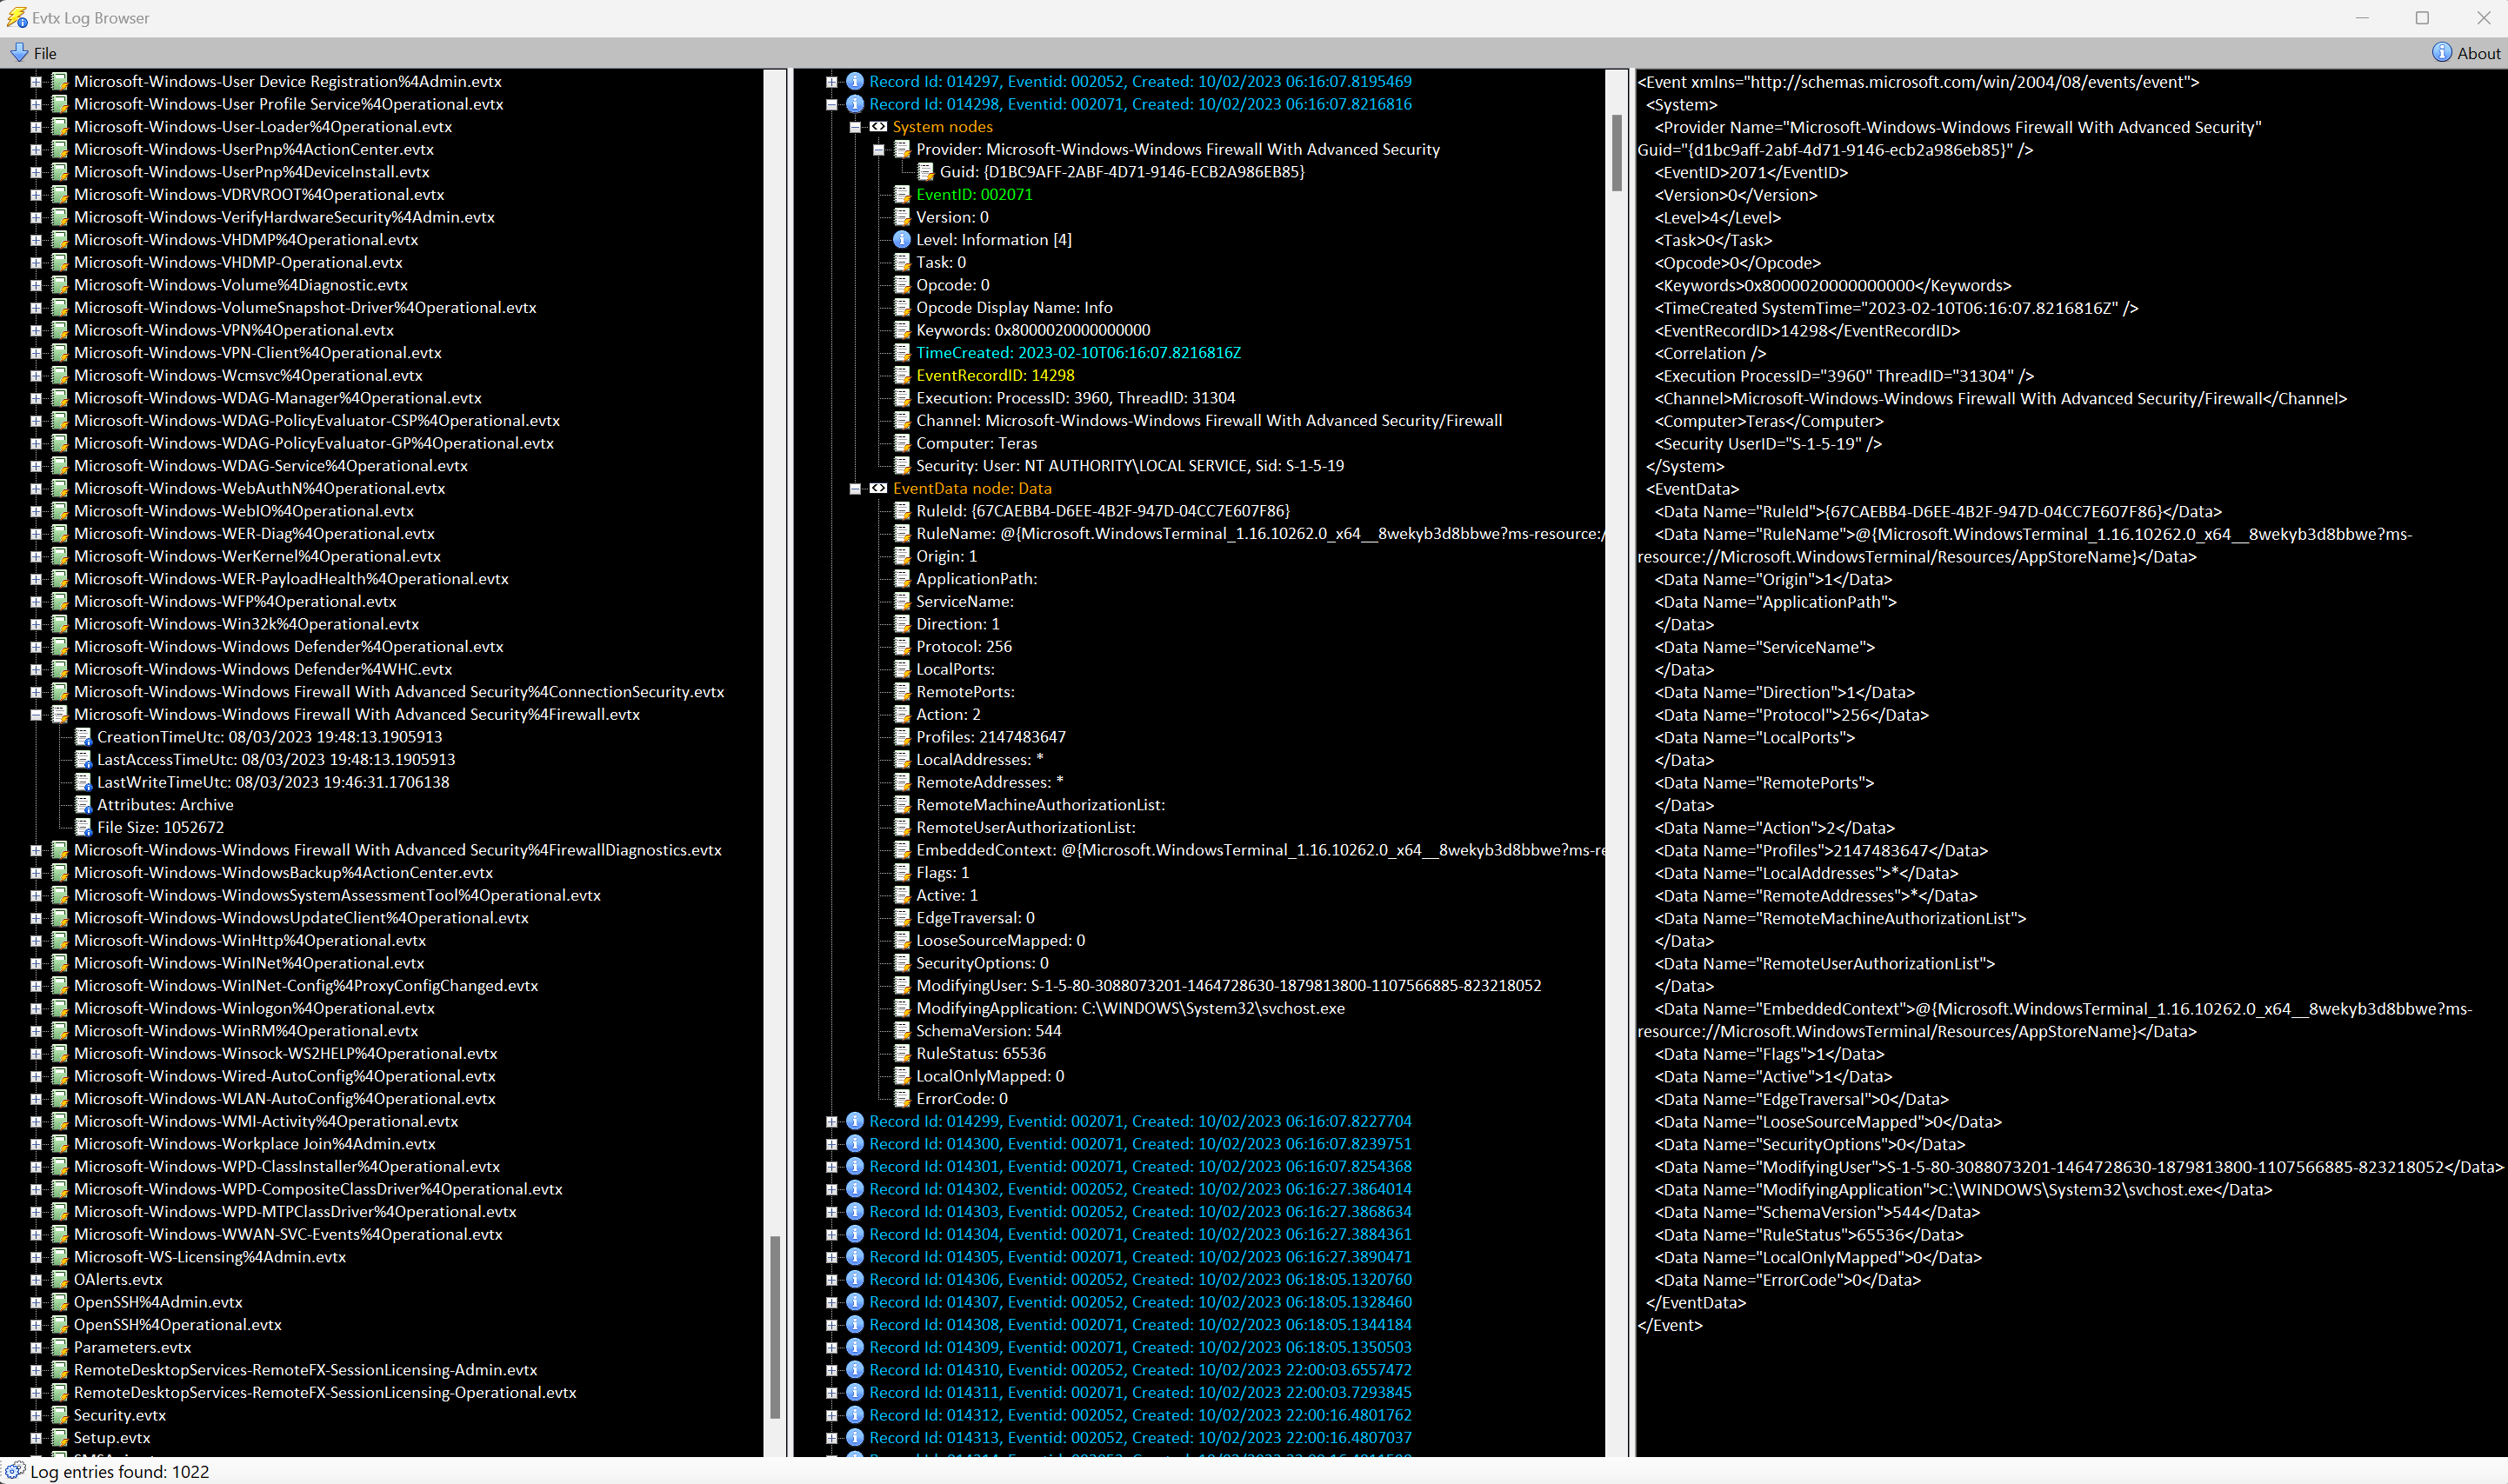 kacos2000/evtx_log_browser
Evtx Log (xml) Browser
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 k11h-de/bbot-ui
a terminal UI to browse bbot reports
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
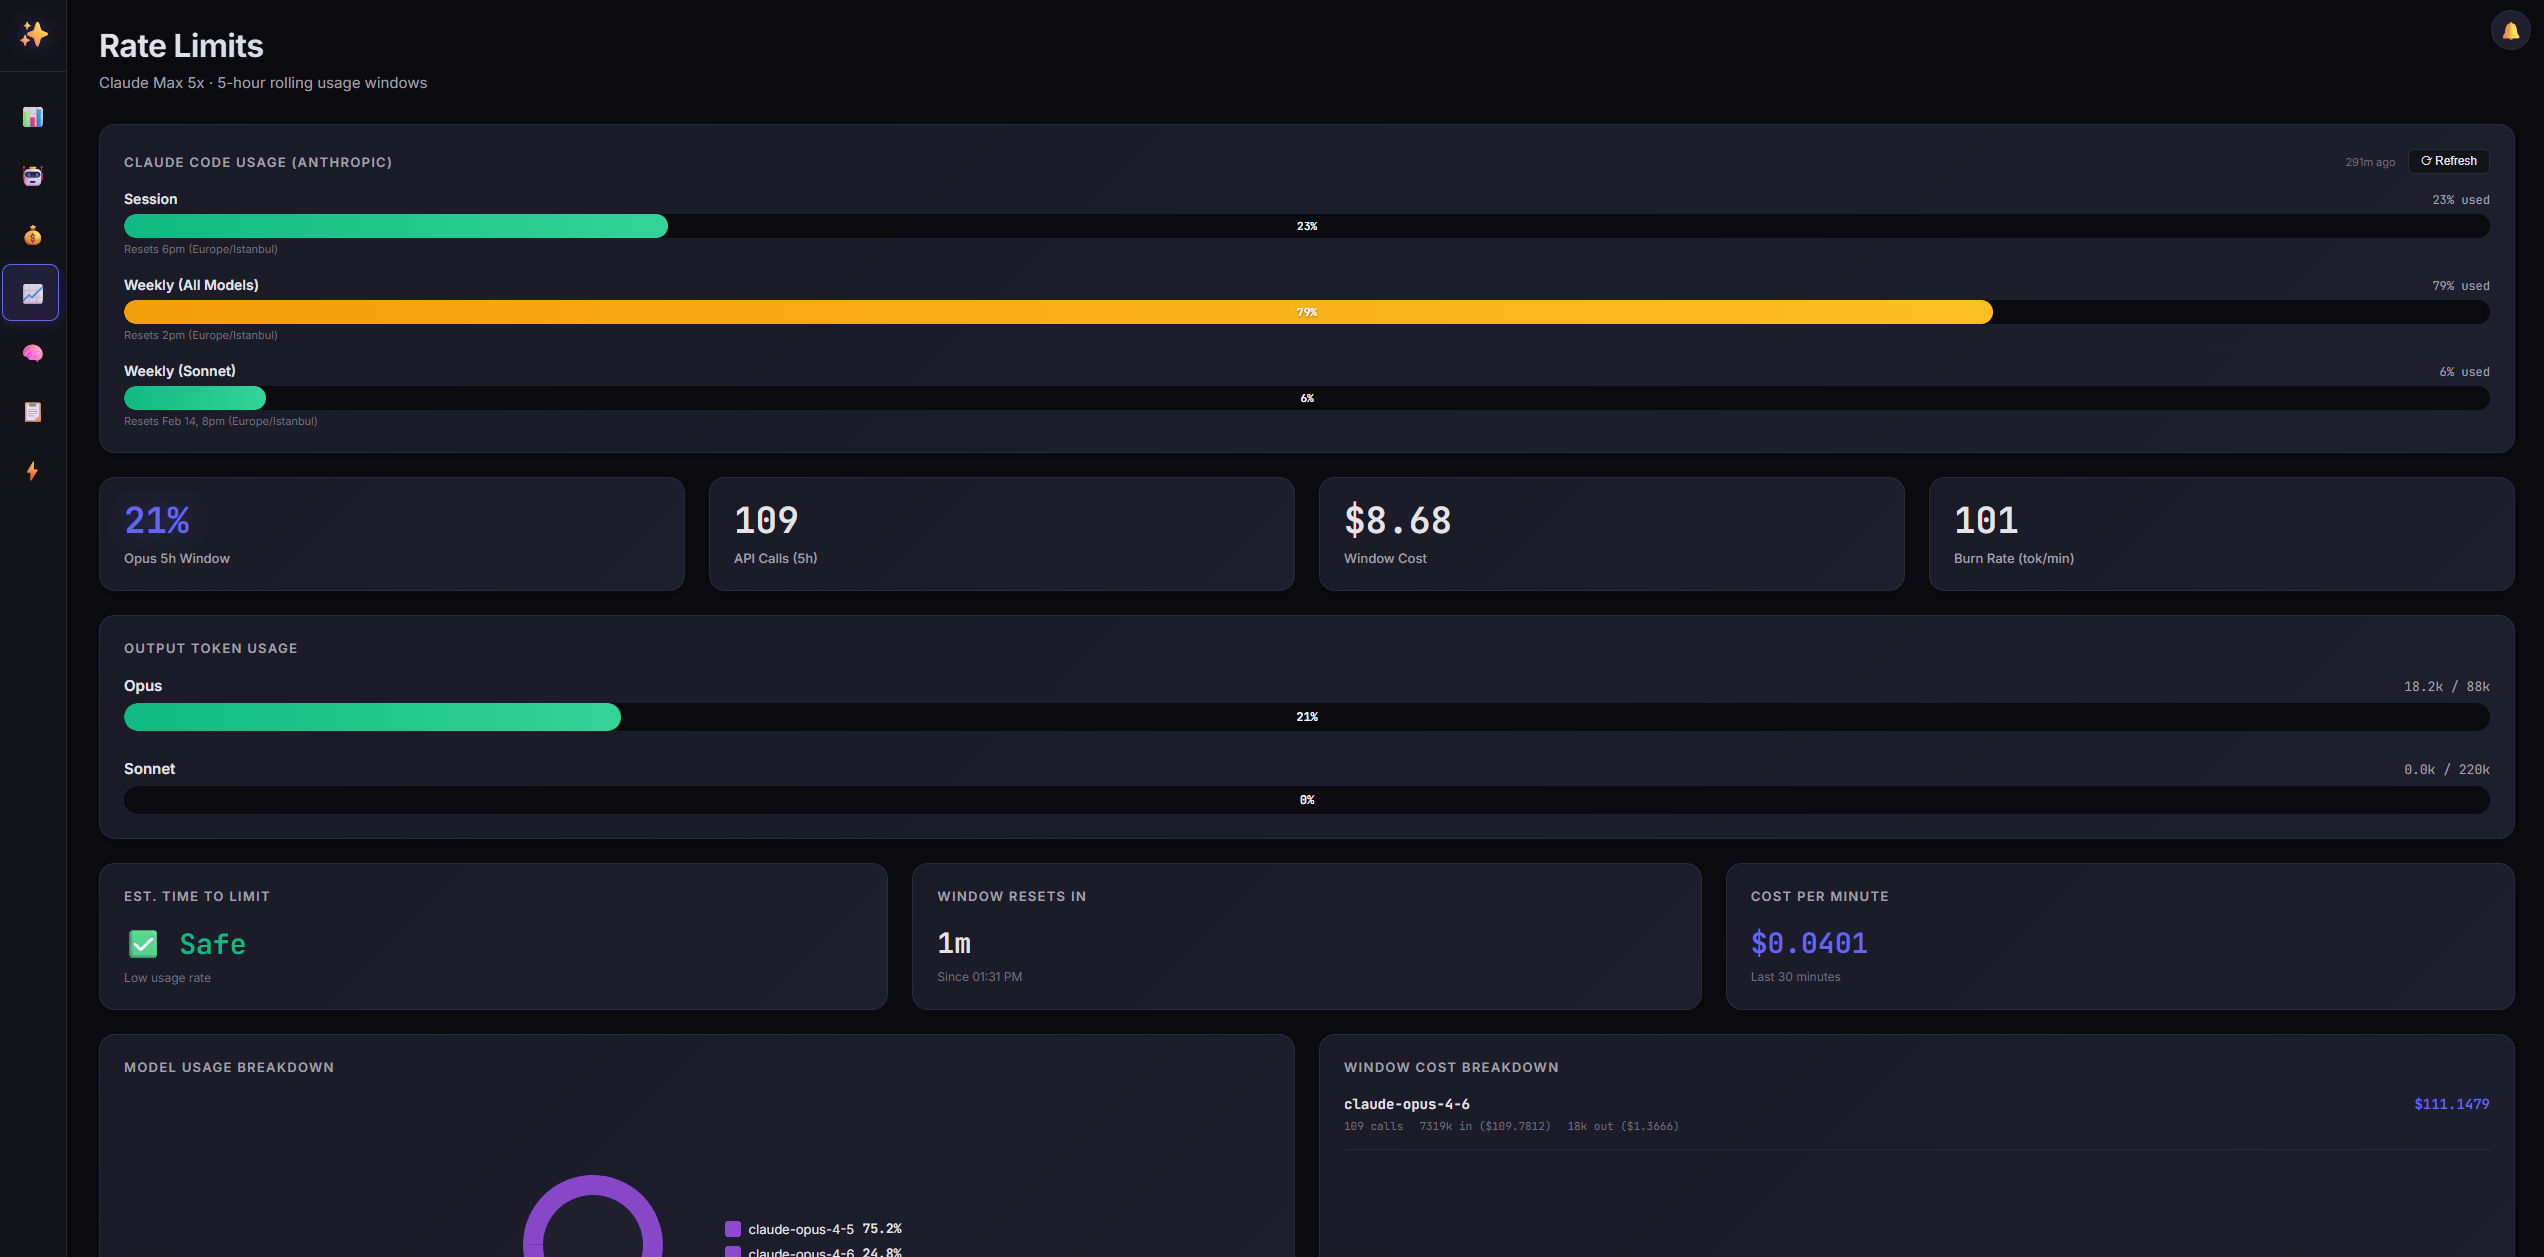 tugcantopaloglu/openclaw-dashboard
🔐 Secure, real-time monitoring dashboard for OpenClaw AI agents. Auth, TOTP MFA, cost tracking, live feed, memory browser and more.
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
 pranshuchittora/simvyn
Universal mobile devtool for Agents & Humans - control iOS Simulators, Android Emulators, and real devices from a single dashboard and CLI
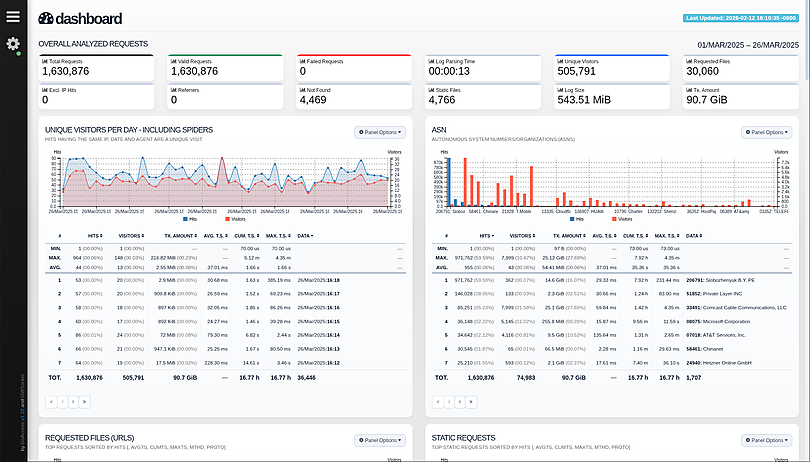 allinurl/goaccess
GoAccess is a real-time web log analyzer and interactive viewer that runs in a terminal in *nix systems or through your browser.
 jamf/aftermath
Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…