cve-2024-36401-security-simulator

Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…

Educational Python simulator modeling a fictional security incident inspired by CVE-2024-36401 to demonstrate vulnerability management, segmentation,…

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

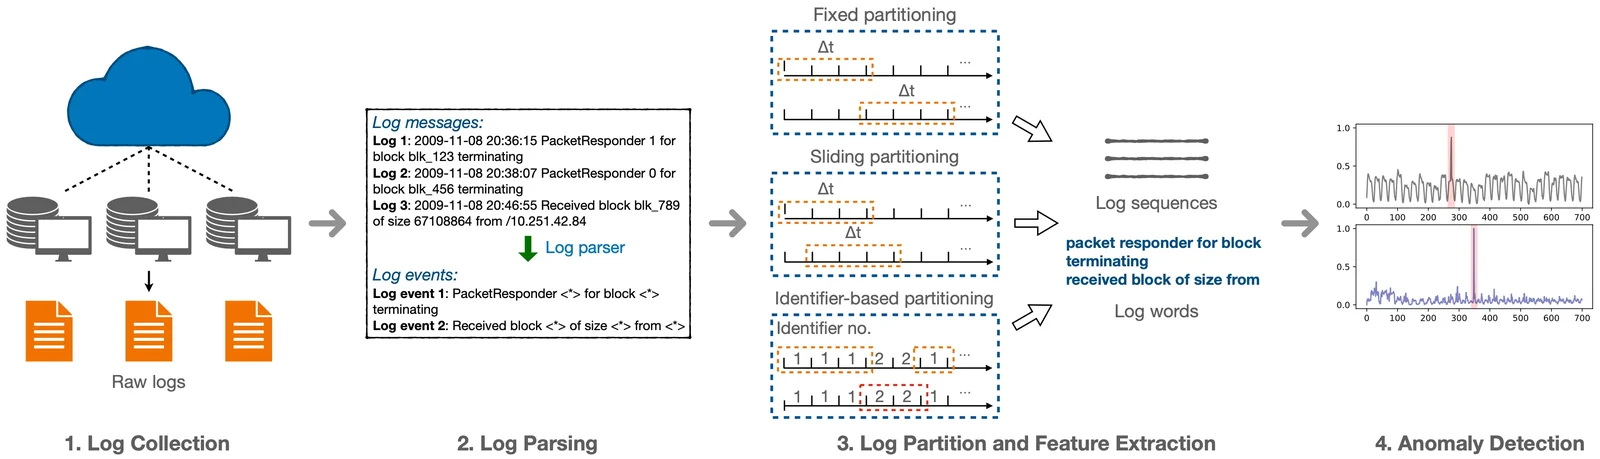
A machine learning toolkit for log-based anomaly detection [ISSRE'16]

A deep learning toolkit for log-based anomaly detection

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Continuously fetches and cryptographically verifies key transparency log updates, maintains a condensed prefix and log tree view, and returns signed…


The Sigma command line interface based on pySigma

Strelka Web UI for File Submission and Analysis

A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.

A Zeek OpenVPN protocol analyzer, based on Spicy.

Audit Preference Pane and Log Reader for OS X

analyze a web-based network traffic 🕶 to detect central command and control servers

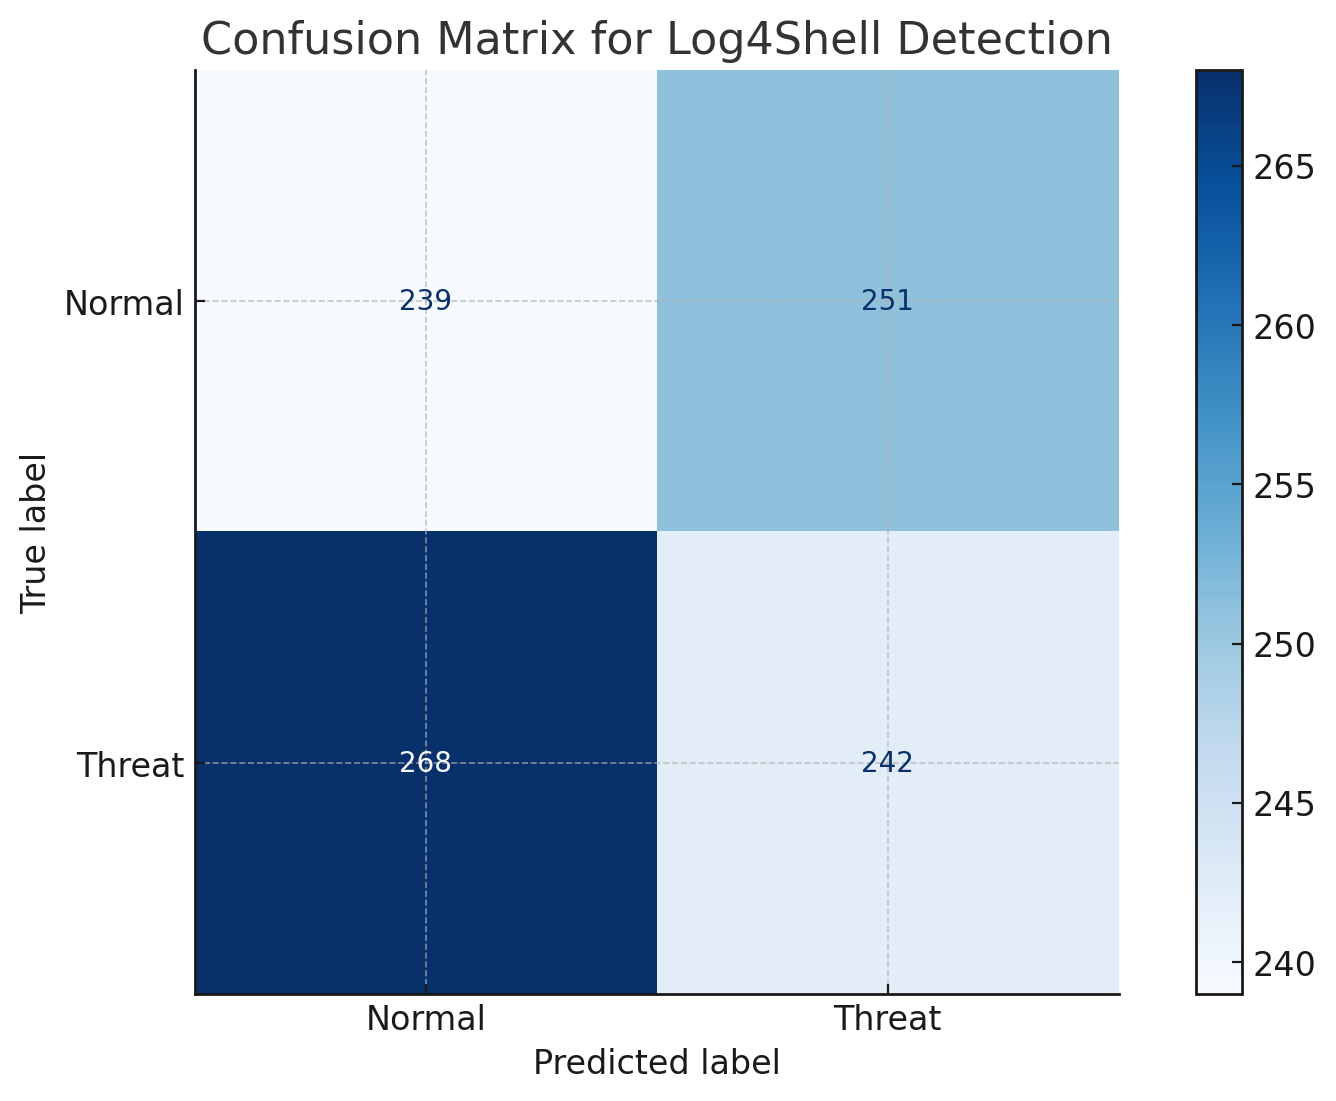
This repository provides an in-depth analysis of the Log4Shell vulnerability (CVE-2021-44228) and implements a machine learning-based approach to…

Unofficial Bash IoC checker for SonicWall SMA1000 appliances affected by actively exploited CVE-2026-15409 and CVE-2026-15410.

Script to check for IOC's created by ProxyNotShell (CVE-2022-41040 & CVE-2022-41082)

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.

CVE-2020-9483 OR CVE-2020-13921