

GPEWebDefender
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
defensive-toolsincident-responseinformation-gathering+8
2
gopasteverything/gpewebdefenderLightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 evergreencartoons/senselessviolence
CVE-2022-31814 Exploitation Toolkit.
 ahmetramazank/cve-2024-4577
Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 schira4396/vcenterkiller
一款针对Vcenter的综合利用工具,包含目前最主流的CVE-2021-21972、CVE-2021-21985以及CVE-2021-22005、One Access的CVE-2022-22954、CVE-2022-22972/31656以及log4j,提供一键上传webshell,命令执行或者上传…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
 cyprianatsyor/letsdefend-cve-2022-41082-exploitation-attempt
Detailed incident report and educational analysis of CVE-2022-41082 (ProxyNotShell) exploitation attempt on Microsoft Exchange Server, including…
 zephrfish/cve-2025-53770-scanner
ToolShell scanner - CVE-2025-53770 and detection information
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 joakimbulow/cve-2026-1337
CVE-2026-1337 - Neo4j - Log Injection
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 ne0zer01/cve-2024-27198_lab
Docker-based lab for CVE-2024-27198 TeamCity authentication bypass. Includes exploit reproduction, IoC hunting with Sigma/Suricata rules, and…
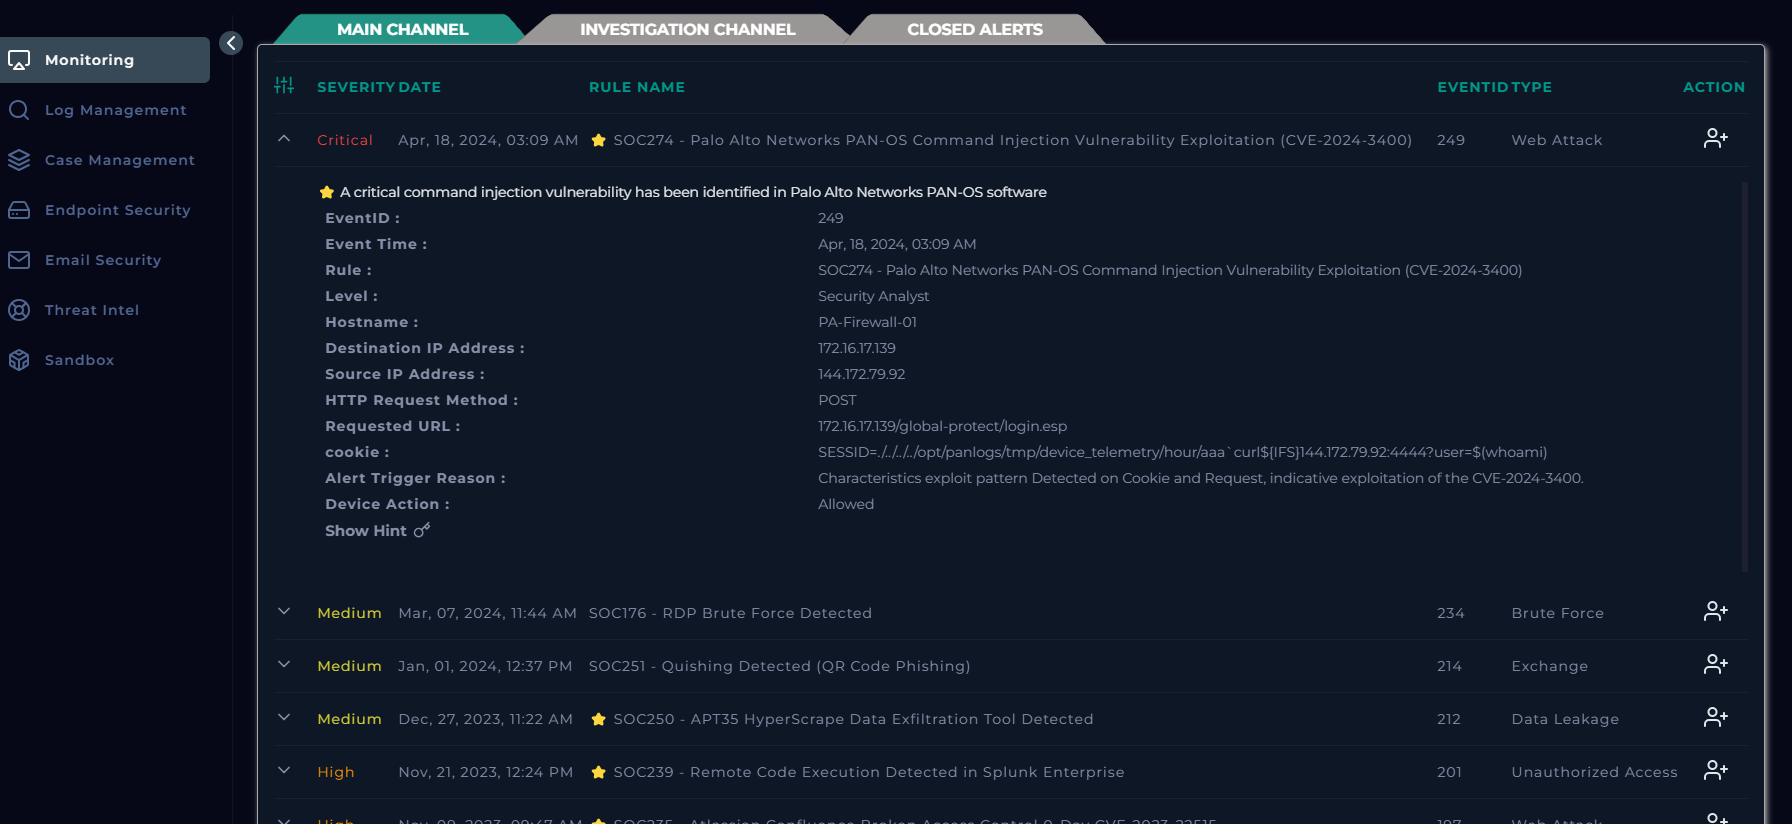 cyprianatsyor/letsdefend-cve2024-3400-case-study
Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…
 airbus-cert/cve-2024-4040
Scanner for CVE-2024-4040
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 alchemist3dot14/cve-2025-2783
Simulated PoC for CVE-2025-2783 — a sandbox escape vulnerability in Chrome's Mojo IPC. Includes phishing delivery, memory fuzzing, IPC simulation,…