
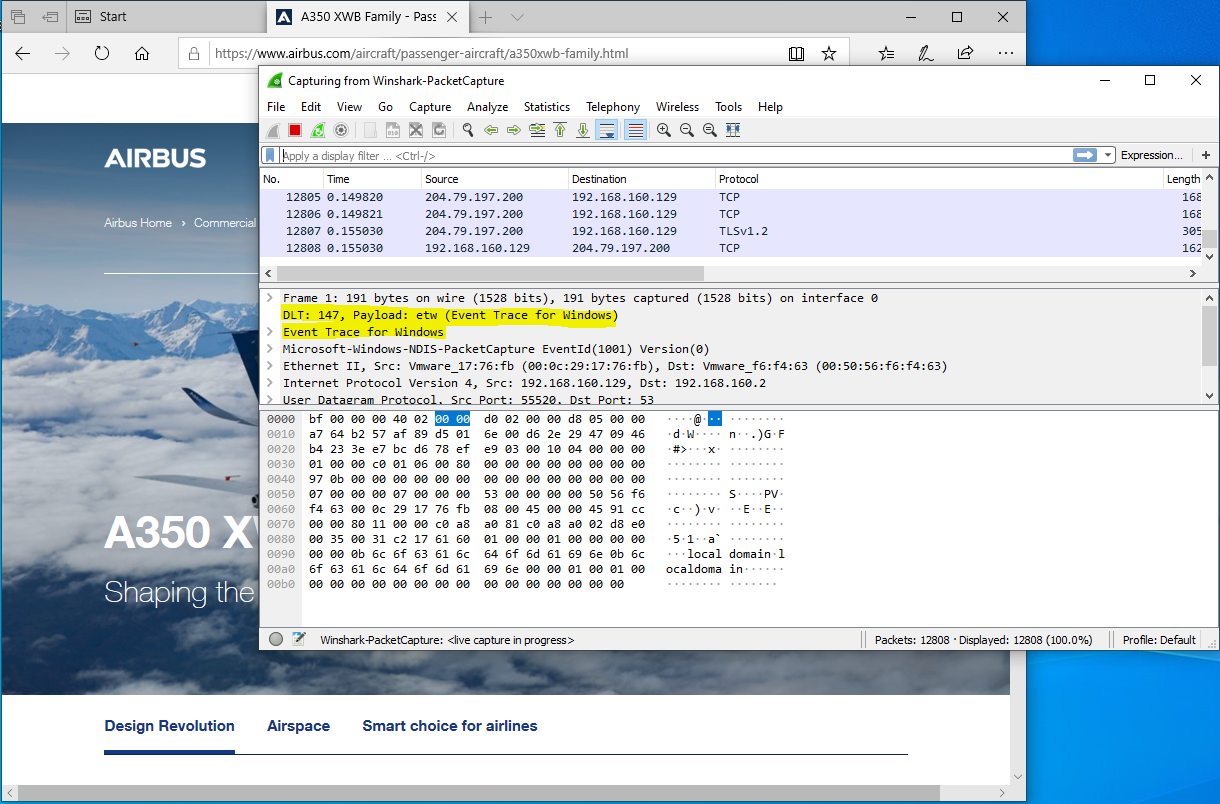
Winshark
 airbus-cert/winshark
A wireshark plugin to instrument ETW
forensicslog-analysisnetwork-security+1
airbus-cert/winsharkA wireshark plugin to instrument ETW
 phpboyscout/go/redact
Strip credential-like content from free-form strings before they reach logs or telemetry. Part of the phpboyscout Go toolkit. ·…
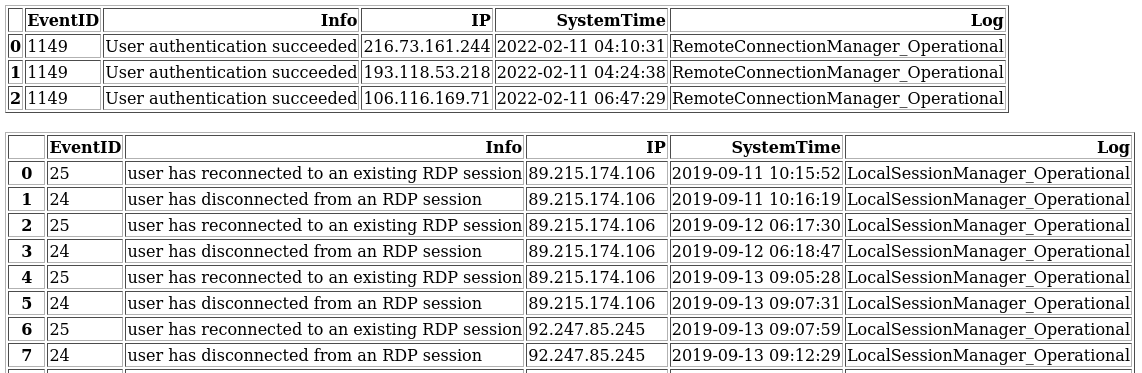 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
 michaelsanford/log4shell-honeypot
Dockerized honeypot for CVE-2021-44228.
 trustedsec/sysmoncommunityguide
TrustedSec Sysinternals Sysmon Community Guide
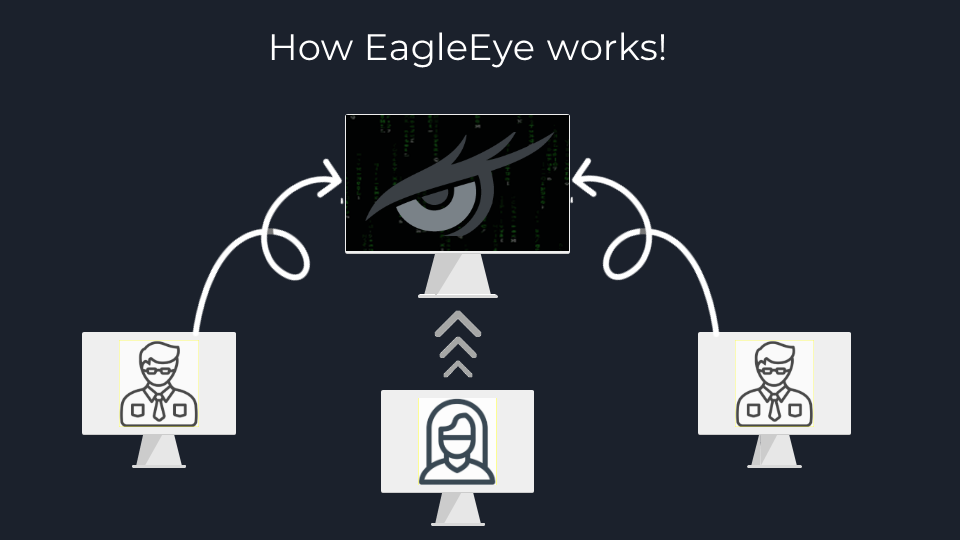 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 mingchen-script/cve-2020-1472-visualizer
PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…