
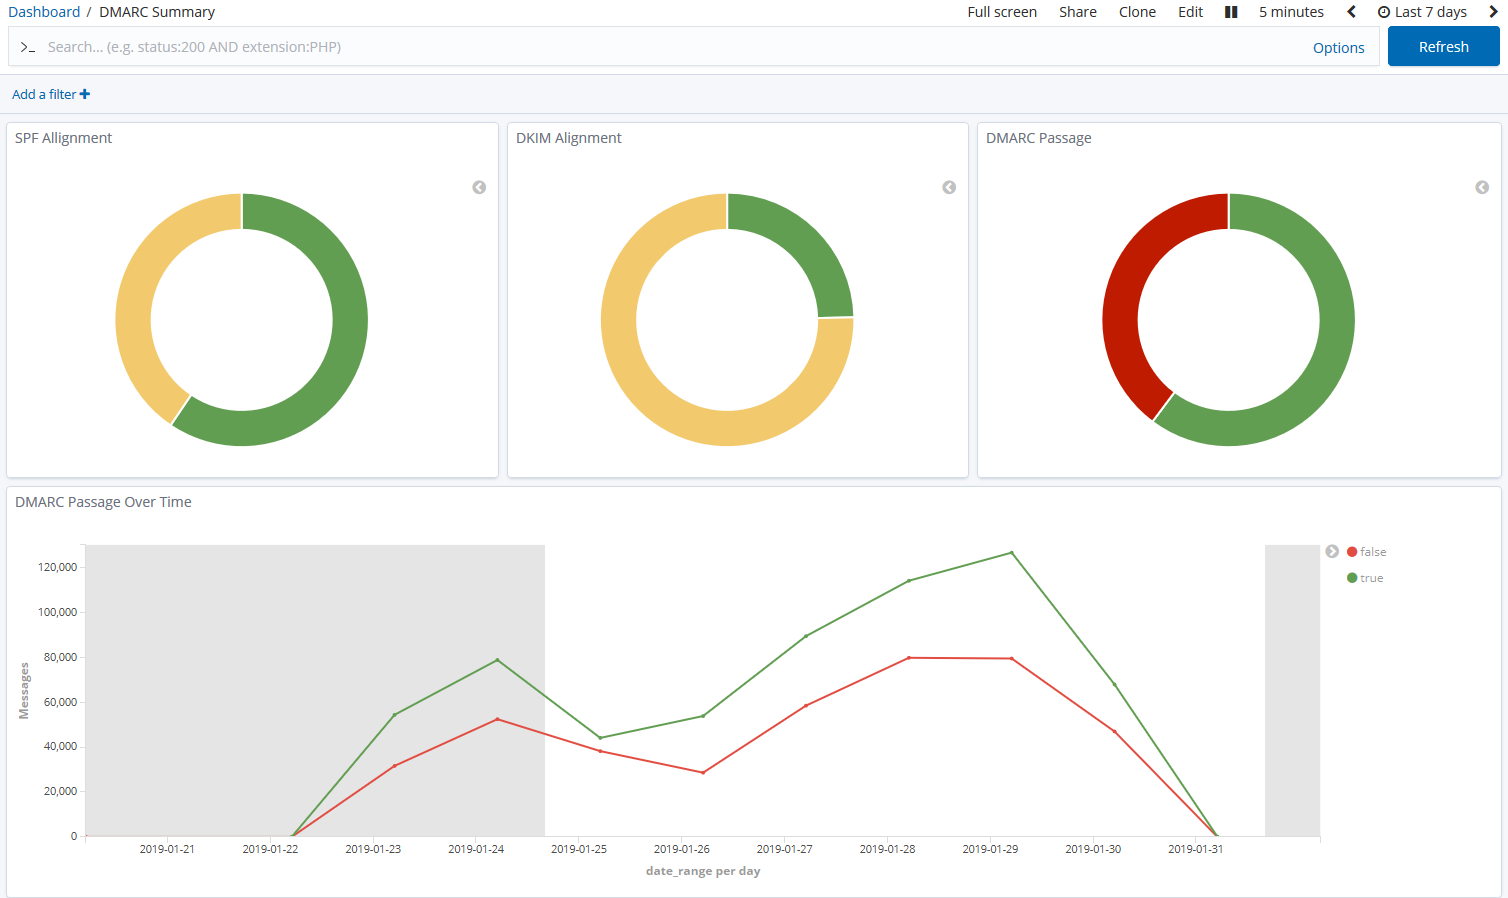
parsedmarc
 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
authenticationdefensive-toolsdns-analysis+2
1.3k3 days ago
domainaware/parsedmarcA Python package and CLI for parsing aggregate and forensic DMARC reports
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 anssi-fr/dfir4vsphere
Powershell module for VMWare vSphere forensics
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 atlassion/rs4logj-cve-2021-44228
Provides upgrade and mitigation instructions for Apache Log4j vulnerability CVE-2021-44228 in Remote Syslog products, including version checks and…
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection