phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Automated IP ban service that detects failed login attempts from event logs and files, blocking attackers on Windows and Linux via firewall…

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…

The easiest, and most secure way to access and protect all of your infrastructure.

An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity

Enhanced SSH client with TUI — manage connections, keys, and sessions

SSH bastion/jump host/jumpserver

PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…

HonSSH is designed to log all SSH communications between a client and server.

Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…

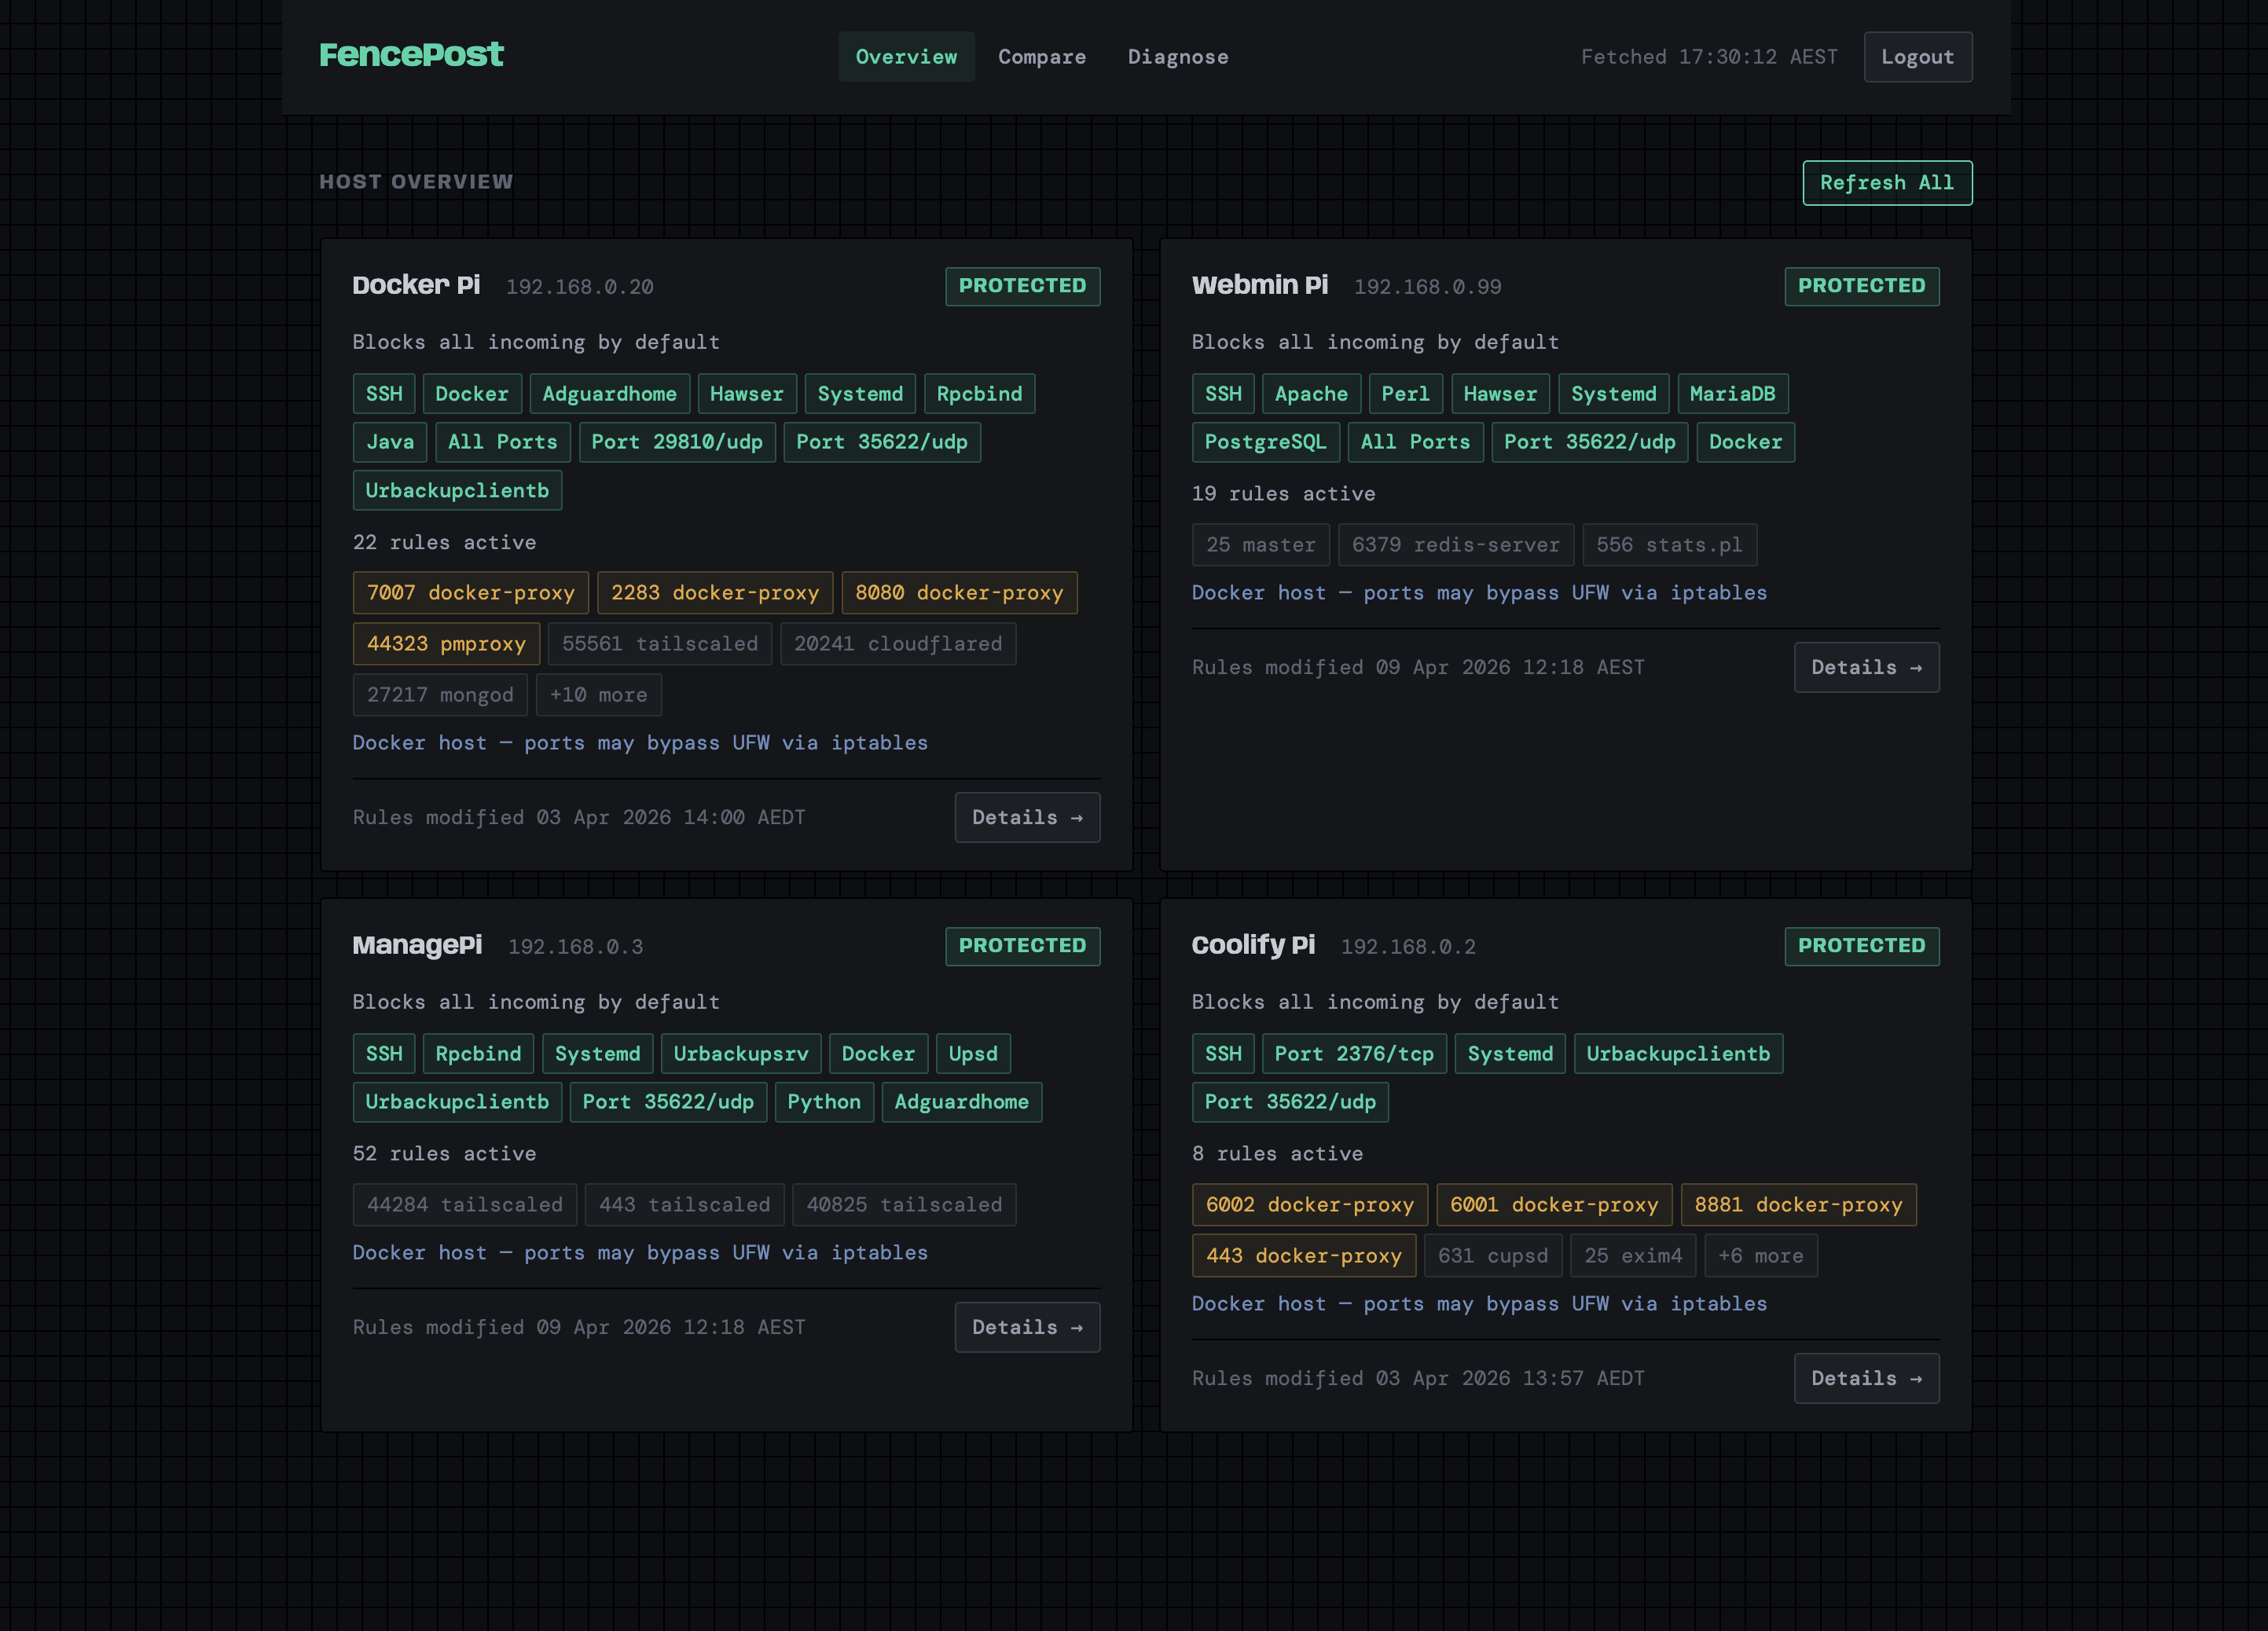
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…

A collection of scripts which may come in handy during your freedom fighting activities.

This project explores whether modern OpenSSH reveals valid usernames through subtle response or timing differences. CVE-2016-6210 user enumeration…

Experimental Decoy Broker