
ALEAPP
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
digital-forensicsincident-responselog-analysis+1
abrignoni/aleappAndroid Logs Events And Protobuf Parser
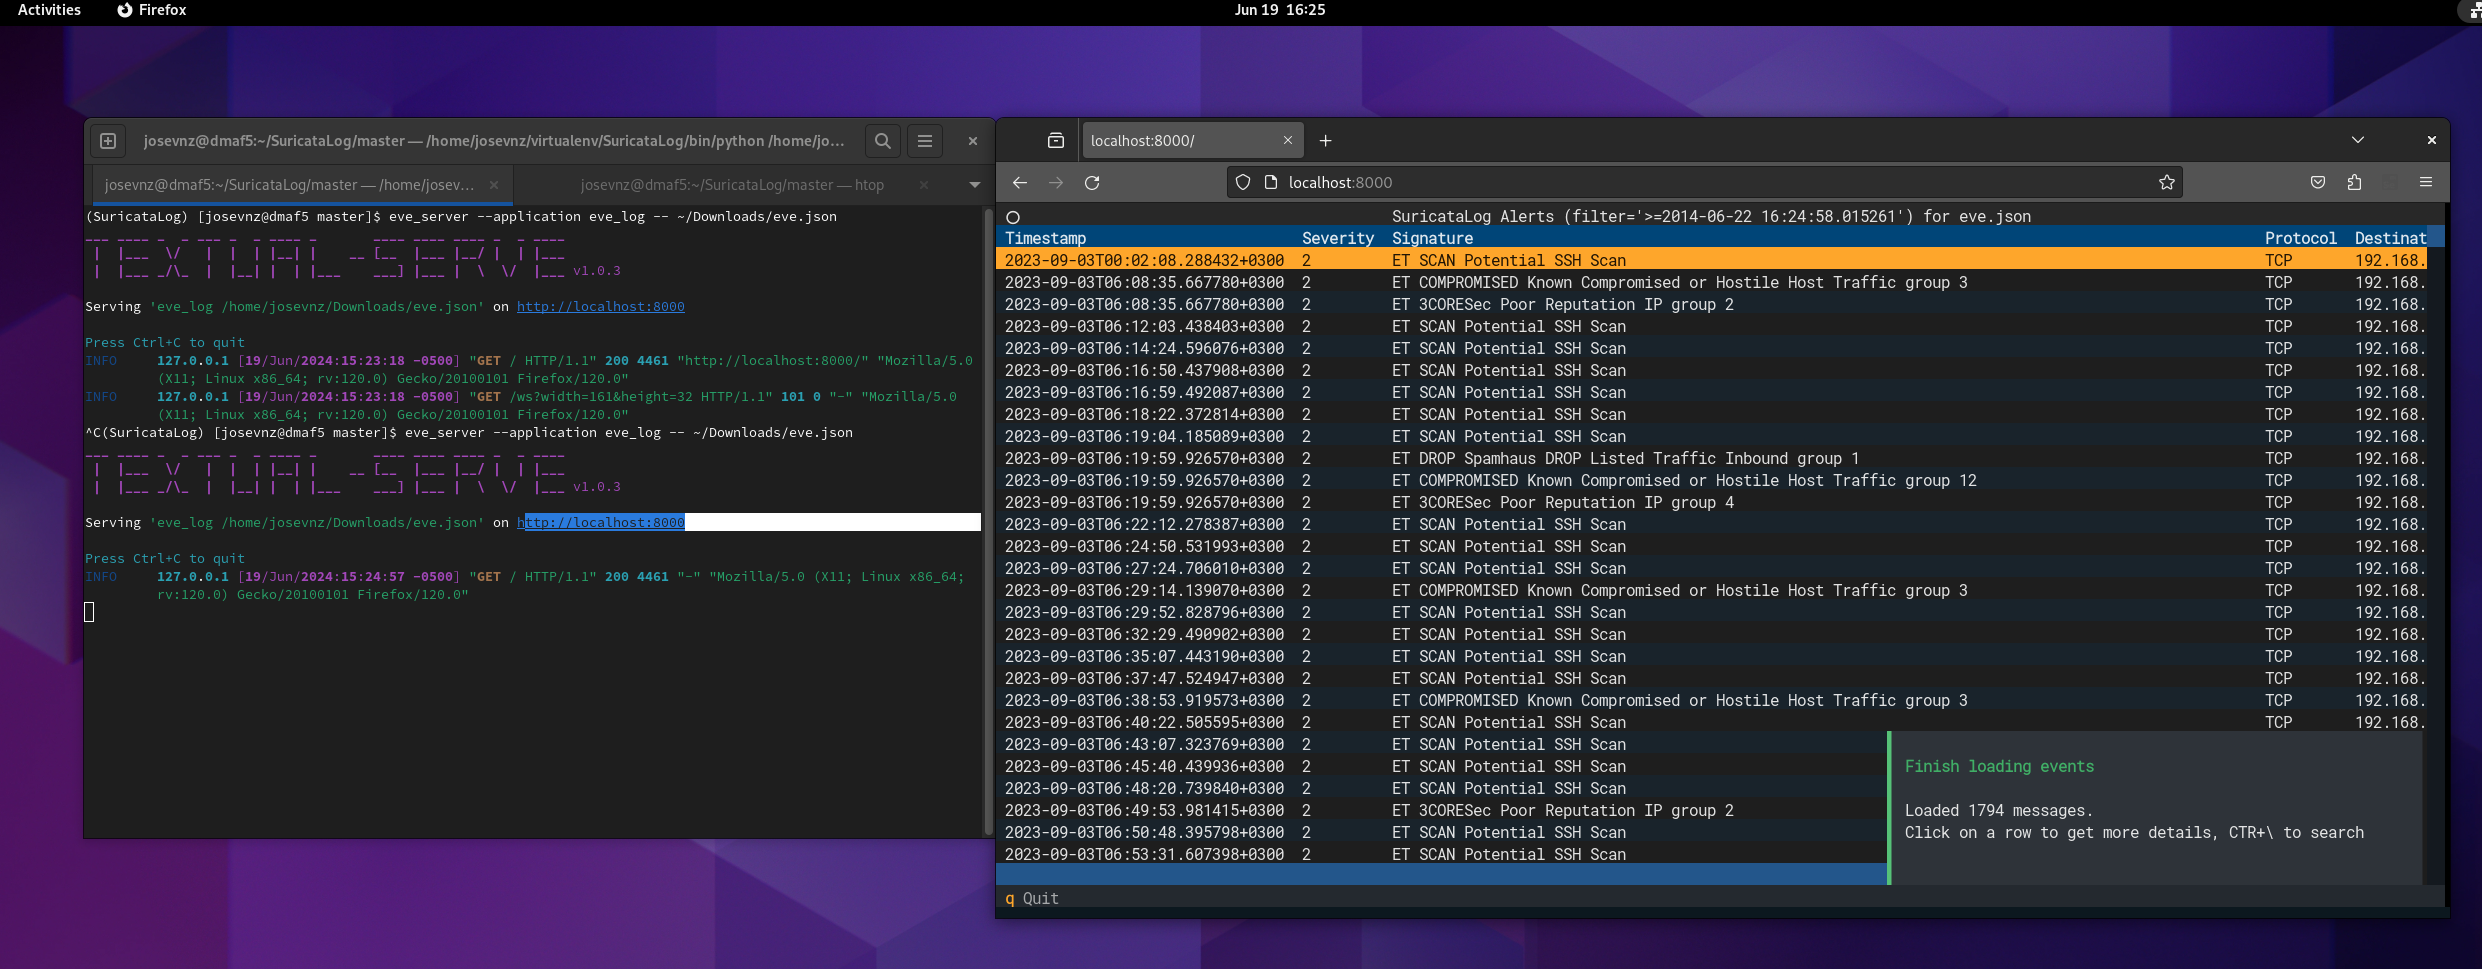 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…
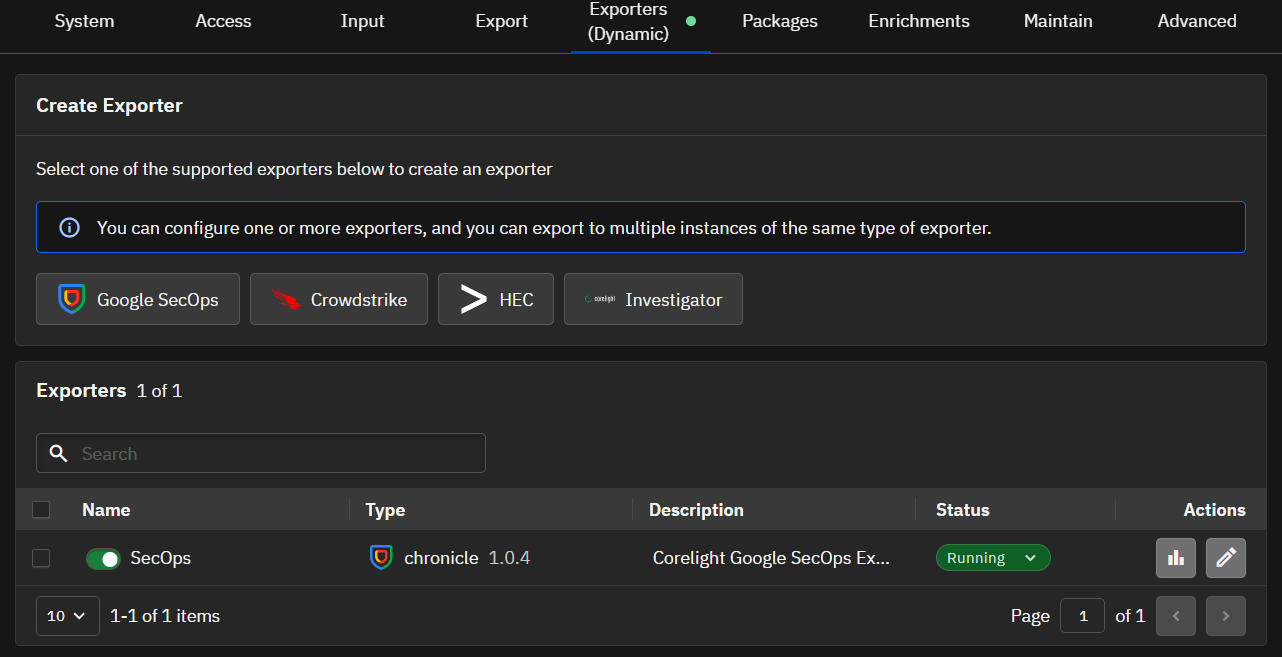 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 zh54321/snafflerparser
Parses Snaffler output file and generate beautified outputs.
 airbus-cert/etl-parser
Event Trace Log file parser in pure Python
 certat/citrix-logchecker
Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 tenzir/tenzir
Collect, parse, normalize, aggregate, store, query, and route security telemetry data at scale using pipeline-based dataflows for threat detection…
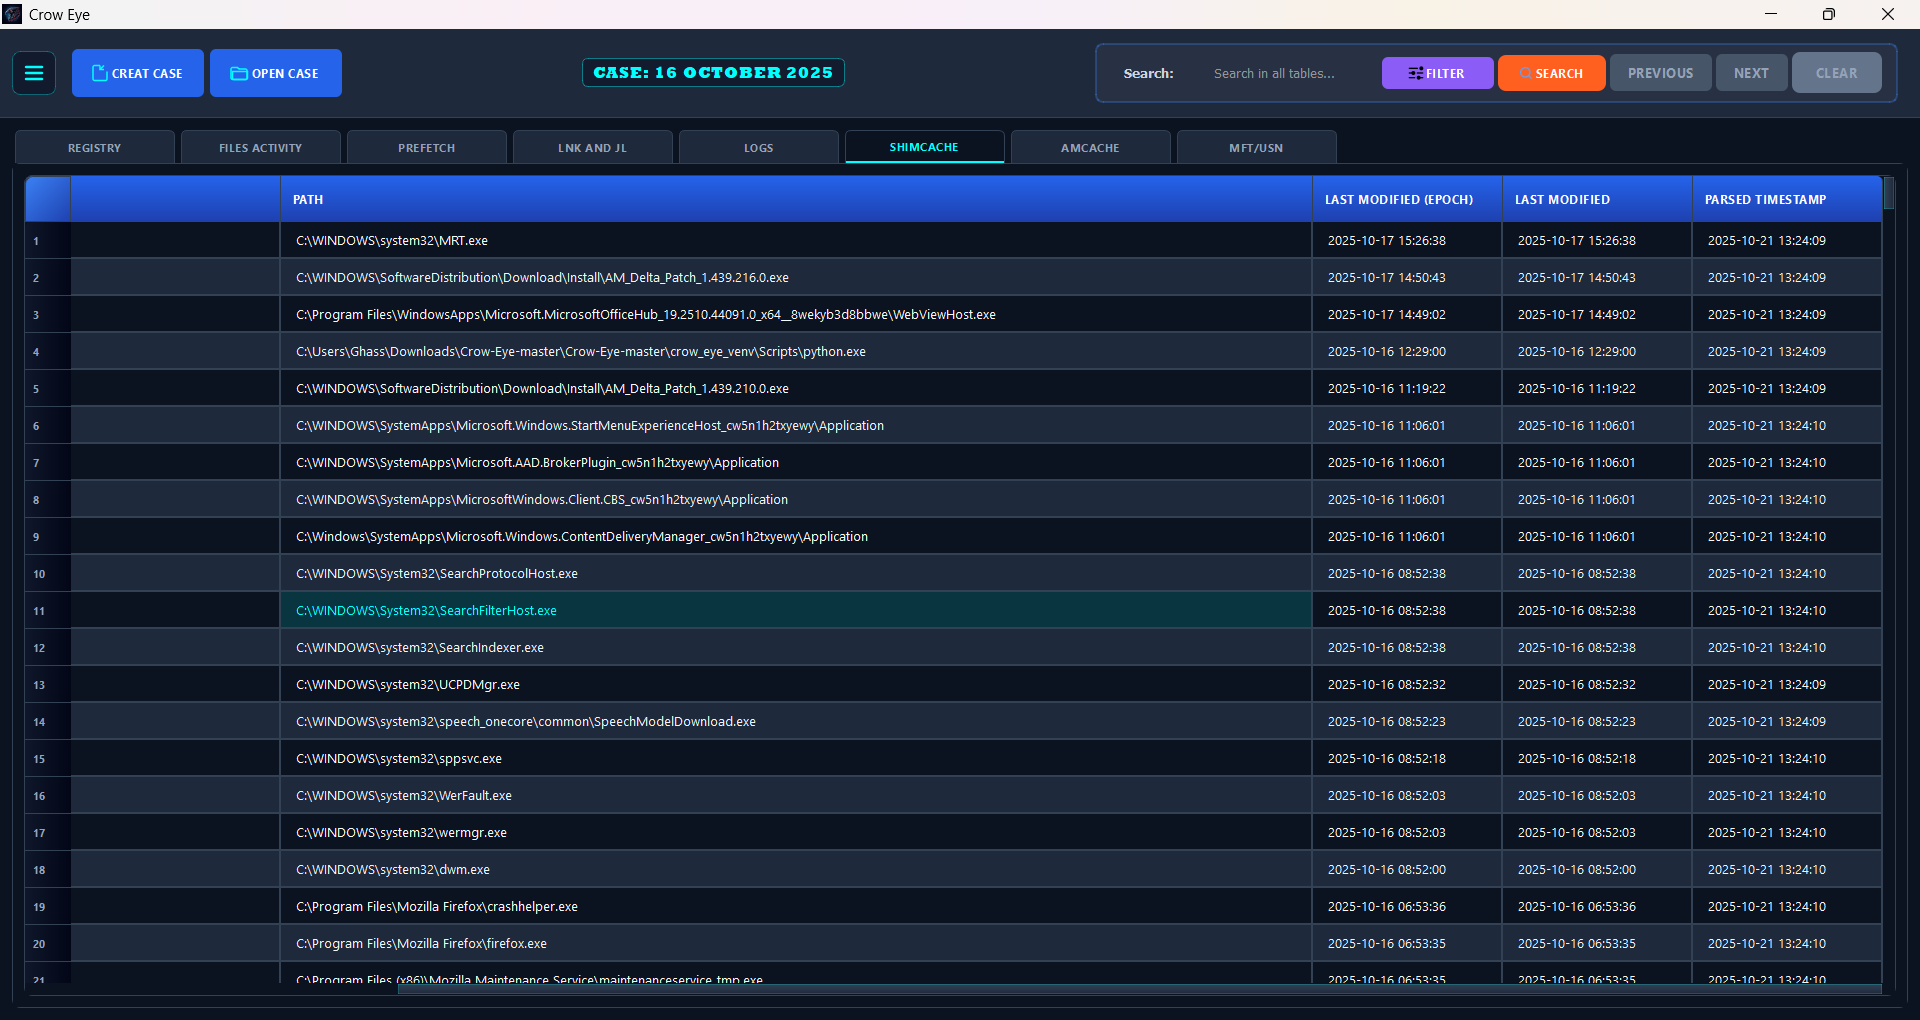 ghassan-elsman/crow-eye
Open-source Windows forensics engine that acquires, parses, and correlates artifacts (MFT, USN, Registry, etc.) to reconstruct timelines with…
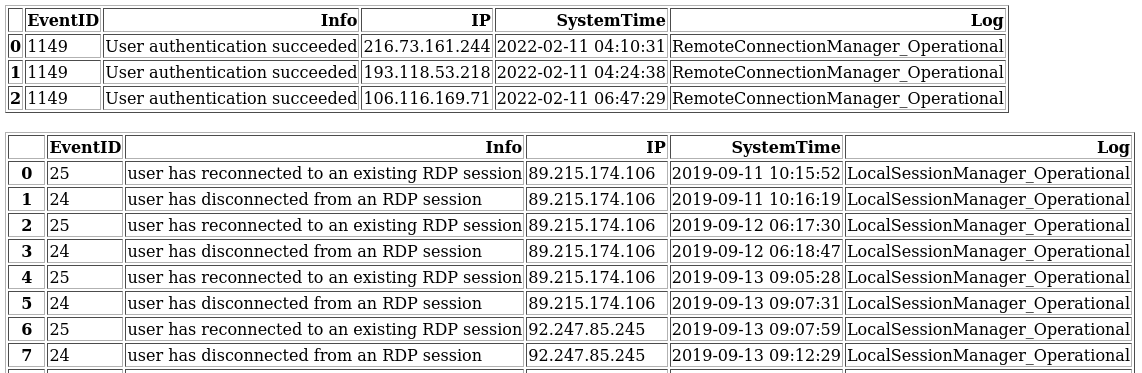 georgi-i/winevt_logs_analysis
Parses Windows .evtx logs to identify remote connections and public IPs by analyzing EventIDs related to remote logins and sessions.
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.
 jschicht/logfileparser
Parser for $LogFile on NTFS
 rnb-team/loghound
Post-Exploitation EVTX Analyzer for BloodHound Mapping
 corelight/zeek-quic
Bro analyzer that detects Google's QUIC protocol
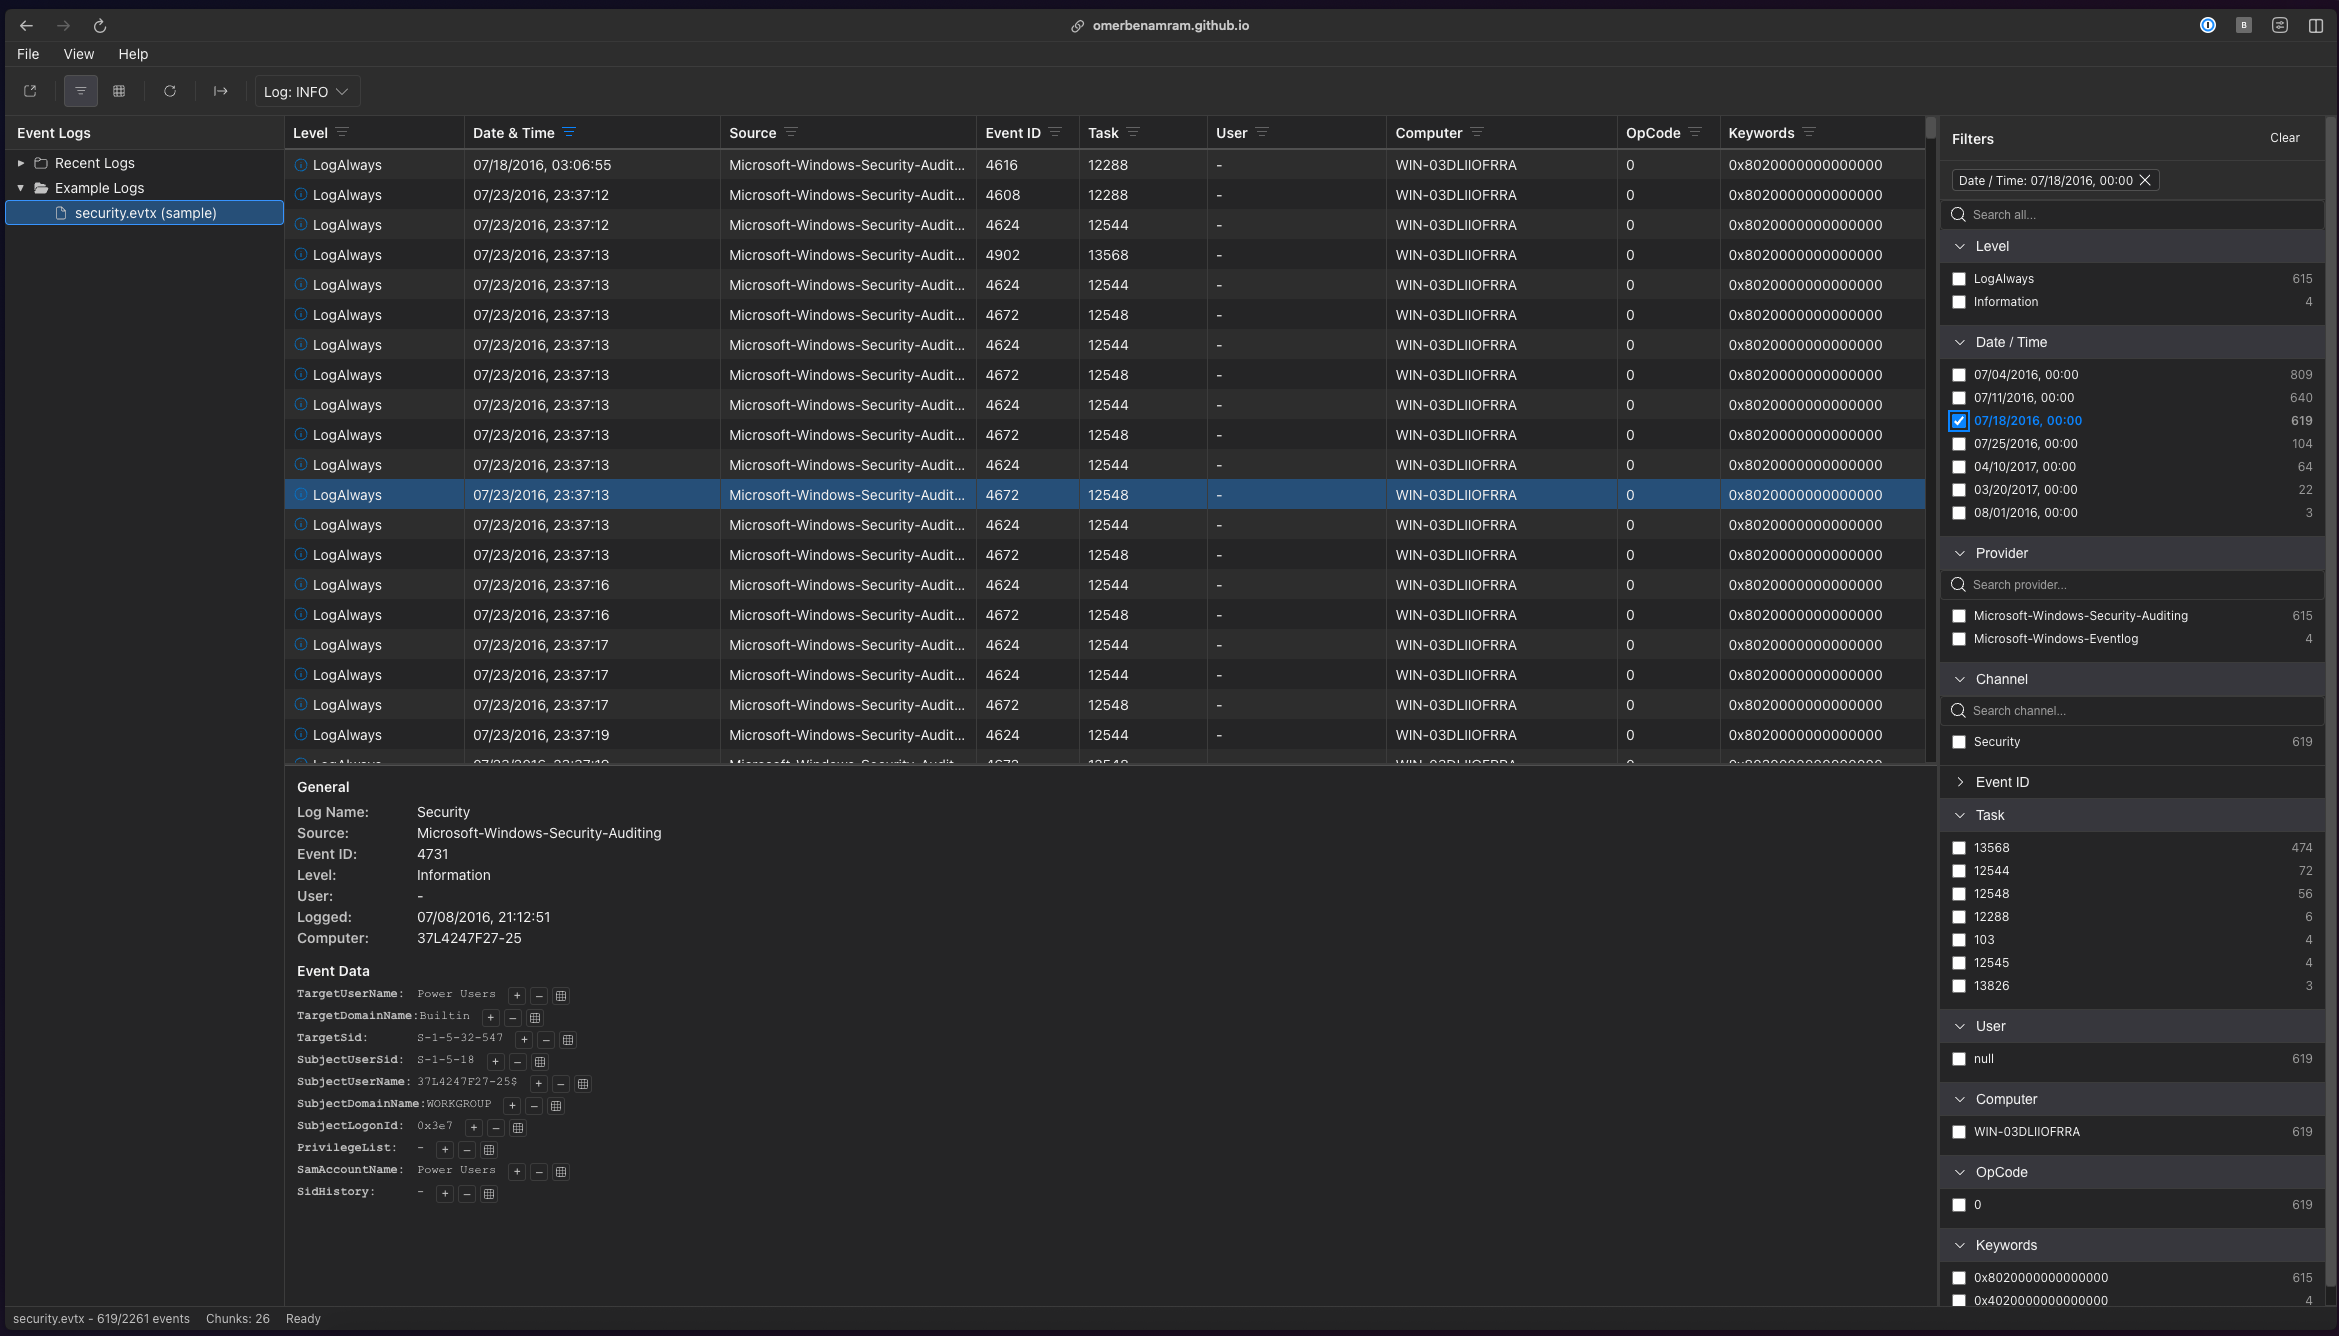 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format