Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Python CLI/TUI for forensic triage of Ubuntu systems — detects and remediates persistence mechanisms with artifact collection, timeline correlation,…

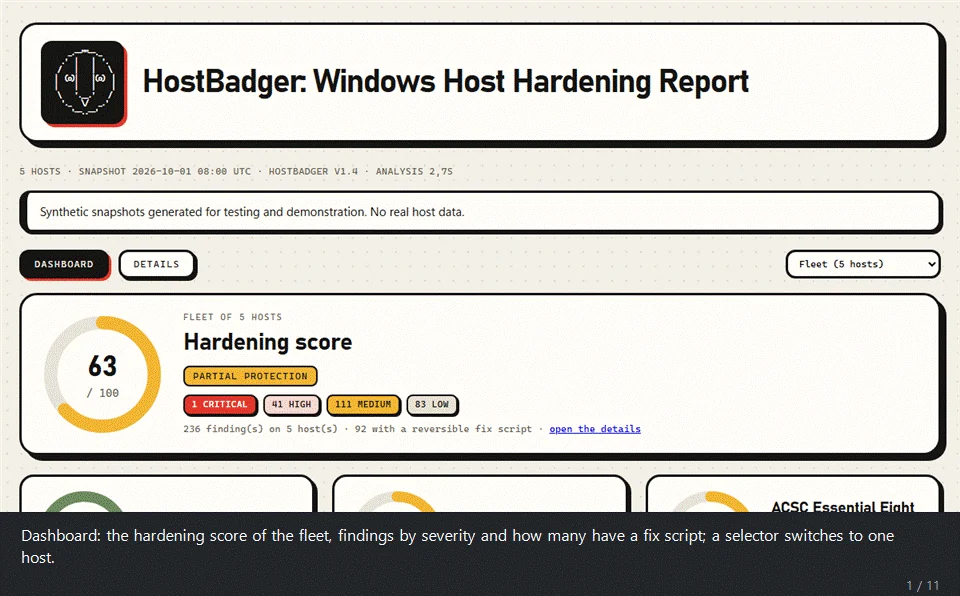
Windows host hardening auditor and remediation tool in PowerShell: CIS, DISA STIG, Essential Eight checks, reversible fixes, optional AI analysis

Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…

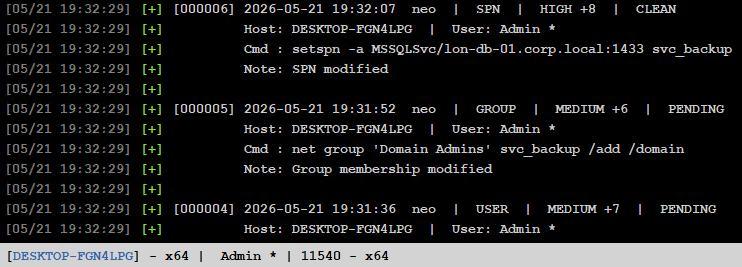
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…

CVE-2022-31814 Exploitation Toolkit.

AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

Kvasir: Penetration Test Data Management

Data from a BRAWL Automated Adversary Emulation Exercise

macos-collector - Automated Collection of macOS Forensic Artifacts for DFIR

A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…


Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…

CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script

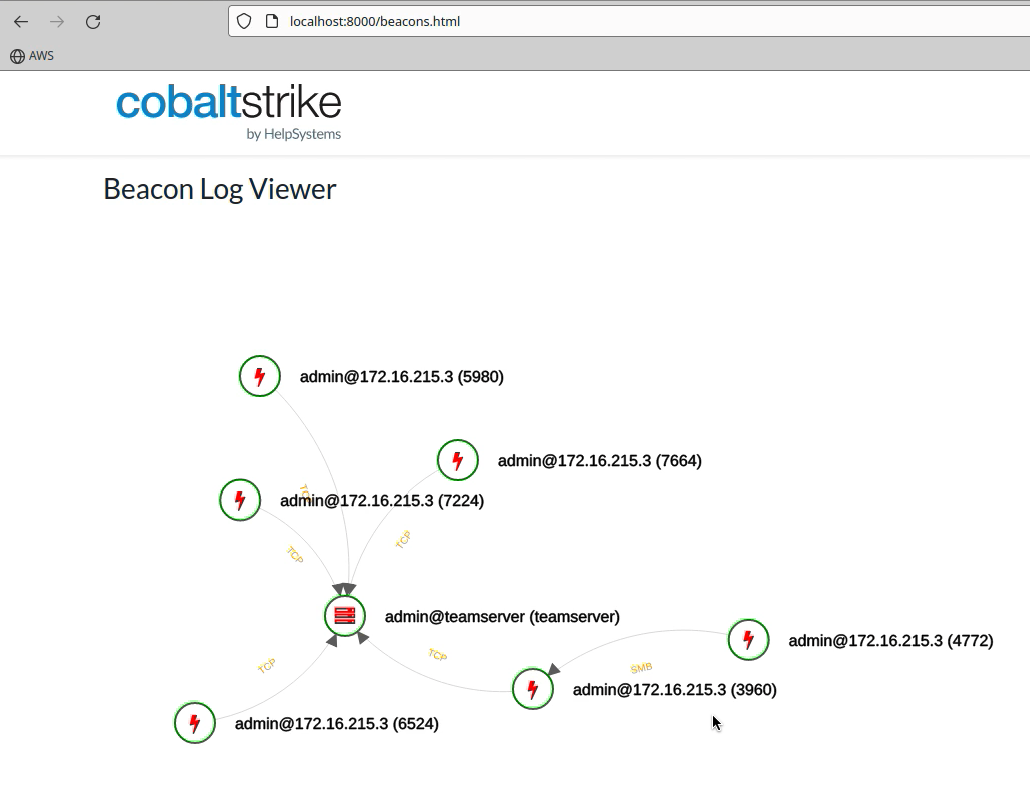
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…

Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…

Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…