Incident-Response-Powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
digital-forensicsdisk-forensicsforensics+6
824

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…

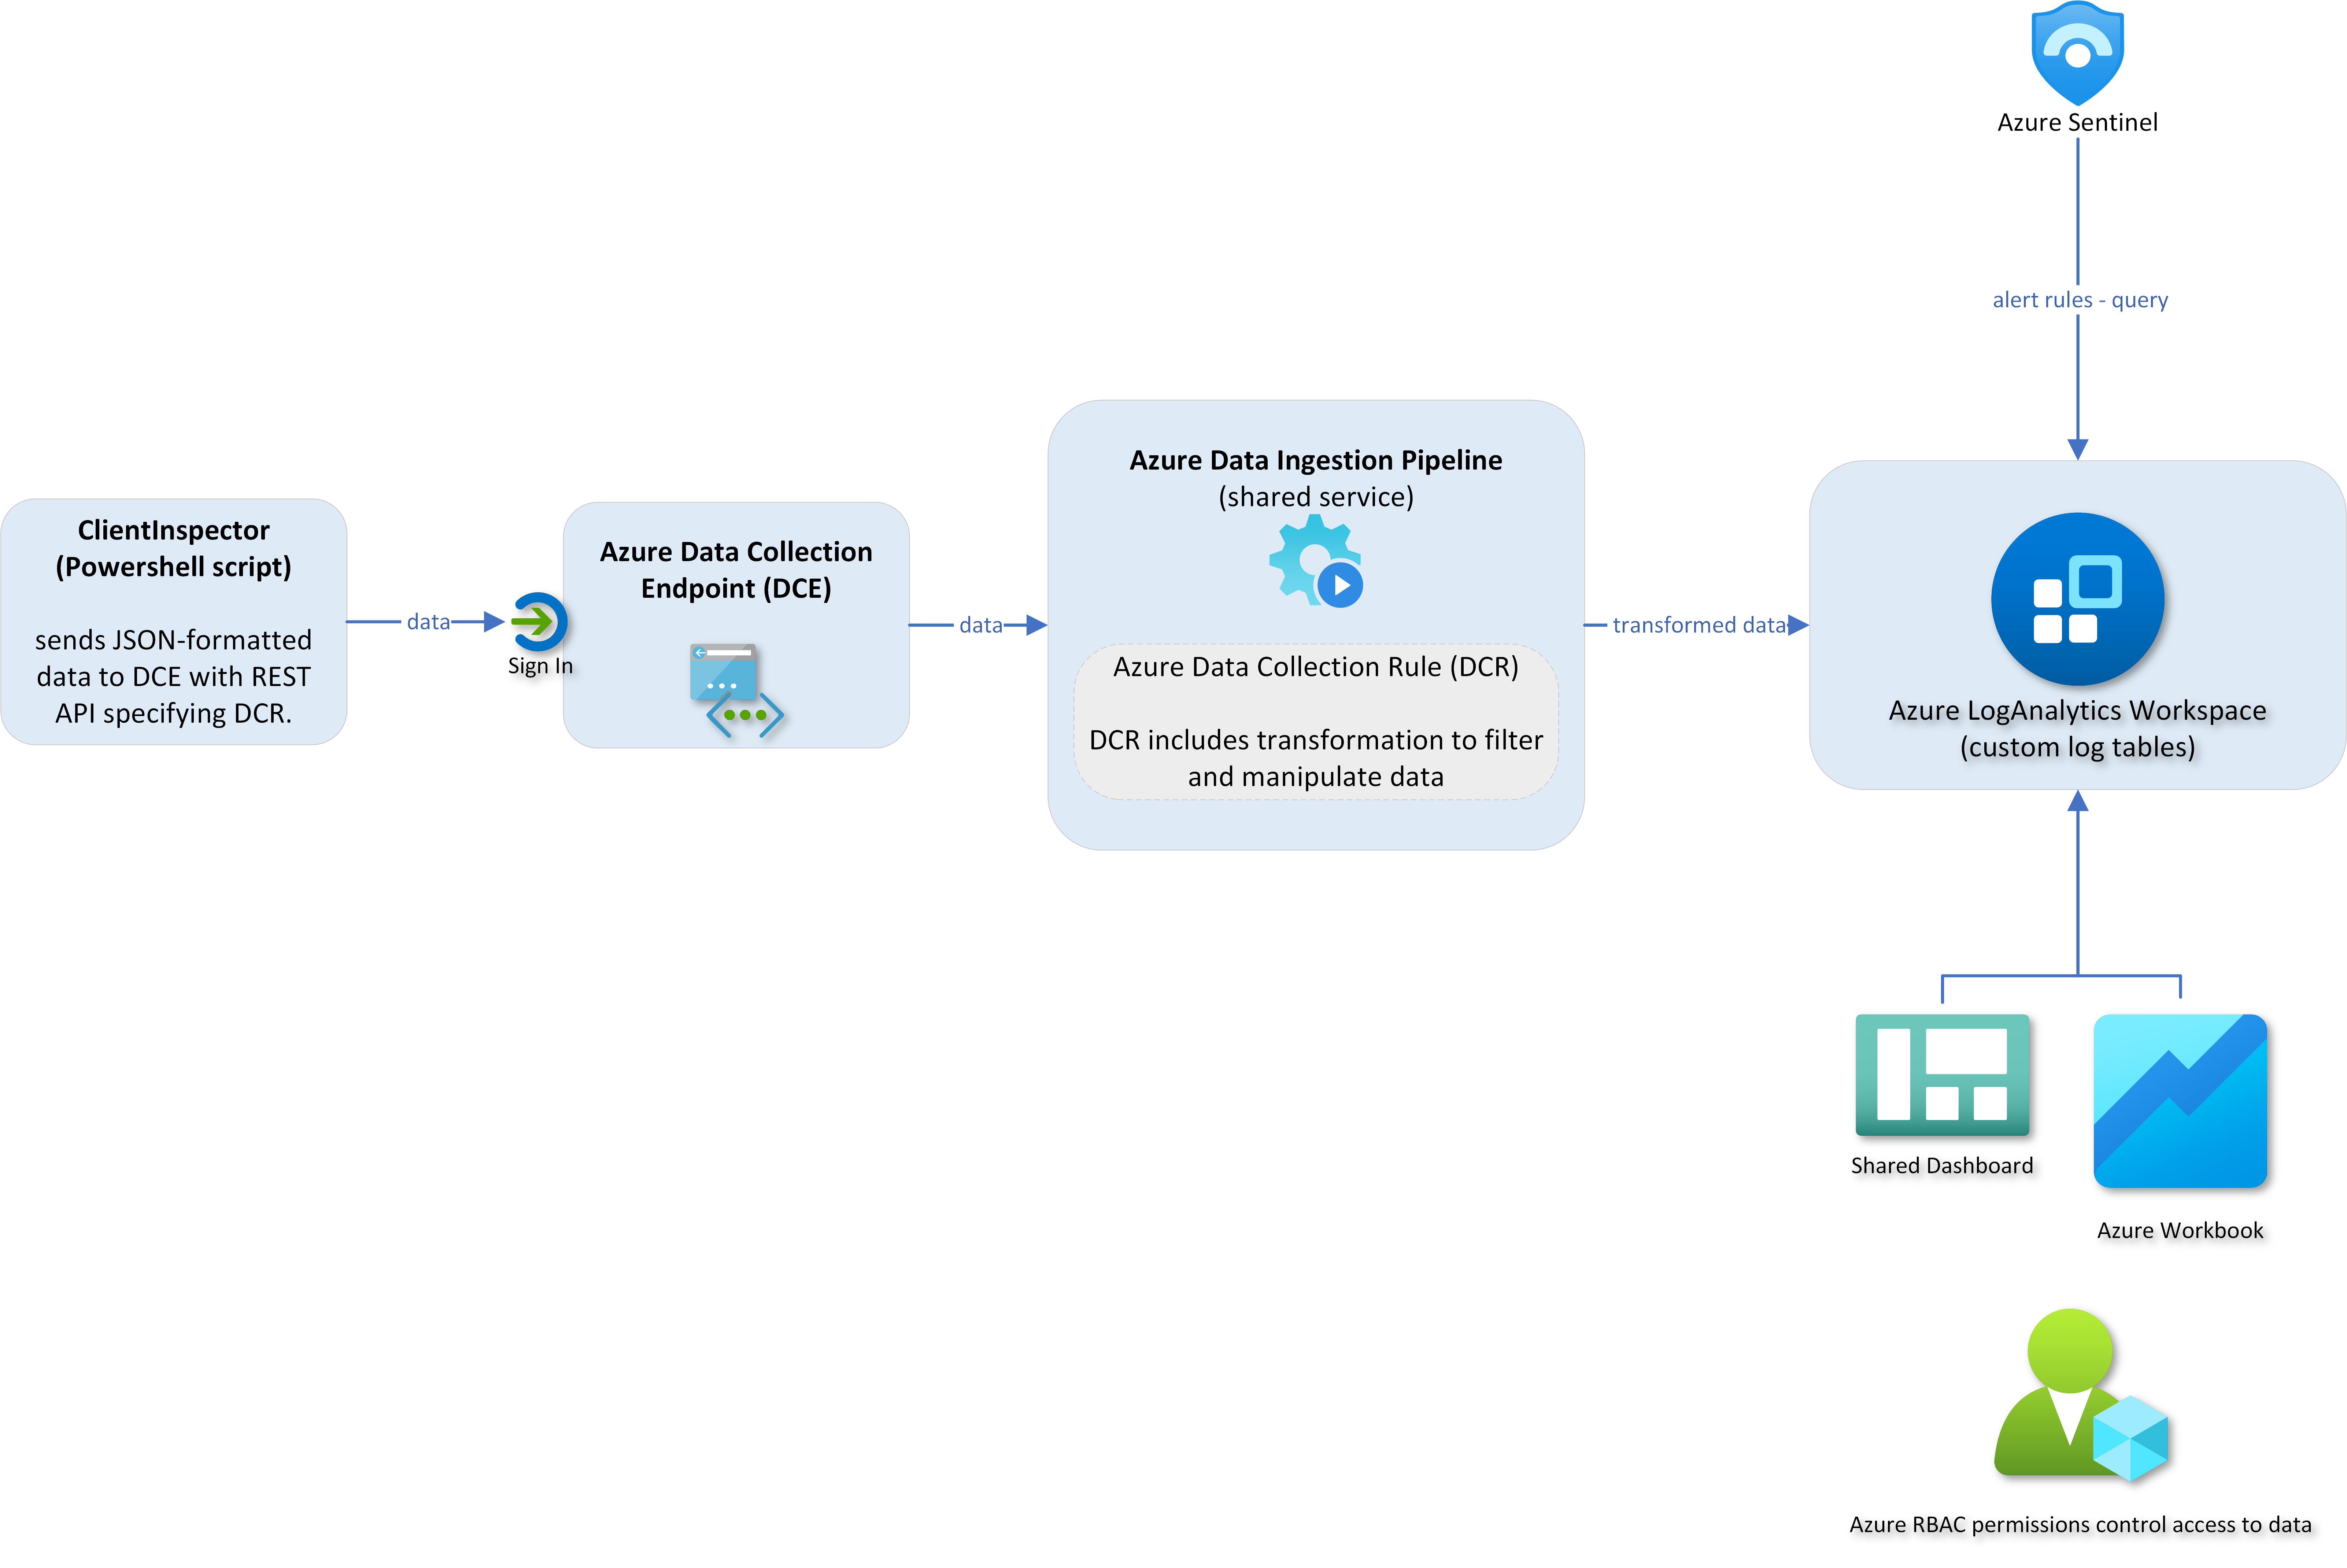
Azure-based client inventory and drift detection tool that collects Windows configuration data (antivirus, patching, Bitlocker) into LogAnalytics for…

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…