

zeek
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
zeek/zeekZeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
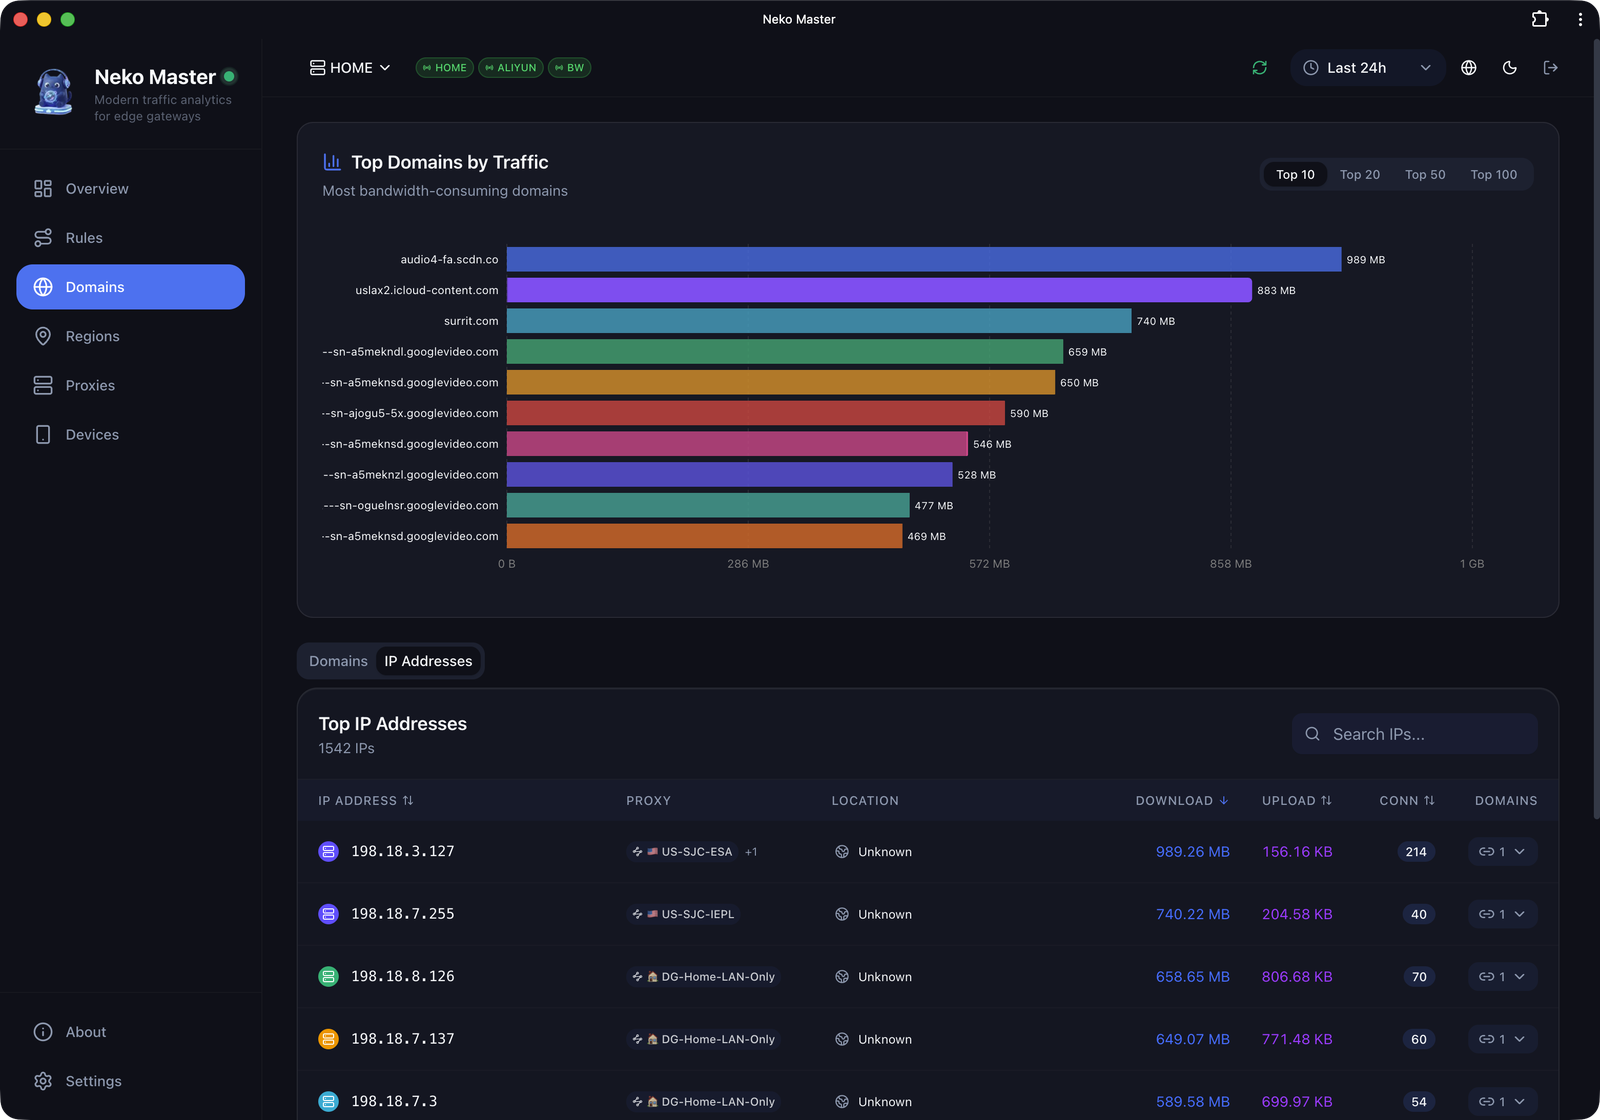 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
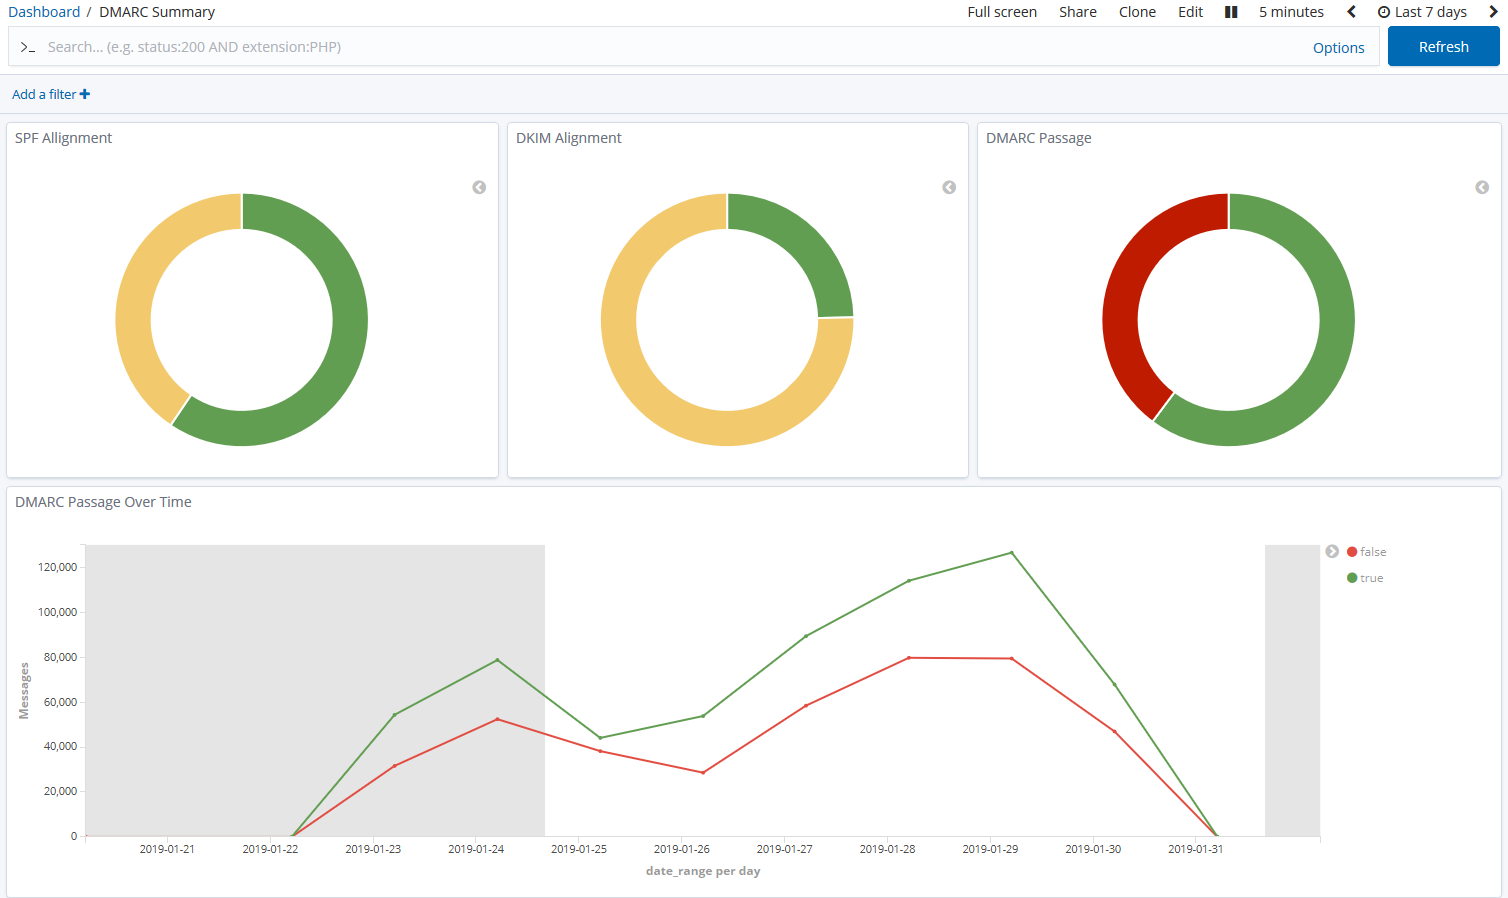 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
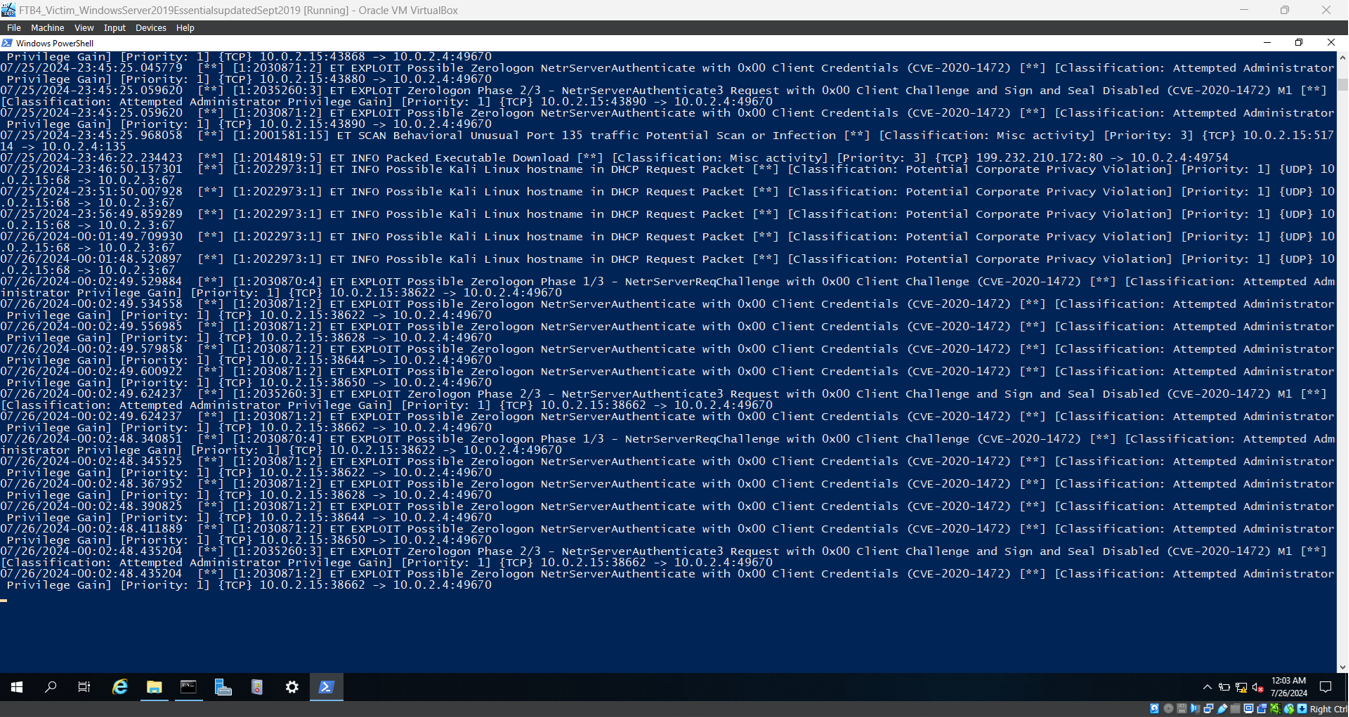 tdevworks/cve-2020-1472-zerologon-demo-detection-mitigation
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…
 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 mitre/brawl-public-game-001
Data from a BRAWL Automated Adversary Emulation Exercise
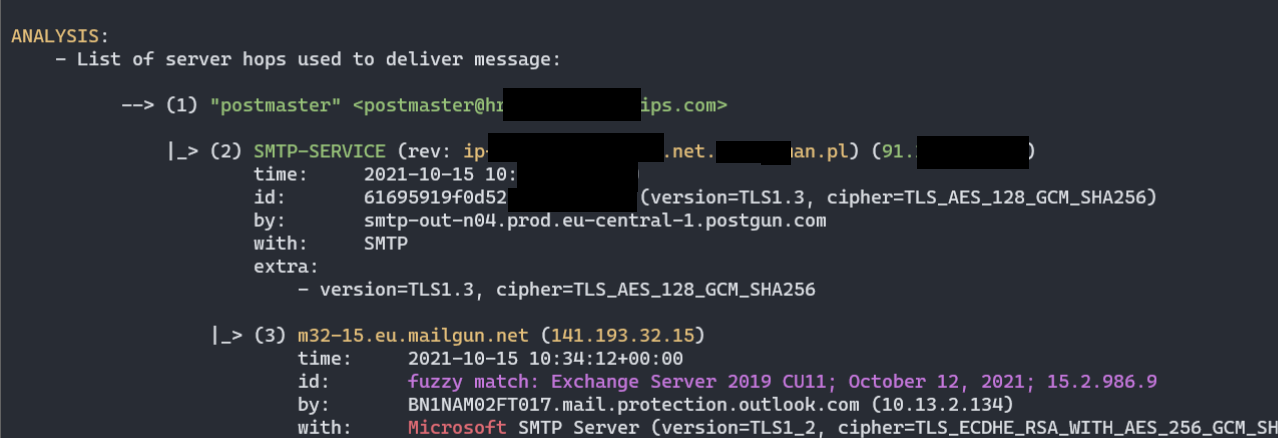 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
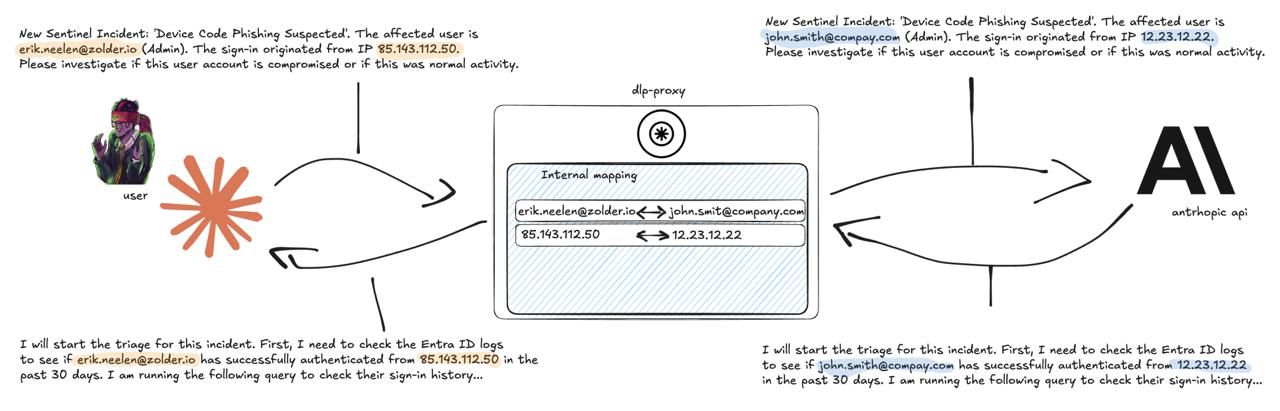 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 gossithedog/threathunting
Tools for hunting for threats.
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…