
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
CloudGrappler preview

CloudGrappler

GitHubpermiso-io-tools/cloudgrappler

Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.
cloud-securitydefensive-toolsincident-response+2
267
10 months ago
chainsaw preview

chainsaw

GitHubwithsecureopensource/chainsaw

Rapidly Search and Hunt through Windows Forensic Artefacts

defensive-toolsdigital-forensicsforensics+4
3.7k29 days ago
SenselessViolence preview

SenselessViolence

GitHubevergreencartoons/senselessviolence

CVE-2022-31814 Exploitation Toolkit.
command-and-controlexploitationlog-analysis+7
44 years ago
CVE-2020-1472-ZeroLogon-Demo-Detection-Mitigation preview

CVE-2020-1472-ZeroLogon-Demo-Detection-Mitigation

GitHubtdevworks/cve-2020-1472-zerologon-demo-detection-mitigation

Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…
educationids-ips-evasionintrusion-detection+3
1 year ago
nightHawkResponse preview

nightHawkResponse

GitHubbiggiesmallsag/nighthawkresponse

Incident Response Forensic Framework
digital-forensicsdisk-forensicsforensics+7
6076 years ago
EventLogging preview
Archived

EventLogging

GitHubblackhillsinfosec/eventlogging

Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.

configuration-auditingdefensive-toolsincident-response+3
4911 year ago
icannTLD preview

icannTLD

GitHubcorelight/icanntld

Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
dns-analysisinformation-gatheringintrusion-detection+3
81 year ago
DShield-SIEM preview

DShield-SIEM

GitHubbruneaug/dshield-siem

DShield Sensor Log Collection with ELK
defensive-toolsincident-responseintrusion-detection+4
501 month ago
defender preview

defender

GitLab0warn/defender

This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
anomaly-detectionauthenticationconfiguration-auditing+6
6 months ago
pywintrace preview

pywintrace

GitHubfireeye/pywintrace

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

defensive-toolsdigital-forensicsincident-response+2
3033 years ago
pySigma preview

pySigma

GitHubsigmahq/pysigma

Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
defensive-toolsintrusion-detectionlog-analysis+2
59713h 45m ago
zeek2es preview

zeek2es

GitHubcorelight/zeek2es

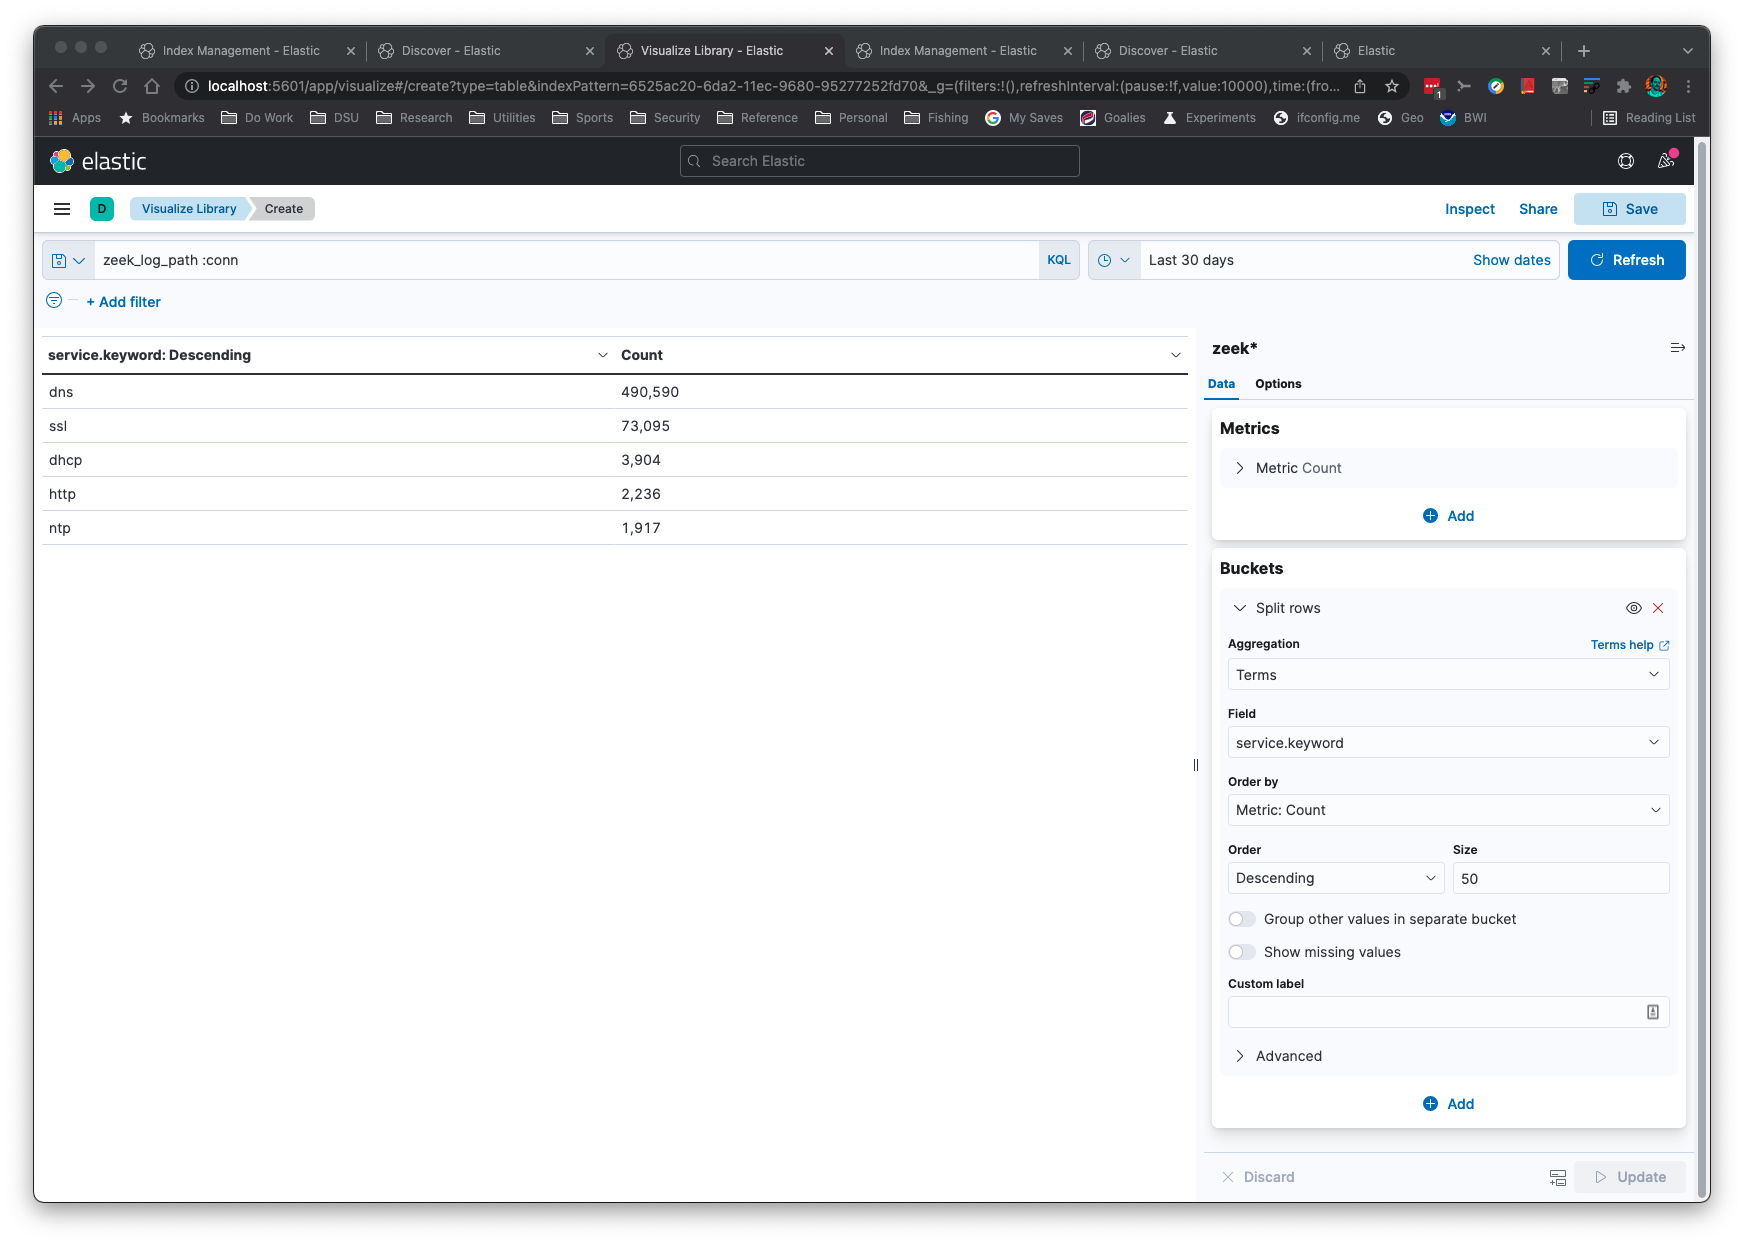
A Python application to filter and transfer Zeek logs to Elastic/OpenSearch+Humio. This app can also output pure JSON logs to stdout for further…
log-analysisnetwork-securityscripting-automation+1
404 years ago
sysmon-parser preview

sysmon-parser

GitHubolafhartong/sysmon-parser

Automatically generated Sysmon parser for Azure Sentinel
cloud-securitydefensive-toolslog-analysis+1
188 months ago
reactor preview

reactor

GitHubnccgroup/reactor

Runs custom filters on Elasticsearch and alerts on matches
anomaly-detectiondefensive-toolsincident-response+2
33 years ago
printnightmare-detection-lab preview

printnightmare-detection-lab

GitHubjoertx07/printnightmare-detection-lab

Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
adversarial-attackeducationexploitation+6
1 month ago
sigmalite preview

sigmalite

GitHubrunreveal/sigmalite

Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
code-analysisintrusion-detectionlog-analysis+2
591 year ago
Log4Pot preview

Log4Pot

GitHubthomaspatzke/log4pot

A honeypot for the Log4Shell vulnerability (CVE-2021-44228).

intrusion-detectionlog-analysispayload-generation+2
941 year ago
My-Sigma-Rule-Collection preview

My-Sigma-Rule-Collection

GitHub17patmaks/my-sigma-rule-collection

Sigma Rule for CVE-2025-49666

curated-resourceseducationintrusion-detection+3
6 months ago
Previous12Next
