ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…

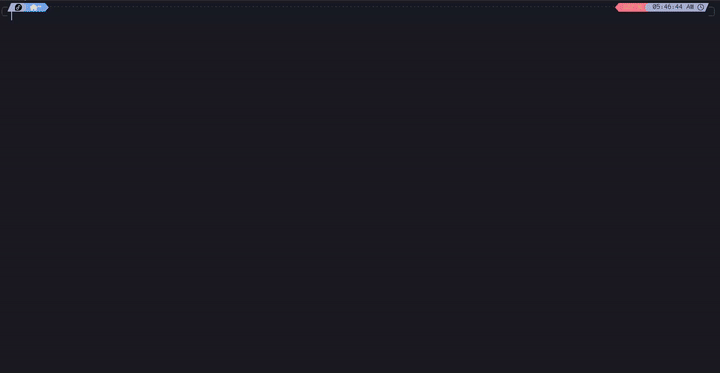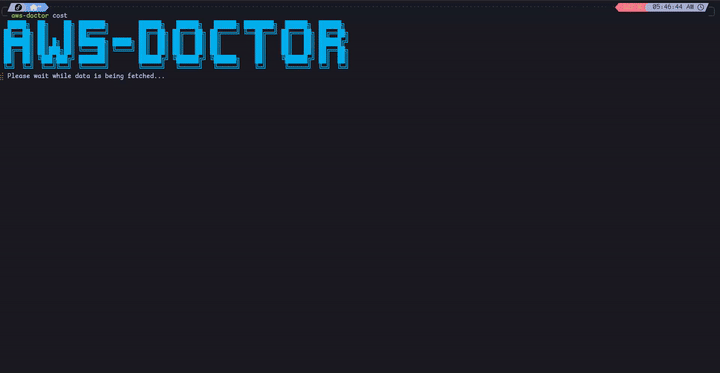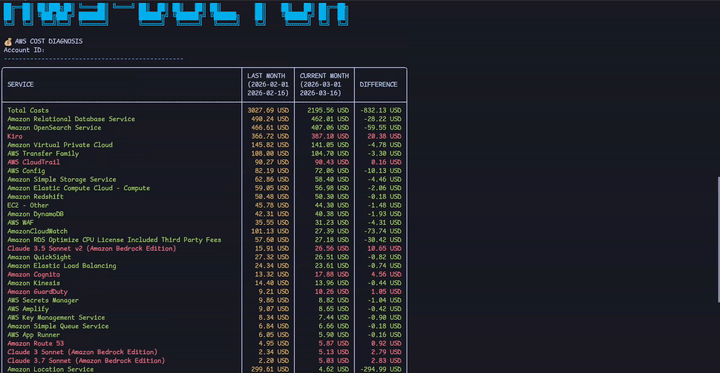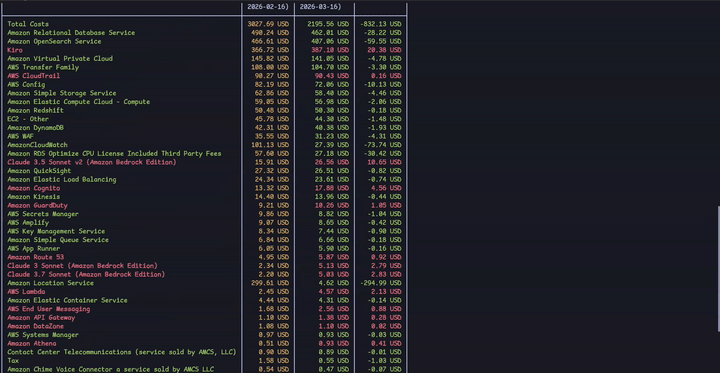
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️

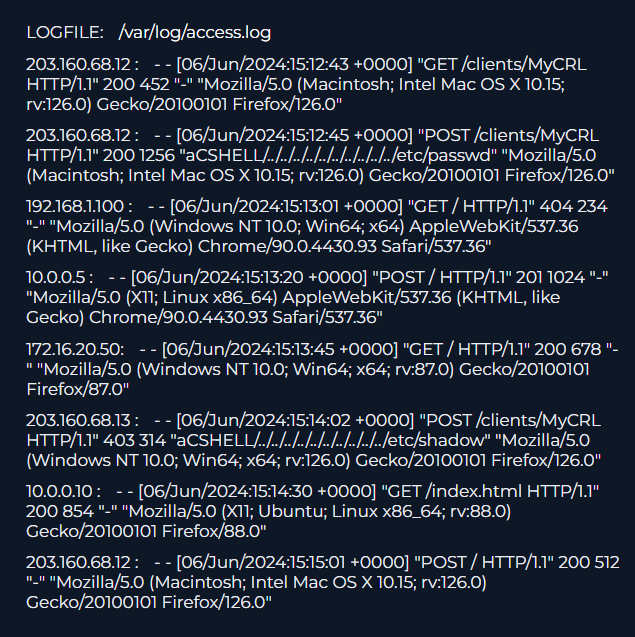
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…

Powershell Based tool for gathering information related to O365 intrusions and potential Breaches


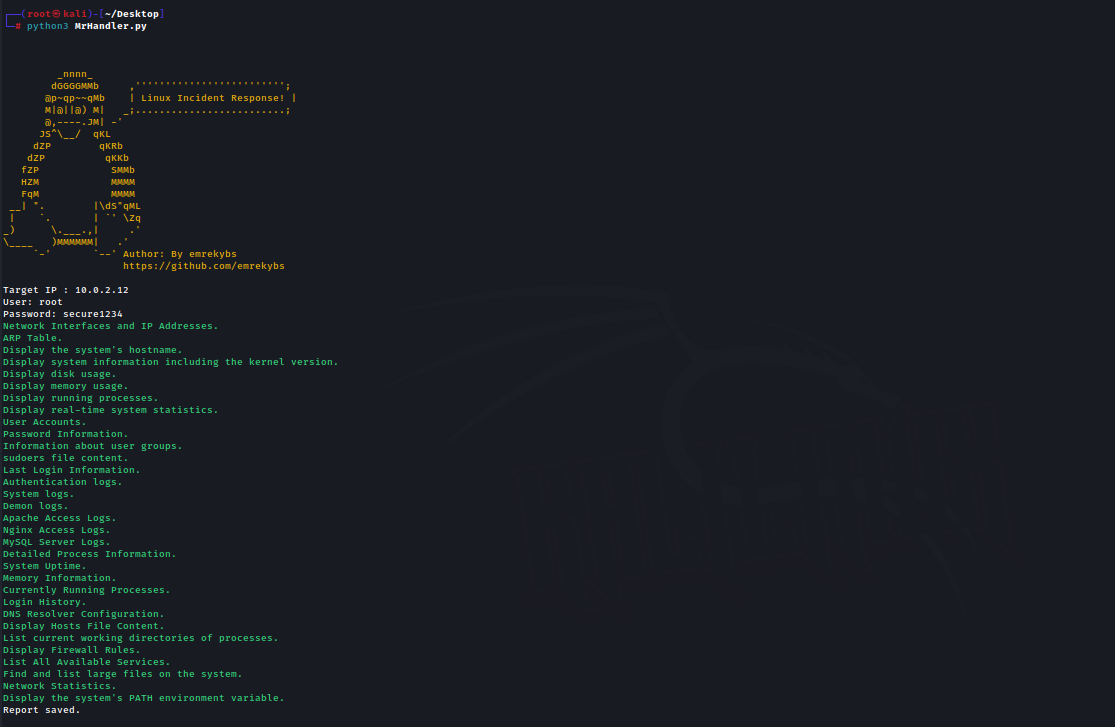
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…

Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…

This project aims to compare and evaluate the telemetry of various EDR products.

Cyber Threat Defense World Modeling

Dockerized honeypot for CVE-2021-44228.

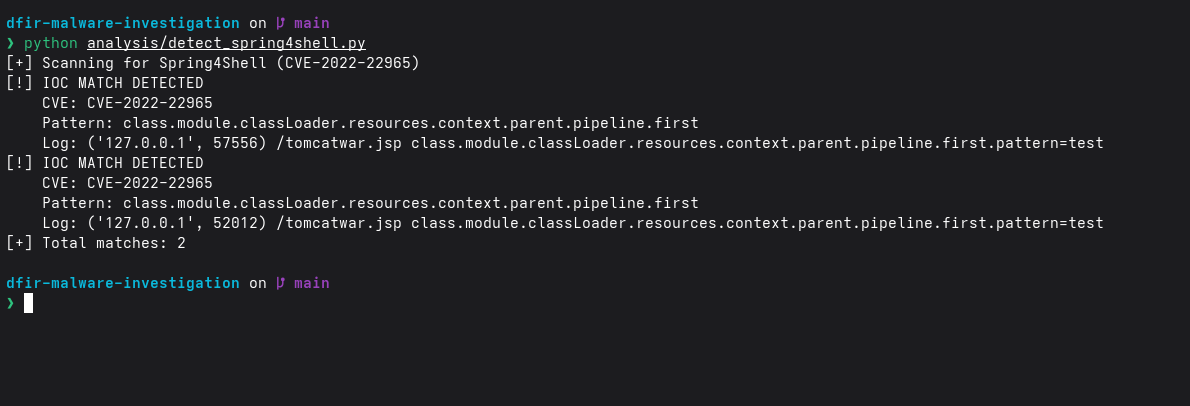
Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.

A comprehensive ETW (Event Tracing for Windows) event generation tool designed for testing and research purposes.

A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…

PHP 8.4+ security library (mirror)

A comprehensive Security Operations Centre (SOC) incident response simulation demonstrating threat detection, triage, analysis, and mitigation of the…