

ModSecurity
 owasp-modsecurity/modsecurity
ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
anti-botapi-securitydefensive-tools+7
9.8k
owasp-modsecurity/modsecurityModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 corelight/log-add-http-post-bodies
Add POST body excerpt to Bro's HTTP log
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 elshaheedy/cve-2025-29927-sigma-rule
Sigma rule for detecting CVE-2025-29927 exploitation via suspicious x-middleware-subrequest HTTP headers in Next.js applications, with detection…
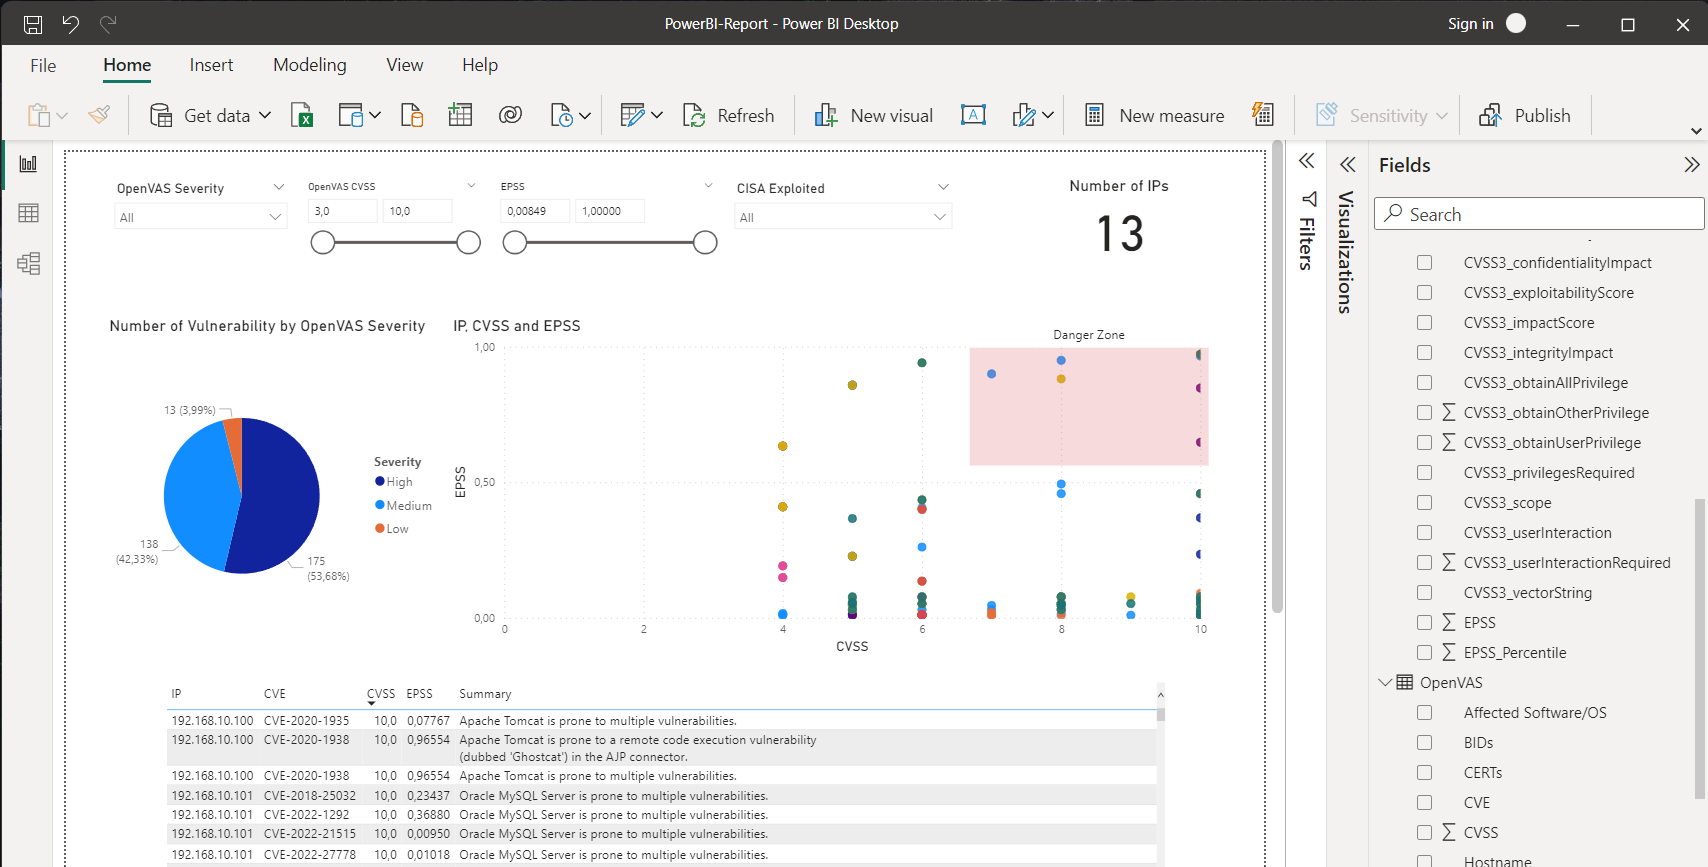 trinitor/cve-vulnerability-information-downloader
Downloads and aggregates CVSS, EPSS, and CISA known exploited vulnerability data into unified JSON/CSV files and a SQLite database. Enriches…
 ossie-git/log4shell_sentinel
A Smart Log4Shell/Log4j/CVE-2021-44228 Scanner
 joakimbulow/cve-2026-1337
CVE-2026-1337 - Neo4j - Log Injection
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 garethmsheldon/cve-2026-22557-unifi-detection
Detection content for CVE-2026-22557 — UniFi Network Application unauthenticated path traversal (CVSS 10.0). Includes YARA, Sigma, KQL, Splunk SPL,…
 airbus-cert/cve-2024-4040
Scanner for CVE-2024-4040
 alexpena5635/cve-2021-44228_scanner-main-modified-
Scans jar, war, and ear files for the presence of JndiLookup.class to detect applications vulnerable to CVE-2021-44228 (Log4Shell).
 ostesayed/oste-web-log-analyzer
OSTE WLA automate the process of analyzing web server logs with the Python Web Log Analyzer.
 chrisandoryan/nethive-project
Restructured and Collaborated SIEM and CVSS Infrastructure. Presented at Blackhat Asia Arsenal 2020.
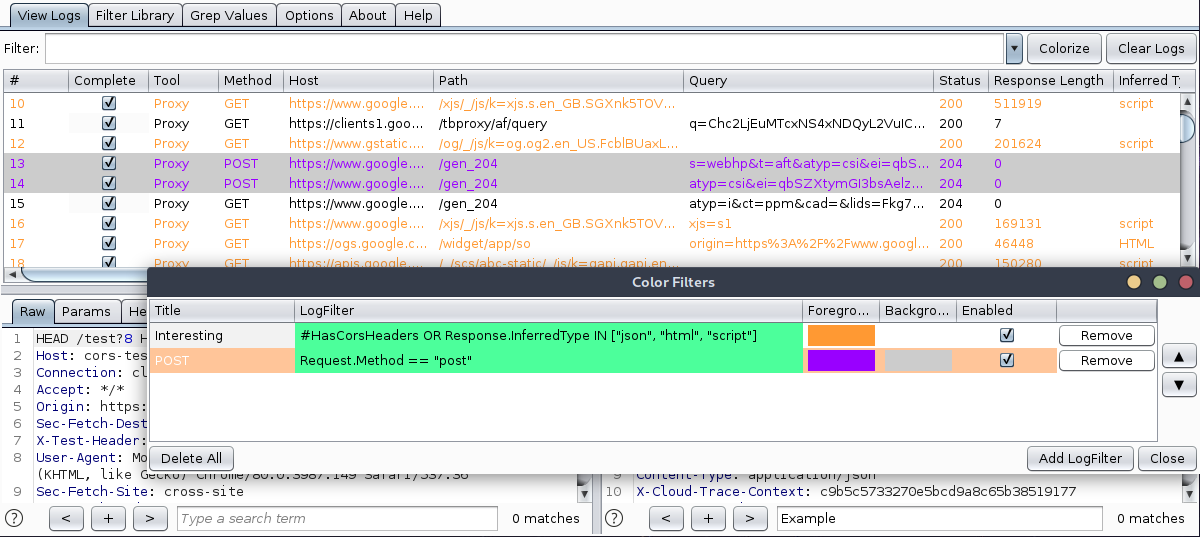 nccgroup/loggerplusplus
Advanced Burp Suite Logging Extension
 maikelnight/zerologon
Check for events that indicate non compatible devices -> CVE-2020-1472