
DeepBlueCLI
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
digital-forensicsincident-responseintrusion-detection+2
sans-blue-team/deepbluecliPowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
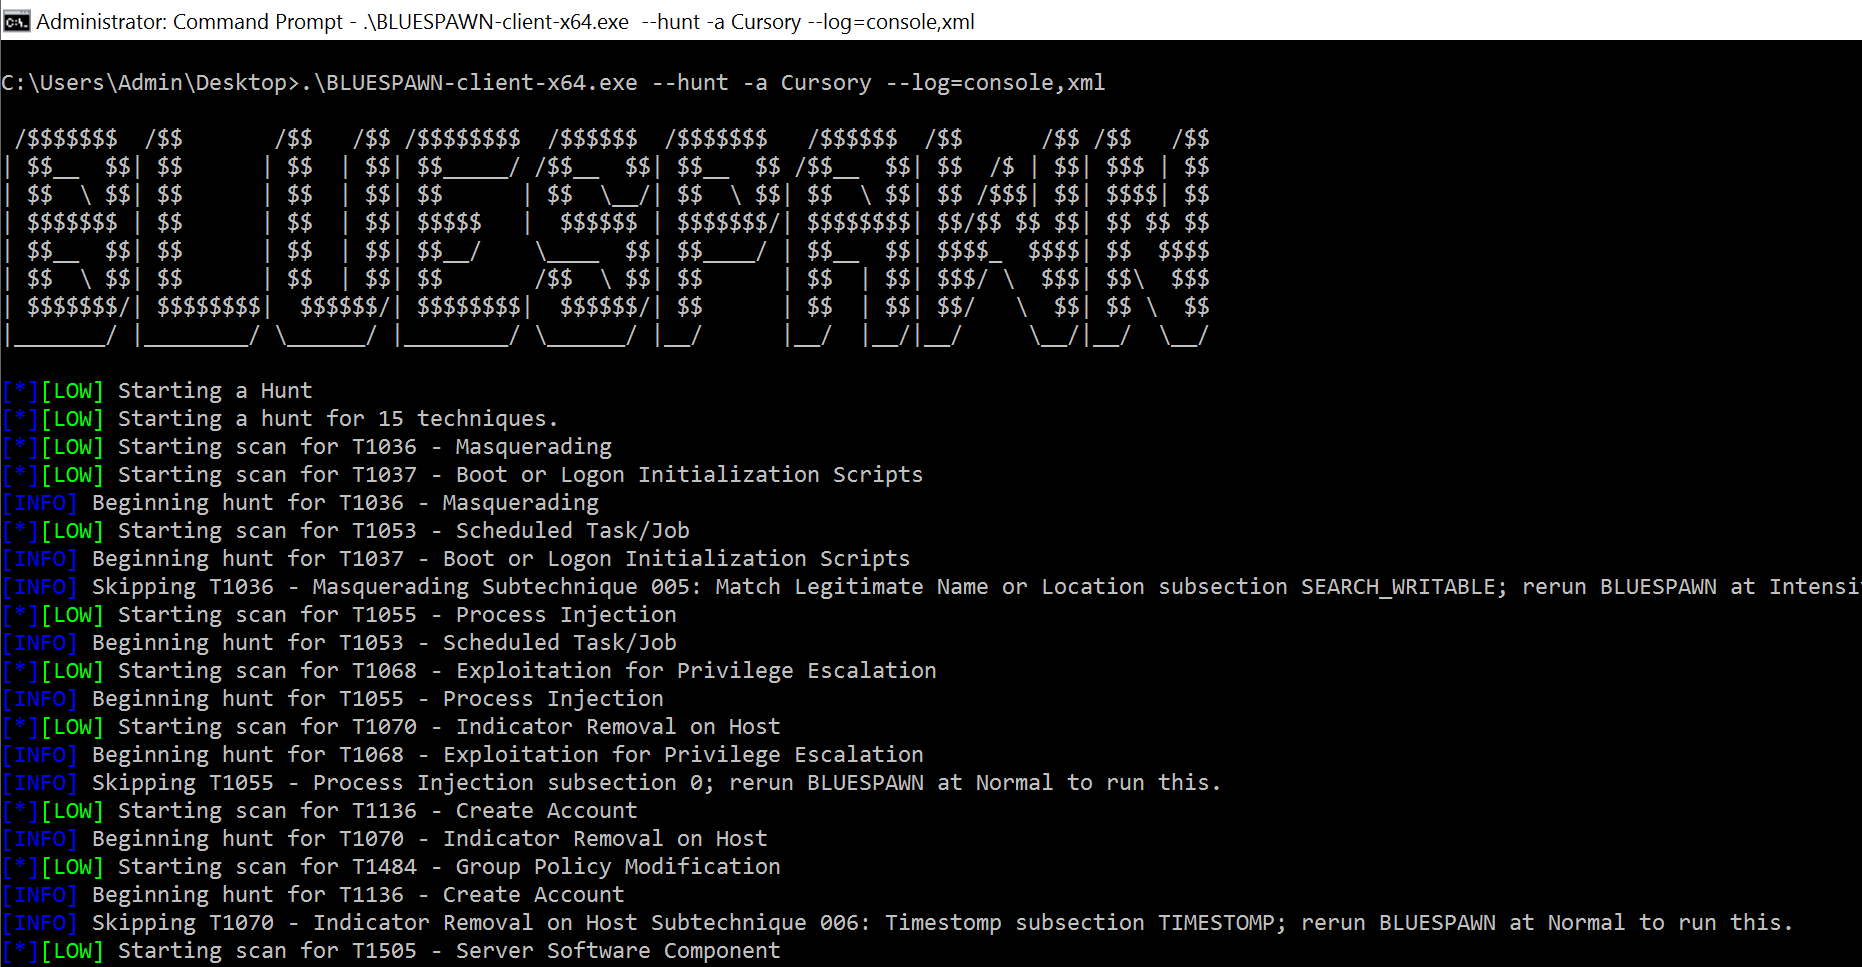 ion28/bluespawn
An Active Defense and EDR software to empower Blue Teams
 emrekybs/nginxhunter
Analyzes Nginx access logs to detect SQL injection, scanner tools, webshells, and exploitation attempts, aiding system administrators in server…
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
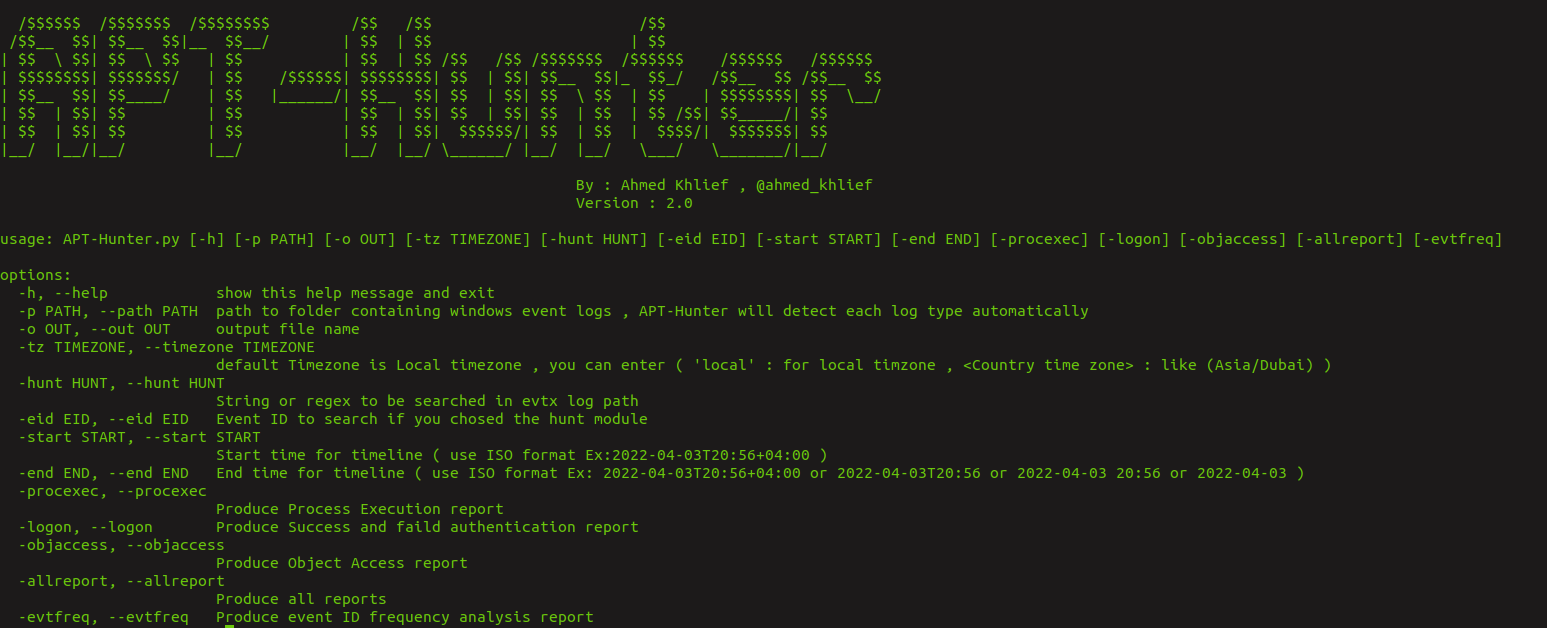 ahmedkhlief/apt-hunter
APT-Hunter is Threat Hunting tool for windows event logs which made by purple team mindset to provide detect APT movements hidden in the sea of…