

TryHackMe-Roadmap
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
ctfcurated-resourceseducation+8
604
hunterdii/tryhackme-roadmapHello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 netlas-io/netlas-cookbook
The goal of this guide is very simple - to teach anyone interested in cyber security, regardless of their knowledge level, how to make the most of…
 r-s0n/ars0n-framework
Modular bug bounty hunting framework automating reconnaissance, subdomain enumeration, and vulnerability scanning with an educational focus to help…
 parasimpaticki/awesome-appsec-interview
A curated list of resources, practice questions, and study materials to help you prepare for Application Security (AppSec) interviews
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 sifatnotes/-recon-mysql-ssh-ica-cve-2026-13247-tomcat
Hands-on cybersecurity and CTF labs covering service fingerprinting, MySQL enumeration, HTTP clues, SSH discovery, port probing, host discovery, ICA…
 hslatman/awesome-threat-intelligence
Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)

 zishanadthandar/pentest
Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 dev-angelist/ejptv2-notes
eLearnSecurity Junior Penetration Tester (eJPT) v2 Notes
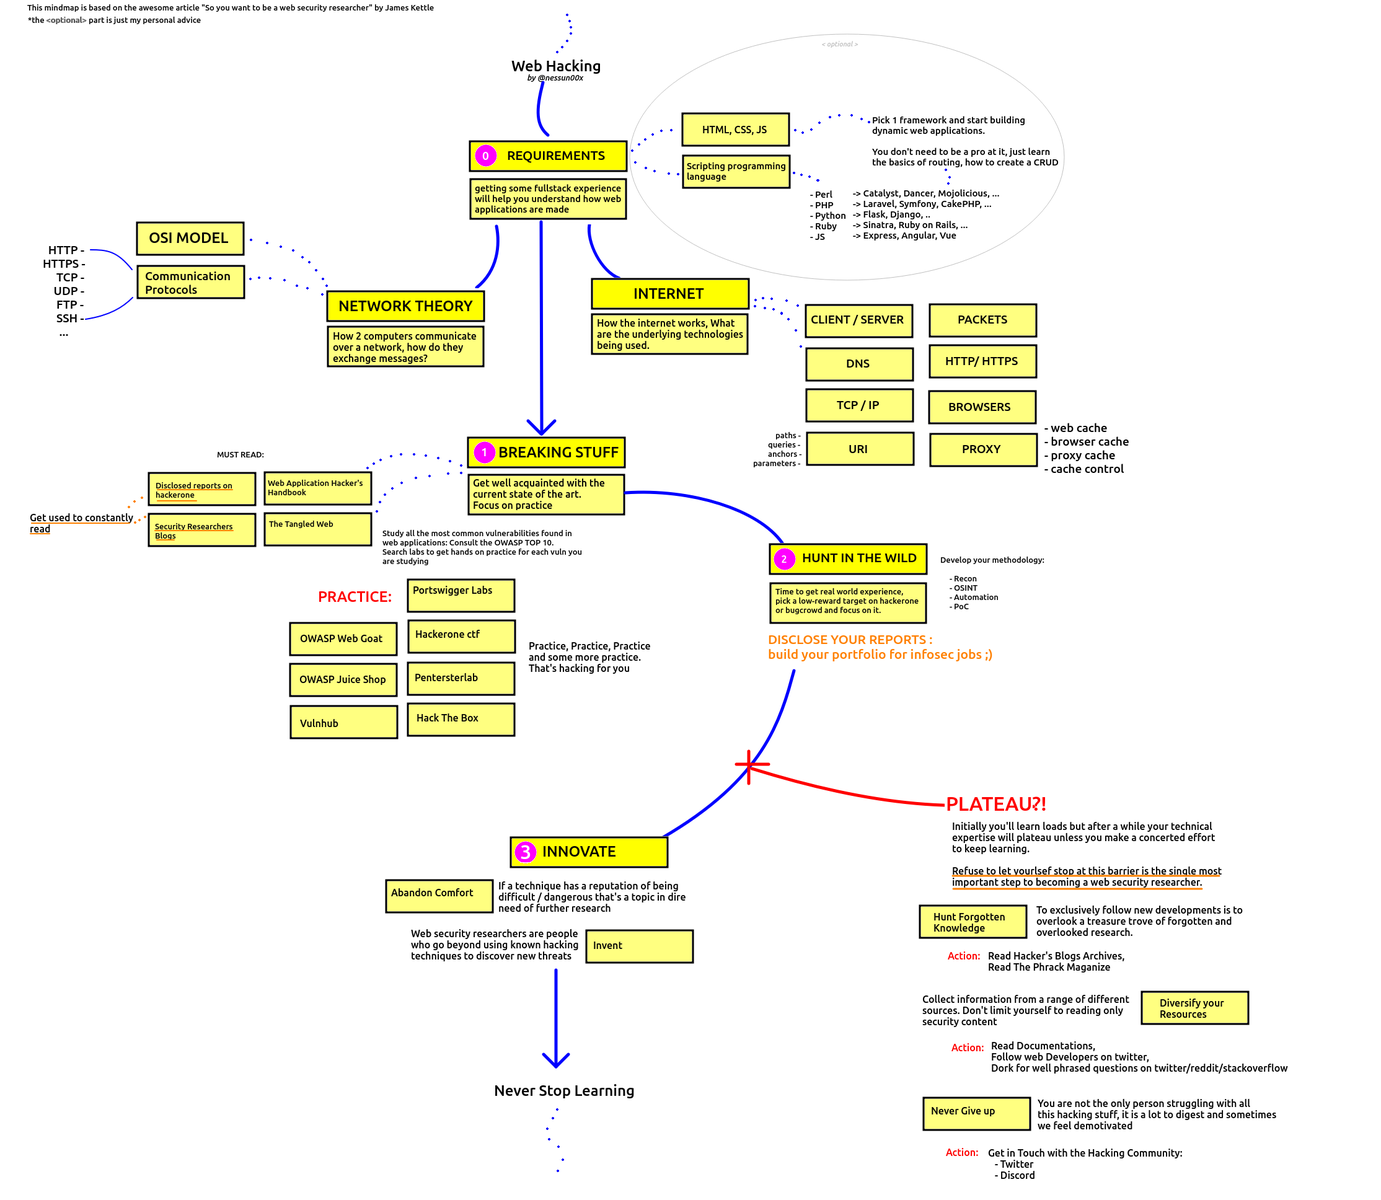 domssilva/vulnsearch
A deep look at some recon methodologies and web-application vulnerabilities of my interest where I will merge all my notes gathered from books,…