Massive-Web-Application-Penetration-Testing-Bug-Bounty-Notes

A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…

A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…

Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…

A collection of awesome penetration testing resources and tools

Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…

Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…

Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10

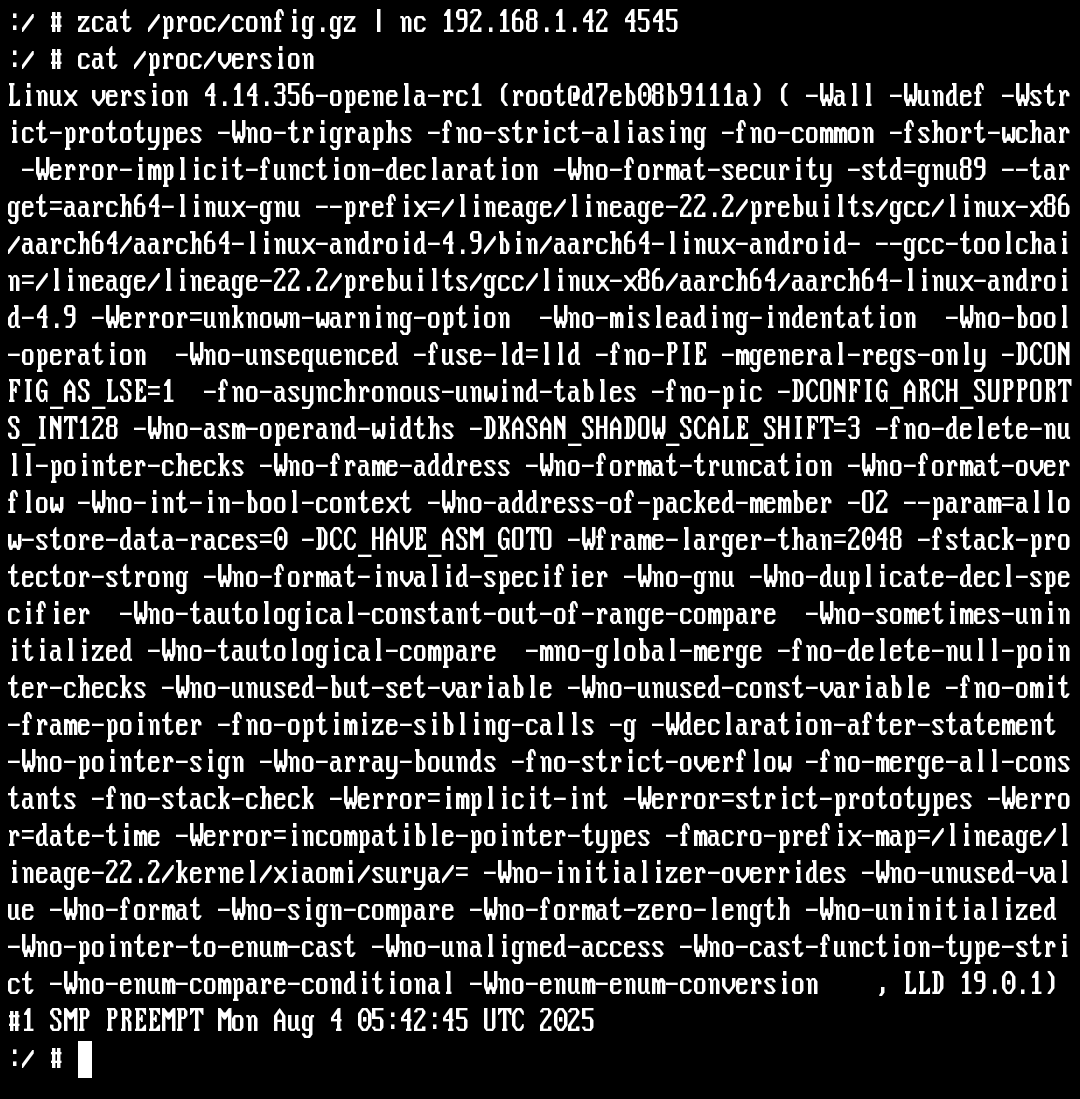
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.

*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…

OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…

Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…

😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.

Lab materials and practice resources for OSCP certification preparation, including penetration testing exercises and hands-on security training…

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code

Official Elastic Skills