
 elastic/agent-skills
Official Elastic Skills
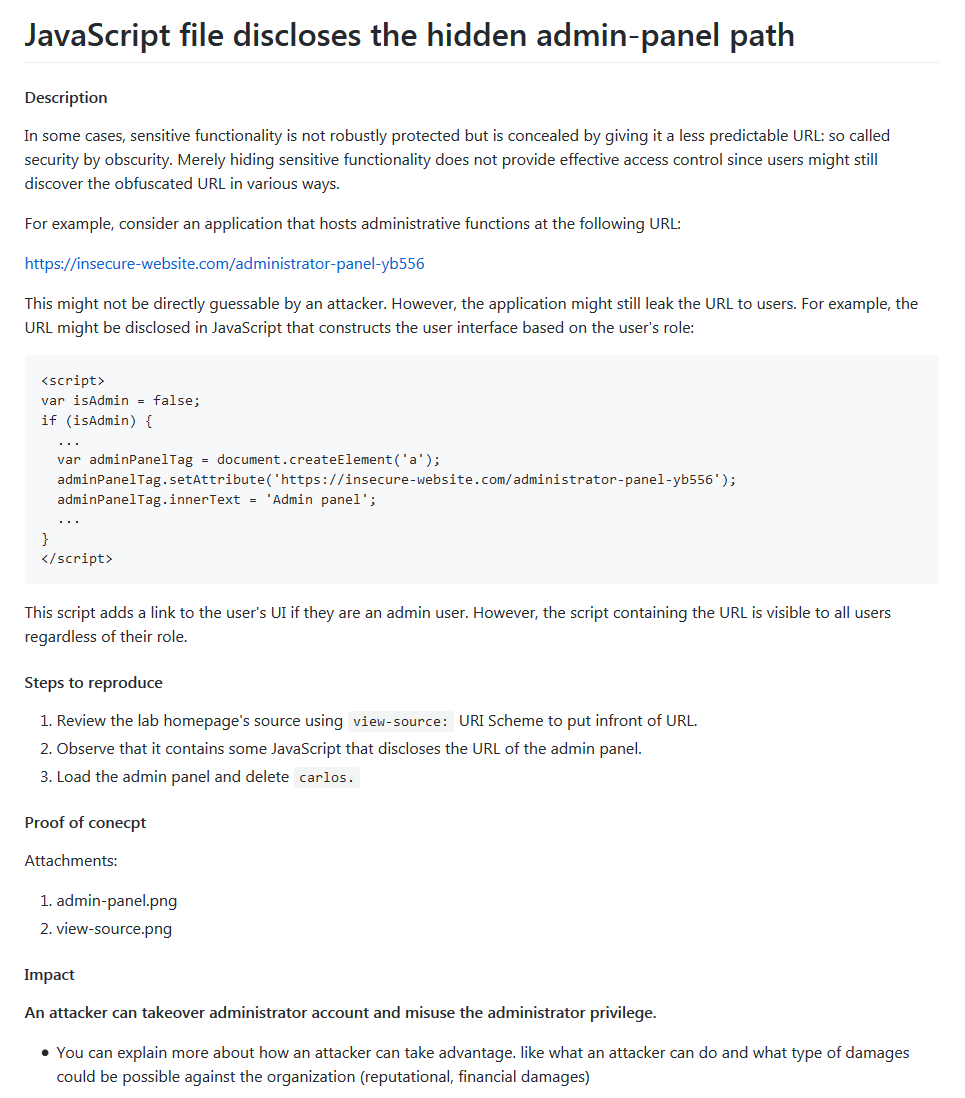 bittentech/bug-bounty-beginner-roadmap
This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 tandasat/tandasat.github.io
Remote hypervisor development class for security researchers; covers virtualization internals, hypervisor security, and vulnerabilities in privileged…
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
 bunbuncodes/cpsc253_cybersecurityfinalprojectreports
Report written on CVE-2024-38112
 owasp/wafec
Structured evaluation criteria framework for assessing Web Application Firewalls (WAFs), enabling users, vendors, and third parties to compare…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
 owasp/osib
Centralized YAML-based knowledge base linking MITRE CWE, OWASP Top10, ASVS, and other security standards with versioned references. Includes MkDocs…
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 owasp/pwnzzai
Hands-on AI security learning platform with intentionally vulnerable LLM applications. Explore OWASP Top 10 for LLMs through interactive pizza shop…
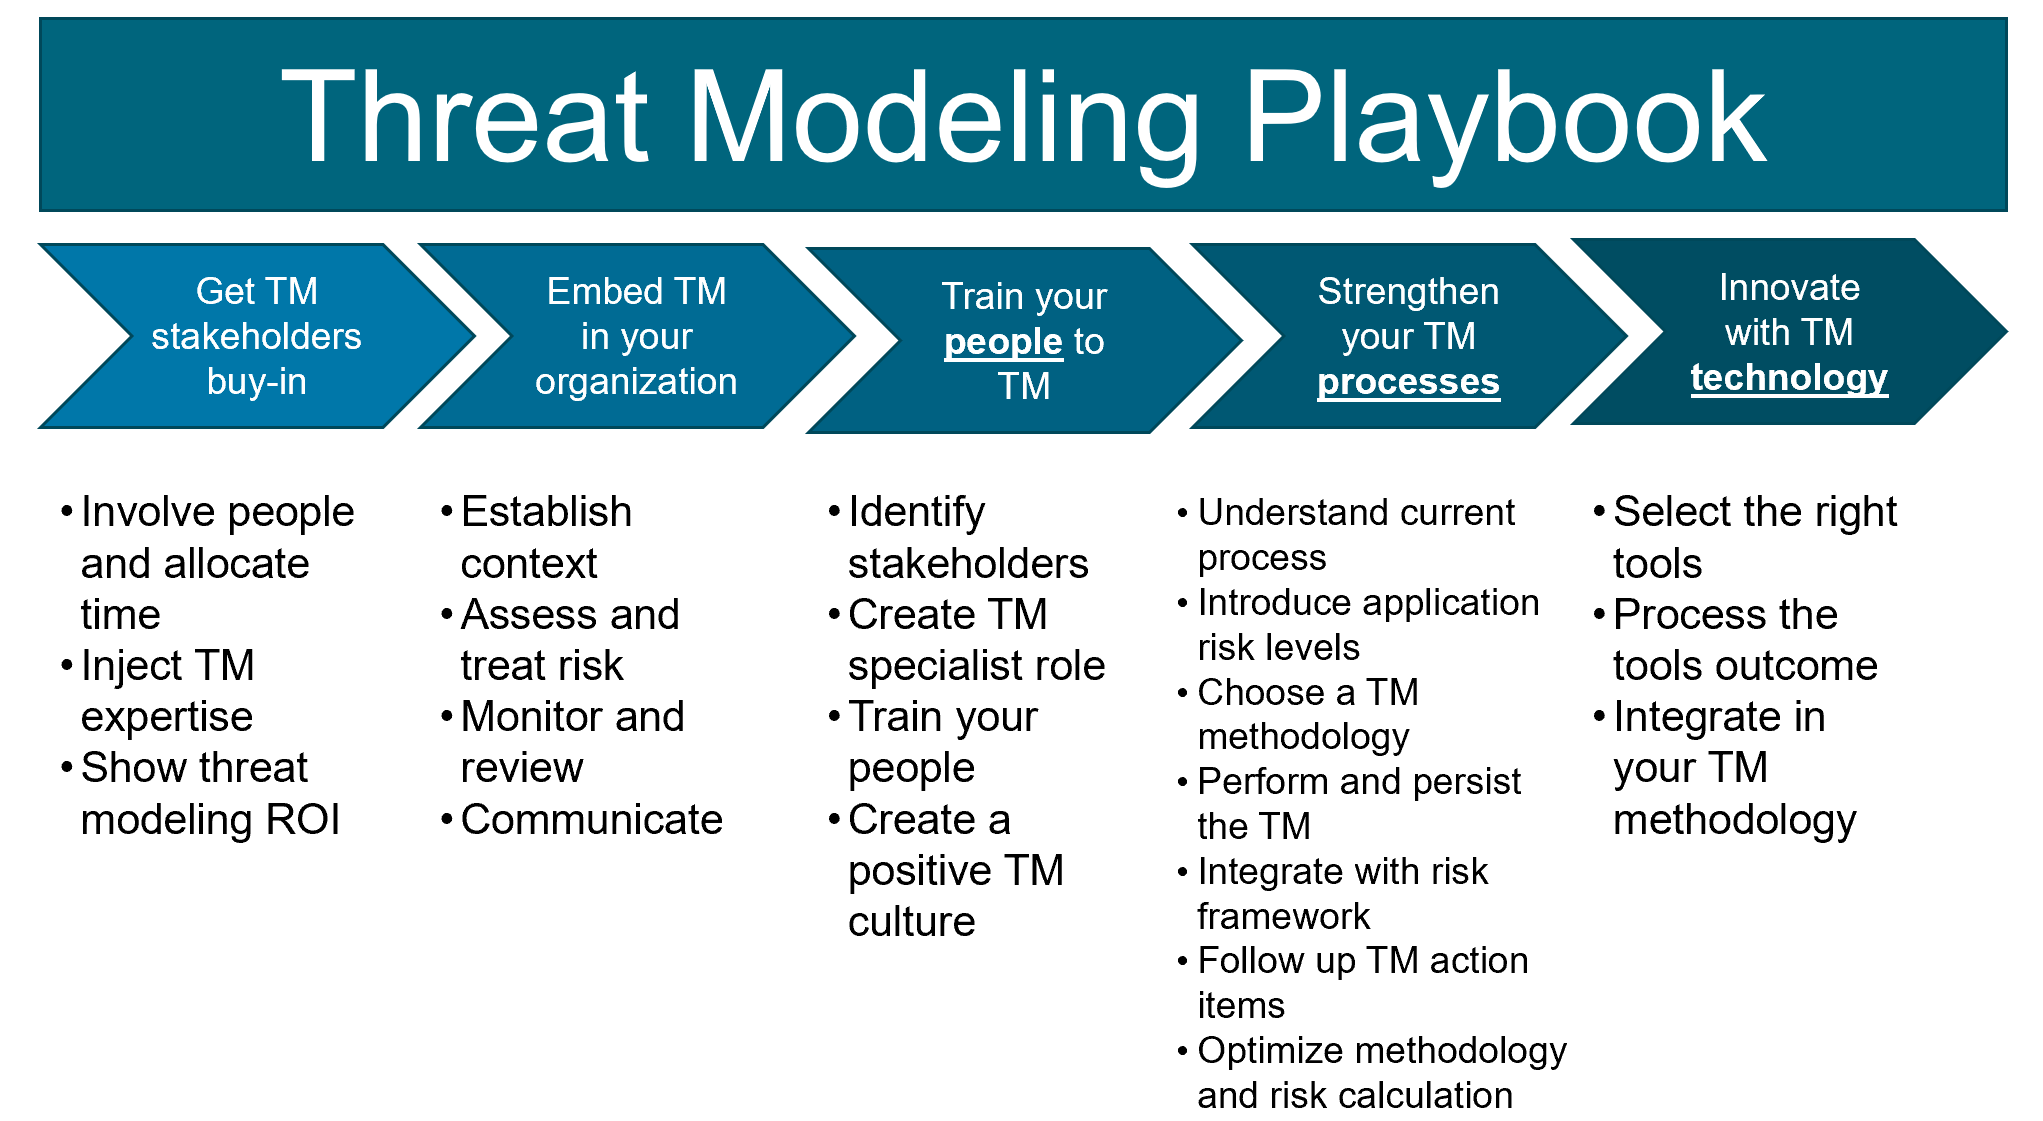 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 nahamsec/resources-for-beginner-bug-bounty-hunters
A list of resources for those interested in getting started in bug bounties
 syslifters/offsec-reporting
Offensive Security OSCP+, OSEP, OSWP, OSWA, OSWE, OSED, OSMR, OSEE, OSDA, OSIR, OSTH Exam and Lab Reporting / Note-Taking Tool