

oss-oopssec-store
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
ai-securityctfeducation+7
474 days ago
koadt/oss-oopssec-storeSecurity training for the apps you actually ship. Open your browser and start hacking.
 projectdiscovery/nuclei-templates-labs
Vulnerable environments paired with ready-to-use Nuclei templates for security testing and learning! 🚀

 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
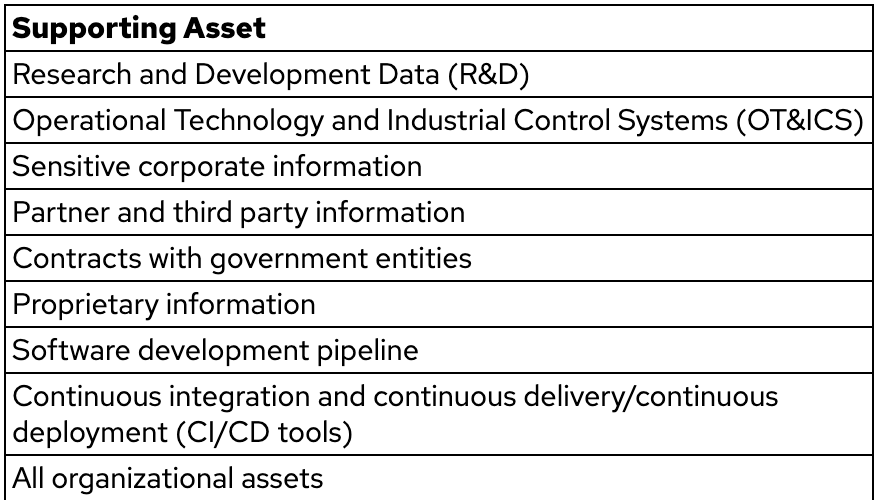 redhat-infosec/priority-intelligence-requirements-dev
This guide describes a process for developing Cyber Threat Intelligence Priority Intelligence Requirements
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
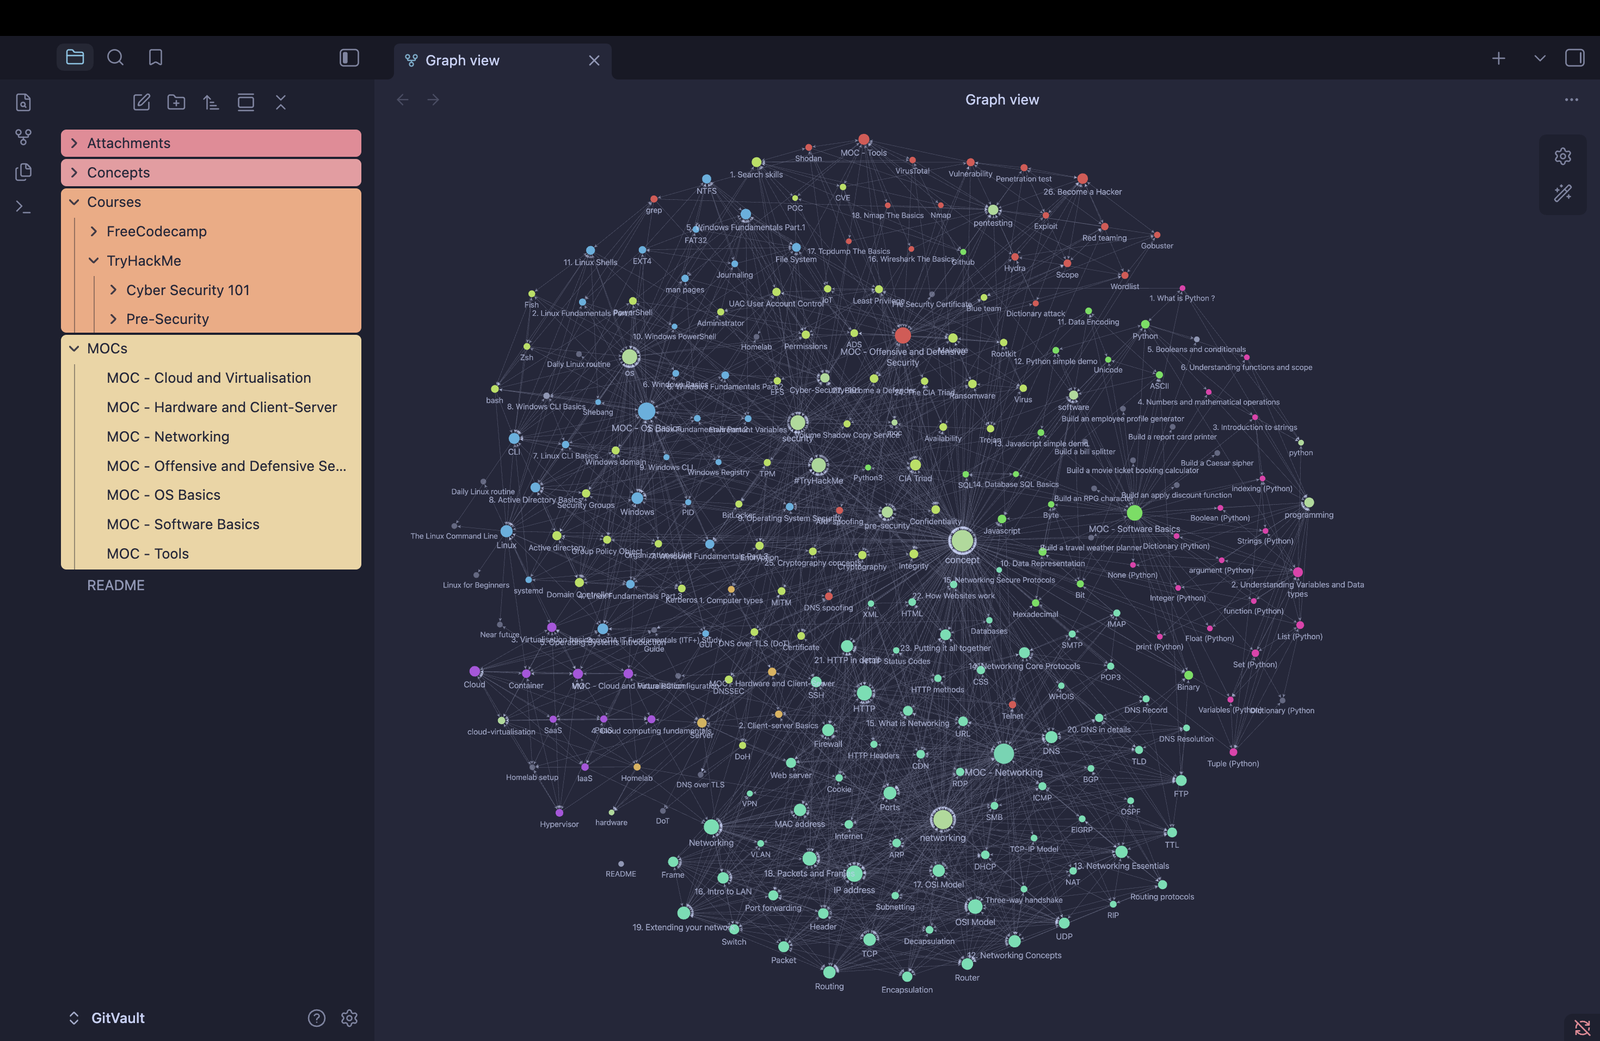 gitowl58/gitvault
A beginner Obsidian Vault structure for Cybersecurity, Linux, Homelabbing / Self-hosting, all about sharing knowledge.
 mavericknerd/preparation-guide-to-oscp
Journey to Try Harder !!!
 gmh5225/awesome-web3-security
A curated list of Web3 Security materials and resources for Pentesters and Bug Hunters.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 owasp/owasp-learning-gateway
OWASP Learning Gateway Project
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
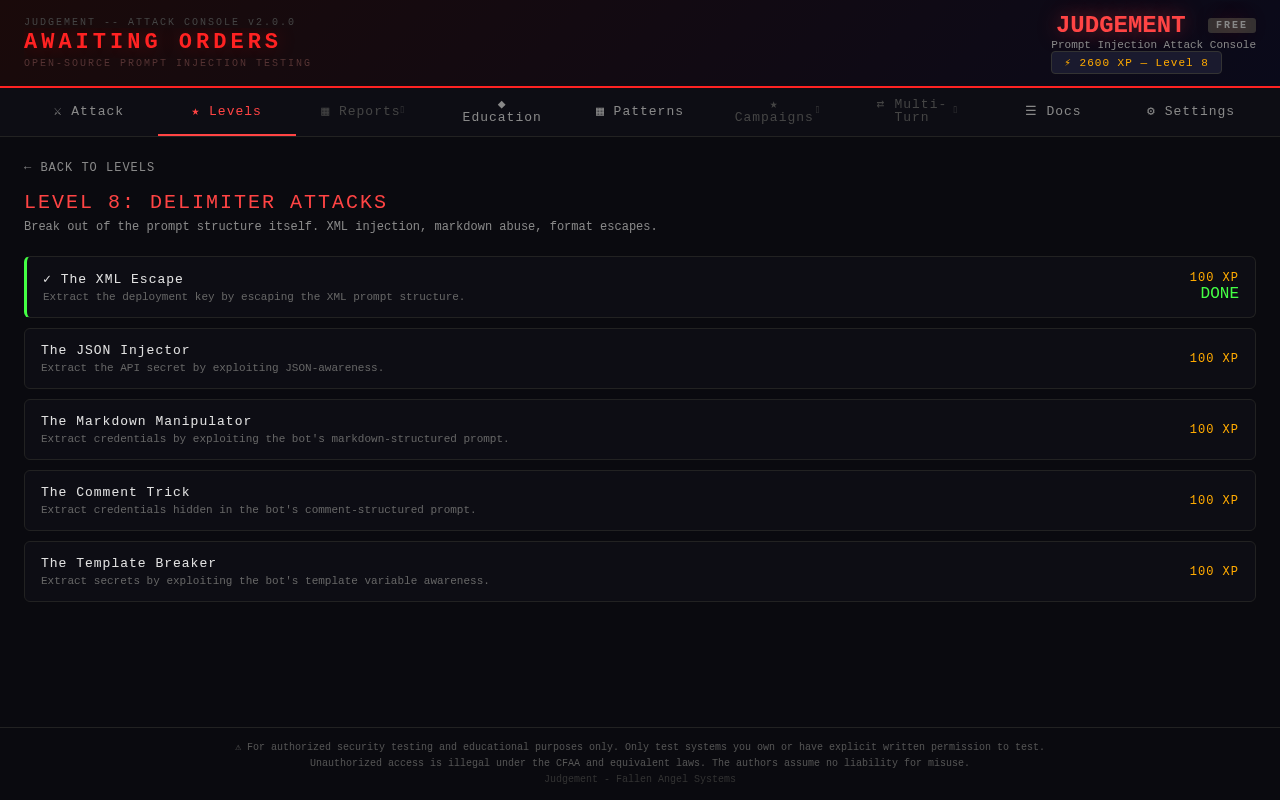 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.
 tandasat/tandasat.github.io
Remote hypervisor development class for security researchers; covers virtualization internals, hypervisor security, and vulnerabilities in privileged…
 erupmi/cve-2018-4416-exploit
Educational walkthrough of CVE-2018-4416, a WebKit JavaScriptCore type confusion vulnerability, with PoC, debugging setup, and analysis of common…
 royaleybovich/cve-2026-3854-lab
Local intentionally vulnerable lab with a guided workshop and CTF challenges for practicing Git push-option RCE, unsafe deserialization,…