
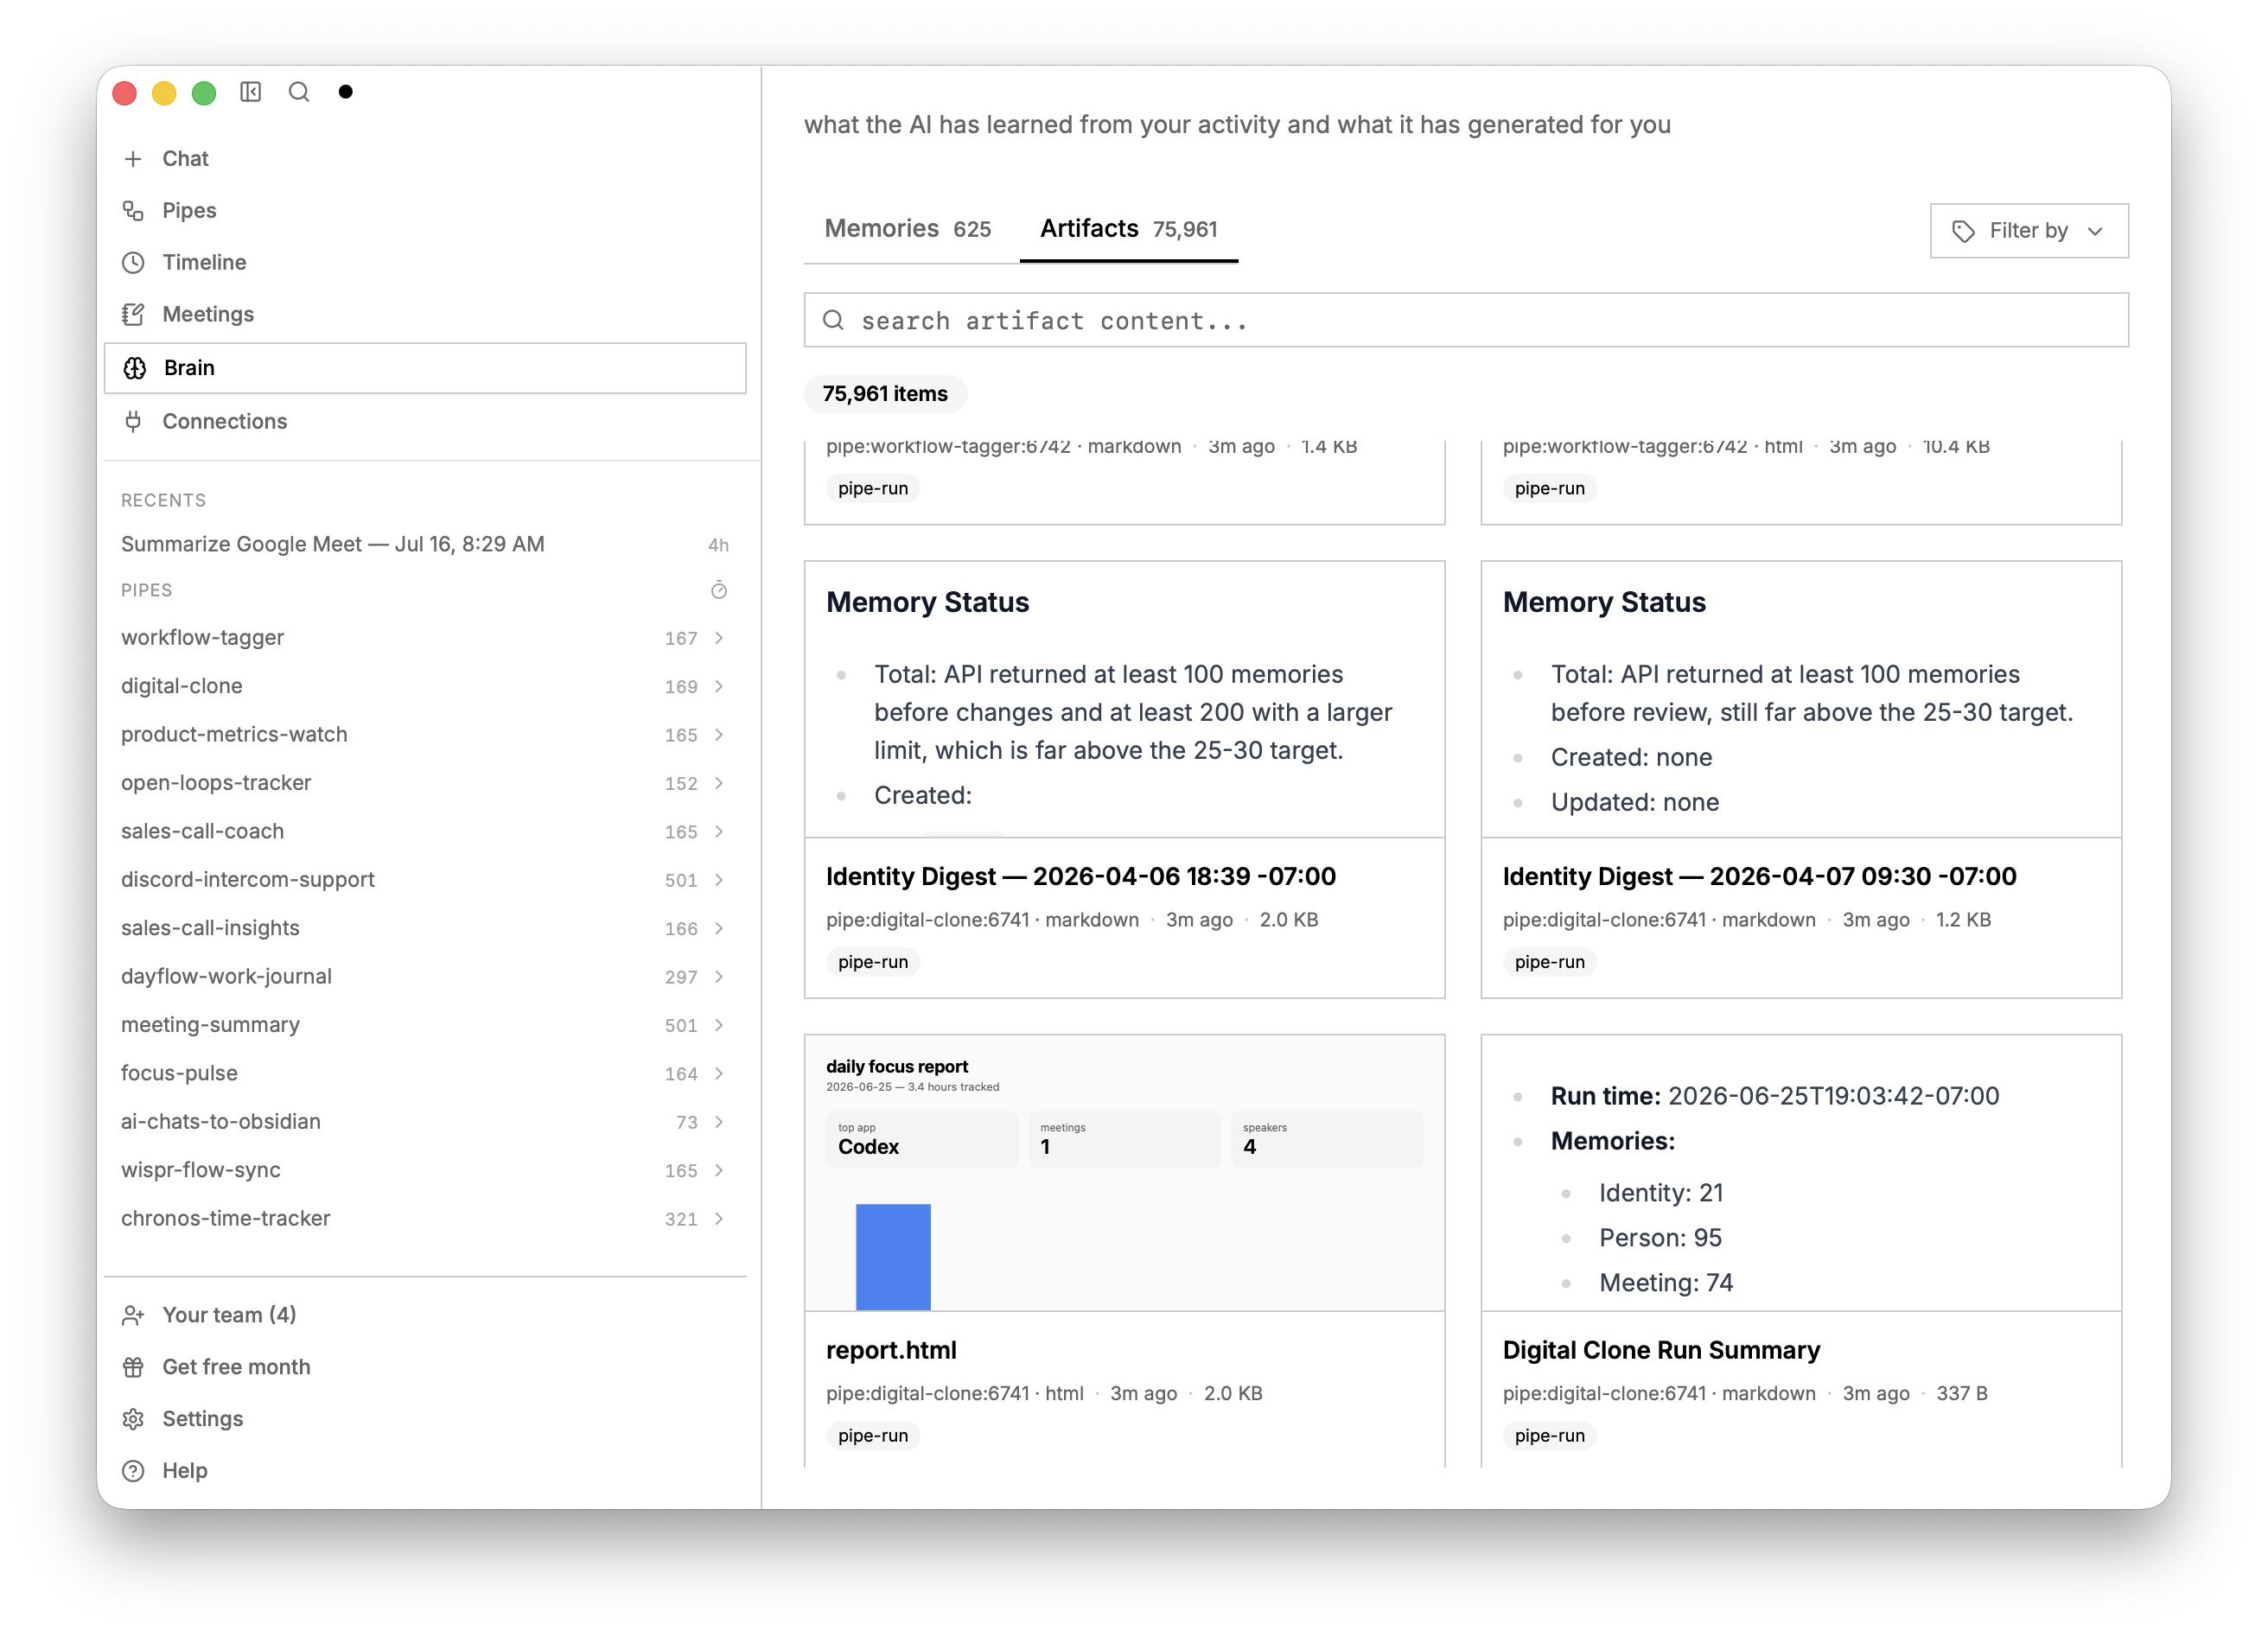
screenpipe
 screenpipe/screenpipe
YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
ctfcurated-resourceseducation+8
screenpipe/screenpipeYC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
 sbilly/awesome-security
A collection of awesome software, libraries, documents, books, resources and cools stuffs about security.
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 carterperez-dev/cybersecurity-projects
Building 70 Projects ranging from beginner to advanced so anyone can — learn from, build upon, use as a reference, or even copy directly. Owned by my…
 rshipp/awesome-malware-analysis
Defund the Police.
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 jassics/security-study-plan
Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
 microsoft/security-101
8 Lessons, Kick-start Your Cybersecurity Learning.
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 secfigo/awesome-fuzzing
A curated list of fuzzing resources ( Books, courses - free and paid, videos, tools, tutorials and vulnerable applications to practice on ) for…
 0x4d31/awesome-threat-detection
Curated list of threat detection and hunting resources: detection rules, SIEM and log analysis tools, endpoint/network monitoring, datasets,…
 bst04/cybersources
A curated list of cybersecurity tools and resources.

 joe-shenouda/awesome-cyber-skills
A curated list of hacking environments where you can train your cyber skills legally and safely
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.