

Android-Security-Masterclass
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
android-securitycryptographyeducation+6
3
owasp/android-security-masterclassOWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
 six2dez/wahh_extras
The Web Application Hacker's Handbook - Extra Content
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 kathanp19/howtohunt
Collection of methodology and test case for various web vulnerabilities.
 hacker0x01/hacker101
Source code for Hacker101.com - a free online web and mobile security class.
 gracenolan/notes
Curated study notes and interview preparation guide for security engineering roles, covering networking, web security, cryptography, malware…
 owasp/nodegoat
The OWASP NodeGoat project provides an environment to learn how OWASP Top 10 security risks apply to web applications developed using Node.js and how…
 xalgord/massive-web-application-penetration-testing-bug-bounty-notes
A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…
 mohshomis/modo
Curated collection of cybersecurity learning resources, CTF writeups, research papers, and practical labs for hands-on skill development across web…
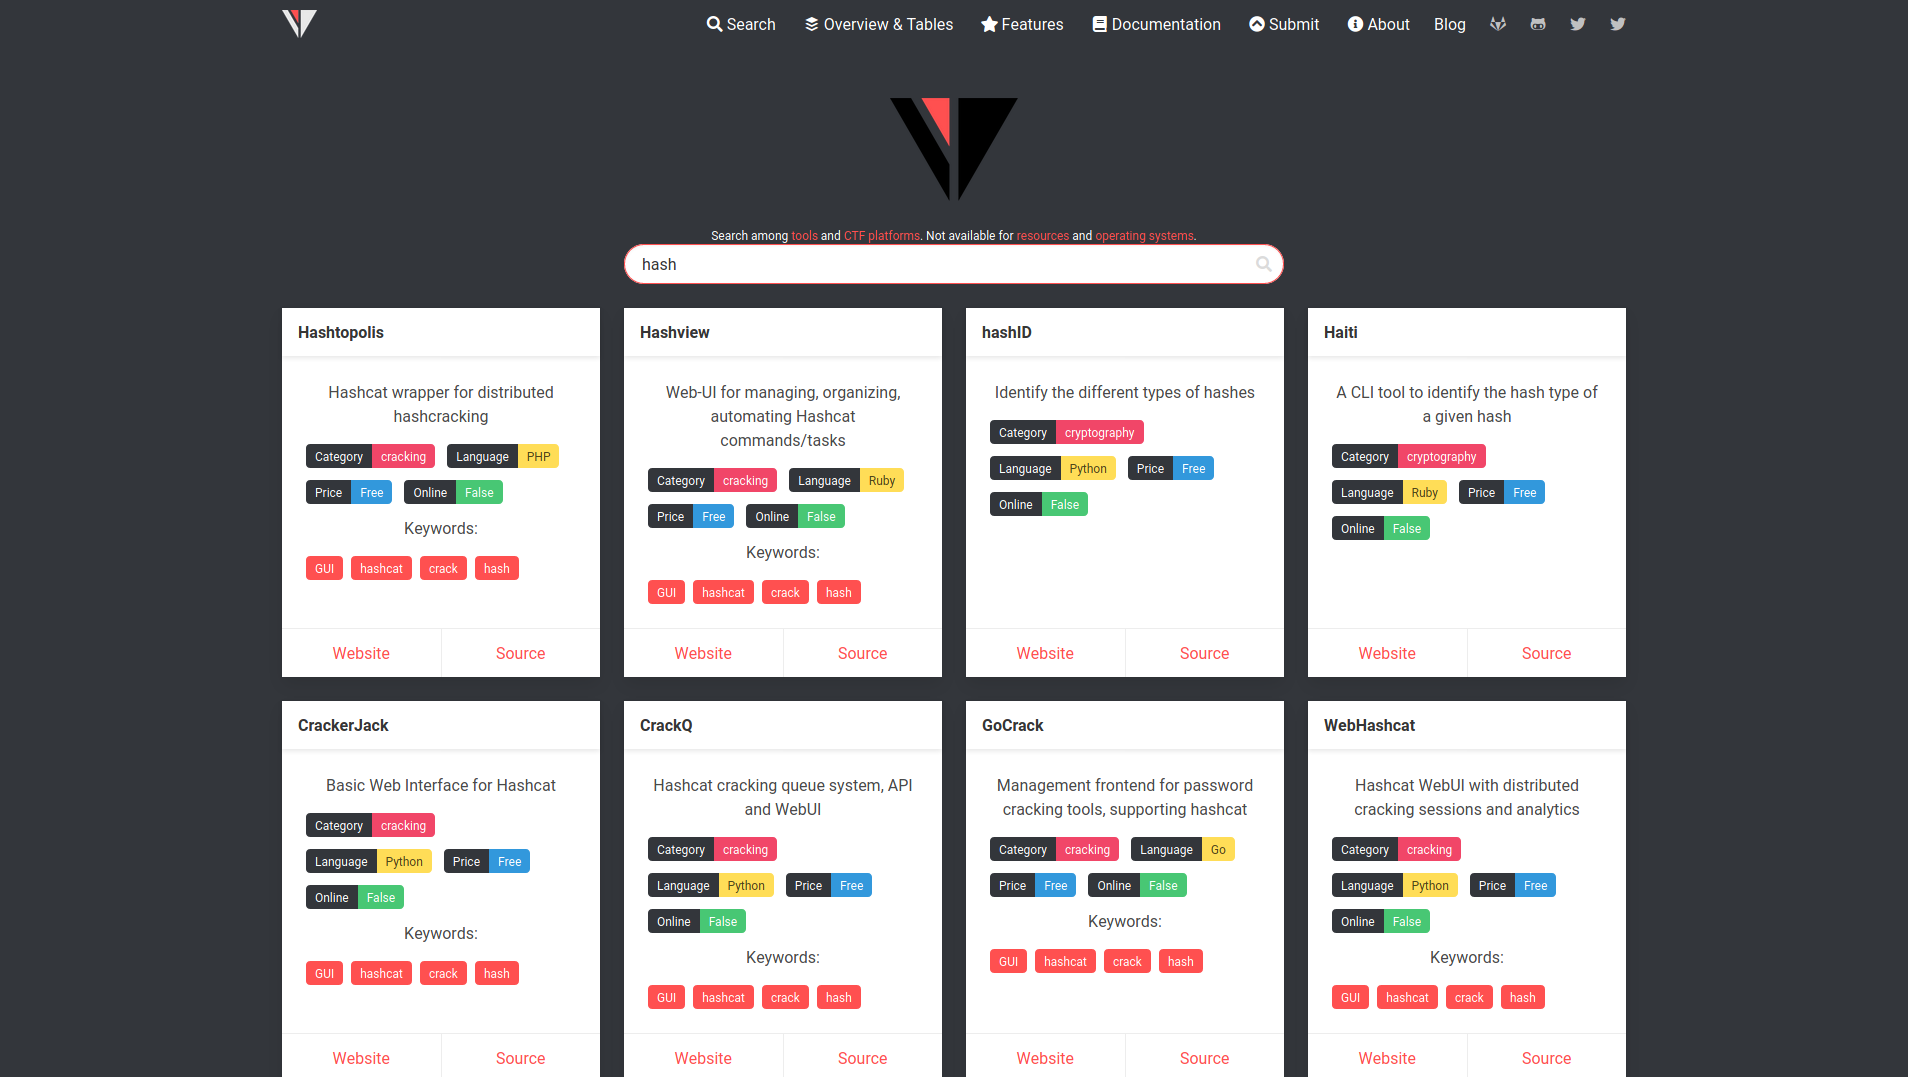
 rawsec/rawsec-cybersecurity-list
Curated inventory of cybersecurity tools and resources covering penetration testing, forensics, OSINT, web security, malware analysis, cryptography,…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 excalibra/cybersecurity-interview-questions
Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 nu11secur1ty/python
Curated collection of Python scripts and tutorials for penetration testing, web security, and exploitation techniques, designed for security…
 owasp/wafec
Structured evaluation criteria framework for assessing Web Application Firewalls (WAFs), enabling users, vendors, and third parties to compare…