awesome-threat-intelligence

Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…

Curated directory of threat intelligence sources, feeds, frameworks, tools, and research for SOC/CTI teams—covering IOCs, STIX/TAXII formats, and…

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Curated bug-bounty methodology library with runbooks, recon/fuzz playbooks, checklists, and CLI helpers for target scoping, cert enumeration, and…

Course repository for PowerShell for Pentesters Course

This is a resource factory for anyone looking forward to starting bug hunting and would require guidance as a beginner.

SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…

Red Team Guides

These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…

Windows Local Privilege Escalation Cookbook


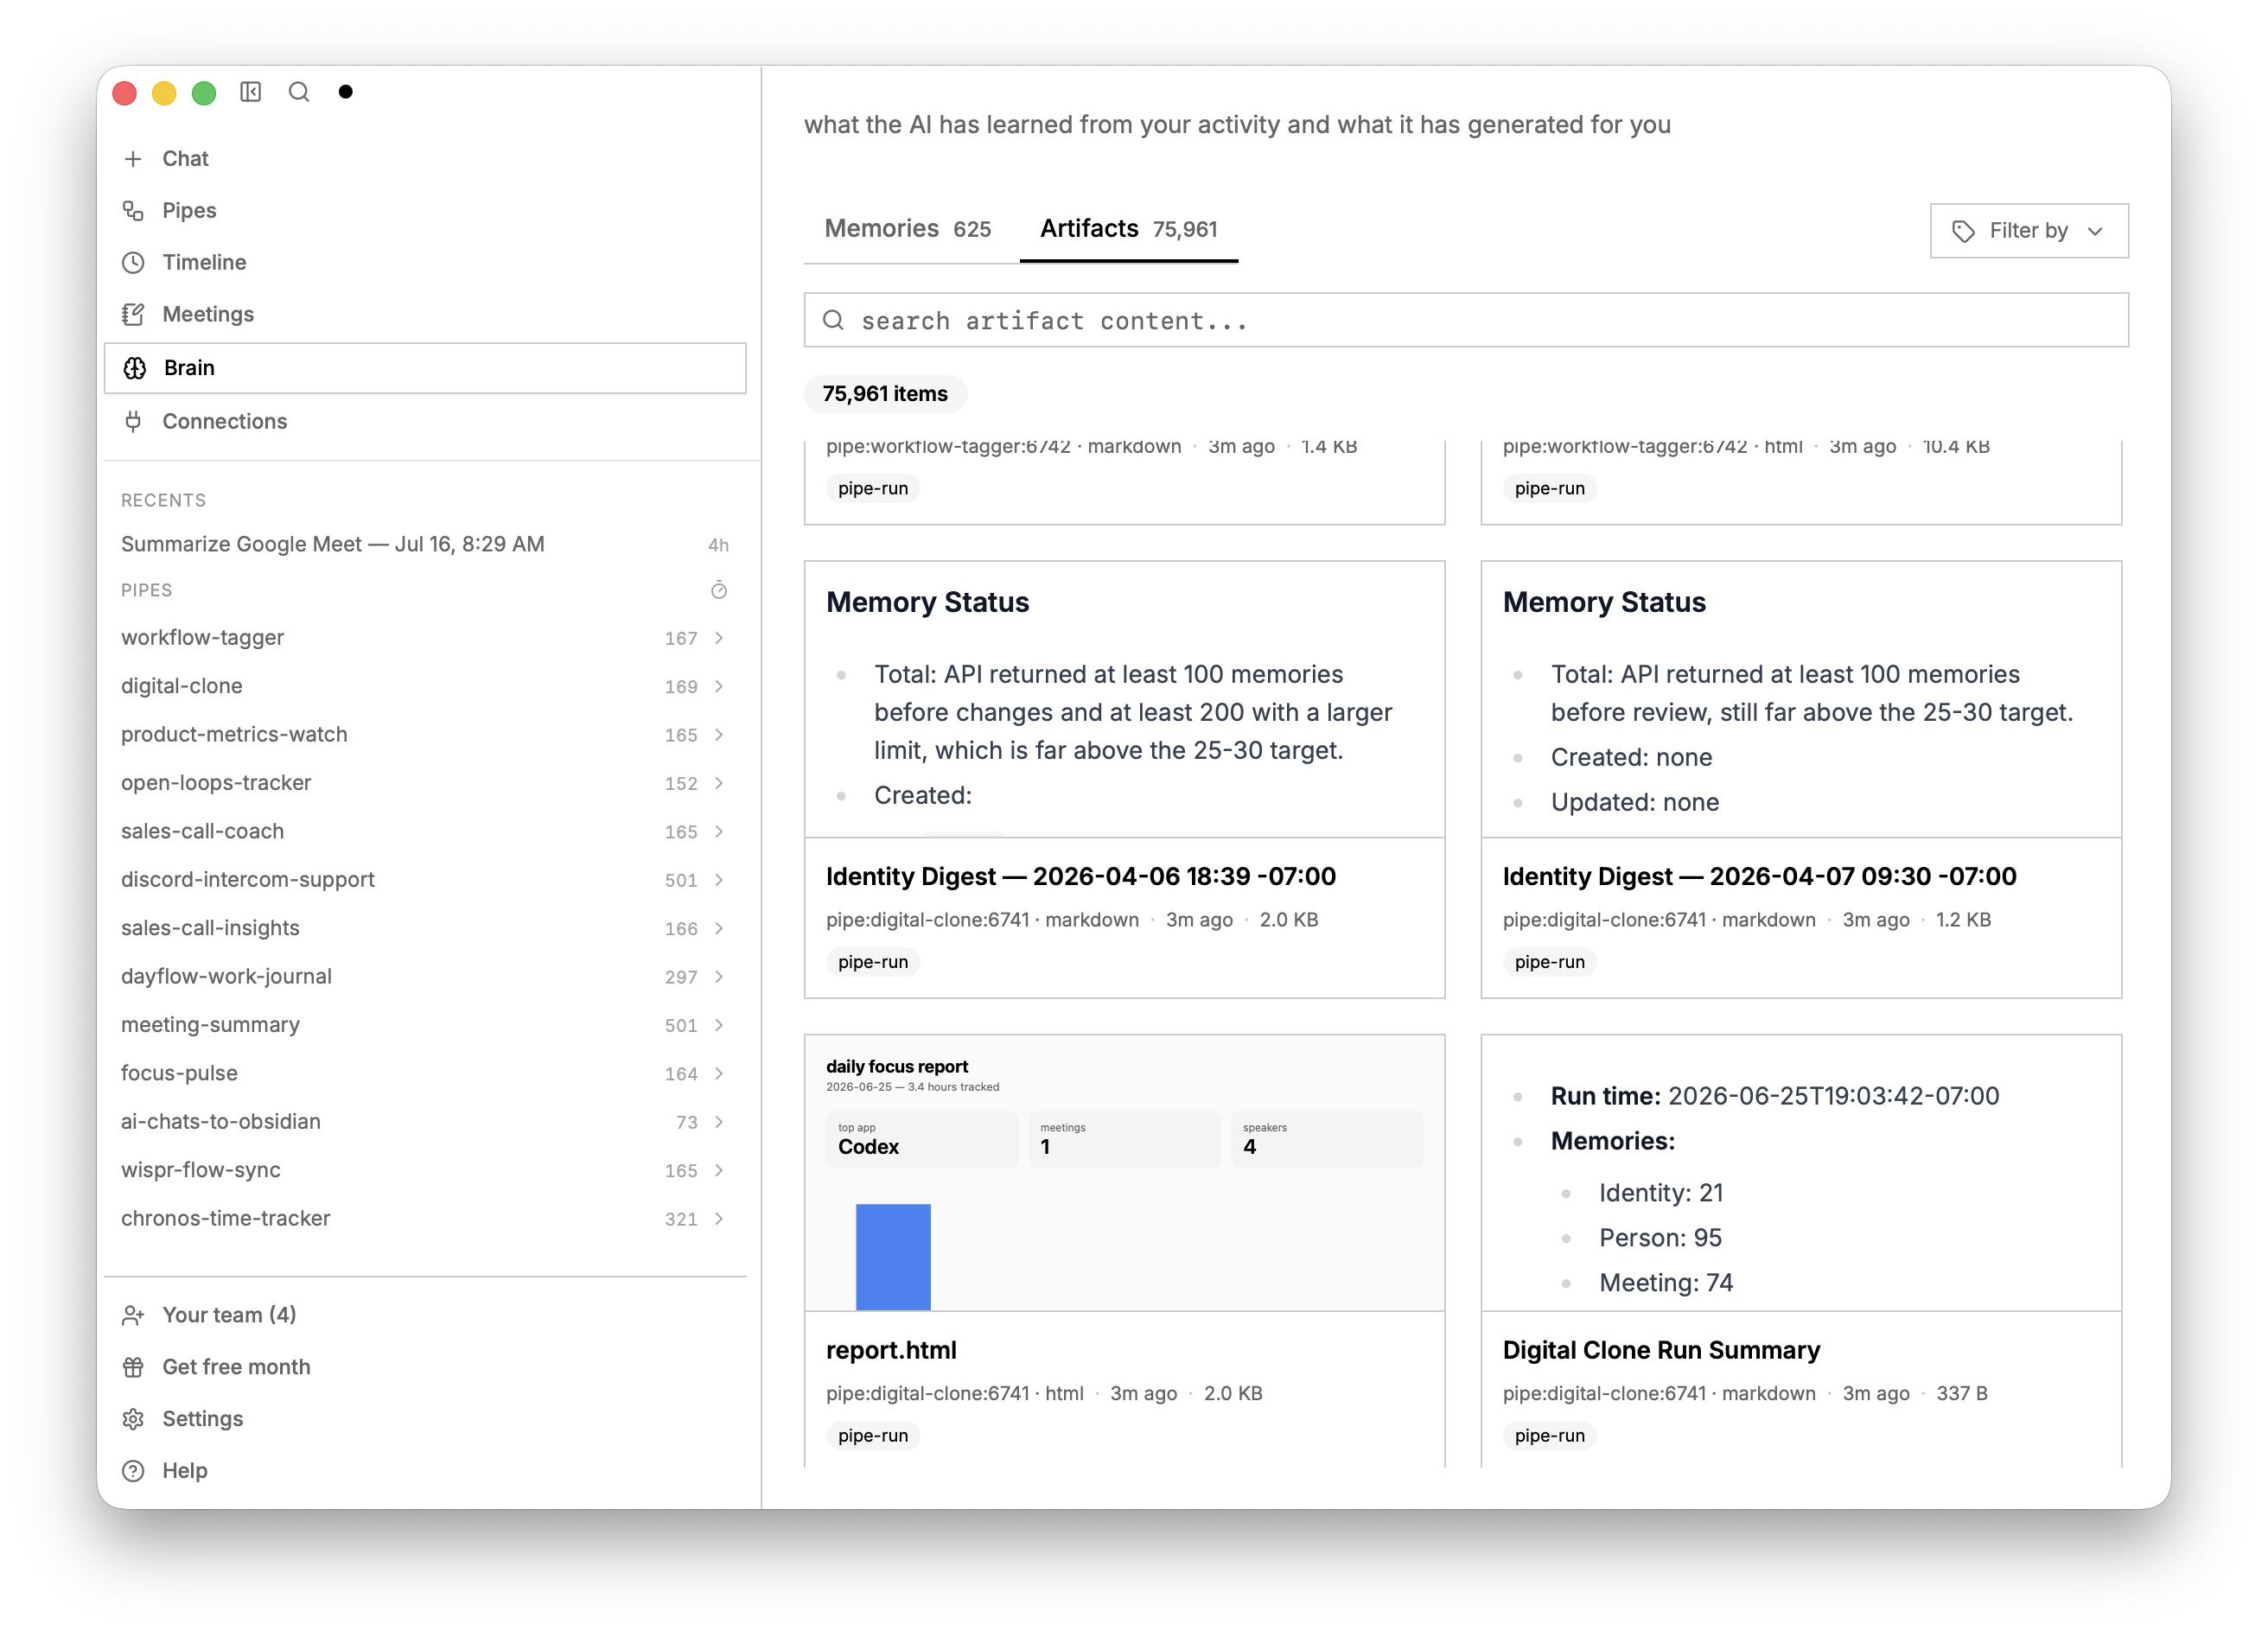
HiddenSteps — a local-first personal workflow intelligence platform

YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…

😱 A curated list of amazingly awesome OSINT

A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance

All about bug bounty (bypasses, payloads, and etc)

Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code

ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.