

PayloadsAllTheThings
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
ctfcurated-resourceseducation+8
swisskyrepo/payloadsallthethingsA list of useful payloads and bypass for Web Application Security and Pentest/CTF
 owasp/android-security-masterclass
OWASP hands-on Android security training lab with 78 MASVS/MASTG modules pairing vulnerable, secure, and attacker apps to demonstrate mobile…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 jas502n/2024informationsecurityengineer
2024年信息安全工程师、2024InformationSecurityEngineer
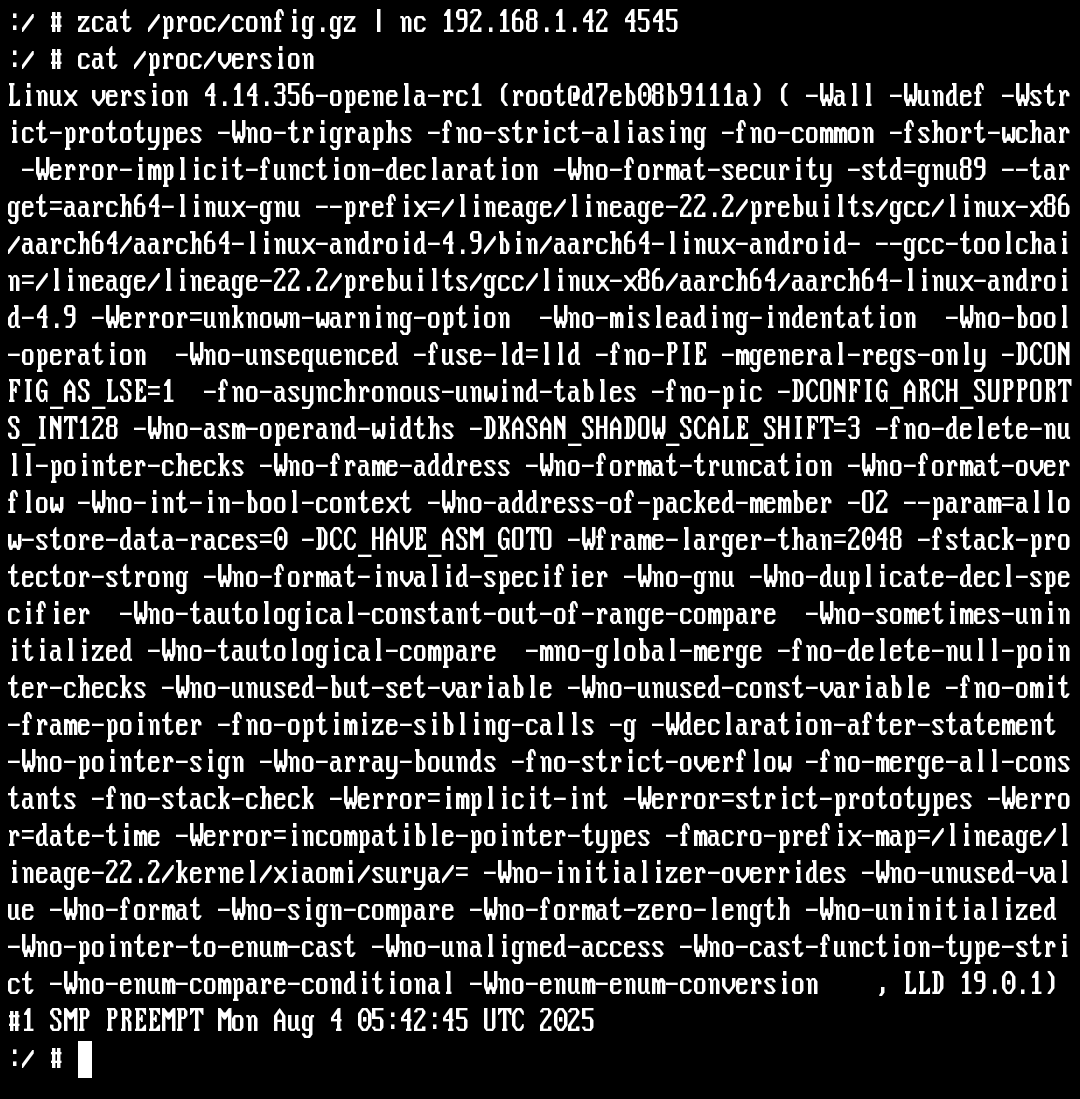
 akabulous/so_you_want_to_build_a_nethunter_kernel
Step-by-step guide to building custom Kali NetHunter kernels for Android: source retrieval, toolchain selection, cross-compilation, and flashing.
 owasp/mastg
Comprehensive OWASP guide for mobile app security testing, reverse engineering, and verifying MASVS/MASWE weaknesses through static, dynamic, and…
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 ralireza/android-security-teryaagh
Android security guides, roadmap, docs, courses, write-ups, and teryaagh.
 bc-security/beginners-guide-to-obfuscation
Hands-on red-team obfuscation workshop teaching AMSI bypass, ETW evasion, and payload obfuscation with PowerShell, Visual Basic, and C# to evade…
 nvisium-jack-mannino/owasp-goatdroid-project
*This project is no longer maintained* OWASP GoatDroid is a fully functional and self-contained training environment for educating developers and…
 n3oari/bscp-exam-guide-by-n3oari-2026
Burp Suite Certified Practitioner - Portswigger - My notes - Guide
 harsh-bothra/securityexplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…
 thyrlian/charles-proxy-mobile-guide
Step-by-step guide to intercepting Android and iOS HTTP/HTTPS traffic with Charles Proxy, covering SSL proxying, CA certificate installation, and…
 merill/awesome-entra
😎 Awesome list of all things related to Microsoft Entra