
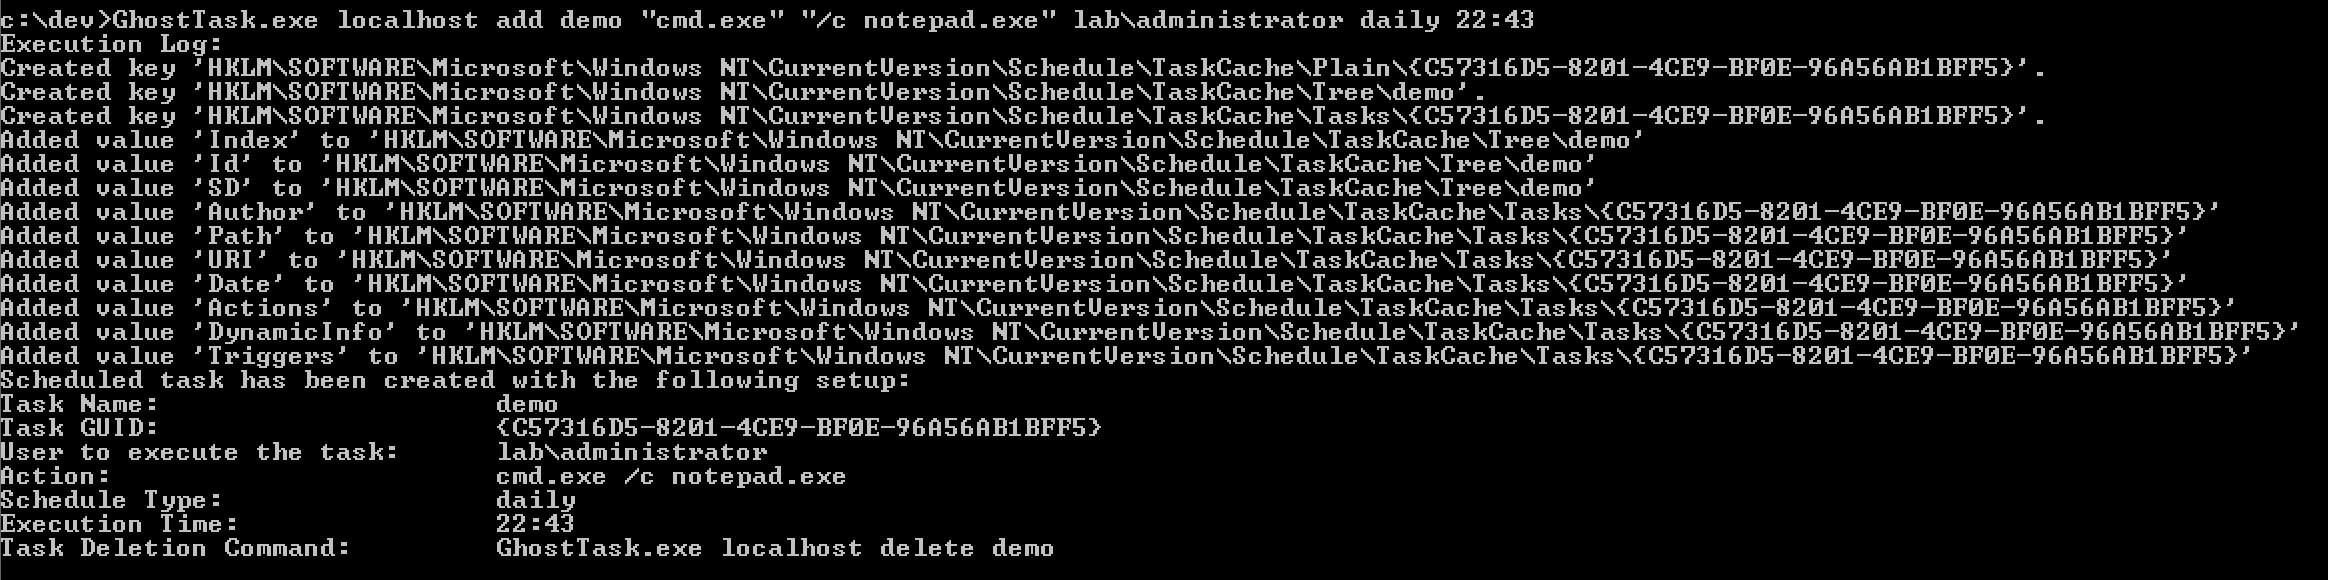
GhostTask
 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
lateral-movementpersistence-mechanismsprivilege-escalation+1
640
netero1010/ghosttaskA tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 horizon3ai/cve-2023-34051
VMware Aria Operations for Logs CVE-2023-34051
 0nin0hanz0/cve-2024-24919-poc
Proof-of-concept exploit for CVE-2024-24919, an unauthenticated file read in Check Point Security Gateways; scans single or multiple IP targets and…